Why This Stuff Actually Matters
Most people watch these movies for the glowing-terminal fantasy. The reality is way less glamorous but more useful if you pay attention. I've spent years in security work and I still watch hacker films to see how culture shapes public understanding of what we actually do. The good ones give you a rough sense of the mindset. The bad ones give you terrible habits you'll have to unlearn later. This isn't about ranking them as entertainment. It's about identifying which ones actually teach you something worth knowing versus which ones you watch once and forget. I organized this list by what you can realistically learn from each one and where the inaccuracies start to become dangerous if taken literally. WarGames (1983) starts with a teenager accidentally connecting to a military training system through a terminal. The film is dated in its technology but remarkably sound in its core idea about how access controls fail when systems are left overly permissive. I've seen this exact pattern repeat in modern cloud misconfigurations. The kid in the movie didn't hack anything. He just had an open connection and a government system that treated every dial-up session as equally trustworthy. That same assumption existed in early corporate networks and it still shows up in poorly segmented environments today.
The scene where Matthew Broderick's character types commands directly into a supercomputer looks ridiculous now but the underlying principle was already present in the 80s. You give someone a shell and they will figure out what you can do with it. I learned that lesson the hard way during a penetration test around 2014 when a client assumed their internal network was safe because nobody outside the building had credentials. One default credentials issue on a forgotten development server opened the whole thing up. WarGames predicted exactly that kind of thinking failure decades before it became a common audit finding. Who Am I (2014) is a German film about a hacking collective operating in Berlin. It's the closest most Western audiences will get to seeing how social engineering actually works in practice. The protagonists don't brute-force their way into anything. They manipulate people. They build trust. They exploit curiosity and hospitality. This is what real intrusion campaigns look like ninety percent of the time. I've sat through briefings where the initial access vector was a phishing email that looked like an invoice from a vendor the company actually worked with. The film shows the psychological mechanics behind that without turning it into a thriller spectacle. What the movie gets right is the team dynamic. Hacking isn't a lone-wolf activity in any professional context. The collective in Who Am I argues about methodology, shares research, and splits work based on skill. That's how bug bounty teams operate and that's how real APT groups function. The one misleading element is how quickly they gain high-level access. In my experience, even a skilled team needs weeks of reconnaissance before they're confident enough to attempt a targeted intrusion. The film compresses that timeline for dramatic purposes.
Sneakers (1992) is probably the most technically honest film ever made about physical security and social engineering combined. The team breaks into a building not through digital means but by exploiting human behavior, tailgating, badge cloning, and insider cooperation. The climax revolves around a cryptanalysis problem that, while simplified, is fundamentally correct. The device they steal processes encryption keys and the government wants it because it breaks existing systems. I worked a security assessment where the physical entry took longer than any technical exploit would have. We spent three days gaining access to a server room by posing as HVAC technicians, watching shift changes, and befriending a janitor who knew which doors stayed unlocked. Sneakers captured that reality with a level of detail most films ignore completely. The movie also shows how a single compromised individual can be worth more than a thousand vulnerabilities. The insider in the film makes the entire operation possible. That's not Hollywood fiction. That's standard operational procedure in nearly every breach I've reviewed.
Get the Full Details
Good Concepts, Terrible Execution
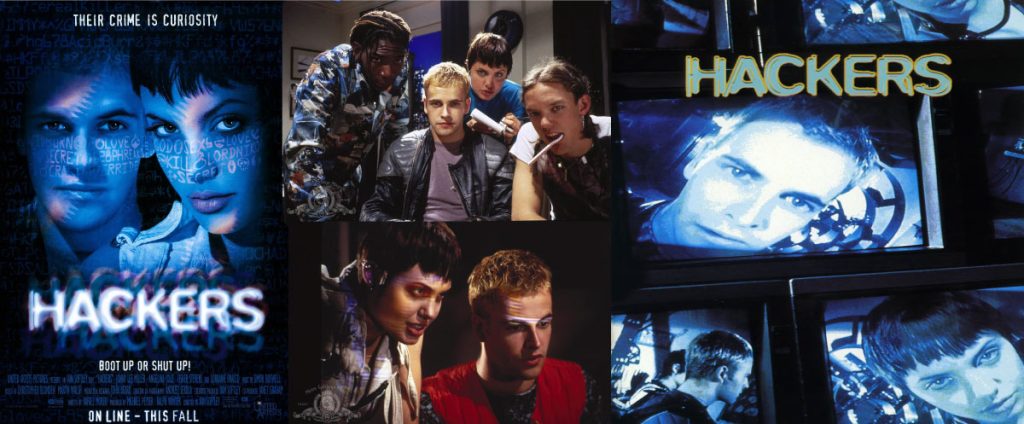
The Matrix (1999) introduced millions of people to the idea that software could be weaponized and that reality itself might be simulated code. The hacking aesthetics were influential and the action sequences were groundbreaking for their time. But treating it as educational material is pointless. Characters plug directly into machines with cables. They fight inside digital spaces. They rewrite reality by changing code on the fly. None of that is even remotely possible with current technology or foreseeable technology. What the film did successfully was create a cultural framework that made cybersecurity seem cool and important. Without movies like The Matrix, the public interest in information security would have stayed niche much longer. I've had clients tell me they got into cybersecurity because they saw someone jacking into a terminal and thought it looked like The Matrix. The cultural impact is real even if the technical content is pure fiction. Hackers (1995) has a cult following and a soundtrack that defined an era. The fashion, the attitude, the keyboard clacking over dramatic music. It's also almost entirely useless as a reference. The hacking scenes show characters typing furiously and then suddenly accessing systems they have no business reaching. The film treats passwords like suggestions and firewalls like decorative screensavers.
I once had a junior analyst on my team reference Hackers as a training resource. We spent twenty minutes explaining why nothing in that film works the way shown. The kid wasn't embarrassed. He genuinely didn't know the difference between cinematic hacking and actual penetration testing methodology. Don't be that person. Watch it for the style points and leave the technical education to documentation and hands-on practice. Office Space (1999) isn't technically a hacker movie but it deserves mention because it captures the bureaucratic environment where security failures thrive. The characters use a microchip to siphon cents from payroll transactions. The concept of logic bombs and data manipulation is there. The execution is comedic but the underlying idea of exploiting trusted systems from within is accurate. Financial fraud through system manipulation happens constantly in the industry. I've seen it in payroll systems, expense report platforms, and healthcare billing. The Office Space scenario is simplified but the principle is sound. Someone with system access can alter transaction values and the audit trail often doesn't catch it unless someone is actively looking. That's why monitoring and logging matter more than you'd think from watching movies.
The Dangerous Ones
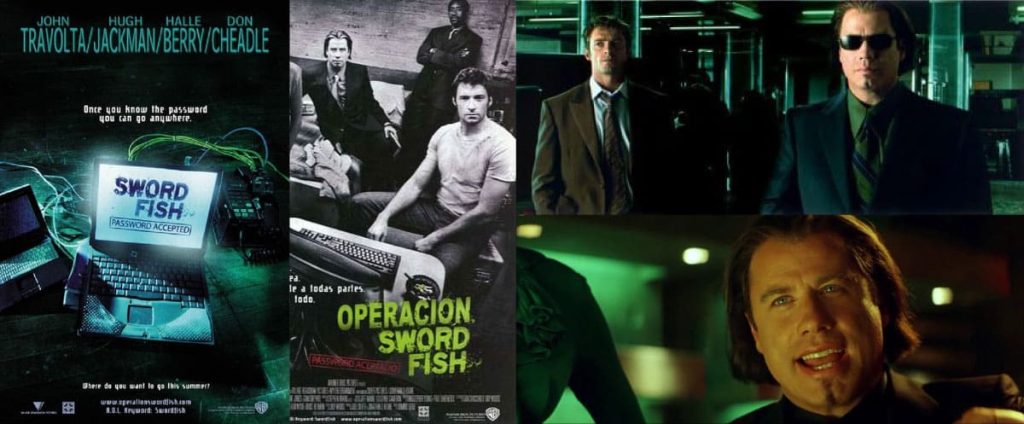
Swordfish (2002) shows Hugh Jackman's character hacking the Federal Reserve in under ten minutes by pressing his forehead against a keyboard. This is the kind of film that creates unrealistic expectations in people who are new to the field. I've had interviews where candidates described their "hacking projects" using techniques that closely mirrored Swordfish scenarios. When I asked follow-up questions about command structure and authentication bypass methods, the answers revealed they'd only seen the movie and never read a single technical document. The worst part about films like this isn't that they're inaccurate. It's that they make legitimate cybersecurity careers seem like jokes. Real work involves reading logs, writing scripts, understanding network topology, and spending hours on tasks that would never look good on screen. The patience required is the opposite of cinematic. If you're entering this field expecting the excitement shown in Swordfish, you'll be disappointed within a week. Untraceable (2008) centers around a website that kills real people based on viewer count. The premise is speculative fiction but the film touches on real concerns about distributed systems, botnets, and the speed at which malicious content can spread online. The technical details are thin but the general direction of the risks is legitimate.

What the film gets slightly right is how difficult it is to track someone operating through distributed infrastructure. The protagonist hunts a website operator while the site runs through countless compromised machines across multiple countries. That pattern exists in reality. The takedown timing in the film is compressed but the structural challenge of pursuing distributed threats is real. I've worked cases where the initial compromise traced through servers in fourteen different jurisdictions and the actual operator was never identified through traditional means.
Documentaries That Actually Help
Coded Anxiety (2023) examines how surveillance technology shapes behavior and privacy in modern society. It's not a narrative film but it's more accurate than most fictional portrayals because it features actual security researchers and privacy advocates discussing real techniques. The documentary covers keylogging, metadata collection, and the tradeoffs between convenience and exposure. The Great Hack (2019) focuses on Cambridge Analytica and data harvesting through social media platforms. While the film takes some narrative liberties, the core mechanism described—collecting user data through seemingly harmless applications and building psychological profiles—is well documented and verified. The ethical implications it raises are the same ones security professionals debate in daily operations. I recommend starting with these documentaries before watching any fictional films about hacking. The factual foundation they provide makes it easier to separate cinematic fantasy from actual technique when you encounter inaccurate portrayals later. Without that baseline knowledge, you'll have no way to tell the difference.
What You Should Actually Take Away
The common thread across the useful films is that most breaches start with human factors, not technical skill. Social engineering, poor access controls, and institutional complacency appear repeatedly. The technical hacking scenes in WarGames, Sneakers, and Who Am I are secondary to the human mistakes that enable them. In my experience this holds true regardless of the target organization's size or sector. Most security incidents I've reviewed followed the same pattern: someone clicked a link, reused a password, left a door unlocked, or trusted the wrong person. The attacker didn't need zero-day exploits or advanced persistent threat tools. They needed opportunity and patience. The films that show this clearly are the ones worth rewatching. If you want to understand the digital underworld the way it actually exists, skip the keyboard-smashing fantasies and focus on the movies that show how systems fail through human error. That gap between theoretical security and practical implementation is where everything falls apart. Understanding that gap is more valuable than any cinematic hacking sequence you'll ever watch.