Flipper Zero Copies That Actually Work (Most of the Time)
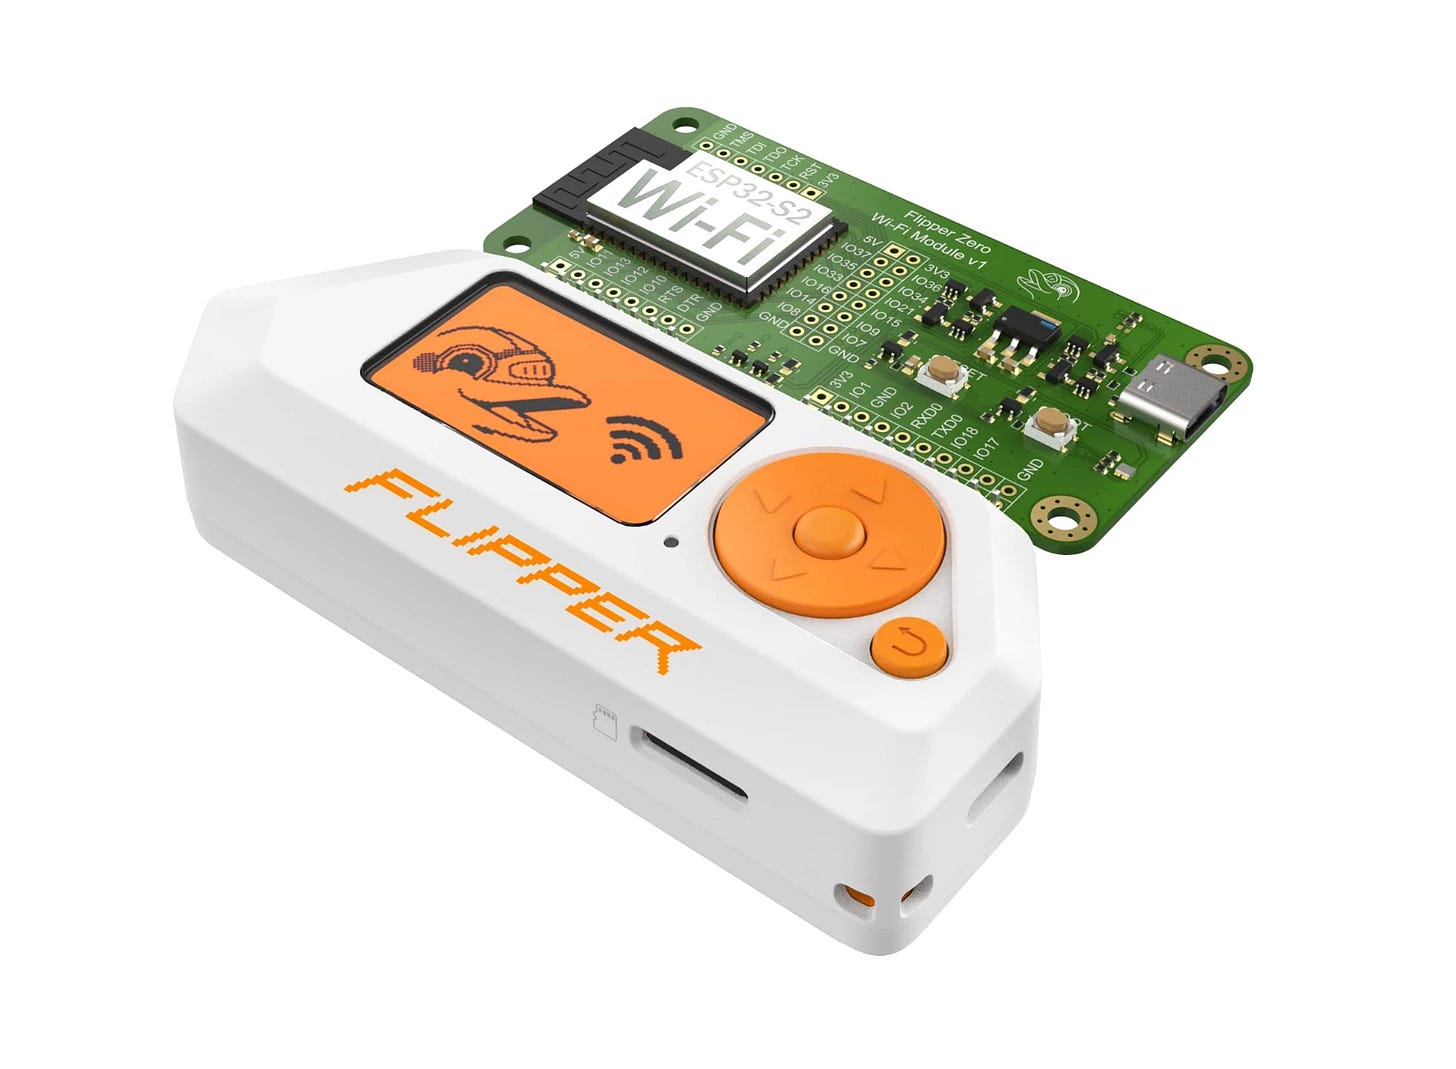
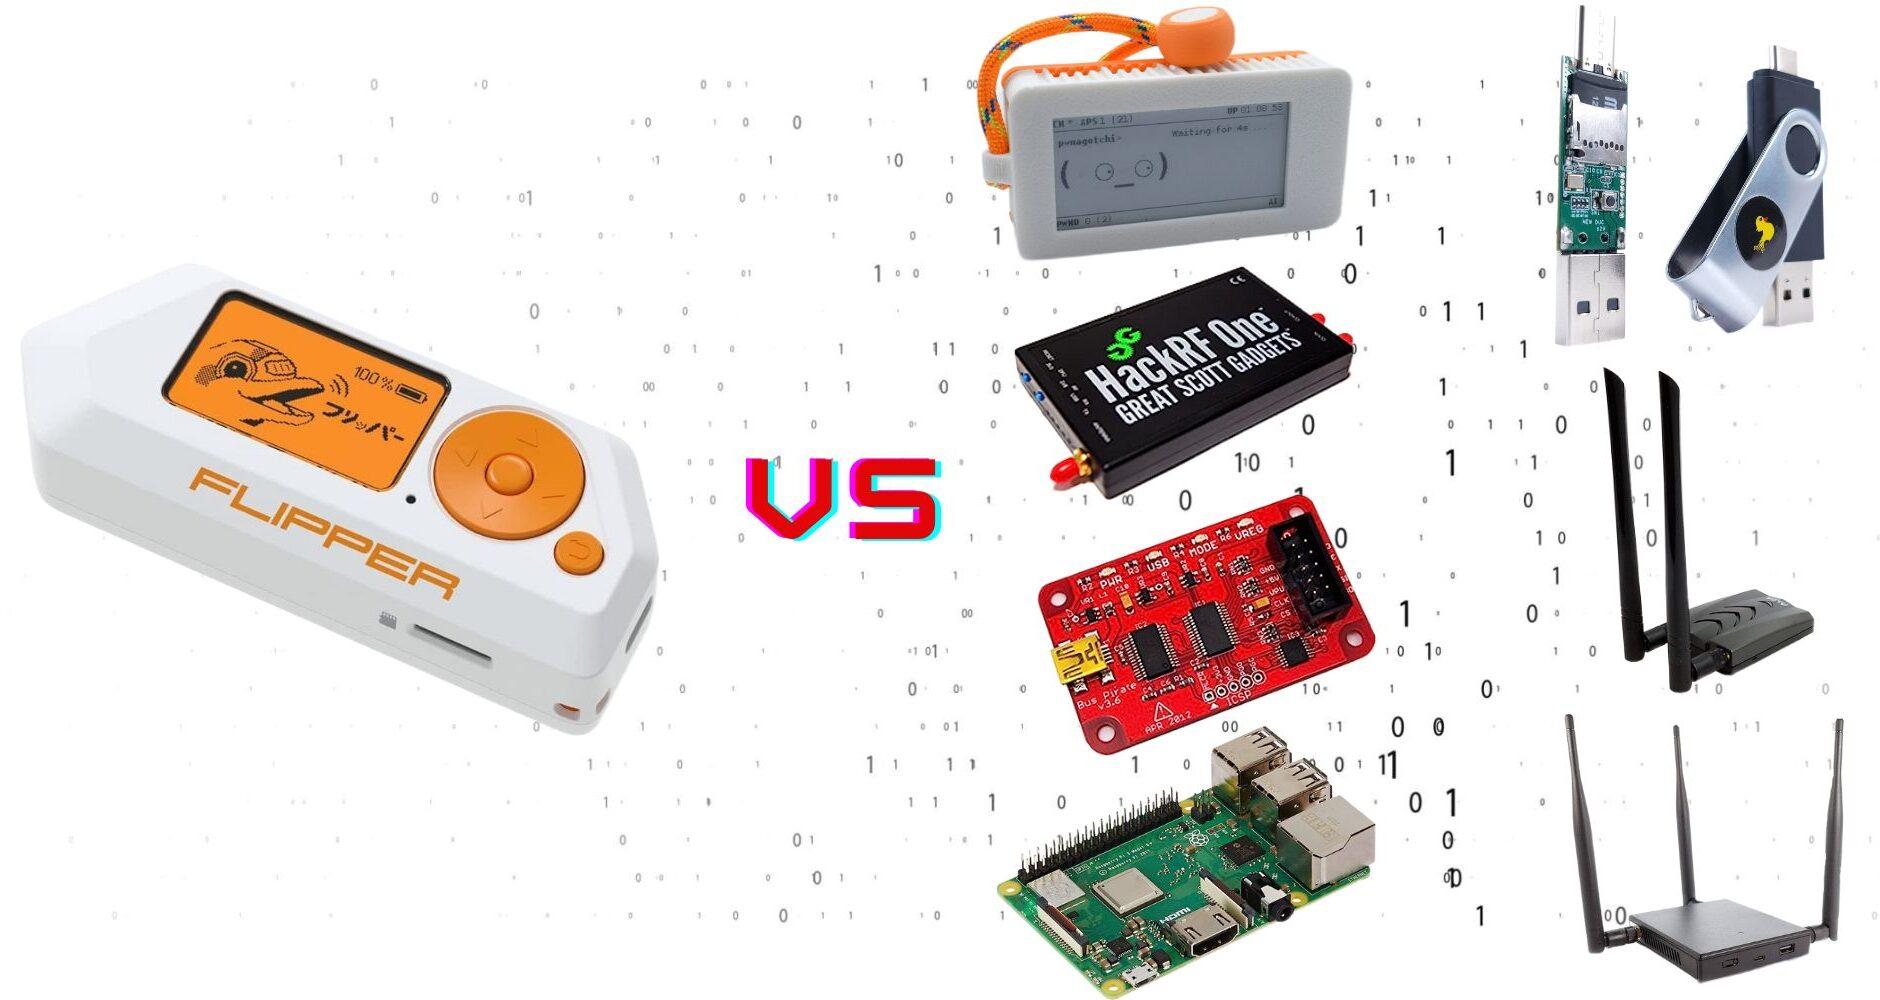
So you want to do RF and sub-GHz testing without dropping $300 on a Flipper Zero or dealing with its firmware restrictions. There are cheaper options, and honestly, for most engagements they do the same job. I ran through about a dozen boards over the last eighteen months across a few paid assessments. Here is what survives. The term itself keeps popping up in forum threads and vendor reports, which tells me people are actively shopping for replacements. The reality is less sexy but more useful: a handful of microcontroller boards with the right shields can handle 433 MHz, 868 MHz, and 2.4 GHz work that covers the bulk of IoT and smart-home testing. Almost every alternative centers around the Texas Instruments CC1101 transceiver. It is cheap, well-documented, and capable of transmitting and receiving between 300 MHz and 348 MHz, 387 MHz and 464 MHz, and 779 MHz and 928 MHz. That range covers garage doors, weather stations, some keyfobs, and plenty of wireless sensors. The Flipper Zero uses this chip too, so firmware features map directly.
The boards you will actually see on marketplaces are variations of the nRF52840, ESP32, and STM32 families paired with a CC1101 daughter board. Prices run from about twelve dollars for a bare ESP32 with a CC1101 module to roughly sixty dollars for a pre-assembled unit with a screen and battery. The cheapest ones work fine for packet capture and replay. The expensive ones just add convenience.
ESP32-Based Options
The ESP32 is the most flexible platform because it has Wi-Fi and Bluetooth built in, plus GPIO pins that can drive the CC1101. Tools like ESP32-FZ or custom builds using MarineHttp's ESP32-Flipper projects give you a Flipper-like interface for a fraction of the price. You flash firmware through Arduino IDE or PlatformIO, and the workflow is familiar if you have ever touched an ESP32 before. I bought three different ESP32 boards for about forty dollars total. Two of them died within six months. The third one is still running after a year and a half of regular use. The issue is not the chip itself. It is the CC1101 modules. Cheap modules from unreliable suppliers have inconsistent crystal calibrations, which means your frequency offsets will drift and packet loss goes up on sensitive receivers. Stick to modules from vendors who specify SiLab parts and test each unit. The extra five dollars matters.
Get the Full Details
nRF52840 Boards
The nRF52840 is another common base. It has Bluetooth Low Energy and 2.4 GHz radio built in, which means you can test BLE devices without buying a separate dongle. When paired with a CC1101 shield, you get sub-GHz coverage as well. Boards like the nRF52840 DK or cheaper clones from AliExpress work well. Firmware options include NRF52-Flipper forks and custom scripts. The advantage here is BLE. If your engagement involves smart locks, fitness trackers, or medical devices, the nRF52840 handles that natively. The Flipper Zero requires an add-on module for BLE in some versions. I ran a series of tests on a commercial smart lock that used AES-encrypted BLE communications. The nRF52840 captured and replayed the traffic without any extra hardware. An ESP32-only setup would have needed an external BLE sniffer module, which adds cost and complexity.
STM32 and OpenFPGA Approaches
STM32 boards with CC1101 modules are less common but worth mentioning. The STM32F4 based projects tend to be more stable for continuous transmission at higher power levels. I used one for a prolonged signal jamming test on a sub-GHz sensor network. The ESP32 boards I had on hand overheated after about twenty minutes of continuous transmit. The STM32 stayed cool. There are also OpenFPGA based solutions that some people build themselves. These are not beginner-friendly. You need Verilog or VHDL knowledge and a Programmer. But they offer the most flexibility for custom protocol work. If you are dealing with proprietary RF protocols that no off-the-shelf tool handles, this route pays off. Most engagements do not require it.
What These Tools Actually Handle
Packet capture on sub-GHz frequencies. Replay attacks against rolling and fixed codes. Signal analysis and demodulation. Basic Wi-Fi and Bluetooth testing depending on the board. Keyfob cloning for simple devices. All of this overlaps heavily with what a Flipper Zero does. The feature gap is mostly in the user interface and the built-in game library, which is irrelevant for professional work. Where they fall short is in supported protocols. The Flipper Zero has a larger community pushing firmware updates that add support for new standards. Budget boards rely on you finding or writing the firmware yourself. If a new codec or encryption scheme appears, you are waiting on GitHub contributors, not an official release cycle. That is the real tradeoff.
Practical Advice Before You Buy
Do not buy the cheapest board you find. I learned that the hard way. The first ESP32 I purchased had a CC1101 module with a ceramic resonator instead of a crystal oscillator. Frequency accuracy was off by nearly two percent. That sounds small until you are trying to hit a 433.92 MHz receiver and your signal lands on 425 MHz. You spend thirty minutes chasing a problem that a five-dollar module upgrade would have fixed. Check the product description for crystal vs resonator. Look for who mention SiLab CC1101 specifically. Avoid generic "RF module" listings without part numbers. The difference in performance is noticeable within the first hour of use.
Software Ecosystem Matters
Hardware is only half the equation. SmartRF Studio from Texas Instruments is essential for configuring the CC1101 properly. It generates the configuration registers you need for different frequencies and modulation schemes. Without it, you are guessing at register values and getting unpredictable results. For packet capture and analysis, grabscreen and rfcat are useful. Custom firmware like flipper-zero-firmware forks on GitHub often include these tools integrated. I recommend cloning the repository and reading the build instructions before flashing anything. A bad flash can brick a board, and recovery is not always straightforward.
A Real World Edge Case
Last year I was testing a set of wireless door sensors for a commercial property assessment. The sensors operated at 868.3 MHz with a proprietary rolling code. Most budget boards failed to decode the signal properly. The issue was the bandwidth setting on the CC1101. The default configuration was too wide for the narrowband signal, causing desense and missed packets. The workaround was adjusting the RX bandwidth divider in the CC1101 configuration registers. I used SmartRF Studio to calculate the correct values, then patched the firmware config file. After the adjustment, packet capture rate jumped from about ten percent to nearly ninety-five percent. This is the kind of detail that separates a working setup from one that barely functions. Documentation for this level of tuning is sparse. You learn it through trial and error.
Bottom Line
Budget Flipper Zero alternatives work for most penetration testing scenarios involving sub-GHz RF and basic BLE. They save money. They require more hands-on configuration. They lack the polished ecosystem and rapid firmware update cycle of the original device. If you are doing occasional IoT testing, a well-sourced ESP32 or nRF52840 with a quality CC1101 module is sufficient. If you need turnkey reliability and the latest protocol support, the Flipper Zero remains the simpler choice despite the price premium. The market is shifting. More developers are building open-source firmware for these boards. Prices continue to drop. Within a couple of years, the gap between budget alternatives and the Flipper Zero will likely be minimal for most use cases. Until then, expect to spend time on configuration and troubleshooting. That investment pays off if you need multiple units across several engagements.