How Digital Trust Actually Works in Transformation Programs
The way organizations approach digital trust usually starts wrong. Leadership treats it as a technical problem to be solved by the IT department, which means they deploy tools before they've mapped the human layers underneath. I worked on a retail transformation about three years ago where the client had already purchased a $2 million identity management platform before anyone asked frontline employees what their biggest friction point was. The platform sat there for eight months unused because the workflow it was supposed to secure didn't actually match how people worked. That's the standard pattern I see repeatedly, and it's why Dan Hayhurst's framework around transformative leadership in North America matters. Hayhurst's approach centers on the idea that digital trust isn't a product you buy. It's an organizational capability that has to be built through deliberate leadership behaviors at every level. The core concept is simple but easy to mess up in practice. You start with understanding where trust is currently broken in your digital ecosystem, then you design leadership interventions that address the root cause rather than the symptom. Most people I talk to confuse data security with digital trust. They are related but completely different things. A system can be perfectly secured and still be untrusted by the people who have to use it daily. I remember consulting for a regional healthcare network that had passed every compliance audit in the book. Their EHR system was encrypted, access-controlled, and tracked. The nurses still found workarounds because the system required fifteen clicks to accomplish a task that took them forty seconds when they did it manually. Security was perfect. Trust was nonexistent. That gap between security and trust is exactly what Hayhurst's model addresses.
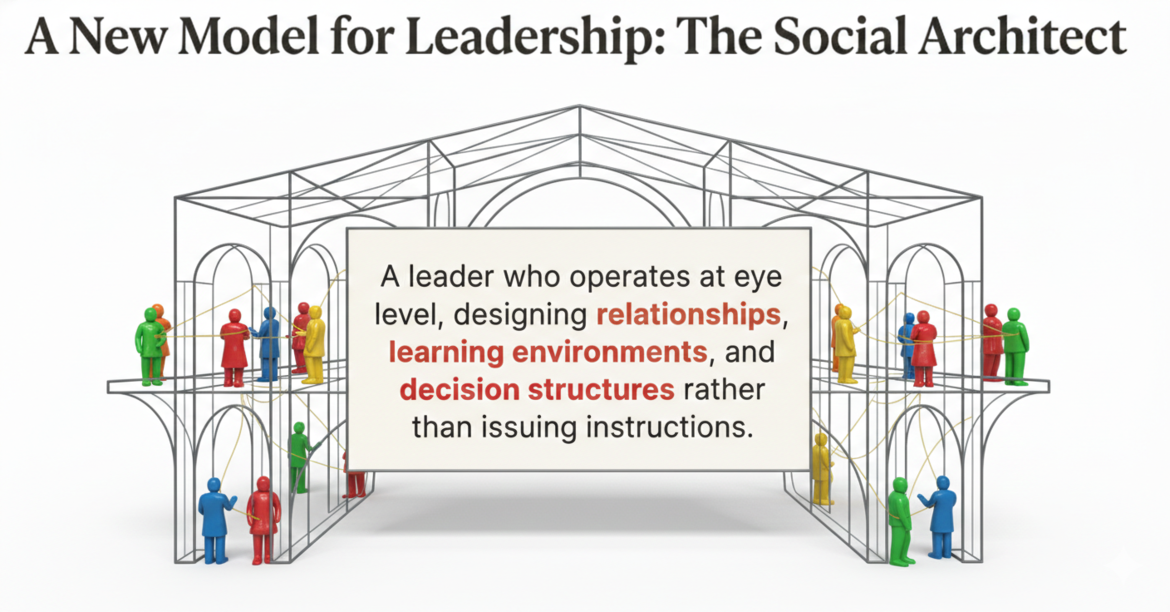
The transformative leadership component comes into play because fixing digital trust requires changing how leaders communicate, make decisions, and distribute authority. It's not a process you hand off to a project manager and check off quarterly. Leaders in North American organizations tend to want something they can implement in ninety days and measure with a dashboard. Digital trust doesn't work that way. Here's how the actual methodology unfolds when you're doing it properly. First, you map the trust landscape. This means conducting structured interviews across three tiers: executive sponsorship, middle management, and frontline operators. Each group will have a completely different understanding of where trust exists and where it's failing. You're looking for patterns, not individual complaints. The executive team at one logistics company I worked with insisted their tracking system was trusted company-wide. The drivers' feedback was entirely different, and the disconnect wasn't a communication problem. The system had been designed without input from the people whose daily workflow depended on it. Second, you identify the specific trust gaps. Not all gaps are equal. Some are structural, meaning the technology itself creates friction that erodes confidence. Others are behavioral, arising from leadership decisions that signal either transparency or opacity. The third category, and the one most people miss, is cultural. An organization might have good systems and honest leadership but still lack the shared norms that make digital trust stick. You need to diagnose which layer you're actually dealing with before prescribing anything.
The intervention design phase is where most transformation programs stall. Leaders want to jump to solutions. Instead, you spend time co-designing the fixes with the people who will live with them. This takes longer upfront but saves roughly six to eight weeks of rework later. I once watched a manufacturing firm skip this step with their ERP rollout. They spent fourteen weeks building custom dashboards for floor supervisors without showing them a prototype first. When they finally did a walkthrough, sixty percent of the features were rejected because they solved problems the supervisors didn't have and ignored the three issues that mattered most. That's a six-to-eight-week delay caused by skipping the co-design step. One thing beginners consistently get wrong is assuming trust metrics are enough to track progress. They implement surveys and scorecards and then declare success when the numbers improve. The problem is that trust scores are lagging indicators at best. By the time a survey shows a dip, the damage to actual behavior has already happened. I started using a combination of system usage analytics and unannounced shadowing sessions instead. Watching someone actually navigate your platform reveals frustration points that no survey will ever capture. I once caught a user abandoning a critical workflow after encountering an error message so cryptic it looked like gibberish. The error code wasn't logged anywhere the helpdesk could access it. That single observation led to a fix that reduced support tickets by forty percent over the next quarter. There's also a counter-intuitive element to this that isn't widely discussed. The more trust you need from people, the less control you should exert through the system. Overly restrictive access policies, constant monitoring prompts, and mandatory approval chains all signal distrust. They also create the exact behavior they're supposed to prevent: people finding ways around the controls. I've seen this play out in financial services organizations where compliance requirements drove system designs that made legitimate work nearly impossible. The result was a parallel system of unofficial processes that had zero visibility to anyone in charge.
Get the Full Details

The workaround I've used successfully is implementing what I call graduated trust architecture. New users or those in higher-risk roles start with tighter controls. As they demonstrate consistent compliant behavior through system usage patterns, the controls ease automatically. This rewards trustworthiness instead of punishing everyone with the same restrictions. It requires a decent data pipeline to track behavior, but most organizations already have that infrastructure from their existing systems. Another nuanced point involves the role of failure in building trust. Organizations that punish digital mistakes drive them underground. When someone makes an error in a system, whether it's a data entry mistake or a misconfigured workflow, the natural instinct is to discipline. What actually builds trust is making the error visible and using it as a learning opportunity for everyone. I once worked with a supply chain team where a minor configuration error in their inventory system caused a $300,000 discrepancy. Instead of assigning blame, they held a public postmortem that led to a system change preventing the same error from happening again. That incident became the most cited example of why people should report mistakes early. The regional differences across North America matter more than most consultants acknowledge. Leaders in the United States tend to favor fast implementation and measurable ROI within a single fiscal year. Canadian organizations often place higher value on stakeholder consensus and longer timelines. This isn't a stereotype I'm throwing around. I've run transformation programs in both countries where the exact same framework required different pacing and communication strategies to land correctly. What works in a Boston tech company will fall apart in a Toronto-based financial institution if you don't adjust the approach.
Here's where the model breaks down and you need something else. If your organization has deeply embedded corruption or leadership that is actively hostile to transparency, no amount of framework application will fix digital trust. The model assumes a baseline of goodwill from those in power. When that's absent, you're not dealing with a trust problem. You're dealing with a governance problem that requires board-level intervention, not a leadership methodology. I've encountered this situation twice in my career and both times the right answer was to escalate beyond the scope of any transformation program. Another limitation involves small organizations with fewer than fifty employees. The framework assumes a certain level of organizational complexity that simply doesn't exist in smaller setups. In those cases, direct conversation between leadership and staff is usually faster and more effective than any structured methodology. Don't force a framework that was designed for mid-to-large enterprises onto a small operation. It will slow you down more than it helps. The practical takeaway is that digital trust is built through consistent leadership behavior over time, not through any single tool or initiative. Hayhurst's contribution in the North American context is providing a structured way to think about that behavior across multiple organizational layers simultaneously. It's not a quick fix. It's also not as complicated as the consulting industry makes it sound. Start by mapping where trust actually lives in your organization. Then design interventions that address the specific gaps you find. Measure progress through behavior, not just survey scores. And recognize when the problem is bigger than any leadership framework can solve.