Visa Test Card Numbers: What They Actually Are and Who Uses Them
I ran into this mess about three years ago when I was integrating a payment gateway for a client. They wanted "test credit cards" and pointed me at some sketchy generator site. I had to explain that half the tools out there are scams, and the other half generate numbers that look real but trigger every fraud alert in the book. The legitimate version is way simpler than anyone selling these things wants you to believe. A Visa credit card number generator is, at its core, a script that outputs card numbers passing the Luhn check algorithm. That's it. The Luhn algorithm is the checksum Visa uses to validate card numbers on the spot when you type them in at checkout. Any number that passes Luhn gets one star of legitimacy. But passing Luhn doesn't make a number usable. It just means it won't get instantly rejected at the input field. Here's what most people don't realize: generating a card number that passes Luhn is trivial. You can write it in Python in about eight lines. The hard part is getting a number that maps to an actual active account, and that's the line you're not supposed to cross. The sites selling "fullz" or "live cards" are either scamming you or handing you stolen data. Both outcomes are bad for you.
The legitimate world of test card numbers exists entirely within payment processor documentation. Stripe publishes a whole page of them. Square has theirs. Adyen, Braintree, you name it. These are numbers like 4242 4242 4242 4242 that go through their test mode without any real money attached. They're designed so your dev environment doesn't start charging actual customers while you're debugging. This is what the term should mean. But search around and you'll hit the gray market. People building phishing tools, or running chargeback fraud schemes, or just curious. I've seen forums full of folks who spent twenty minutes generating numbers, then another forty trying to figure out why none of them worked on random checkout forms. The answer is always the same: test numbers only work in test environments. Real merchant gateways require a PAN that's issued to a real account with a valid expiry date, CVV, and billing address matching what's on file. You can't generate your way past that without already having access to someone's real account data. Here's a practical example that shows the gap between theory and reality. I had a colleague set up a test environment for a fintech startup. We used the standard Visa test ranges — the 4111 series and the 4012 series. They worked perfectly for six weeks of integration testing. Then the startup moved to staging and tried the same numbers against a different processor. Every single transaction returned "do not honor." The processor in question had updated their test card list mid-quarter, which happens more often than you'd think. The workaround was checking the provider's changelog and updating the test PAN list accordingly. Took about ten minutes if you're paying attention. Could have been a two-day headache if you're not.
How The Luhn Algorithm Actually Works In Practice
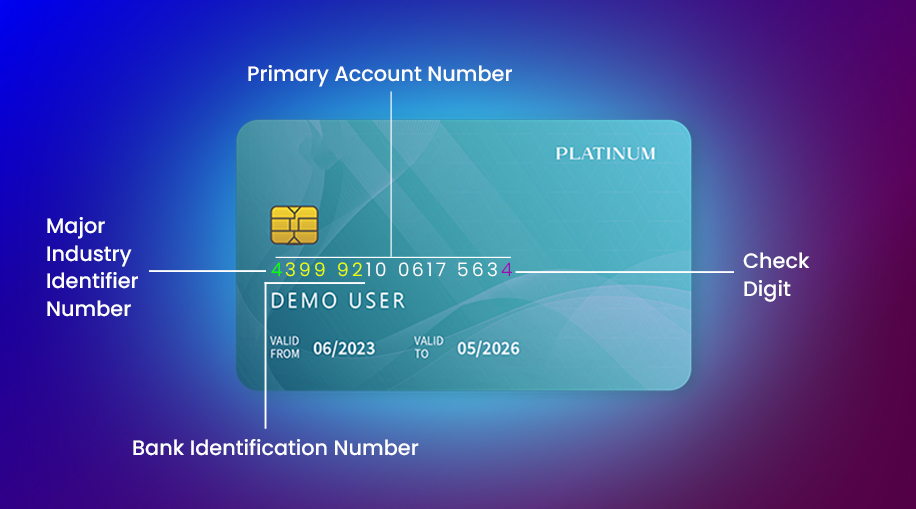
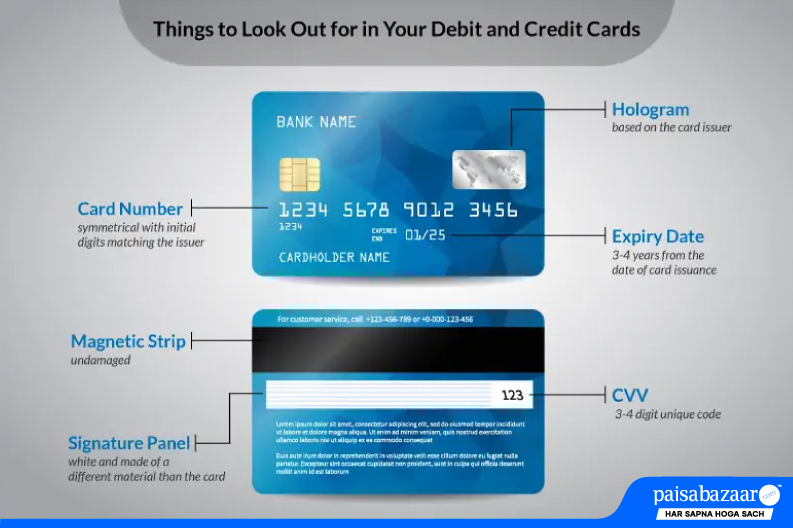
Every Visa card number starts with 4. That's the IIN, the Issuer Identification Number. The next digits identify the specific issuing bank. Then you have the individual account identifier, and the last digit is the Luhn checksum. Generate a 15 or 16 digit string where the final digit makes the Luhn sum divisible by ten, and you have a structurally valid number. Nothing more. The reason this matters is because some generator tools out there produce numbers that fail Luhn entirely. If you're testing an application and you keep getting format errors before the request even hits the payment processor, your generator might be broken. Or worse, you're using one that only produces numbers for a different card brand but labels them as Visa. I've seen this happen with tools that hardcode 4-prefixes but don't actually run the checksum. The numbers look right but get rejected immediately by any system that validates Luhn before forwarding to the acquirer. There's also the matter of BIN ranges. Not all numbers starting with 4 are Visa. Some prepaid cards and debit products fall in adjacent ranges. If your test suite isn't filtering by IIN properly, you might think you're testing Visa checkout when you're actually testing a different product class with different rules. I learned this the hard way when a client's test data kept failing on a specific merchant category code. Turns out the generator was pulling from a mixed BIN table and slipping in a few debit-style PANs that the merchant terminal didn't support. Switched to the provider's official test BIN list and the issue vanished.
Get the Full Details

The Risks Are Real And They're Not Just Legal
Let's be clear about what happens when you use generated numbers outside a test environment. It's fraud. Period. There's no clever loophole. A card number generated by an algorithm without a corresponding real account is either a test number (which only works in sandboxed environments) or it's someone else's stolen data. Using either for actual purchases is unauthorized use of a payment instrument. In most jurisdictions that's a felony with serious sentencing guidelines. But even people who only use these tools for "testing" run into trouble. I've watched devs get their accounts banned from payment processors for using test card numbers in production environments. Not because the processor can't tell the difference — they can, immediately — but because using test credentials in a live environment looks like an attempt to bypass controls. Stripe, Square, PayPal, they all have automated detection for test PANs in production flows. The ban is automatic and usually permanent. Getting it reversed requires going through support, explaining yourself, and hoping someone reads your ticket. It's not impossible, but it's not quick either. There's also the security risk of the generators themselves. Many of these tools are hosted on domains that rotate frequently. Downloading and running them exposes your machine to malware. I've personally seen several GitHub repos that claim to be "Visa card generators" but embed cryptominers or credential harvesters in their executables. The .exe files are tiny because they're mostly downloaders pulling the actual payload from a C2 server. If you're going to run any of this code, use a VM with no persistent storage and monitor network egress. Worth five minutes to avoid an hour of incident response.
What Legitimate Developers Should Actually Do
If you're building a payment integration, use your provider's official test card list. Stripe's is at stripe.com/docs/testing. Square's is in their developer docs. These lists are updated regularly and include not just Visa but Mastercard, Amex, and Discover test numbers across different transaction types — success, decline, insufficient funds, stolen card, you name it. Each one returns a predictable response code so you can test your error handling without touching real money. For more advanced testing, set up a local test environment with a tool like Stripe's CLI or the Braintree sandbox. These let you simulate the full payment flow including webhooks, refunds, and disputes. Takes about fifteen minutes to set up if you follow the documentation, which is actually good. That's far more useful than any generator because you're testing your own code, not just validating that a number passes Luhn. One edge case that trips people up: some payment processors require you to whitelist test card numbers in their dashboard before they'll work in your test mode. I hit this with a newer gateway where the default configuration rejected all test transactions until I explicitly added the test PANs to an allowlist. The documentation mentioned this in passing, but it took me an afternoon of debugging before I found the right setting. Check your provider's docs for "test mode configuration" or "test card whitelisting" before assuming the numbers aren't working for some deeper reason.
Also worth noting: test card numbers expire. Not in the traditional sense, but providers rotate them. A number that worked last quarter might be blacklisted this quarter. If your integration tests start failing en masse and you haven't changed your code, check whether your provider updated their test PAN list. It happens quarterly at Stripe and semi-annually at some other providers. The change log is always public. Takes two minutes to read.

Bottom Line
Test card numbers exist for a reason and using them properly is straightforward. The moment you try to use them outside a controlled test environment, or the moment you use a generator that claims to produce "working" real card numbers, you've left legitimate territory. The risks aren't abstract — they're financial, legal, and technical, and they compound quickly. If you need test cards for development, stick to the official lists. Everything else is a shortcut that leads somewhere you don't want to go.