SafeSnapshot: What It Actually Does For You
SafeSnapshot is a monitoring service that crawls the dark web, paste sites, and public breach databases to find instances where your personal information has surfaced outside of authorized channels. It takes a baseline snapshot of where your data exists online, then re-checks periodically and alerts you when it detects new appearances. That's essentially the entire value proposition. A lot of people think it's some kind of magic shield. It's not. It's an alarm system that tells you when someone already opened your data. I spent probably six months running a personal instance before I trusted it enough to recommend it to anyone. The main thing that tripped me up early on was false positives from old breaches that weren't actually active threats. SafeSnapshot will flag your email from a 2014 forum leak even though nobody is doing anything with that password. It doesn't necessarily distinguish between dormant exposure and active exploitation. That's something you have to figure out yourself.
The Ultimate Safersnapshot Protecting Your Online Identity And Devices
Setting it up is straightforward if you don't overcomplicate it. You create an account, verify your primary email and phone number, then run the initial scan. The scan pulls from known breach repositories, pastebin archives, and dark web marketplaces. You'll get a report showing where your data appears. From there you set up monitoring thresholds and notification preferences. Here's the part nobody really talks about clearly. The effectiveness of SafeSnapshot depends almost entirely on how much data you feed it during setup. If you only enter your primary email address, you're going to miss a huge chunk of your exposure. I had a friend who signed up with just his main Gmail and his spouse's data was sitting in three separate breach databases he didn't know about. You need to enter every email, every phone number, and any aliases you've ever used. Spend maybe twenty minutes on this step. It matters more than anything else you do with the service. The monitoring interval is another area where people make mistakes. The default scan frequency is reasonable for most users, but if you're in a higher-risk category or you've just dealt with a confirmed breach, you should bump the frequency up temporarily. SafeSnapshot can scan as frequently as daily on paid tiers. I usually run daily scans for about two weeks after I detect a new breach appearance, then drop back to weekly. This caught a reused password appearing on a completely different site that I hadn't seen in the initial report.
What It Misses and Where It Breaks
SafeSnapshot doesn't monitor your actual devices. It doesn't scan your hard drive or check your router. If someone has physical access to your laptop or a keylogger is running on your machine, this service won't tell you. It only monitors external exposure. People conflate this sometimes. There's a difference between your data being leaked publicly and your device being compromised. SafeSnapshot handles one of those things. The other limitation is coverage. No service has complete visibility into the dark web. There are private forums, encrypted marketplaces, and regional breaches that don't make it into the databases SafeSnapshot scans. I once found my data in a breach from a smaller Eastern European payment processor that wasn't indexed anywhere SafeSnapshot was looking. It showed up six months later through a completely different channel. Nothing is comprehensive. The service gives you a best-effort approximation, not a guarantee. There's also the response problem. SafeSnapshot will alert you that your credentials appeared somewhere. What you do with that information is entirely on you. A lot of people get notifications and then sit on them for weeks. The window between a breach becoming public and someone attempting credential stuffing is usually measured in hours, not days. I've seen people get locked out of accounts within forty-eight hours of a notification because they didn't act fast enough. The tool does its job. The rest is on you.
Get the Full Details

Practical Steps After You Get Alerted
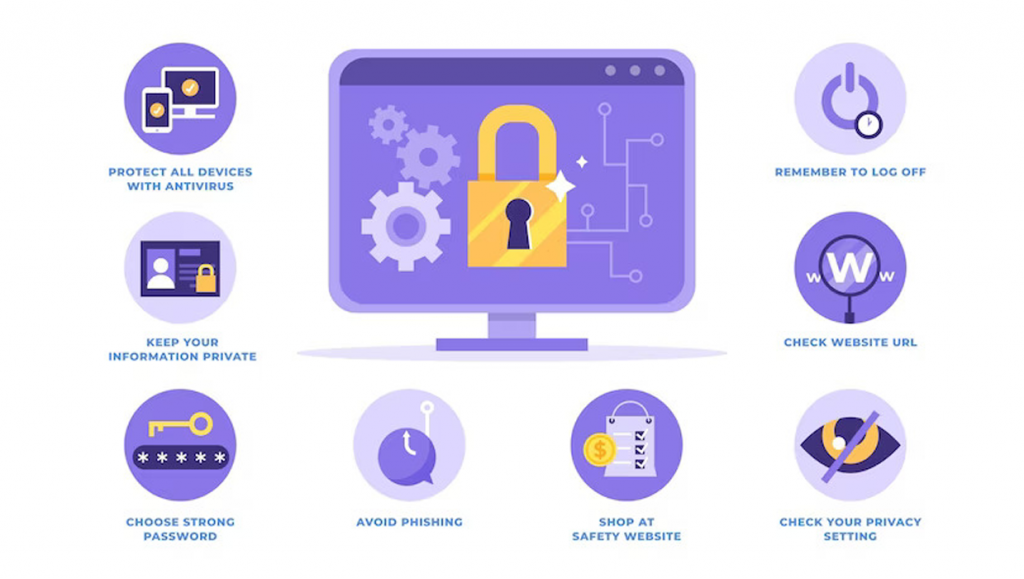
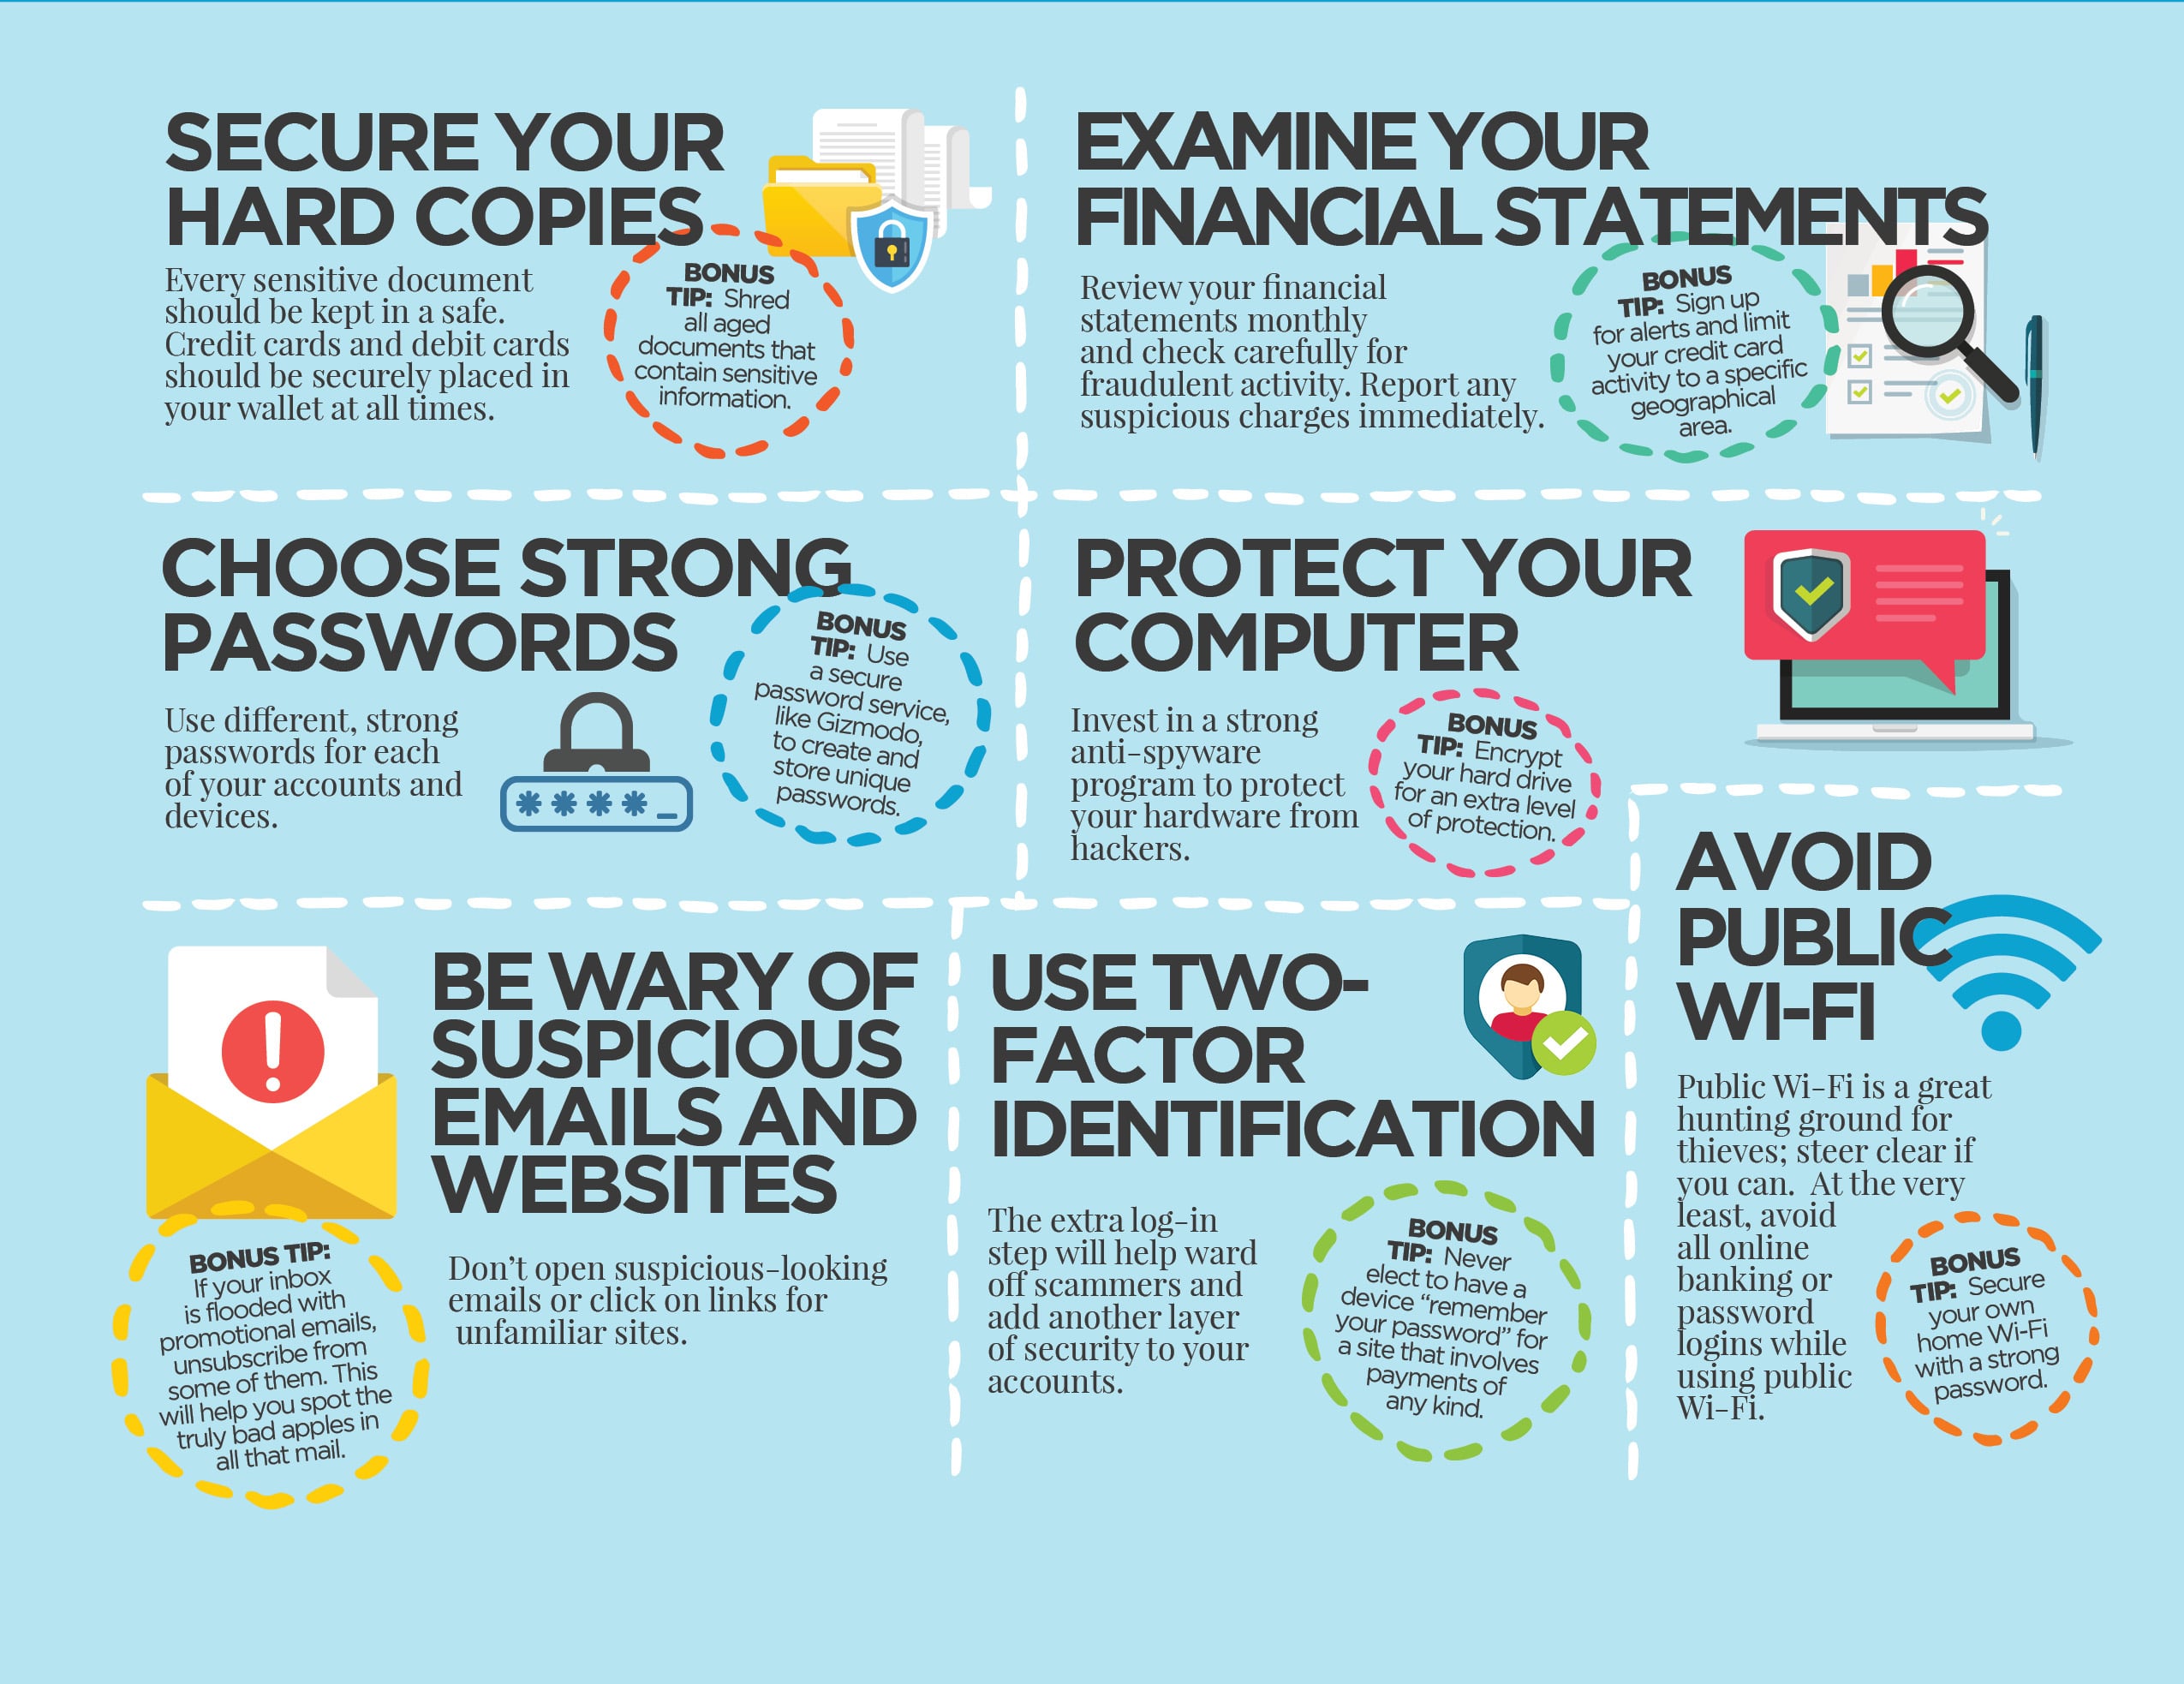
When SafeSnapshot flags your data, don't just change the password on that one service and call it done. The whole point of these breaches is that most people reuse passwords. If your email and password combo showed up in a breach, assume it's been tried against every major platform. Change passwords on your email, banking, social media, and anything else that uses the same combination. Use a password manager. Stop picking the same eight characters across thirty different services. Enable two-factor authentication everywhere it's available. Preferably using an authenticator app or hardware key, not SMS. I know SMS 2FA is annoying because of SIM swapping, but it's still better than nothing and it covers the vast majority of attack vectors. After a breach notification, I walk through every account I care about and check whether 2FA is active. Usually two or three are missing it. Keep the SafeSnapshot reports. They become useful if you ever need to dispute fraudulent activity or prove that your data was compromised before an attacker used it. Having a timestamped record from a reputable monitoring service carries weight with banks and credit bureaus. I had to dispute a charge that came from an account my data was exposed in. The SafeSnapshot alert log was the documentation that made the dispute go through without a fight.
Alternatives Worth Knowing About
If SafeSnapshot isn't the right fit, there are other options. Have I Been Pwned is free and covers a massive breach database, but it doesn't offer continuous monitoring unless you pay for additional features. It's good for one-off checks but not ideal if you want ongoing surveillance. Identity theft protection services like IdentityForce or Aura do broader monitoring that includes credit reports and dark web surveillance, but you're paying significantly more for less targeted coverage. If you just want to know where your data has been exposed and when, SafeSnapshot is the more focused tool. If you need full identity recovery assistance built in, you might look elsewhere. The service itself is available through their website at safersnapshot.com. They offer a free tier with limited scans and a paid tier that unlocks continuous monitoring, deeper breach data, and faster alerts. The free version is decent for a first pass. I'd recommend running it, seeing what comes back, and then deciding whether the paid monitoring is worth it based on what you found. Don't pay for a year upfront without testing the free tier first. The data they find on you in the free scan is the same data they'd monitor on the paid plan. There's no difference in coverage quality between tiers, only in frequency and alert speed.