Why You Need to Know Where Is My IP
Most people treat their IP address like it's secret government intelligence. It's not. It's the digital equivalent of your home address, and it changes depending on how you connect. When you look up where is my ip, you're really just asking what address the world sees when you reach out. That matters more than most users realize. I've spent years dealing with network debugging, security audits, and the occasional "why am I blocked from this site" complaint. The truth is that IP tracking is both simpler and more limited than pop culture makes it seem. This guide walks through what actually happens, how to read the results, and where the common mistakes are.
The Ultimate Guide To Where Is My Ip Uncovering Your Online Identity
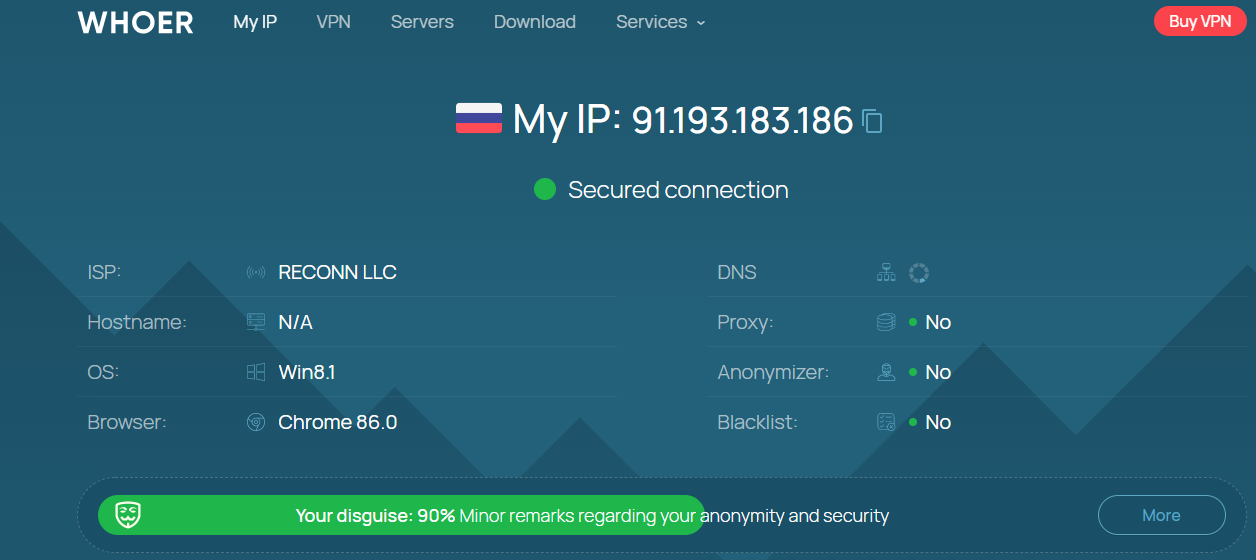
Let's start with the basics. An IP address is a numeric label assigned to every device on a network. IPv4 looks like 192.0.2.45. IPv6 is the longer version people don't deal with yet because most consumer routers still hand out IPv4 addresses. When you run an IP lookup, you're querying a database that maps that number to a geographic region, an ISP, and sometimes a data center or hosting provider. A standard IP geolocation lookup gives you four or five data points. The city or region, the postal code if it's granular enough, the country, the ISP or organization that owns that block of addresses, and occasionally the latitude and longitude coordinates. That's it. It does not tell you your exact street address, your name, your browsing history, or what device you're using. A lot of people expect more from these tools than they can deliver. Here's the part that trips people up. The geographic data comes from regional internet registries and commercial geolocation databases, and they are not perfectly accurate. The city-level precision is usually good within a metropolitan area, but rural regions and border zones can be off by tens or even hundreds of kilometers. If you're seeing an IP location that doesn't match where you live, the ISP's headquarters might be listed instead of the local exchange. That's normal. It happens all the time.
How to Check Your Own IP Address
The simplest way is to visit any IP lookup service and read what it tells you. But if you want to do this without handing your traffic to yet another random website, you can run a lookup from your own machine. On Windows, open Command Prompt and type ipconfig. On macOS or Linux, use ifconfig or ip addr in the terminal. That gives you your private IP, which looks like 192.168.x.x or 10.x.x.x. That number only means something inside your local network. It's not visible to the outside world. The public IP is what matters for anything related to online identity. Your router or modem handles the translation between your private address and the public one through NAT. To find your public IP, you can use a command like curl ifconfig.me or ping an external service that echoes your address back. Or just visit any basic IP checker. The result is your public IP, and running a geolocation query against it will show the data points I described above.
Get the Full Details

Why Your IP Location Might Be Wrong
I once had a client who was convinced someone in another country was accessing their admin panel because the IP geolocation showed a completely different nation. The investigation revealed they were using a VPN at the time. When they disabled it, the IP pointed exactly where they lived. That's not a flaw in geolocation. That's exactly how VPNs work. They route your traffic through a server in another location, and the destination sees that server's IP instead of yours. But even without a VPN, there are other reasons the location data drifts. Mobile carriers often use carrier-grade NAT, which means dozens or hundreds of phones share a single public IP. The geolocation database associates that shared IP with the carrier's main hub, which could be in a different state or province. Residential ISPs do the same thing on a smaller scale. Data center IPs are another source of confusion. If you're hosting something or using a CDN, the IP might resolve to a facility that has no connection to your actual physical location. There's also the issue of outdated database entries. Geolocation providers update their records regularly, but there's always a lag. A newly assigned IP block might still be mapped to the previous tenant's location for weeks after the change. If you recently moved and your ISP reassigned your block, your public IP might still show your old city until the database catches up.
What Your IP Does and Doesn't Reveal
Your IP address alone does not identify you as a person. It identifies your connection point to the internet. To trace that back to a specific individual, someone would need access to the ISP's logs, which contain the mapping between the public IP and the specific customer account at a given time. That information is generally only available through legal process, not through a public lookup tool. However, your IP combined with other data can build a fairly detailed profile. Browsing patterns, login timestamps, and device fingerprints tracked by websites can be correlated with your IP address over time. Advertisers and analytics platforms do this routinely. It's why you might see ads for something you searched for hours ago. Your IP is one piece of a larger tracking puzzle, and that's worth understanding even if the IP itself is just a number. The common misconception is that changing your IP changes your identity online. It helps with privacy to some degree, but it doesn't erase your digital footprint. Websites remember you through cookies, local storage, and fingerprinting techniques that work independently of your IP address. I've seen users switch networks multiple times and still get recognized by the same platform because the device fingerprint remained consistent.
Using IP Lookups for Security and Troubleshooting
One practical use case that most people overlook is checking the IP of an unfamiliar connection. If you run a website or an API, you might see login attempts from addresses that don't match your usual traffic patterns. A quick reverse lookup can tell you whether that IP belongs to a known hosting provider, a Tor exit node, or a residential connection in a region you don't serve. That information alone helps you decide whether to block, monitor, or ignore the activity. I ran into this recently with a client who was getting hammered by requests from an Asian IP range on their WordPress admin page. The geolocation data showed it was coming from a data center in Singapore, and their entire user base was domestic US. We set up a firewall rule blocking known hosting and data center ranges and reduced the volume immediately. The false positive rate stayed low because legitimate traffic was almost entirely residential. For home users, the most useful application is verifying that your own IP matches your expectations. If you're traveling and your IP suddenly shows your hometown instead of your hotel location, something might be routing through a proxy or VPN you didn't intentionally enable. Some router firmware and smart home devices have background services that periodically connect to corporate servers, and those connections can originate from unexpected locations.
Limitations and When IP Lookup Fails Completely
Here's the honest part. IP geolocation is not a surveillance tool, and it shouldn't be treated like one. The accuracy varies wildly depending on the database you're querying. Some free lookup services use older or less reliable datasets. Commercial databases like MaxMind offer better granularity but still have blind spots, especially in developing regions and mobile networks. The bigger limitation is that IP lookups can't track movement in real time. If someone is moving through different networks, the IP changes with each hop. There's no continuous breadcrumb trail from the lookup side. You only see the current address, and even that might be a relay or proxy. For anything requiring actual forensic precision, you'd need cooperation from the relevant ISPs and often legal authority to access their logs. Public tools can't provide that level of detail. Another failure mode is deliberate spoofing or misdirection. Advanced attackers can route traffic through multiple layers of proxies and VPNs, making the final visible IP meaningless for location purposes. I've seen this in penetration testing engagements where the target IP pointed to a residential connection in a completely unrelated country. The actual attacker was three hops away, and the geolocation result was just noise.
For most everyday purposes, an IP lookup is fast and informative enough. It takes about ten seconds to run a check and usually returns results within a minute. The real value is in understanding what the results mean and what they don't mean. A lot of anxiety around online identity comes from expecting an IP lookup to do something it was never designed to do.