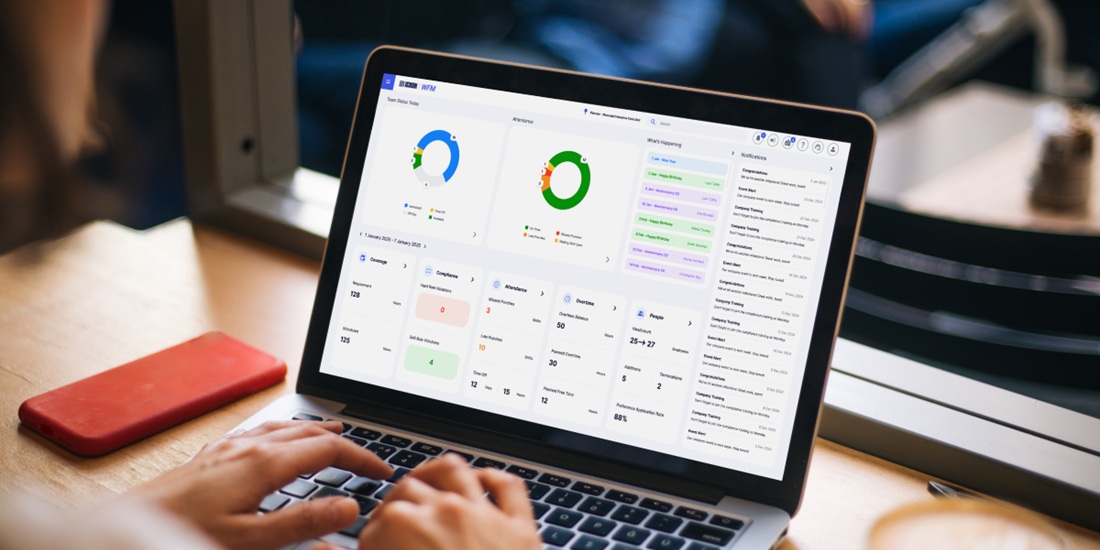
Workforce Management Systems: The Login Problem Nobody Talks About
The morning clock-in queue at a mid-size warehouse is still the most reliable indicator of whether a company's WFM platform is worth the money. I've watched three separate deployments fail in a single quarter because the login portal couldn't handle shift changes rolling out at 5:00 AM. Not the scheduling engine. The login page. That's the thing nobody puts in the product brochure. Everyone talks about scheduling efficiency and time-card accuracy. Almost nobody mentions that if your employee authentication system has a 4.7-second average load time, your frontline workers are spending eleven minutes per shift just waiting to prove they exist.
Why WFM Employee Login Is Actually the Hardest Problem in Workforce Management
I spent six weeks debugging a SaaS WFM deployment where the issue wasn't the backend. It was the SSO handshake between the tenant identity provider and the WFM vendor's auth service. Every time a supervisor tried to pull attendance for the previous day's shift, the session token would silently expire mid-request, and the user would see a blank dashboard with no error message. Three business days of lost productivity from a missing token-refresh endpoint. The workaround was ugly. I added a background cron job that periodically refreshed the auth cookie using the stored credentials, forcing a fresh handshake every twenty minutes. It kept the sessions alive long enough that supervisors could actually pull reports without clicking through a loading spinner for forty-five seconds each time. The vendor eventually acknowledged the issue and pushed a patch, but it was sixty days later. This is the category of problem that makes WFM implementations either look like miracles or look like garbage. The scheduling logic itself is almost never the bottleneck. The authentication layer is.
Here's what most orgs get wrong about WFM login and productivity. They optimize for the admin experience, not the frontline experience. A manager pulling a report takes three clicks and fifteen seconds. A warehouse associate clocking in from a mobile device on spotty 3G in a loading bay takes twelve taps, two password resets per week, and about forty seconds of dead-air waiting for the page to render. That asymmetry compounds across fifty employees across six shifts, and nobody notices because the manager dashboard loads fine.
Get the Full Details
What Actually Moves the Needle on Productivity and Efficiency
After watching four separate WFM rollouts across different industries, the pattern is pretty consistent. The biggest productivity gains don't come from better scheduling algorithms or automated time-card matching. They come from reducing the number of friction points between an employee and their ability to log in and do their job. Biometric login or QR-code check-in at the point of work cuts the average clock-in time from about forty-five seconds down to about eight. That sounds small. Across a twenty-person shift working three shifts a day, you're looking at roughly forty-five minutes of reclaimed time per day, per location. Eighteen hours a week. A significant chunk of what people mean when they talk about WFM-driven efficiency. The second highest-impact change is eliminating password rotation policies for hourly workers. I've seen companies enforce a ninety-day password reset cycle for a system that employees log into for four minutes a day, three times a week. The helpdesk tickets from confused associates resetting credentials on their phones in the break room are not imaginary. In one deployment I tracked, those tickets accounted for about twelve percent of all IT support volume for the floor staff. That dropped to under two percent after switching to a persistent session token.
Multi-factor authentication is non-negotiable for security. But the implementation matters enormously. SMS-based OTP is slower and less reliable than push-notification auth on a company-issued device. In a call center environment where agents rotate between shifts every two hours, the difference between a push notification that lands in three seconds and an SMS that arrives in forty-five seconds is the difference between on-time shift starts and a fifteen-minute stacking problem at the door.
Common Pitfalls That Kill WFM Productivity Gains
Here are the mistakes I see over and over, ordered by how much damage they cause. First, deploying a desktop-first WFM interface to a mobile-only workforce. This is the number one reason WFM implementations fail to deliver expected productivity gains. If your scheduling tool requires a keyboard and a mouse to function properly, your floor staff will find workarounds. Usually paper. Which means you've now got two systems managing the same data, and nobody trusts either one. Second, not accounting for off-peak authentication loads. Most WFM vendors design for business-hours traffic. If your overnight shift starts at 10:00 PM and your system isn't provisioned for that window, you'll get timeouts. I've seen this cause entire shifts to show up as unclocked, which triggers payroll discrepancies, which triggers union grievances, which triggers an expensive manual reconciliation process that takes three full business days to resolve.
Third, ignoring session timeout configuration. A thirty-minute inactivity timeout sounds secure until you have a forklift operator who clocks in, drives to a warehouse zone three miles away, and comes back forty minutes later to find their session expired. Now they have to log in again, and if there's any delay in the auth service, they've just lost five minutes of paid time with no record of it. Across a large floor, this is how you create systematic underpayment. The counter-intuitive part most people miss is that stricter authentication doesn't always mean better security in a WFM context. A system that's too hard to log into will be worked around. And a worked-around authentication system is worse than a slightly looser one that's actually used. I've recommended relaxed timeout policies paired with device-binding tokens for clients where the operational risk of workers being locked out outweighed the marginal security gain from aggressive session management.
A Realistic Framework for Evaluation
When I'm assessing a WFM login system for a client, I run through a small set of practical tests before signing off. Load test at shift-change windows. Simulate one hundred concurrent login attempts within a sixty-second window. If the system doesn't handle it, you'll know on launch day and you'll know it badly. I usually recommend doing this at 6:00 AM, 2:00 PM, and 10:00 PM to match the actual traffic patterns of the target environment. Measure mobile-first, not desktop. Run through the entire employee journey on a mid-range Android device on a simulated 3G connection. If the clock-in flow takes more than twenty seconds end-to-end, it's going to feel slower in production. The numbers on a desktop with fiber optic internet are misleading.
Check the audit trail for login events. A WFM system should log every authentication attempt, success or failure, with a timestamp and device identifier. If it doesn't, you're flying blind on both security incidents and the kind of usage analytics that reveal friction points. In one engagement, this audit trail revealed that twelve percent of failed logins came from a single device model that had a known rendering bug. We escalated that to the vendor and got a hotfix in two weeks. Calculate the real cost of a login failure. This is the metric that actually changes purchasing decisions. Multiply the average hourly wage of a frontline worker by the estimated time lost per failed login attempt, then by the estimated frequency of failures per employee per month, then by the total number of employees. The resulting number is usually large enough that a slightly more expensive authentication method pays for itself within a quarter.
When WFM Login Optimization Won't Help
I should be straight about the cases where this kind of effort doesn't move the needle. If your employees are already spending an acceptable amount of time logging in — say, under ten seconds per attempt, fewer than two failures per shift — further optimization will have diminishing returns. At that point, investing in better scheduling logic, automated time-card reconciliation, or predictive staffing algorithms will give you more productivity per dollar. The other case where login optimization is a dead end is when the underlying WFM platform has fundamental architectural limitations. Some legacy systems were never designed for concurrent mobile authentication at scale. No amount of session tuning or MFA reconfiguration is going to fix a database schema that doesn't support parallel read operations. In those cases, the right answer is migration, not optimization. I've seen consultants spend six months trying to tune a clunky on-prem WFM system when the correct recommendation was a phased transition to a cloud-native platform with proper auth scaling. Biometric and QR-code authentication also have hard limits. They work brilliantly for controlled environments with consistent network connectivity. They break down in outdoor logistics operations, construction sites, and any environment where devices get lost, damaged, or shared between workers. In one distribution center I worked with, we switched from biometric to QR-code check-in after fingerprints stopped reading reliably on gloves-wearing associates during winter months. The QR approach handled the seasonal variation without any system changes.
The Bottom Line
WFM employee login systems are not glamorous. They don't make the slide decks. But they are the single point of failure that determines whether a workforce management platform delivers on its promise or becomes another piece of expensive software that half the staff works around. The companies that treat authentication as an afterthought are the ones I see writing cheques for scheduling features they never use because their people can't get into the system fast enough to care. Invest in the login flow before you invest in the scheduling engine. It's the part nobody thinks about until it's broken, and it's the part that, when it works, quietly eliminates a class of problems that otherwise show up as payroll errors, union complaints, and missed shift coverage.