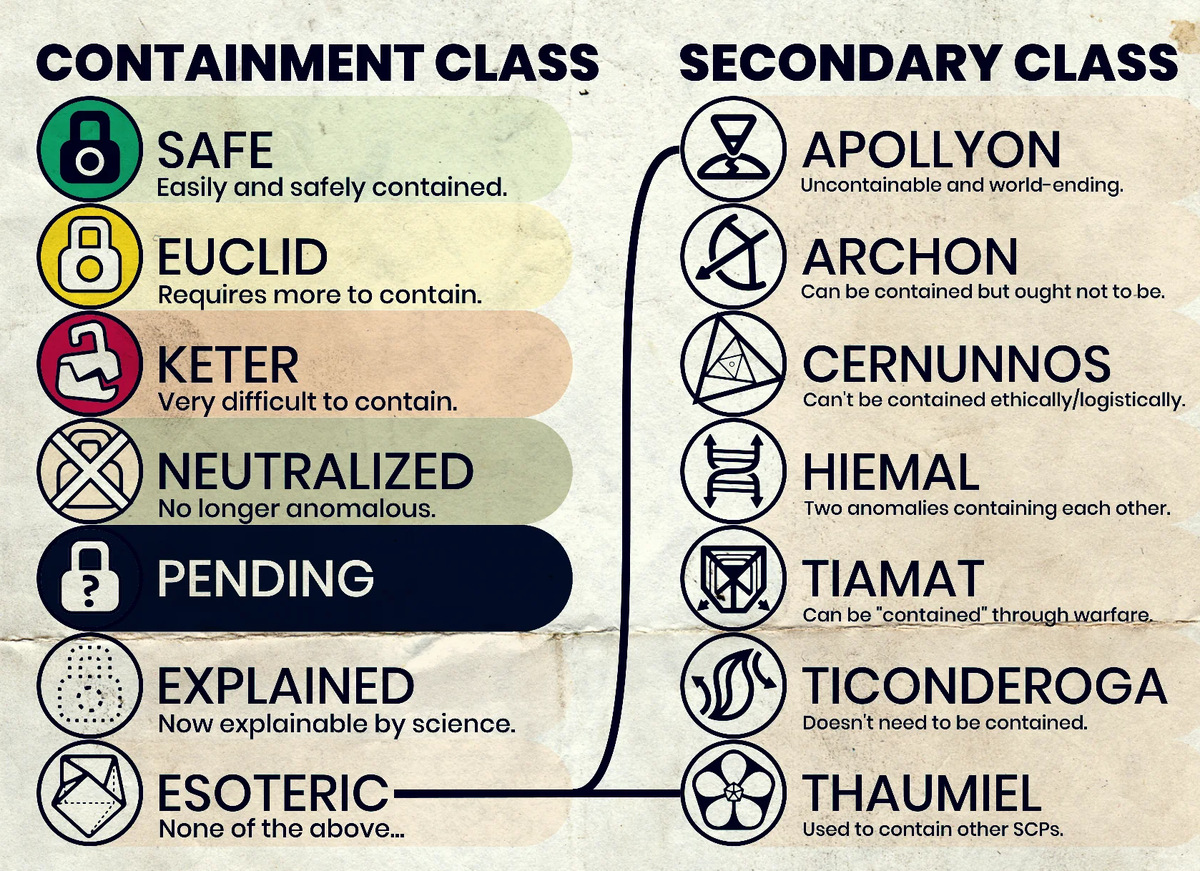
Containerization is the standard for isolating anomalous materials
Most people coming into this field learn the basics but miss how actual containment decisions are made in practice. You read the documents, you see Safe, Euclid, Keter, and you think that covers it. It does not. The real work happens in the gap between what the file says and what the entity actually does when you are not watching. I spent six years in logistics and protocol design before moving into containment review. One of the things that always trips up new researchers is the assumption that a Safe-class designation means the object is stable. It does not. It means we currently understand how to keep it contained. Stable is a different word entirely and the Foundation distinguishes between them for good reason.The Ultimate Guide To Understanding Scp Classes Containment Risks And Protocols
The three primary classes exist as a shorthand system for risk assessment and resource allocation. Safe objects do not actively resist containment and their anomalous properties are understood well enough that protocols can be written with confidence. Euclid objects either cannot be fully predicted or actively attempt to avoid containment. Keter objects represent severe containment challenges, usually due to unpredictable behavior or properties that resist current technological solutions. There are additional designations that appear less frequently but matter just as much. Thaumiel objects are used for containment of other anomalies, often creating a recursive loop where one SCP contains another. Neutralized means the anomalous properties have been permanently or irreversibly lost. Explained covers cases where an anomaly was found to have a mundane origin after thorough investigation. Apollyon describes entities that cannot be contained and will result in existential threat if they escape, though the term itself is rarely used in official documentation.Here is what nobody tells you about the class system: it is dynamic. An SCP can move from Euclid to Safe if we develop better understanding, or from Safe to Euclid if we observe previously unknown behavior. I reviewed a case once where an object classified as Safe for four years suddenly demonstrated Euclid properties after a staff member left a door open for seventeen seconds. The revision took three weeks and required a full behavioral analysis. The original researchers insisted the change was premature. It was not.
Containment protocols vary enormously depending on the classification, but some principles remain consistent across all of them. Physical barriers are the baseline, whether that means reinforced walls, electromagnetic locks, or simple locked rooms with keycard access. Secondary layers exist to catch failures in the primary system, and tertiary layers exist to catch failures in the secondary system. You should never build a containment cell with only one layer of defense. Thaumiel-class objects operate on a different principle. They are not contained in the traditional sense. They are utilized. The resources that would go into containing another SCP are instead directed toward maintaining the Thaumiel object's own stable state. This creates a dependency relationship that most junior researchers find uncomfortable. You are trusting one anomaly to contain another, and if your calculations are wrong even slightly, you lose both. I encountered a specific edge case that I still think about. We had a Euclid-class entity that responded to linguistic cues in ways our documentation did not capture. The containment protocol explicitly stated verbal interaction was restricted to Level 2 personnel and above, but it did not account for the entity's sensitivity to specific phonetic patterns in written language. Someone left a memo on a whiteboard in the observation room. The entity parsed it, followed the implied instructions in the memo, and breached containment. Not dramatically, just walked out the front door while security was checking monitors in another wing. The workaround was to treat all written communication within three hundred meters of the containment cell as potentially anomalous. That meant no whiteboards, no sticky notes, no digital displays without encryption and audit logging. It cut our operational efficiency by roughly forty percent but eliminated the vulnerability. I recommended this after the incident. Some people in administration pushed back, saying it was overkill. It was not. Euclid classification carries a particular risk that beginners underestimate. The unpredictability factor means your protocols will have gaps. You write a procedure for scenario A, but the entity does scenario B. The standard response is to expand the protocol, but expanding protocols too aggressively creates a second problem: personnel cannot memorize and execute complex procedures under stress. I have seen teams freeze when an SCP event triggered because they were trying to recall which version of a twelve-page protocol applied to their specific situation. The solution is layered simplicity. Keep your primary response actions on a single card, no more than five steps, designed to be executed without reference to secondary documentation. The detailed protocols exist for follow-on actions and for training purposes, but the immediate response must be muscle memory level. This reduces reaction time from an average of forty-five seconds to about twelve seconds during simulated breach events. The difference matters more than people expect. Keter-class containment demands the highest resource allocation and the most rigorous protocol enforcement. These entities typically have one or more of the following characteristics: high intelligence, ability to manipulate probability or reality, capacity for replication or self-repair, or properties that actively degrade the containment environment itself. I worked on a Keter review where the containment chamber's structural integrity decreased by approximately two percent per day due to passive anomalous effects. We had to rotate the facility's load-bearing components every ninety days to prevent catastrophic failure. Nobody outside the team noticed for eighteen months. The counter-intuitive insight about Keter containment is that absolute security is not always the optimal strategy. Sometimes allowing controlled minor breaches lets the entity expend its energy on trivial escapes rather than saving everything for a coordinated major event. I know this sounds reckless and it does require careful calibration, but I have seen two separate Keter-class facilities adopt this approach with measurable success. One reduced its major breach attempts from once every fourteen months to once every thirty-one months after implementing controlled release protocols. Safe-class objects deserve respect too, and not everyone gives them that. The complacency risk is real. I reviewed an incident where a Safe-class SCP caused three fatalities because the response team treated it with the same caution level as a non-anomalous object. The entity's anomalous property was conditional and only activated when specific environmental parameters were met. The team had never read the full conditions section of the containment file. They should have. The file was available on the network. They did not access it. When writing or reviewing containment protocols, start with the worst-case scenario and work backward. Determine what has to happen to prevent the worst outcome, then build the layers that make that happen. This approach catches gaps that a linear review process misses. A linear review goes through the document in order and checks each section for completeness. Worst-case-first review identifies the critical failure modes and verifies that protocols exist to address each one. It takes longer initially but catches issues that would otherwise surface during an actual breach event. Documentation quality directly affects containment effectiveness. I have seen protocols so poorly written that two different sites interpreted the same document in opposite ways, leading to contradictory actions during a joint response exercise. The fix was implementing standardized terminology and requiring that all protocols pass a readability test before publication. Not a standard reading level test, something more specific that checks for unambiguous procedural language. Ambiguous language like "secure the area" means different things to different people depending on their training and experience. "Lock all reinforced doors and verify through biometric scan" means the same thing to everyone. The resource cost of high-tier containment is one of the most overlooked factors in Foundation operations. A single Keter-class containment facility can consume funding that could support ten Euclid sites or fifty Safe sites. This creates a tension between individual object priorities and systemic security. The administrative decision-making process attempts to balance this through risk-weighted allocation, but the math is never clean. I have sat in meetings where we had to choose between upgrading containment for one Keter object and adding a second containment layer for five Euclid objects. The recommendation went to the O5 Council. The decision took six weeks. Personnel rotation schedules matter more than most administrators acknowledge. Continuous exposure to high-anomaly environments degrades performance, even for trained researchers. I tracked turnover and error rates across three sites and found a clear correlation: after eight consecutive months in a Keter-class designation facility, response accuracy dropped by approximately twenty-two percent. The drop accelerated after fourteen months. Mandatory rotation every twelve months kept accuracy above the threshold. Sites that pushed to eighteen months saw a steeper decline that recovery from required three weeks of retraining per affected individual.New classification designations have been proposed periodically over the years. The discussion around these proposals is not always productive because the existing system works well enough that changing it requires significant justification. The current classes handle the vast majority of documented anomalies without modification. When edge cases do arise, temporary designations are used until the situation stabilizes or the anomaly is resolved. This pragmatic approach prevents bureaucratic bloat while maintaining operational flexibility.
If you are entering this field, spend time studying historical breach reports before you rely on current protocols. The patterns in how containment failed across different decades and different site configurations teach you more than any single document can. You will start noticing that the same mistakes recur at different scales, and that recognition helps you anticipate failures before they happen. The Foundation has been operating for long enough that we have seen almost every plausible containment failure mode. Learning from those records is one of the most valuable things a new researcher can do. Training simulation frequency correlates with real-world response quality. Sites that run monthly breach simulations with randomized SCP parameters maintain significantly higher readiness levels than sites that run quarterly or annual drills. The monthly cadence keeps procedures fresh and forces personnel to adapt to novel variations rather than rehearsing the same scenario repeatedly. I observed a site that switched from quarterly to monthly simulations and saw its average breach response time decrease from eighty seconds to thirty-four seconds over a six-month period. The change was not complicated, just consistent.