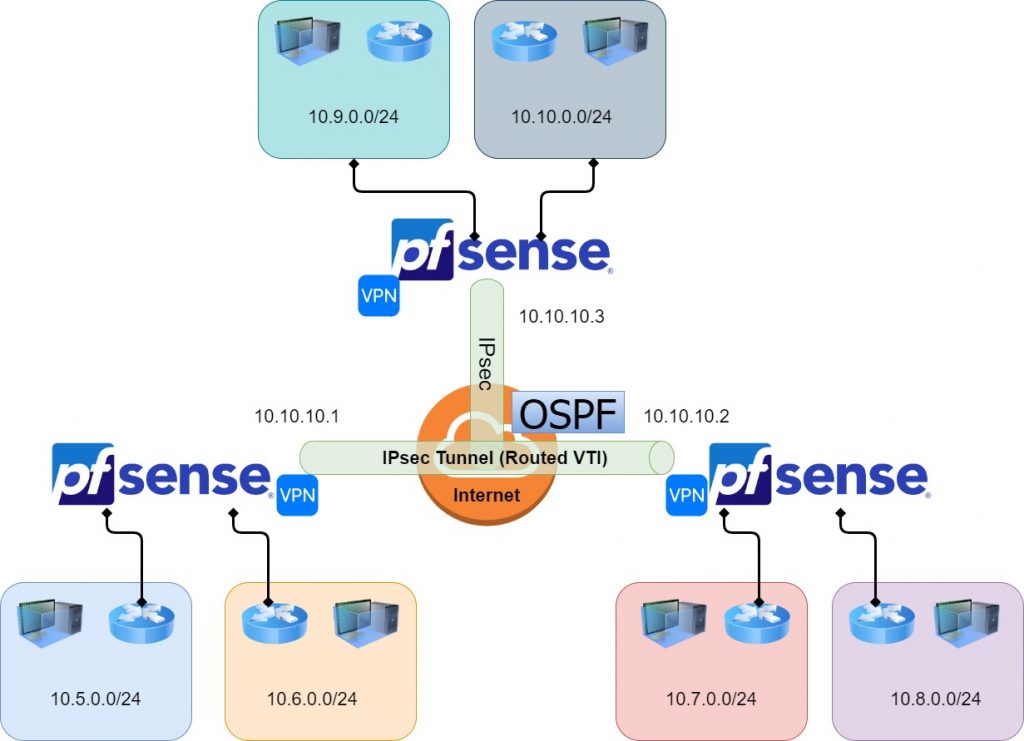
Setting Up OSPF on pfSense Actually Works Differently Than You Expect
Most people come to pfSense thinking they can just enable OSPF and watch the routes magically appear. That is not how it works. The Free BSD underpinning means ospfd does not behave the same way as something like Cisco IOS or even FreeBSD's own older routing daemons. It runs as a package, yes, but the configuration model is its own thing. You will need to understand the basics of how Open Shortest Path First actually functions before the pfSense implementation makes any sense. I have spent years dealing with OSPF across different router platforms. When I first moved to pfSense, I expected the behavior to be roughly similar. It was not. The package available in the pfSense repository is the FreeBSD version of Quagga or FRR, depending on your version, and the quirks are specific. I ran into a problem where two pfSense nodes in a VRRP cluster would each advertise the same network into OSPF, but the route preference was completely inconsistent because both instances thought they were the primary. The fix was not obvious. I had to bind OSPF to a specific virtual IP rather than letting it pick up whichever interface was active at the time. That detail alone cost me about four hours of troubleshooting on a client network last year. Let me walk through what you actually need to do.
Installing the Routing Package
In pfSense 2.6 and later, you go to System -> Package Manager, find the routing package, and install it. It will pull in the FRR (Free Range Routing) dependency. Before 2.6, it was Quagga. The difference matters because FRR has slightly different configuration file paths and a few more protocol options. If you are upgrading from Quagga to FRR, do not skip the step where you export your existing configuration. The formats are close but not identical, and you will lose stub network definitions if you do not handle the migration manually. Once installed, navigate to Services -> FRR. You will see tabs for BGP, OSPF, RIP, and other protocols. Click the OSPF tab. You will notice the interface is spartan. There are no wizards. There are no pre-configured examples.
Configuring the OSPF Process
The first thing you configure is the OSPF process ID and area assignments. The process ID is local to that pfSense box. It does not need to match any other router. The area numbers, however, must be consistent across your entire OSPF domain. Area 0 is the backbone. That is standard. Do not skip it or assign multiple backbone areas. OSPF does not allow that, and pfSense will not warn you nicely if you try. Under the network field, you enter the subnet and wildcard mask. This is not a netmask. It is a wildcard mask, which is the inverse of a subnet mask. A /24 becomes 0.0.0.255. This trips up more people than anything else in the setup process. I have seen admins put 255.255.255.0 here and wonder why their interfaces never come up in the OSPF adjacency table. The wildcard mask must match exactly what you would use in an access-list.
Get the Full Details

Authentication and Neighbor Relationships
OSPF supports plain-text and MD5 authentication, and FRR on pfSense supports both. Plain-text is fine for isolated lab networks. MD5 is what you use on any production link. The key ID and key string need to match on both ends. If they do not, the adjacency will stay in the INIT state. You will see the neighbor listed in the routing table output, but no routes will be exchanged. I spent an afternoon once troubleshooting this exact issue on a site where a contractor had configured MD5 on one end and nothing on the other. The logs are not helpful here. You have to look at the adjacency state directly. One thing the pfSense documentation does not cover well is the interaction between OSPF and CARP. If you are running dual pfSense boxes in a high availability pair, OSPF will advertise routes from both boxes simultaneously unless you control which box is the master for each interface. The default behavior is to advertise from whichever box currently holds the CARP VIP for a given network. This can cause suboptimal routing or even routing loops in certain topologies. The workaround is to use OSPF interface priorities so that one box always wins the DR election and controls advertisement for shared broadcast segments. Another issue is MTU mismatch. OSPF requires matching MTU on the link between neighbors for the adjacency to complete past the Exstart state. If one side is on a tagged VLAN with a lower MTU and the other is not, you will see neighbors briefly come up and then drop. The kernel log on pfSense will show LSA retransmission failures. Checking the physical interface MTU on both ends is something most people overlook.
When OSPF Is Not the Right Choice
pfSense handles OSPF adequately for small to medium networks. But there are hard limits. If you are managing more than a few hundred routes, the single-threaded nature of the FRR daemon on pfSense can become a bottleneck. Memory usage scales with route count, and on a standard pfSense appliance with 4GB of RAM, you are looking at comfortable operation up to maybe 5,000 routes before performance degrades noticeably. For larger deployments, you should be running dedicated routing equipment with proper hardware forwarding, not a software router on commodity hardware. Static routing or a managed switch with basic RIP support may be the better choice if your network is small and stable. OSPF adds complexity that you do not need unless you have multiple paths, redundancy requirements, or a need for automatic failover. Dynamic routing is not automatically better than static routing. It is only better when your topology justifies it.
Monitoring and Troubleshooting
Once your OSPF is running, do not assume it is working because the service appears enabled. Check the actual adjacencies. The command line interface through Diagnostics -> Command Prompt is useful here. Run show ip ospf neighbor and verify that every expected neighbor shows FULL state. If a neighbor is stuck in EXSTART or two-way, check the MTU and authentication settings first. Then check the area configuration. Then check that the interfaces are actually in the same subnet. For ongoing monitoring, the pfSense log at /var/log/frr/ospfd.log will record adjacency changes and route updates. This log rotates, so set up a remote syslog server if you need historical data. The web interface does not retain old log entries beyond what is visible in the status page.

A Note on Package Updates
pfSense updates the FRR package periodically. After a major version jump, OSPF configuration files may need migration. Always backup your config before updating. I have had two separate incidents where an FRR update broke OSPF because the new version changed how it handled certain route-map syntax. Restoring from backup took minutes. Rebuilding the configuration from scratch would have taken hours. This is the main practical reason to keep your exported configuration files organized and labeled with dates. OSPfon pfSense is functional and reliable when configured correctly. It is not the most polished routing implementation available, but it works for the vast majority of small business and lab environments. The learning curve is steeper than the web interface suggests, and the documentation assumes a level of networking knowledge that not everyone has. Start simple. Get one adjacency working. Then add complexity gradually.