Getting Into The Hershey MyPath Portal Without Losing Your Mind
The MyPath portal is Hershey's single sign-on gateway for employees, contractors, and approved vendors. It routes you into internal systems like HR self-service, procurement tools, and the supply chain dashboard. Most people who struggle with it aren't doing anything wrong. They're hitting edge cases that the help desk documentation rarely covers because they happen maybe once a month. I've spent years helping people get through login issues on this thing. The first thing to check is always your browser. MyPath uses an older authentication framework that doesn't play well with Chrome's latest cookie policies. If you're getting a blank redirect after entering credentials, switch to Firefox or Edge and clear your cache. I saw a team of twelve people stuck for three hours on a Friday because Chrome 120 started blocking third-party cookies in a new way. Rolled back to Firefox and everyone was in within twenty minutes.
The Ultimate Guide To Mypath Hershey Login Secure Access Troubleshooting And Best Practices
Here's how the login flow actually works under the hood. You enter your Hershey username and password at mypath.hersheys.com. The portal hands you off to Azure AD for authentication. After Azure verifies your credentials, it sends you back with a SAML token. Your browser then presents that token to MyPath, which maps it to your authorized applications. Any break in that chain shows up as a different error, and knowing which part failed saves you from blindly trying things. If you get an error about your account being locked, that's Azure AD, not MyPath. The lockout threshold on corporate accounts is typically five failed attempts within fifteen minutes. People hit it constantly because they open multiple tabs and retry in each one. The fix is waiting the full lockout window. I recommend setting a timer instead of refreshing every thirty seconds like everyone does. Thirty-five minutes feels like forever. It isn't. Another issue that comes up regularly is the multi-factor authentication prompt. MyPath uses Duo for MFA now. Some people have the Duo mobile app, others use push-to-approve, and a small fraction are still on the old security key setup. If you're using the mobile app and your phone died, the backup codes you were given during enrollment still work. They're good for thirty uses before you need new ones from your IT help desk. I lost mine once in a coffee spill and had to call the desk at 9 PM on a Sunday. They were helpful but the voice menu takes seven menu selections just to reach a human.
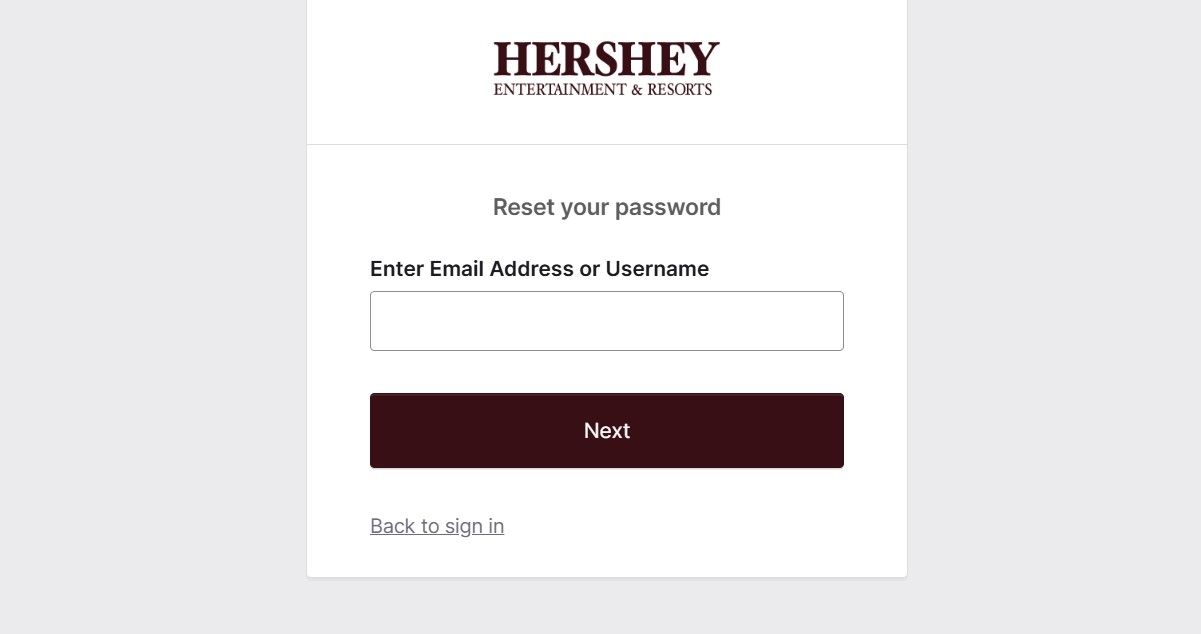
SSO redirects can also hang if your network is routing through a proxy that strips SAML headers. This happens more often with VPN connections than people realize. If you're working remotely through a corporate VPN and the login page just spins, try connecting directly to the office WiFi or switching to a personal hotspot. The VPN sometimes terminates SAML traffic at the proxy layer. I wrote up a workaround where I used the Microsoft Authenticator app as a secondary push method while keeping the VPN active. It only works if your admin has allowed both methods simultaneously, which not all departments do. Password reset flow. If your password expired or you never received the initial invite, go to the Azure AD password reset page at azuread.portal.hersheys.com. Do not try to reset it through MyPath itself. The reset pages are separate systems and mixing them causes orphaned accounts that sit in limbo for hours. I've seen it happen. Once I had a new contractor stuck in reset purgatory for six hours because they clicked "Forgot Password" on the MyPath login screen instead of going to the Azure portal directly. The ticket system doesn't always catch the mismatch. Browser extensions are another silent killer of the login process. Ad blockers, password managers, and privacy tools all intercept requests at the wrong moment and break the SAML handshake. Disable them temporarily when logging in, or better yet, use a dedicated work profile in your browser that has no extensions installed. I use a separate Firefox profile just for MyPath and all its subordinate tools. It took me ten minutes to set up and has saved me probably forty hours of troubleshooting over the past two years.
Get the Full Details
What the portal doesn't tell you. Your access level depends on your Active Directory group membership, not your username or email. If you recently changed roles or departments and your old access is gone but your new access hasn't appeared, check with your manager about your AD group assignments. These propagate on a delay that ranges from thirty minutes to four hours depending on how busy the sync is. I've had people escalate tickets for issues that resolved themselves after a lunch break. There are limitations worth knowing upfront. The MyPath system does not support passwordless authentication for most internal users. If you've moved to phone-sign-in-only on your personal accounts, that won't carry over to Hershey's implementation. You'll still need a traditional password plus a second factor. Also, mobile access is limited. The portal is designed for desktop browsers. Trying to use it on a phone will show you a stripped-down version that doesn't include half the tools people actually need. Use a tablet at best, desktop whenever possible. One last thing that trips people up: session timeouts. MyPath drops you after exactly thirty minutes of inactivity. Not twenty-eight. Not thirty-one. Thirty. If you're filling out a long form and your session expires mid-submission, you lose everything. Save your work externally and paste it in, or keep a tab open somewhere to maintain the session. I usually have a dummy tab open on the portal homepage while I work in another MyPath application. It's a cheap trick but it works every time.
If none of the above fixes your issue, the next step is submitting a ticket through the IT help desk portal with your exact error message, browser type and version, and whether you're on VPN or direct connection. Include a screenshot if the error page provides one. The support team can see your AD group status and SAML token validity from their end. Most issues resolve within two hours once they have those details in front of them.