Signing Out of Gmail When It Actually Matters
You open Gmail, read some messages, and close the tab. Most people assume they're logged out. They aren't. The session persists until it times out or you manually end it, and that distinction matters more than most users realize. I've spent years watching teams get burned by exactly this kind of assumption. The why comes down to session hijacking and credential theft. When you leave a Gmail session active on a shared or public machine, someone can open the browser and land directly in your inbox. That's not theory. I watched an IT admin at a mid-size firm get locked out of his own Google Workspace account because a contractor left a work computer unattended with Gmail open, and a phishing payload harvested the session cookies through a malicious bookmark that had been slid into the toolbar. The workaround was brutal. We had to go through Google's account recovery flow, verify identity across two different email addresses, wait forty-eight hours for the session locks to propagate, and rotate every single credential tied to that Google account. The admin lost access to Drive, Calendar, and YouTube Analytics for three days. All because nobody signed out.
How to Log Out of Gmail Properly
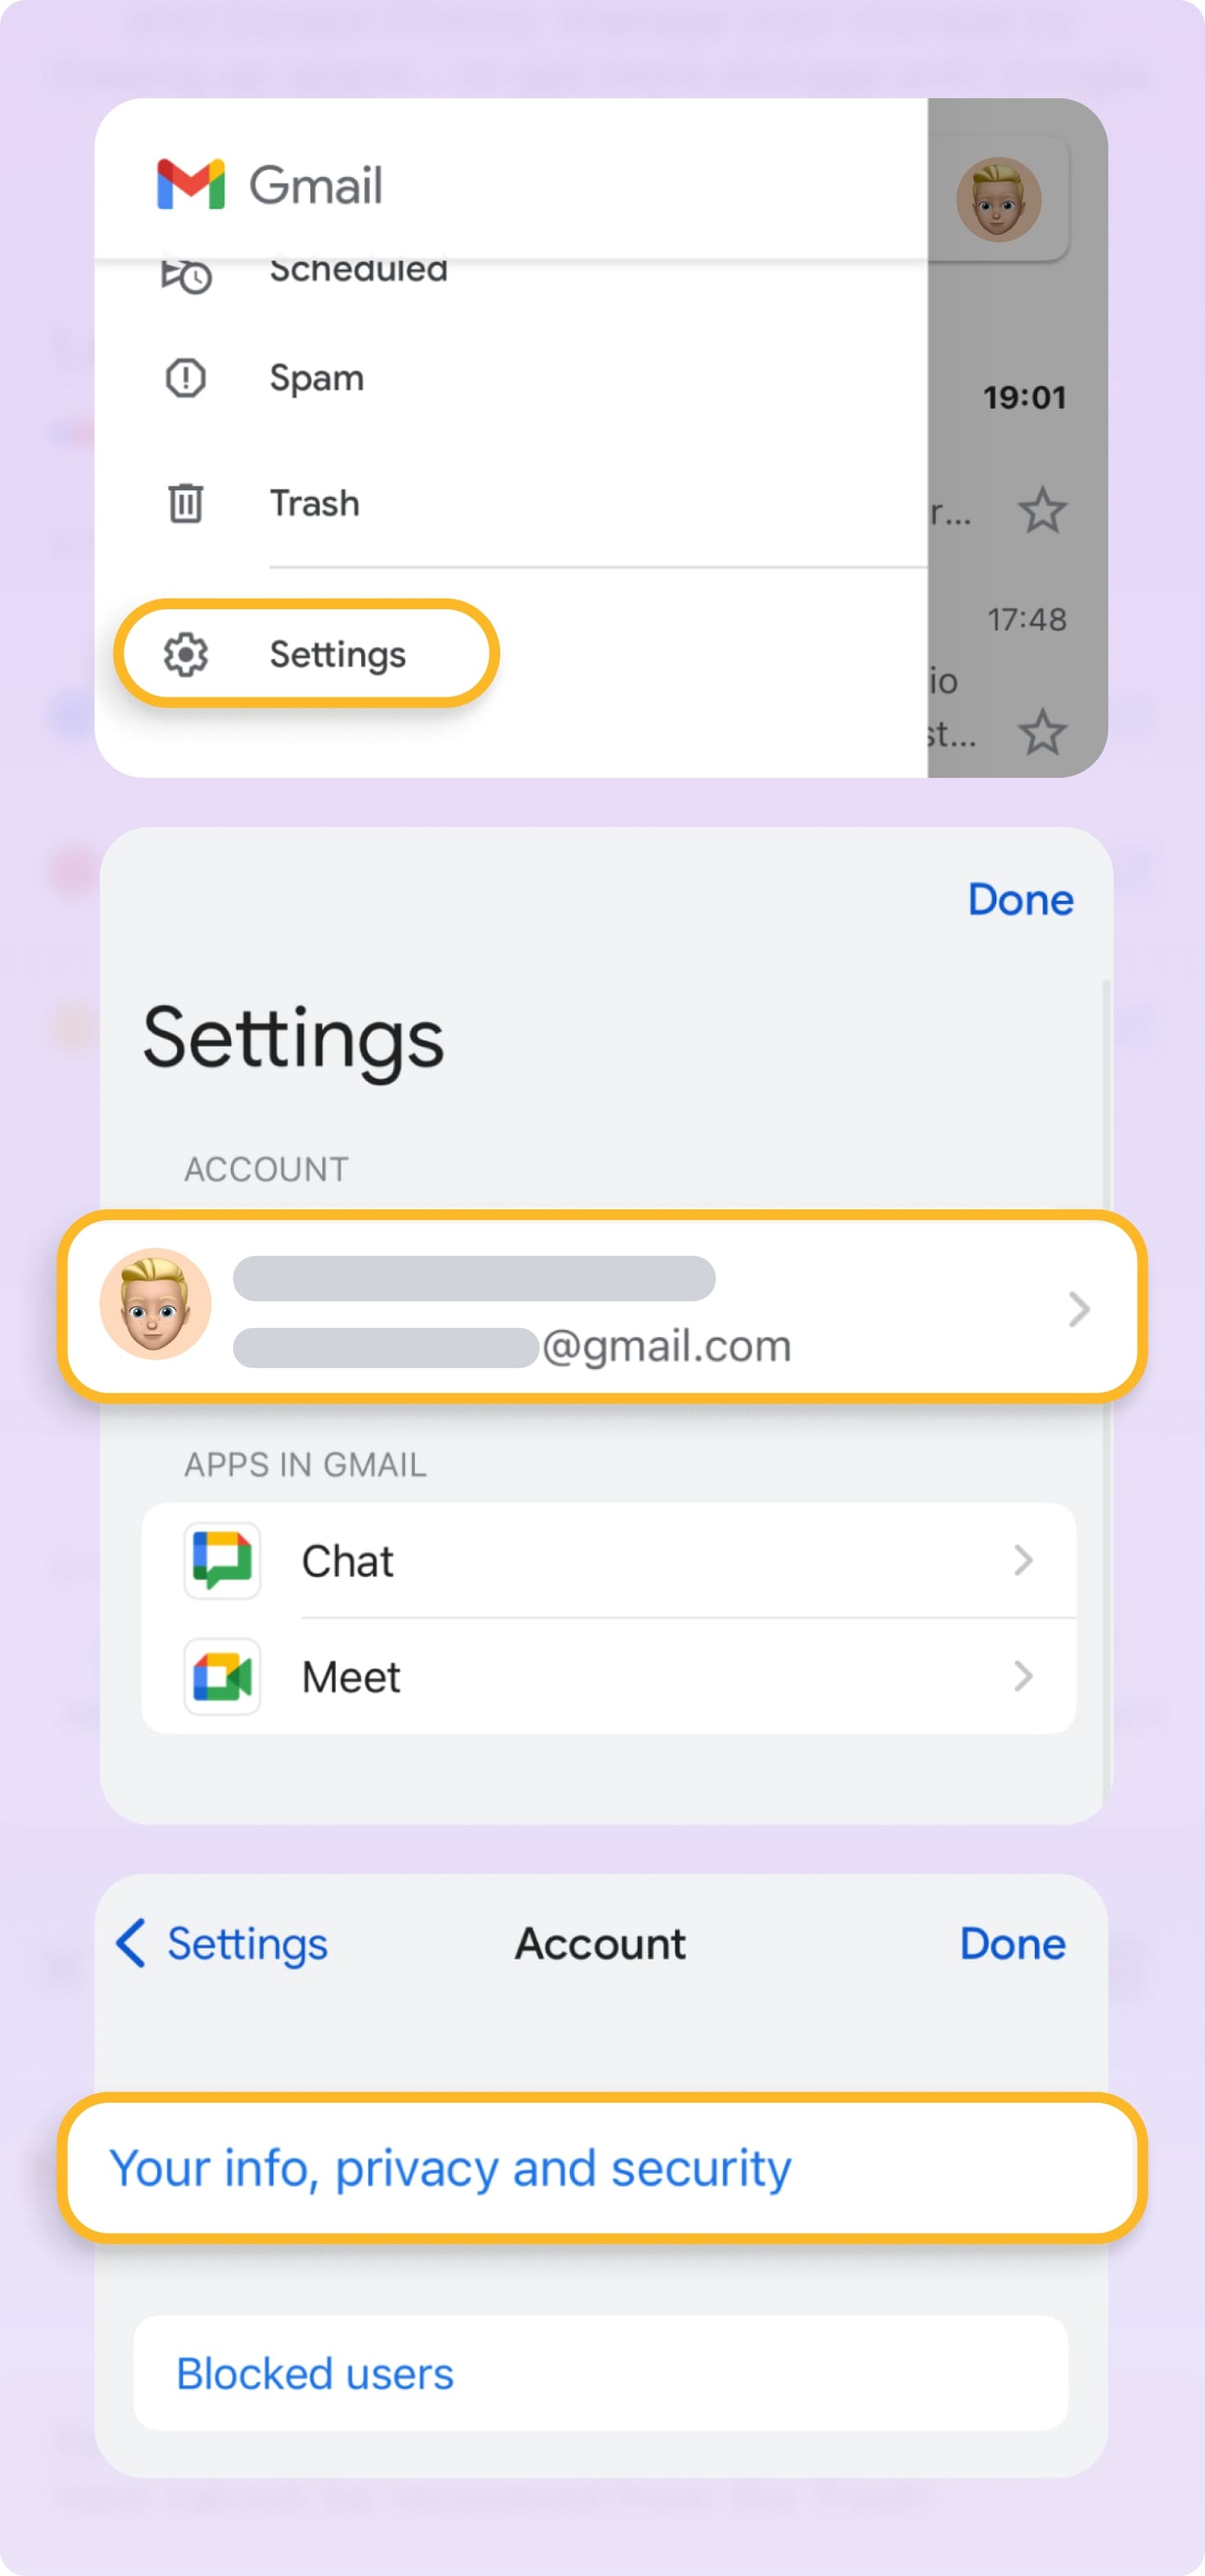
Open Gmail in any browser. Click your profile picture in the upper right corner. A dropdown appears. Select Sign out. That's it. The page redirects to the Google sign-in screen. If you're using a shared computer, close the browser window afterward to kill any remaining tabs that might auto-reopen on launch. On mobile, the process differs slightly. Open the Gmail app. Tap your profile icon in the top right. Tap Manage accounts on this device. Find the Gmail account you want to remove. Tap Remove. This deletes the account from the app entirely rather than just ending a session. If you're sharing a phone and only need to log out temporarily, you can use App Lock or the system's built-in screen pinning features instead, but removing the account is the only guaranteed method on iOS and Android. For Google Workspace accounts, administrators have a separate concern. Device management policies controlled through the Admin Console can enforce automatic session timeouts or remote wipe capabilities, but those settings only apply if MDM is properly configured. A lot of organizations think they have this covered when they actually don't. I audited a company last year where the Workspace admin console showed session controls enabled, but the endpoint configuration was pointing to a deprecated policy template that hadn't been pushed to devices in eighteen months.
Why Manual Sign-Out Is Still Necessary Despite Automation
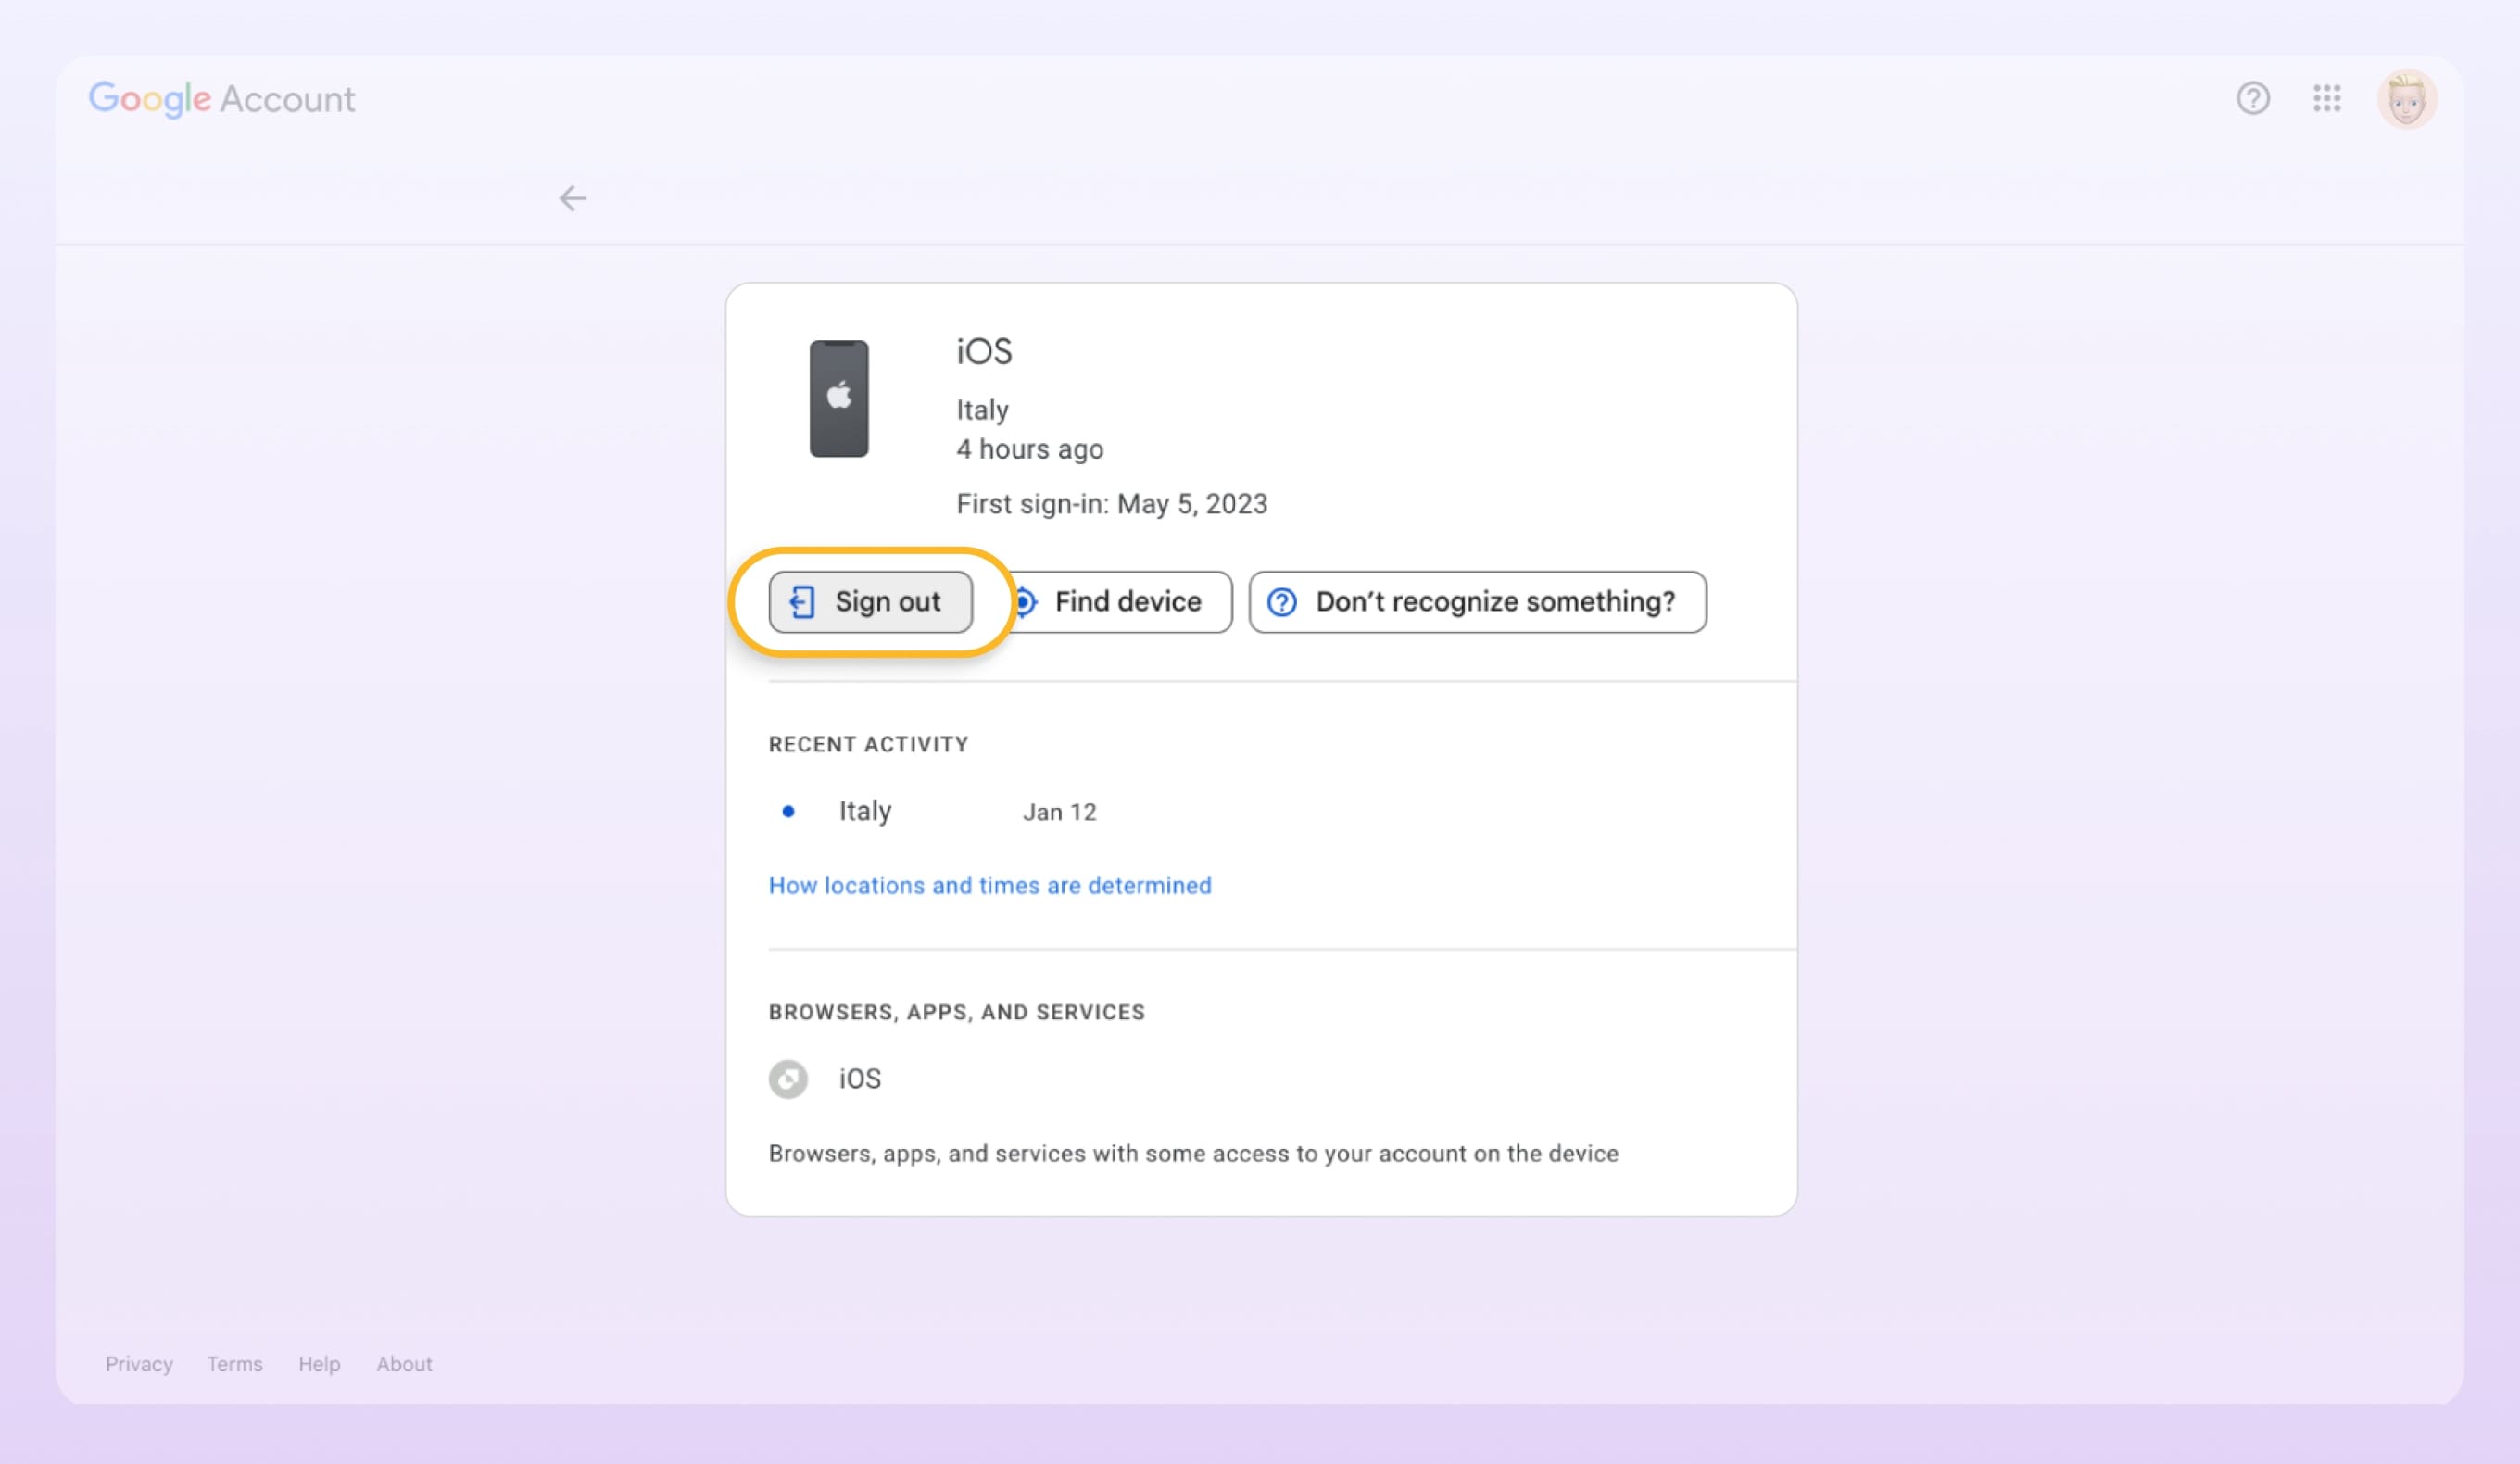
Google implements idle session timeouts, but the exact duration varies by browser, account type, and even geographic IP reputation. A personal Gmail account on Chrome might hold a session for fourteen days before requiring re-authentication. A Workspace account behind a corporate SSO policy might drop after two hours. These numbers shift constantly based on Google's internal risk scoring, which means you can't rely on automation alone. The only consistent way to guarantee a session is terminated is to actively sign out. There's also the question of second factors and trusted devices. When you sign in on a new device, Google marks it as untrusted until you complete verification. But existing trusted devices retain session tokens until explicitly removed. I once helped a user recover a compromised account where the attacker had been accessing mail through a trusted session on a device the user had forgotten about. It was an old laptop sitting in a closet. Removing that device from the account security settings was the only thing that actually stopped the unauthorized access.
Get the Full Details

Common Mistakes That Undermine Your Logout Routine
People often confuse signing out of Gmail with clearing browser cookies. These are not the same action. Clearing cookies may remove a session token, but it also destroys saved preferences, calendar data, and potentially your ability to stay signed into other services. Signing out of Gmail specifically ends only that session without collateral damage to your other browsing data. Another frequent error is assuming that incognito or private browsing mode handles logout automatically. It does not. Incognito sessions expire when you close the window, which is technically a form of forced logout, but the boundary between personal and private browsing gets blurry fast. Users routinely open personal Gmail inside an incognito tab out of habit, then close it and assume security. That works, but it's easy to accidentally switch back to a regular tab where the original session is still live. Mobile users make a different mistake. They lock their phone screen and walk away, believing the app is secured. The Gmail app keeps its session active regardless of screen state. Locking the phone does not log you out. It only encrypts the display. Someone with physical access to an unlocked phone or a device with a weak PIN can open Gmail without re-authenticating.
Best Practices for Maintaining Session Security
Start with device hygiene. Every device you use to access Gmail should have a lock screen, a PIN or biometric gate, and automatic screen timeout set to no more than two minutes. These are baseline requirements, not optional enhancements. I've seen enterprise environments where analysts used shared workstations with PINs set to 1234 or 0000, which effectively nullified every other security control in place. Use Separate Accounts or profiles for different contexts. Personal Gmail should live in a separate browser profile from work or shared-use scenarios. Browser profiles keep sessions completely isolated. Switching profiles is faster and more reliable than juggling multiple Gmail tabs or trying to remember which account is signed in where. I manage four distinct Chrome profiles myself and haven't had a cross-contamination incident in over three years. Enable two-step verification on every Gmail account, including personal ones. This is non-negotiable. A strong password alone does not prevent session theft. If someone obtains your session cookie through XSS, a network attack, or physical access, they bypass your password entirely. Two-step verification forces a second authentication factor that session tokens cannot replicate. Google's Advance Protection Program adds another layer for high-risk users, requiring a physical security key, but that's overkill for most people.
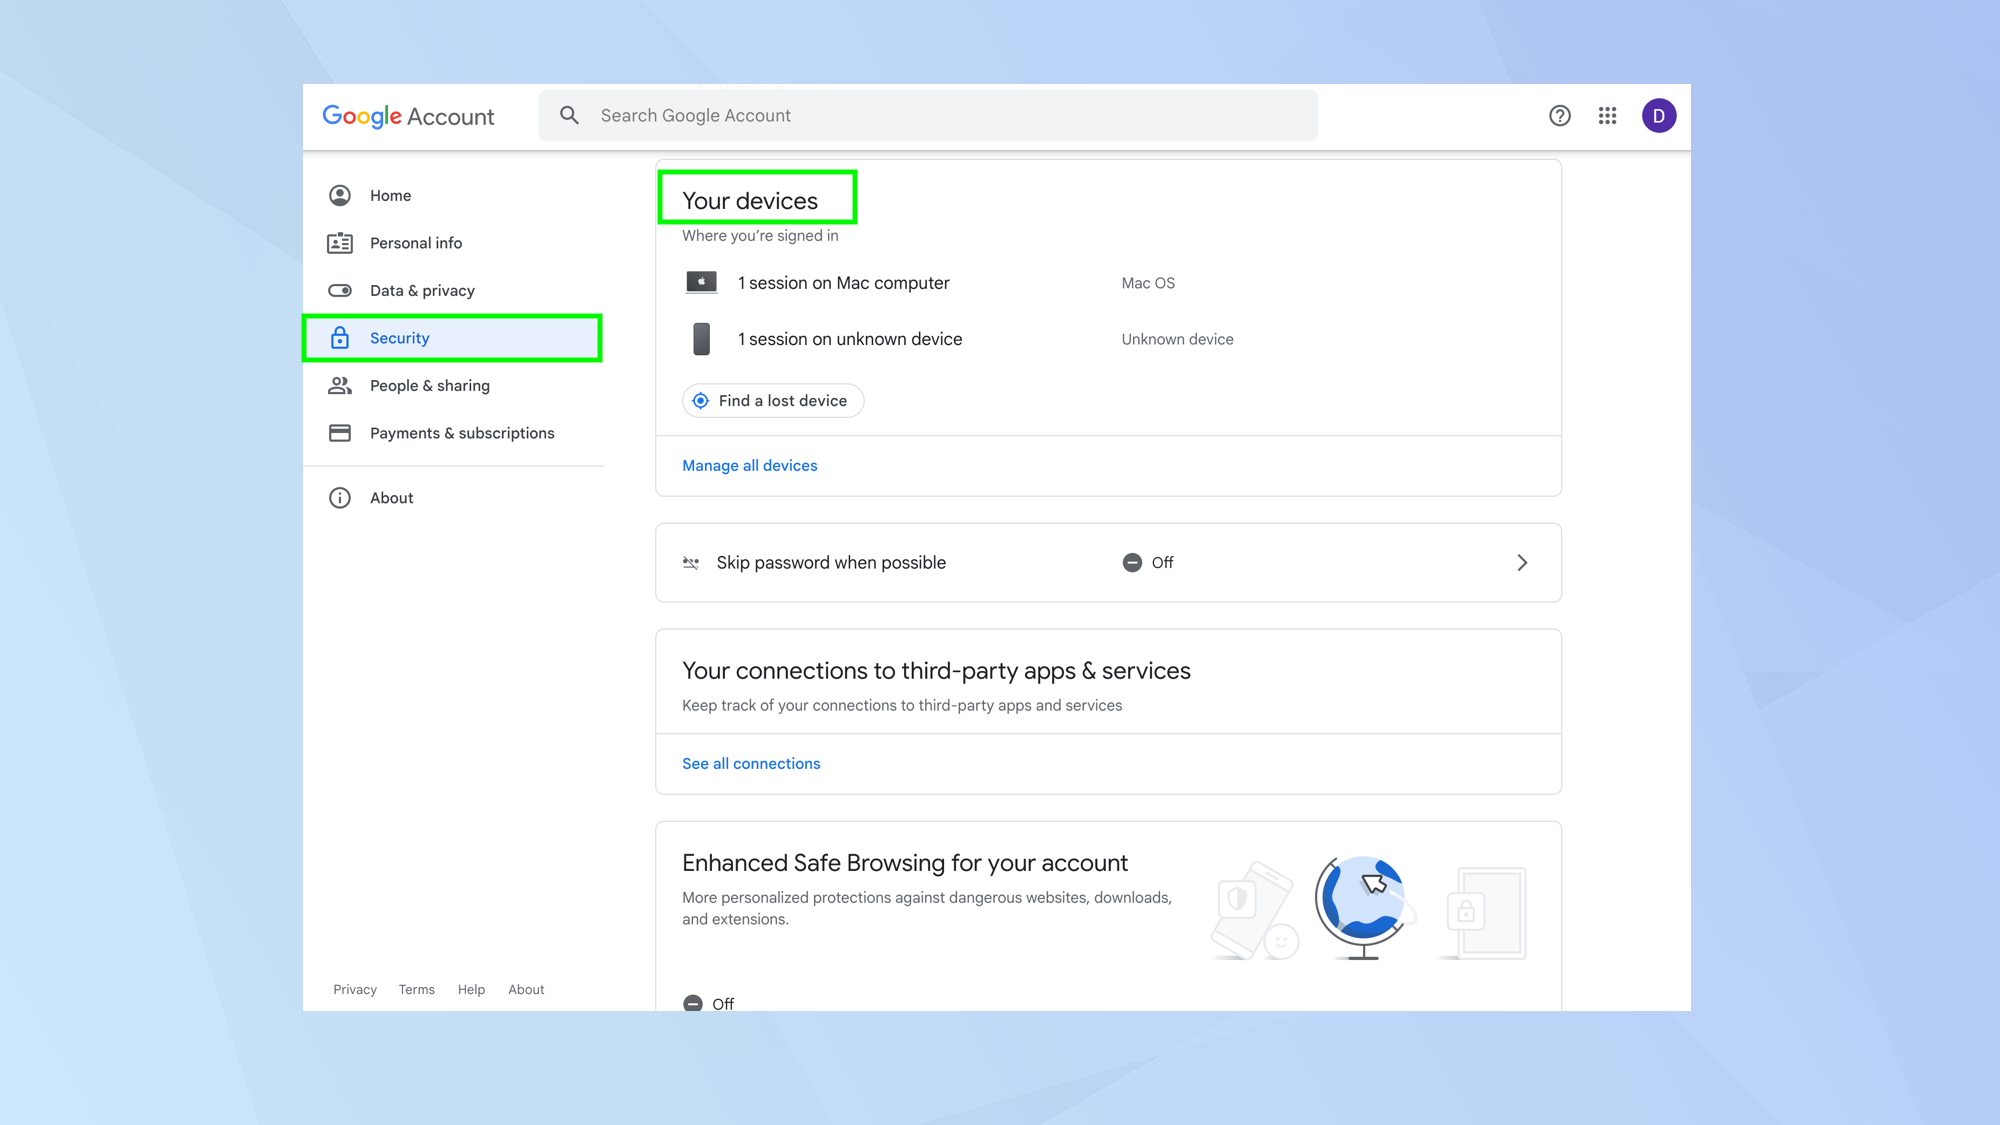
Review active sessions regularly. Go to your Google Account security settings. Look for the Your devices section. You'll see a list of every device and browser currently holding an active session. Remove anything you don't recognize or no longer use. I check this weekly. It takes about thirty seconds and catches problems before they become incidents. Be aware of the limitations here. Google's session management is opaque. There's no public documentation showing exactly how long a session lasts under different conditions, what triggers a forced re-authentication, or how session tokens are transmitted between Google's infrastructure. This lack of transparency means you should treat every session as potentially persistent until you actively terminate it. Assuming otherwise is a risk calculation most people don't make consciously. If you're managing accounts for other people, like family members or employees, consider using Google Family Link or Workspace management tools respectively. These provide centralized session control that individual users often neglect. But even with those tools in place, the manual logout step remains the single most effective action you can take, because automated controls have failure modes and configuration drift that manual actions don't.