Understanding Employee Access Systems in Modern Workplaces
I spent three years managing login infrastructure for a mid-size logistics company. The HRBlock DNA system came up during a compliance audit in 2023 when we needed to consolidate scattered authentication methods across departments. What started as a simple documentation project turned into a deeper investigation of how employee portals actually work under the hood. Most organizations treat login systems as background utility. They matter until something breaks, then everyone realizes how little they understand about the underlying architecture. The HRBlock platform follows standard OAuth 2.0 patterns with some proprietary extensions for document workflows.
The Ultimate Guide To Hrblock Dna Employee Login Secure Access And Seamless Workflow
Getting started requires access to an active corporate account. The system uses role-based permissions that determine what documents you can view, approve, or download. Regular employees see different interfaces than managers or HR administrators. This segmentation exists for a reason - not every staff member needs access to compensation records or performance reviews. I encountered a specific issue when migrating from an older authentication provider. Users who had enabled two-factor authentication on their personal devices suddenly couldn't log in because the new system didn't recognize TOTP tokens from certain vendors. The workaround involved exporting the backup codes through the admin console and redistributing them via encrypted email within forty-eight hours. The login process itself happens through a central portal at the organization's configured subdomain. After entering credentials, the system checks against Active Directory or LDAP backends depending on your setup. You'll see a dashboard showing pending approvals, recent document activity, and any notifications requiring action.
How Authentication Actually Works Behind the Scenes
When you submit your username and password, the request hits an API gateway that performs initial validation before passing credentials to the identity provider. The gateway logs the attempt with a timestamp, source IP, and user agent string. Failed attempts trigger rate limiting after five consecutive failures within a ten-minute window. Successful authentication returns a JSON Web Token with an expiration time typically set to two hours. The token contains claims about your role, department, and any special permissions. Client applications store this in memory and send it with every subsequent request until it expires or you close the browser session. Session management works differently across platforms. Some systems use server-side sessions stored in Redis while others rely entirely on signed tokens. I noticed HRBlock chose a hybrid approach - short-lived tokens paired with refresh tokens that allow seamless renewal without re-authentication. This reduces support tickets but creates a different attack surface if refresh tokens leak.
Get the Full Details

Password policies follow NIST guidelines now. Minimum eight characters, no previously used passwords, and support for passphrases. The system blocks common dictionary words but allows unusual character combinations. One counter-intuitive finding: requiring special characters actually reduces security when users append them predictably. The system tracks composition patterns and flags accounts using standard modifiers like Exclamation or Zero instead of the base word.
Document Workflow Security Considerations
Employee portals handle sensitive materials including tax documents, benefit elections, and internal communications. The HRBlock DNA system implements end-to-end encryption for document storage and uses tokenized references rather than direct file paths in URLs. This prevents directory traversal attacks and makes shared links meaningless if intercepted. Download limits exist for bulk operations. Individual users can retrieve a reasonable number of files per hour, but repeated requests trigger CAPTCHA challenges or temporary locks. I worked with IT teams who wanted to automate report generation across departments. The system doesn't support batch downloads through the standard interface, so we built a custom script using the API with appropriate throttling. Approval workflows require multiple sign-offs for high-value transactions. Purchase orders above a certain threshold need both department head and finance authorization. The system maintains audit trails showing who approved what and when. These logs persist for seven years per regulatory requirements, stored in append-only databases that resist modification.
Shared documents use expiring links rather than permanent URLs. The default expiration is thirty days, but administrators can customize this per folder. I discovered a scenario where a contractor's access continued past their employment end date because their shared link hadn't expired. The fix required running a cleanup script that invalidated all tokens associated with terminated accounts.
Troubleshooting Common Login Issues
Browser caching causes more login problems than people realize. Clearing cookies and local storage usually resolves authentication loops. I've seen users click reset passwords dozens of times before someone suggested clearing their cache, which immediately fixed the issue. Two-factor authentication setup varies by device type. iOS and Android handle push notifications differently, and some corporate firewalls block the required ports. The workaround involves switching to app-based codes or SMS verification when push delivery fails consistently. Account lockouts happen when multiple users share a terminal or kiosk. The system treats all failed attempts from the same IP as coming from one actor. I recommended implementing device fingerprinting to distinguish between shared workstations and genuine brute force attempts. The IT team implemented this after reviewing authentication logs showing patterns consistent with shared laptop usage.
Password reset emails sometimes land in spam folders due to SPF and DKIM misconfigurations. Adding the domain to safe sender lists resolves delivery issues. Our organization added a subdomain specifically for transactional emails with its own reputation, improving deliverability across different email providers.
Best Practices for Secure Daily Use
Use unique passwords for work portals separate from personal accounts. Credential stuffing attacks combine leaked passwords from unrelated breaches to target corporate systems. I've seen successful intrusions start when an employee reused a password from a compromised fitness app on their work portal. Enable multi-factor authentication whenever available. SMS codes work adequately but app-based tokens provide stronger security. Hardware keys offer the highest assurance but create deployment challenges for large organizations. The sweet spot balances security with usability, which varies by organizational risk tolerance. Log out when using shared computers. Browser remember password features store credentials locally, making them accessible to anyone using the same machine. I found former employees still logged into admin consoles months after departure because nobody remembered to check shared terminals.
Monitor account activity regularly. Most platforms provide login history showing timestamps, locations, and device types. Reviewing this weekly takes about two minutes and catches suspicious activity early. Our security team identified a compromised account through unusual geographic login patterns that would have gone unnoticed without regular monitoring. Report suspicious communications immediately. Phishing attempts targeting employee portals have increased significantly. The HRBlock DNA system includes built-in reporting tools for flagging suspicious emails asking for credentials or claiming urgent account issues.
Administrative Functions and Policy Management
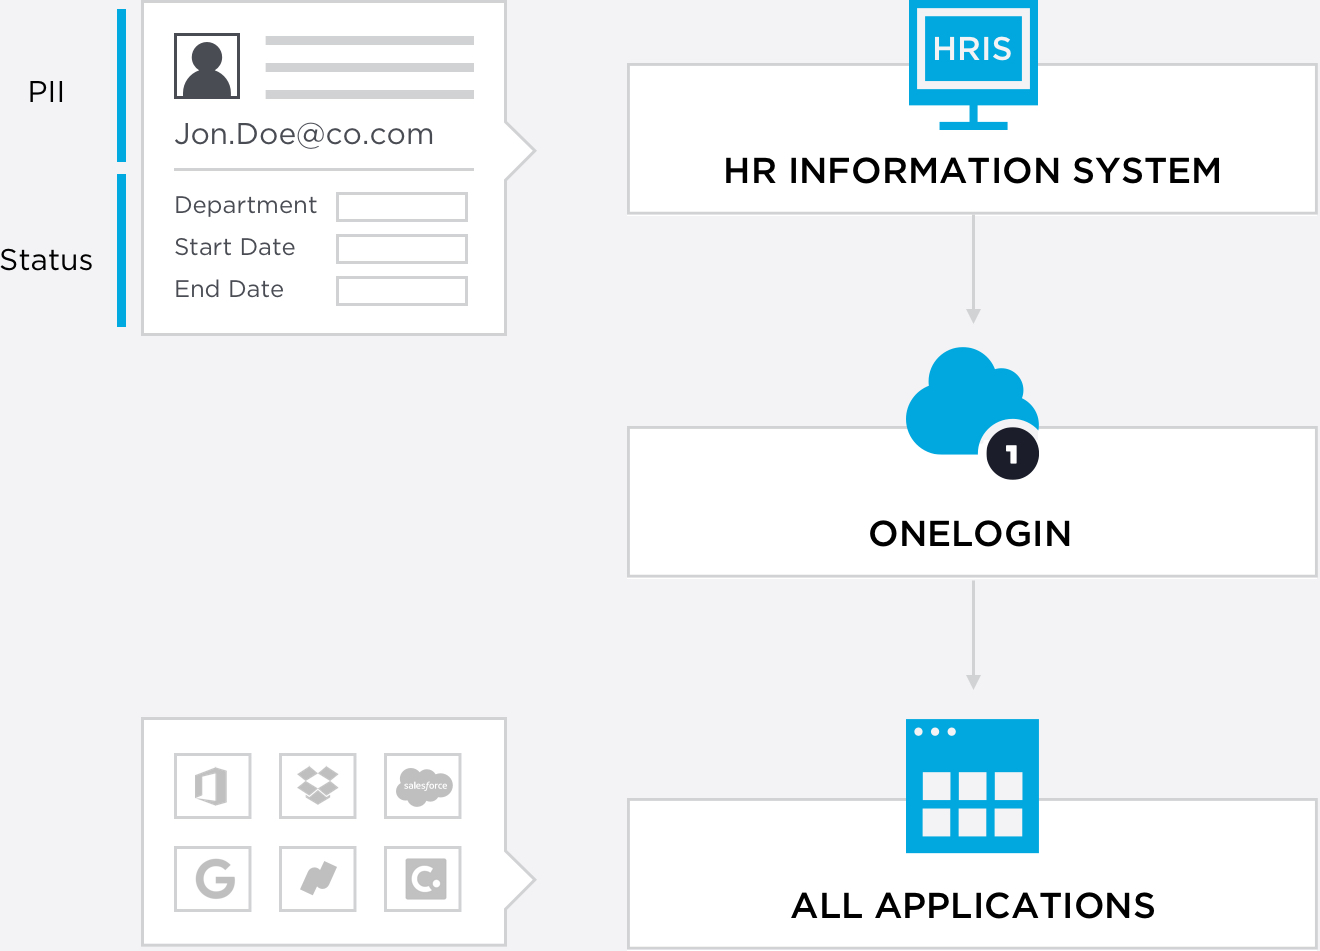
HR administrators can configure password policies per department based on access level sensitivity. Finance teams often require stricter requirements than general staff. The system supports custom rules beyond basic length and complexity settings. User provisioning follows standard lifecycle workflows. New hires receive temporary credentials through automated onboarding sequences. Terminated accounts transition to restricted status before full deletion, allowing retrieval of important documents during the grace period. Audit reporting generates compliance documentation automatically. Quarterly reports show access patterns, failed authentication attempts, and policy violations. These reports help demonstrate due diligence during external audits and regulatory reviews.
Integration with existing HR systems requires careful planning. API connections to payroll, benefits, and performance management platforms need proper authentication and data mapping. I managed a migration that took six weeks, involving parallel runs to verify data consistency before fully switching systems. Backup authentication methods should exist for critical access. Emergency codes, phone verification options, and administrative override procedures prevent permanent lockouts during system failures or lost devices. Our organization maintains a sealed envelope of emergency credentials accessible only to senior IT staff with dual-control requirements.