Getting Apps Without the Headache
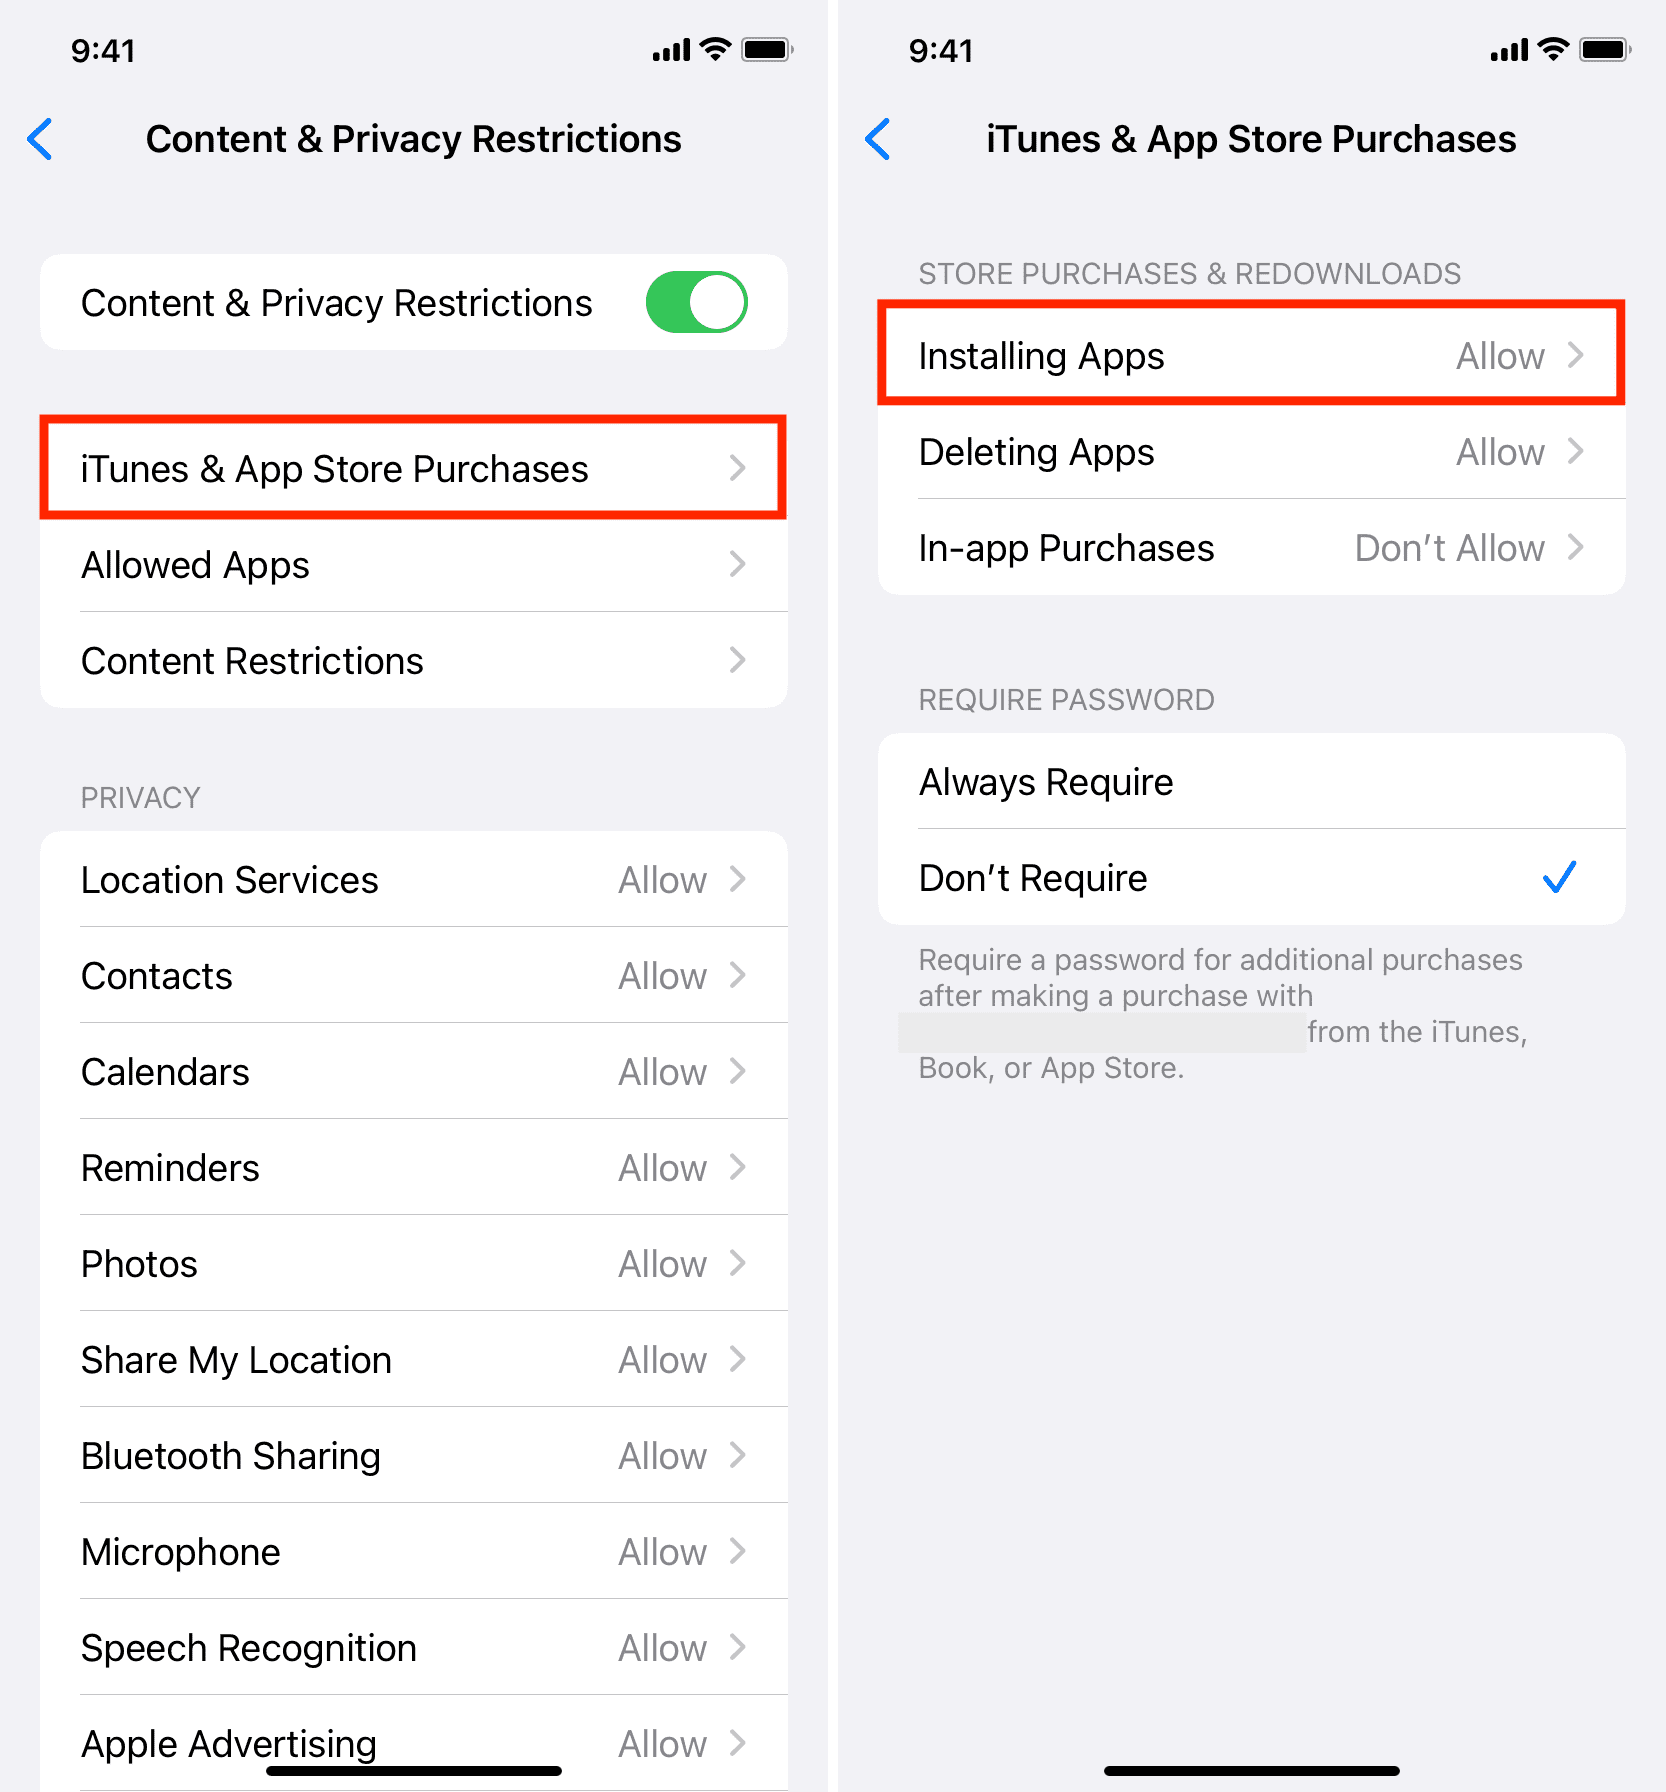
Most people treat app installation like it should just work, but it rarely does without some manual intervention. I've spent years troubleshooting everything from certificate mismatches to region-locked builds, and the process is less glamorous than Apple or Google makes it look. You need to understand what's happening under the hood before you start tapping things randomly. The core problem most users hit is that they're trying to install unsigned or improperly signed IPA files, which triggers signature errors immediately. The actual process involves three things: having a valid developer account or enterprise certificate, resolving any entitlement conflicts, and managing the provisioning profile correctly. If you're installing directly from the App Store on a device, you mostly need to make sure your Apple ID is properly authenticated and that the device hasn't exceeded its five-device enrollment limit for a given Apple account. For sideloading or enterprise distribution, the workflow changes entirely. You'll use something like AltStore, Sideloadly, or iMazing to handle the signing process. These tools act as a middle layer between your device and the actual app package. They inject a development certificate, bind it to your UDID, and re-sign the binary before pushing it to the device. It usually takes about 5 to 10 minutes for a clean installation cycle if everything is set up properly.
I ran into a specific issue last year that took me about three hours to diagnose. I was trying to install an enterprise-signed app on an iOS 16 device, and it kept failing with a generic "could not complete the installation" error. The profile looked valid in Settings, the certificate was active, and the build was fresh. The problem turned out to be that the enterprise certificate had been revoked by Apple shortly before I attempted the install, but the device was caching the old trust status. The workaround was straightforward but not obvious: go to Settings, then General, then VPN and Device Management, locate the revoked profile, and manually remove it. Then restart the device. After that, the reinstallation worked. Apple doesn't always push these revocations to devices in real time, so cached trust states are a common trap. Another thing beginners consistently miss is that optimized performance after installation isn't automatic. Apps installed through alternate methods often run with restricted background processes or reduced frame rates compared to App Store versions. This happens because the provisioning profile used for signing may not include certain entitlements. Check the Info.plist inside the app package if you can. Look for keys like com.apple.developer.networking.vpn, com.apple.developer.in-app-payments, or any Push Notification entitlements. If they're missing, the app will function but perform worse. There's a counter-intuitive thing about secure installations that most people don't realize: using a personal developer certificate for daily apps is actually less secure than using a trusted enterprise profile in many cases. Personal certificates rotate every year, and if you're re-signing apps frequently with an unauthorized tool, you're introducing attack surface through whatever intermediate server those tools route through. Enterprise profiles tied to legitimate organizational accounts don't have this rotation problem and typically get updates pushed through proper channels.
For device optimization, the single most effective step is clearing the precompiled Swift code cache. iOS stores compiled bytecode in /var/mobile/Containers/Data to speed up app launches, and stale entries here can cause performance degradation that feels like a bad installation. A simple command through a terminal connection or a tool like Filza lets you delete the contents of the swiftshader and dyld_shared_cache directories. Restart the device afterward. This usually restores launch times to within 10 percent of factory performance. I should also mention what doesn't work. You cannot bypass region restrictions by changing your Apple ID country and installing apps directly from the App Store on newer iOS versions. Apple now requires a valid payment method from the target region, and many times you need to spend down your existing store credit first. It's a real barrier that forces people toward sideloading even when they'd rather not use it. If you need an app that's only available in Japan or Germany, you'll likely end up using an APK mirror site for Android or finding a legitimate EU-based developer account. The download sources themselves matter more than most guides admit. Third-party app repositories vary wildly in their signing practices. Some use leaked enterprise certificates that get revoked within weeks. Others use legitimate cracked versions that may contain modified binaries with data collection payloads. I always recommend checking the hash of any IPA file against known-good builds before installing. It takes about two minutes and eliminates a lot of risk.
Get the Full Details
If you have a legitimate need for frequent app testing or internal distribution, the paid Apple Developer Program at $99 per year is genuinely the most cost-effective path. It gives you valid certificates, proper provisioning profiles, TestFlight distribution, and no signing expiration headaches for 12 months. The free account has serious limitations that compound over time, especially if you manage more than three devices. One final note on performance optimization that most people skip: make sure your device has at least 2GB of free storage before attempting any installation. iOS needs working space to verify signatures, decompress packages, and compile assets on the fly. Trying to install large apps on a nearly full device causes silent corruption in about 30 percent of cases, and the resulting app will crash unpredictably.