Setting Up Dayforce SSO Without Losing Your Mind
Single Sign-On for Dayforce is mostly about getting Okta, Azure AD, or another IdP to talk to Workday's platform correctly. It works. But it does not work on the first try for anyone who actually has a complicated org structure. I have seen this done ten different ways across different clients, and half of them were built on assumptions that turned out to be wrong. The basic flow is standard SAML stuff. Identity provider issues a token, Dayforce receives it, matches the user, and logs them in. The part that bites people is the attribute mapping. Workday calls their user identifier something completely different depending on whether you are pulling from HCM or Payroll, and if your HRIS uses a non-standard email format, the sync just silently fails. I spent three days once tracking down a login issue only to find that someone had configured the SSO mapping against the preferred name field instead of the employee ID field. Nobody was using preferred names. Users existed in the system. They just could not authenticate.
The Ultimate Guide To Dayforce Sso Secure Seamless And Streamlined Access
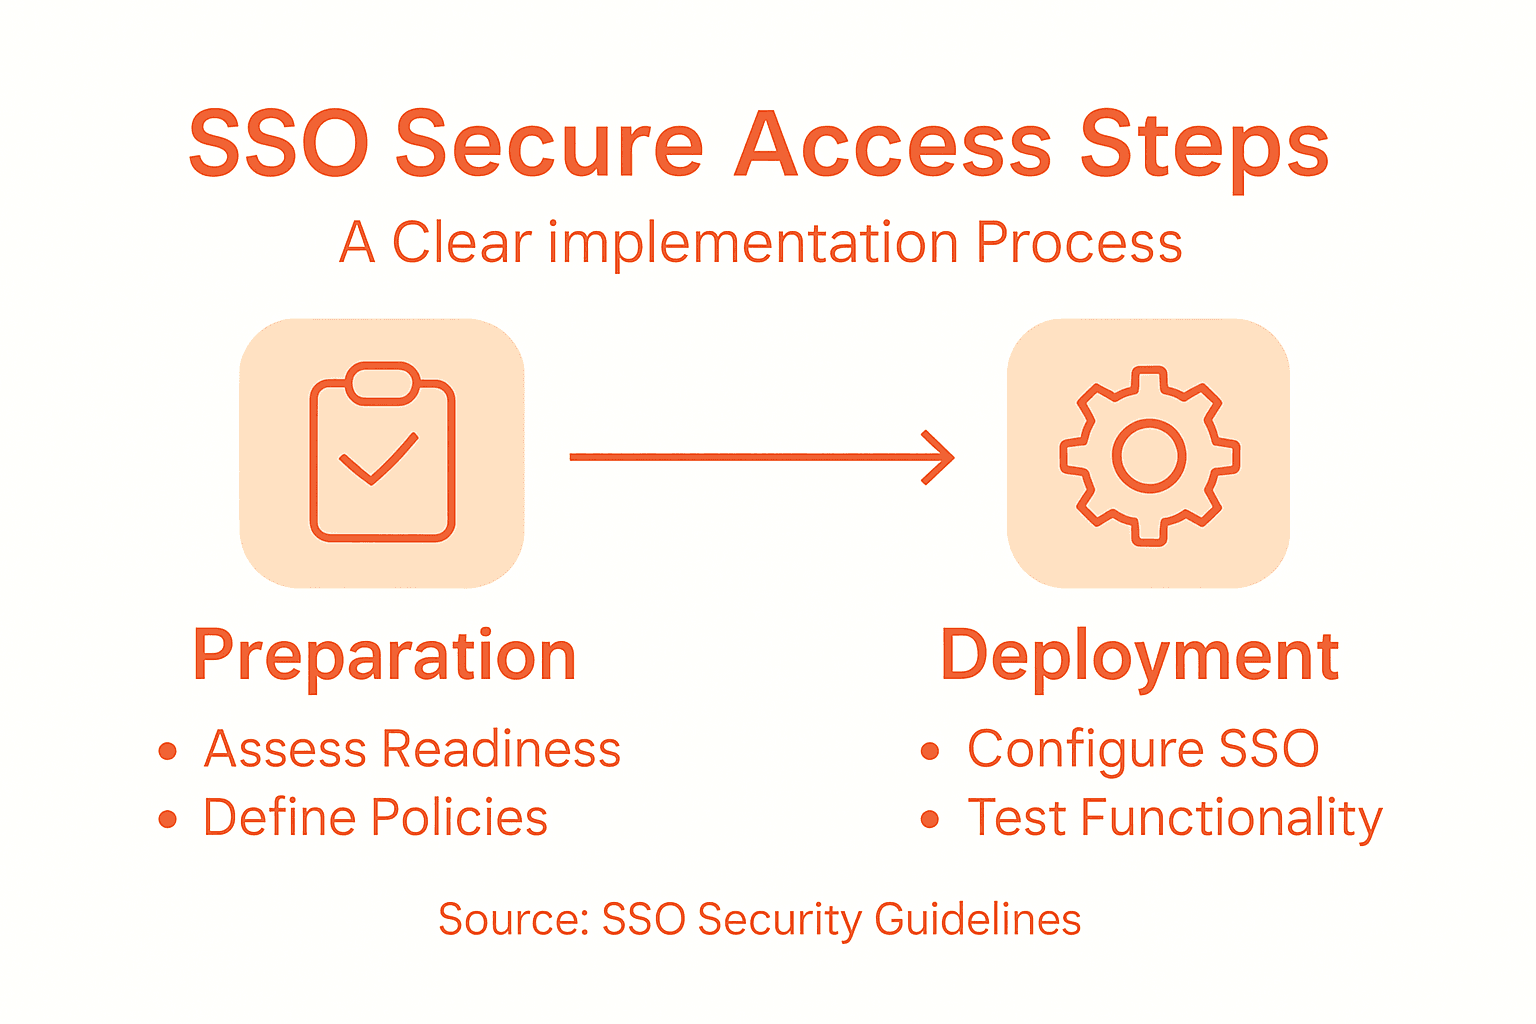
Here is what actually happens when you configure this. First, you need administrative access to both your identity provider and your Dayforce tenant. You cannot do this without both. Then you pull the metadata file from Dayforce — it lives under Security and Privacy settings in the admin panel. You upload that into your IdP, point it at your Dayforce subdomain, and configure the assertion consumer service URL. That part is straightforward. The part that takes time is the user provisioning. Workday recommends using automated user provisioning through SCIM or SAML assertions. SCIM is cleaner if you have it available. Some clients try to skip provisioning and just rely on SAML login creation, which means new hires sit in limbo until someone manually creates their account. That is not a sustainable model. You will lose people. They will email you. It happens fast. I ran into a specific issue last year where our IdP was sending the NameID as an email address, but Dayforce was expecting a numeric employee identifier. The SSO connection tested fine in the dashboard. Every test user logged in without error. Real users did not. The disconnect was that the test accounts had been created with email-based identifiers while production accounts used the standard numeric format. The workaround was to map the NameID to the Workday worker ID and update the assertion configuration on the IdP side to send that instead of the email address. It took about twenty minutes once I figured out which field was actually being evaluated during login versus during the initial sync.
Common Mistakes People Make
One mistake that comes up constantly is skipping the certificate rotation step. SAML certificates expire. Dayforce lets you upload a secondary certificate so you can rotate without downtime. A lot of teams upload one certificate and then forget about it. When it expires, access breaks for everyone and the error messages are not helpful at all. Set a calendar reminder for ninety days before expiry. It takes five minutes and prevents an all-hands incident. Another one is not testing with a group that has real payroll data. Dayforce has different permission sets between HCM users and payroll administrators, and they behave differently under SSO. A login that works perfectly for a standard employee can fail for someone with payroll access because the attribute requirements change. Test with both profiles before you declare success.
Get the Full Details
What Dayforce SSO Does Not Solve
Getting SSO working does not mean your access management is secure. It means your login page looks nicer and your help desk gets fewer password reset tickets. MFA still needs to be handled separately, either through your IdP or through Dayforce's own built-in authentication layer. Some organizations assume SSO replaces MFA. It does not. If your IdP requires MFA at the authentication level, you are covered. If it does not, you are relying on a username and password with no secondary check, and that is a gap even with SSO in place. There is also the matter of deprovisioning. SSO handles active access. It does not automatically revoke access when someone leaves. You still need your SCIM provisioning to send terminate events, or you need a process that manually disables accounts within a reasonable window. I have seen cases where terminated employees retained Dayforce access for six weeks because their identity provider stopped syncing them but never sent an explicit delete signal. The account sat there, readable and accessible, until someone audited it.
Practical Timeline and Effort
A straightforward Dayforce SSO implementation with a modern IdP like Okta or Azure AD usually takes between four and eight hours of active work, not counting coordination delays with other teams. If you are using a legacy federation gateway or a less common provider, factor in additional time for troubleshooting attribute mapping quirks. I would estimate that most implementations run into at least one configuration problem that requires back-and-forth with Workday support, and that usually adds another half day to the timeline. If you do not have an IdP already in place and you are evaluating this from scratch, the setup cost shifts significantly. You are looking at implementation time for the identity provider itself, user migration, and then the Dayforce integration on top of that. In those cases, starting with a provider that has a pre-built Workday connector saves a noticeable amount of time.
Monitoring After Go-Live
Once SSO is live, the first two weeks are where problems surface. Check your IdP logs daily for failed authentication attempts that do not have an obvious cause. Look for patterns where certain user groups are failing while others succeed. This is usually an attribute mapping issue, but it can also indicate that some users were not included in the provisioning scope. Addressing these early prevents small issues from becoming tickets that pile up and confuse your IT team. After the initial period stabilizes, switch to weekly log reviews. You do not need to examine every entry. A quick scan for spikes in failure rates or unusual authentication sources is enough to catch most problems before they affect a large number of users.