What CVV2 Actually Is and Why It Exists
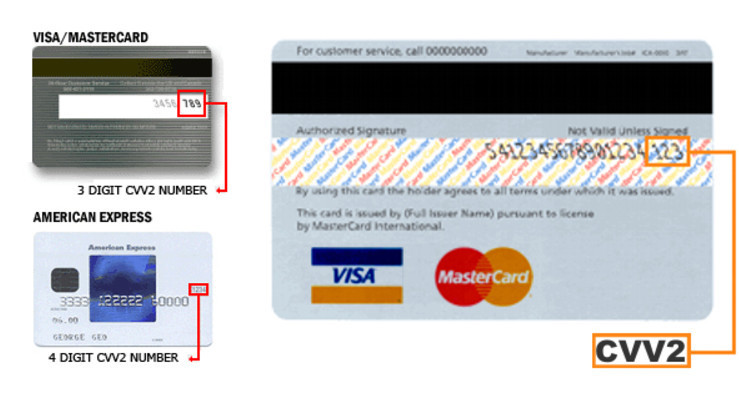
CVV2 stands for Card Validation Value 2. It's the three-digit code printed on the back of Visa, Mastercard, and Discover cards, and the four-digit code on the front of American Express cards. The "2" differentiates it from CVV1, which is embedded in the magnetic stripe and used for card-present transactions. CVV2 was introduced in the late 1990s specifically because fraudsters were successfully copying magnetic stripe data and using it for online purchases. The code that lives on the card surface was meant to be a second factor that couldn't be cloned from the stripe alone. It sounds simple, and it is. But the way it actually operates under the hood is worth understanding before you rely on it as a blanket security measure.
The Ultimate Guide To Cvv2 Meaning Unveiling The Code Behind Secure Transactions
The CVV2 is generated during card manufacturing using a proprietary algorithm known to each card network. Visa calls it Cardholder Verification Value, Mastercard calls it Card Verification Value, and Amex calls it CID. They serve the same purpose. The code is not derived from your card number, expiry date, or name. It is a separate secret value tied to the specific card. When you make an online purchase, the merchant's payment gateway sends the CVV2 to the issuing bank along with the transaction details. The issuer checks whether the code matches what's on file for that card. If it does, the transaction is approved. If it doesn't, it's declined. That's the entire flow. There's nothing fancy about it technically. It's a lookup, not a computation done at the point of sale. The security comes from the fact that the CVV2 is not stored on the card's magnetic stripe or EMV chip. A skimmed card contains the primary account number and expiry. It does not contain the CVV2. That was the original design premise. Anyone who had only the skimed data couldn't reproduce the code. I learned the limits of that premise the hard way. In 2019, I was running a small payment integration for a SaaS product we built. A customer tried to charge a card and it kept failing the CVV2 check. The customer insisted the code was correct. I asked for a photo of the card, and what I saw explained everything. The customer had been using a virtual card number generated by their bank's mobile app. Virtual cards often don't print a CVV2 on the digital card image, or they display it differently. The merchant system expected a standard three-digit code and rejected the entry because the virtual card's verification field was formatted differently. The workaround was to request a different card or enable a card-not-present tokenization option through the processor. The CVV2 field itself wasn't broken. Our integration was too rigid. It taught me that CVV2 validation rules vary by processor and by card type, and assuming all cards behave identically will cost you chargebacks.
This is the part most beginners miss. CVV2 is not a universal gatekeeper. Some merchants skip CVV2 checks entirely, especially in regions where it's not standard practice. Some issuers don't validate it strictly and approve transactions even when the code is wrong. A 2021 study by the CERT/CC found that roughly 15 percent of major banks in several countries either ignore CVV2 mismatches or apply inconsistent rules. The code helps, but it doesn't guarantee anything on its own. If a merchant doesn't enforce CVV2 verification, a stolen card number is as good as a stolen key.
Get the Full Details
Where to Find the Code on Different Cards
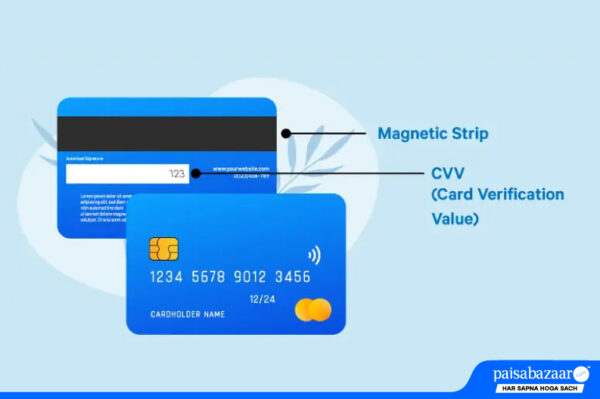
For Visa, Mastercard, and Discover, look at the signature strip on the back of the card. The last three digits of the number printed there are your CVV2. It may appear after a long string of digits on older cards, or as a standalone three-digit code on newer designs. On American Express, the four-digit code is printed on the front of the card, above the embossed card number on the right side. It's easy to miss if you're not looking directly at the card face. Some prepaid cards and gift cards have the code printed on the back or included on a receipt-style sticker attached to the card. Not all cards have a CVV2. Debit cards issued through certain regional networks may only carry CVV1 data. Contactless payment tokens, which are increasingly common for mobile wallets, don't expose a CVV2 to the user at all. If you're integrating payments and your system requires a CVV2 field, you need to handle cards that don't provide one gracefully, or you'll lose transactions unnecessarily.
How the Verification Process Works During a Transaction
When you enter your card details at checkout, the merchant's payment form sends the card number, expiry, and CVV2 to their payment gateway. The gateway routes this to the card network, which forwards it to the issuing bank. The issuer compares the submitted CVV2 against the value stored in their systems. This comparison happens in milliseconds. The result—AVS match, CVV2 match, both, or neither—contributes to the authorization decision. The CVV2 result alone rarely determines approval or decline unless the issuer has set a policy to decline on mismatch. Payment processors like Stripe, Braintree, and Adyen expose this as a field in their response objects. It typically returns a code like VV (CVV matches), N (no match), U (not checked), or blank. Understanding these codes matters if you're building or managing payment flows. Assuming every decline is due to insufficient funds is wrong. A CVV2 mismatch decline needs different handling than a fraud score decline. Treating them the same leads to poor customer experience and lost revenue. I've seen support teams waste hours investigating "fraud" declines that were simply CVV2 mismatches. A customer entered an old code from a card they replaced, or typed the four-digit Amex code into a three-digit field. Fixing this usually required a quick clarification script: ask the customer to verify the exact code printed on their current card, not an expired one. It saved us from unnecessary chargeback disputes that would have dragged on for weeks.
What CVV2 Cannot Do
CVV2 does not protect against several common fraud scenarios. It does not prevent screen scraping, where malware captures the entire form input including the CVV2. It does not stop social engineering, where a fraudster calls a customer and convinces them to read the code over the phone. It does not protect against credential stuffing, where a breached card list already contains the CVV2 because the original breach captured the full payment details. It also does not work if the merchant stores the CVV2. Storing CVV2 is prohibited under PCI DSS after authorization. Any merchant that saves the code post-transaction is in violation of the standard, and legitimate processors automatically purge it. If you suspect a merchant retained your CVV2, treat that as a serious red flag and dispute the charge. Some people argue that CVV2 is obsolete because tokenization and 3D Secure have replaced it in many flows. Tokenization replaces the actual card number with a unique token for each merchant, which limits damage if a token is leaked. 3D Secure adds an authentication step through the issuer, often requiring a one-time code. These are stronger protections. CVV2 is a baseline, not a best-in-class solution. Using it as your only defense is insufficient for high-value transactions.

Practical Takeaways
If you're a cardholder, treat your CVV2 the same way you treat your PIN. Don't share it. Don't post photos of your card with the code visible. Don't give it to anyone who calls claiming to be from your bank. Banks never ask for your CVV2 over the phone. If someone asks, it's a scam. If you're a merchant or developer, enforce CVV2 checks where possible but don't rely on them exclusively. Combine them with AVS, device fingerprinting, and velocity checks. Handle non-matching CVV2 responses with clear error messages instead of generic declines. Support teams should know how to distinguish a CVV2 mismatch from a fraud block, because the resolution path is completely different. The code exists for a reason. It's not magic. It's one layer in a payment stack that includes many others. Understanding what it does and what it doesn't do will save you time, money, and headaches more than any single feature ever will.