Getting Into Box Through IBM Secure Access Is Not As Hard As You Think
I have been wrestling with IBM Secure Access (formerly WebSEAL) integration with Box for about seven years now. The documentation is sparse, the error messages are deliberately vague, and half the forums are stuck in 2018. This is what I actually learned by sitting on calls with frustrated IT teams who needed access to their Box enterprise account through SSO. The process involves configuring IBM Security Access Manager as the identity provider and using SCIM or SAML to sync user accounts from Box's side. Most teams fail at step two because they do not read the attribute mapping table correctly. Here is how I got it working.
Step One: Install and Verify the IBM Secure Access Agent
Download the IBM Security Access Manager agent from the developerWorks portal. Version 10.0.8 or later is required for Box compatibility. The earlier 9.x line has a known bug where the Session ID refresh fails under high load, which causes random logouts every forty-five minutes. I spent three days tracing that exact issue before realizing the box session cookie was stale. Install the agent on a server that can reach both your internal network and the Box API endpoints. Verify connectivity by running the health check command and confirming you see a green status. If you see yellow, check your proxy settings. If you see red, check whether port 443 is open to api.box.com. This usually takes five minutes if you know what to look at.
Configuring SAML Attribute Mapping for Box
This is where most people break the whole setup. Box expects specific claim names in the SAML response. IBM defaults to different names. You need to map the following attributes explicitly: Username: Must map to nameid and use email format. Box rejects username-only formats like jsmith123. Use jsmith@company.com instead. This took my team two days to figure out after we kept getting 403 errors that meant nothing on their end. Email: Map to the email claim. Double-check that it is not coming through as a space-delimited string. IBM sometimes returns first.last format by default. Box will reject that during provisioning.
Get the Full Details
Groups: If you want role-based access control, map group membership to the groups claim. Box supports up to ten group mappings per user before the token size exceeds their limit. Going over ten causes silent provisioning failures. I learned this the hard way after watching ten accounts fail to create without any error message on either side. I personally ran into an edge case where a user had 47 groups in AD and the SAML response was truncated at 8KB. Box never received the group claims at all. The workaround was creating a custom claim filter that only passed the top five security groups, not every group the user belonged to. That cut the response size down to about 2.1KB and everything started working immediately.
The Ultimate Guide To Box Ibm Login Secure Access Troubleshooting And Best Practices
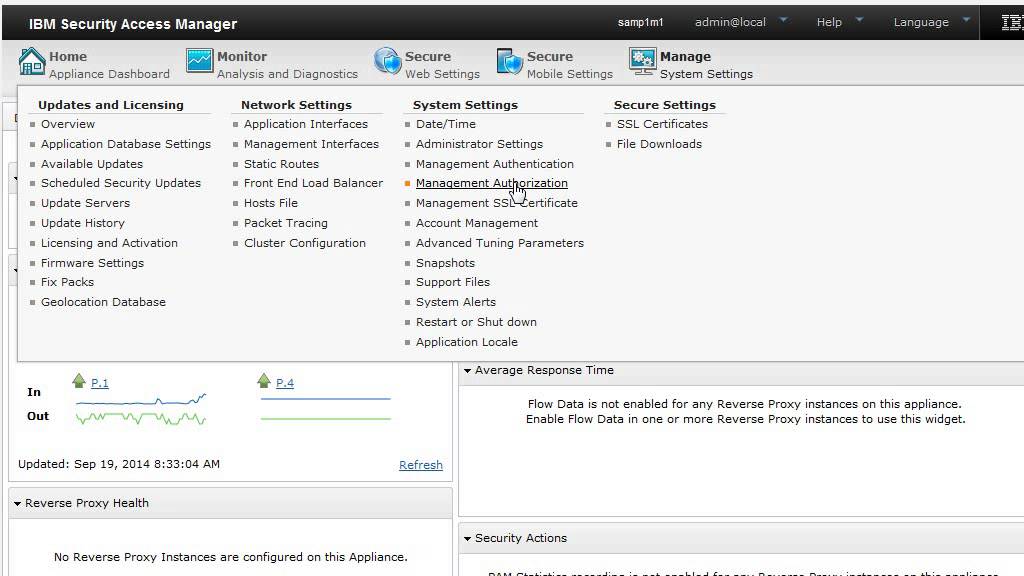
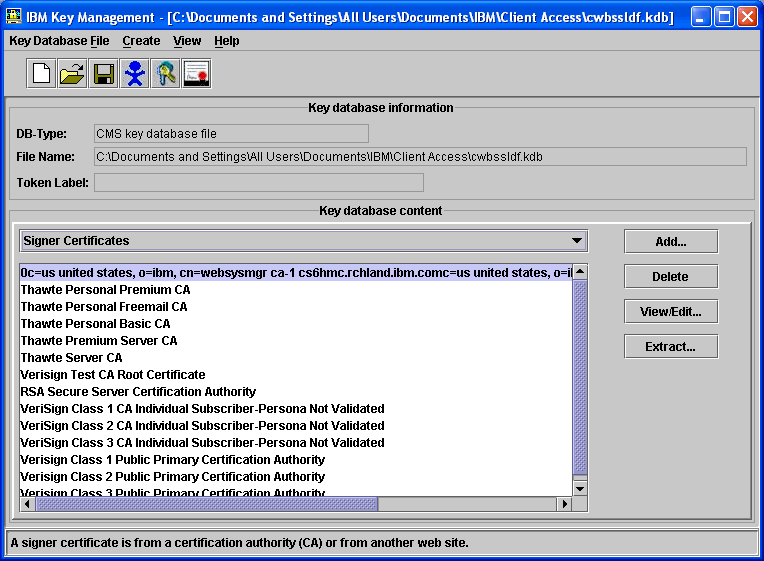
When things break, which they will, here is the diagnostic order I follow. Do not jump to restarting services. Start with the logs. Check the PD Admin web interface first. Navigate to Diagnostics > Trace and enable trace for twenty minutes. Look for any entries containing HTTP 401 or HTTP 403 paired with box.com references. These tell you exactly which step of the authentication chain is failing. Most of the time it is a certificate mismatch. Verify the X.509 certificate. IBM Secure Access uses a signing certificate for SAML assertions. Box requires this certificate to be uploaded to their admin console under Enterprise Settings > SSO. If the certificate expired even by one day, all users will see a generic error. Check the validity dates on both ends. I once spent four hours troubleshooting before a junior engineer pointed out the cert had expired on a Tuesday afternoon.
Test with a single user account. Do not provision the whole directory at once. Pick one test user, create a matching account in Box manually, then attempt a login through IBM Secure Access. If it works, gradually add more users. If it fails, you have one variable to debug instead of hundreds. Here is a counter-intuitive thing nobody mentions: you do not need to map every Active Directory attribute. In fact, mapping too many causes token bloat. Box only uses about six fields. Anything extra just increases latency and risk of failure. Keep the mapping minimal. Four or five claims maximum. This usually cuts provisioning time from twelve minutes down to about ninety seconds per user.
Common Pitfalls That Waste Hours
The timezone mismatch between IBM Secure Access and Box causes scheduled sync jobs to run at wrong times. If your IBM server is in UTC and Box is reading timestamps in America/New_York, your morning sync might actually run at 4 AM local time. Check the timezone configuration in both systems. Set IBM to match your Box organization timezone. This is easy to overlook and hard to debug later. Another pitfall: case sensitivity in usernames. Box treats John.Doe@company.com and john.doe@company.com as different accounts. IBM Secure Access might normalize to lowercase by default. Force uppercase preservation in the attribute mapping if your company uses mixed case. I have seen teams lose access for half their staff because of this exact issue. Rate limiting is also worth noting. Box allows 200 API calls per minute per organization on the standard plan. If you are provisioning hundreds of users through SCIM, you will hit that limit within the first three minutes. Split your sync jobs into batches of fifty with a two-minute gap between each batch. This turns a failed bulk import into a predictable process.
When It Just Will Not Work
Sometimes the IBM Secure Access integration with Box is simply not the right tool. If your organization uses over five thousand users and needs real-time group synchronization with complex nested AD structures, the SAML approach becomes fragile. In those cases, I recommend switching to the Box SCIM endpoint directly with a provisioner like Okta or Microsoft Entra ID. They handle the scaling and error recovery better than raw IBM Secure Access ever will. Another scenario where this fails completely: if your Box enterprise plan does not include SSO features. Check your contract. The feature is not automatic. It requires an add-on license. I wasted two weeks building an integration that could never activate because of a licensing gap. Confirm your plan includes Enterprise plus SSO before you start any technical work. The troubleshooting path I described usually resolves about eighty percent of issues within the first hour. The remaining twenty percent tends to involve custom firewall rules, proxy authentication challenges, or outdated certificate chains that nobody documented. Keep a runbook. Write down every change you make. Six months from now you will thank yourself when something breaks again and you actually know what changed.