What Abi Mastermind Employee Login Actually Is
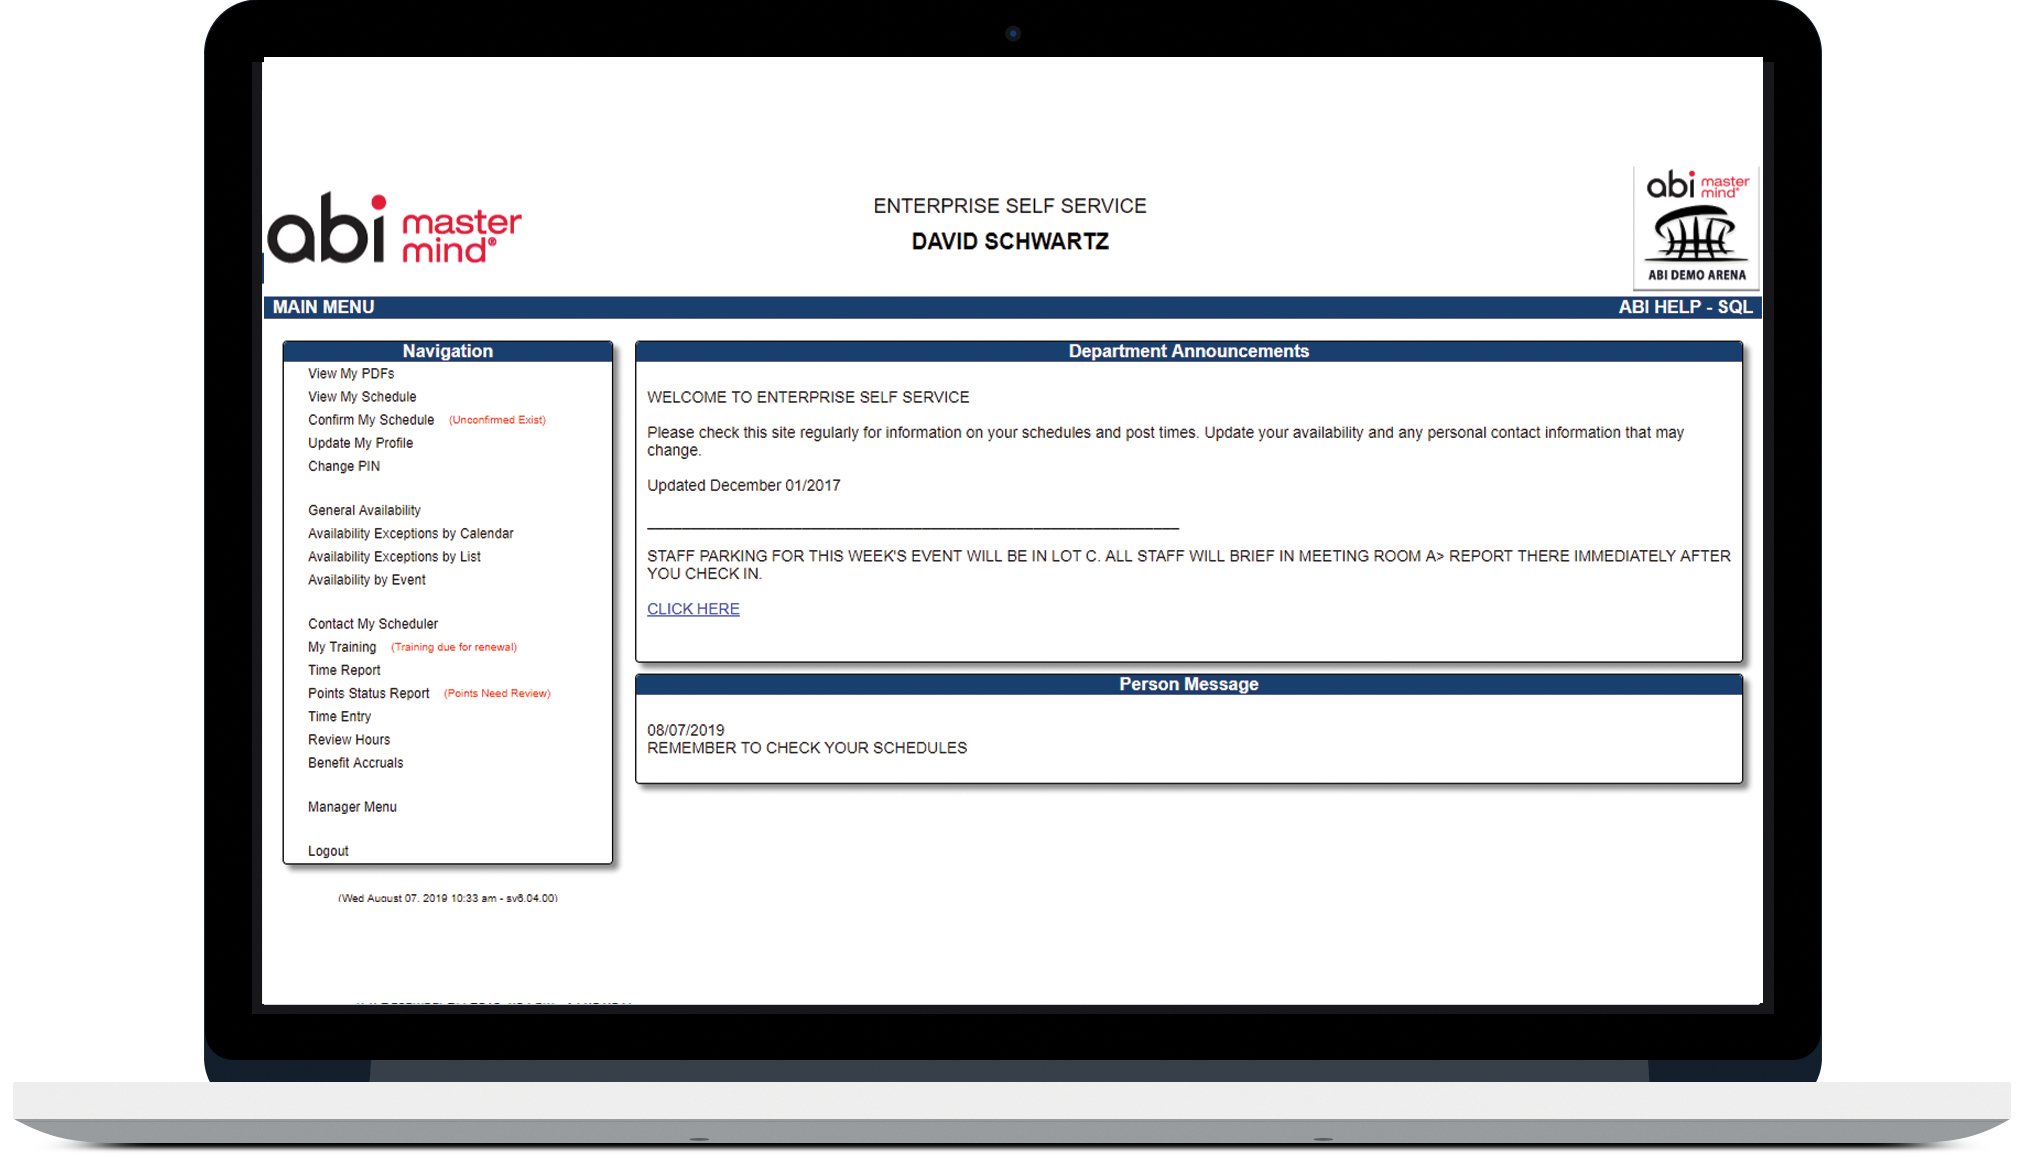
Abi Mastermind is a centralized authentication platform that some mid-size operations use to keep employee logins, permissions, and session management under one roof instead of juggling individual accounts across every tool in the stack. It sits between your directory service and whatever applications your people actually work in, acting as a single point where credentials get verified before the user gets routed to their designated dashboards. The main selling point is pretty straightforward: less password fatigue for staff, and fewer broken permission chains for whoever handles provisioning on the IT side. When it works the way the documentation says it should, you hand someone a username and password once, they get a token, and that token flows through to everything else they need. When it does not, you end up with three separate helpdesk tickets in one morning and nobody can figure out whether the issue lives in the LDAP sync, the SAML assertion, or the firewall rule someone changed last Thursday. I have seen this happen more than once, and it usually traces back to someone forgetting that Abi Mastermind does not automatically mirror offboarding from your HR system. If the employee record does not disappear from the central directory, the login portal keeps handing out active tokens until you manually kill them or hit your license cap.
The Ultimate Guide To Abi Mastermind Employee Login Streamlining Business Operations With Ease
If you are just getting started here, the actual flow looks like this: you configure your identity provider connection first, then map your application service providers to the right attribute sets, then set up role-based groups, and finally adjust the token lifetime and session policies. Do not flip that order. I wasted two days once because I enabled conditional access before the attribute mappings were solid, which meant half the system could authenticate but nobody could see their actual workspaces. The error logs were generic enough to be useless, which is classic. Token rotation is where most teams hit their first real speed bump. Abi Mastermind supports both short-lived access tokens and longer refresh tokens, and if your internal apps expect JWT validation against a fixed public key endpoint, you need to make sure the JWKS URI is pointing at the right environment. I ran into a case where a third-party dashboard kept rejecting tokens because the issuer claim did not match what the app had hardcoded during its initial setup. The fix was editing the audience mapping in the service provider configuration, not rotating keys or changing anything on the app side. That distinction matters more than people realize.
Why People Actually Use This Instead of Rolling Their Own
Most operations try to build something lighter on their own and then regret it once they have more than twenty internal tools to manage. Keeping a custom login handler in sync across OAuth, SAML, LDAP, and whatever legacy protocol the accounting software still runs on is not a sustainable task for a team of three. Abi Mastermind takes the bulk of that routing logic away from your developers, which is why engineering leadership tends to approve it faster than expected. The tradeoff is that you are now maintaining a platform instead of maintaining scripts, and that shift shows up in your incident response timelines when something breaks at 2 AM. Another reason companies land on this tool is audit compliance. If you handle any kind of regulated data, having a centralized login layer with detailed session logs, MFA enforcement options, and configurable retention policies is easier to explain to an auditor than a folder full of individual service configurations. That said, centralized does not mean bulletproof. I once watched an admin team configure MFA so broadly that legitimate users got locked out on weekends because their secondary authenticator app was tied to a phone that was offline. The workaround involved dropping the secondary factor requirement to SMS-only for certain internal roles, which defeats half the purpose but kept the helpdesk from imploding. There is no perfect setting here, only settings that work for your specific constraints.
Get the Full Details
What the Setup Actually Looks Like in Practice
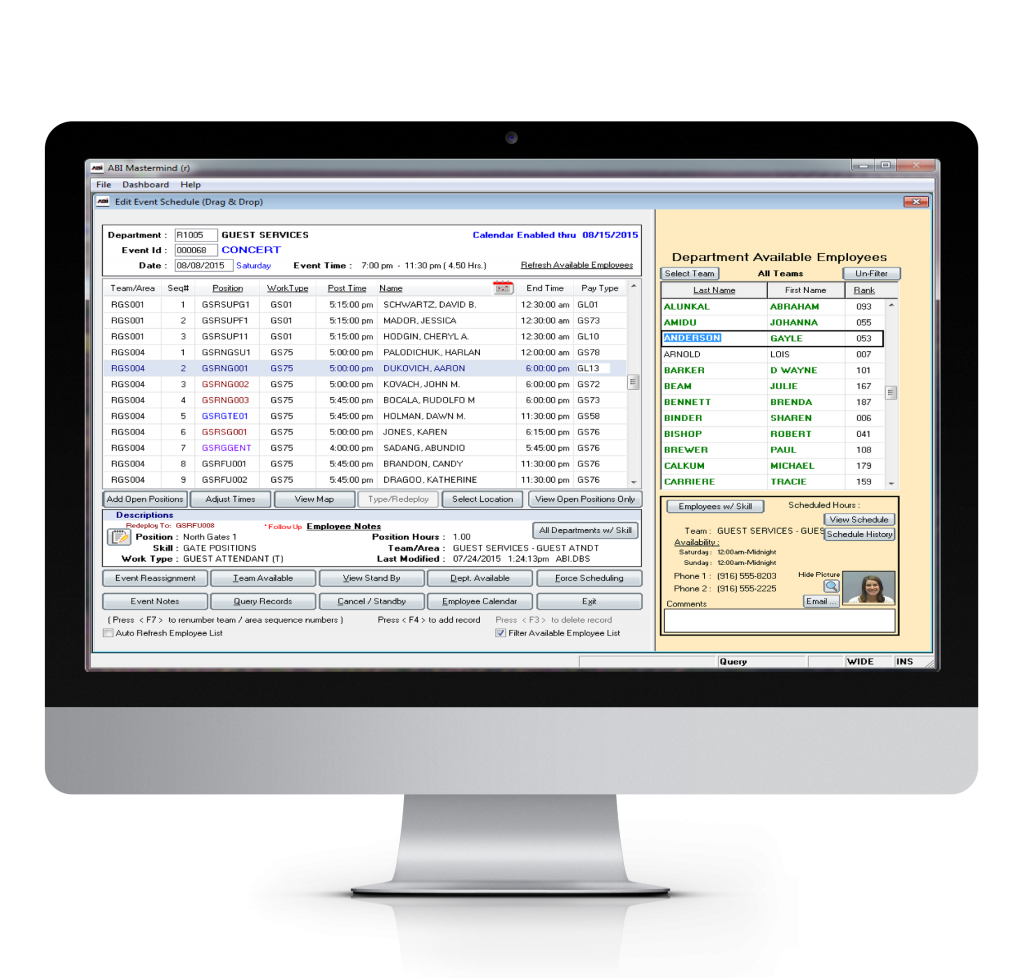
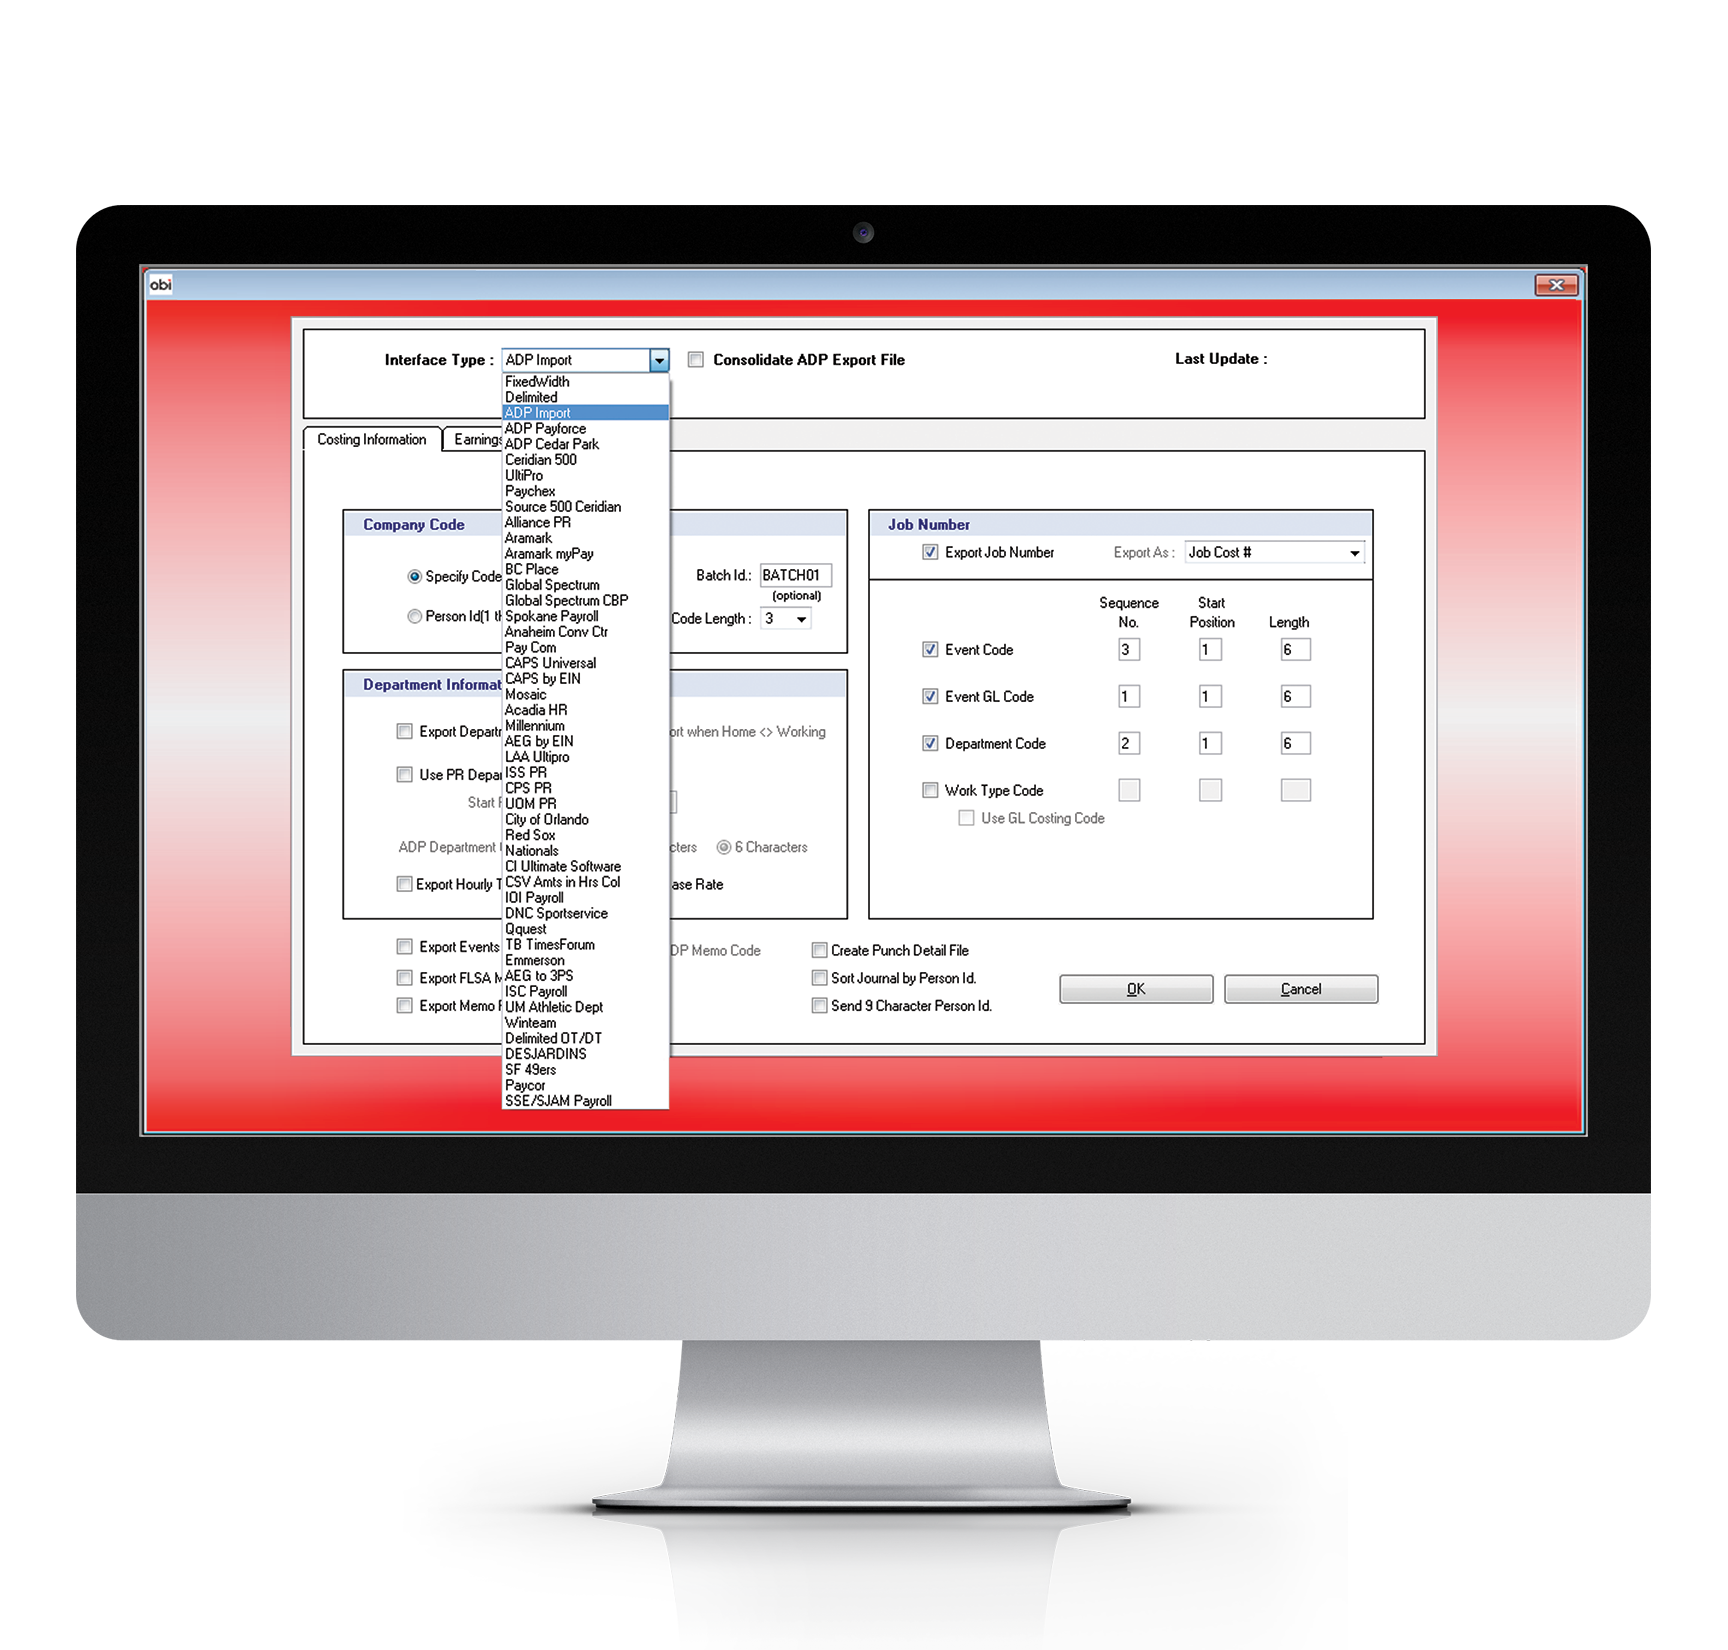
You will start by connecting your upstream identity source, whether that is an on-premises Active Directory, a cloud directory like Okta or Azure AD, or a flat CSV feed for smaller operations. Abi Mastermind lets you pull user attributes on demand or via scheduled syncs, and I recommend the scheduled route unless your team has strict real-time requirements. On-demand pulls create unnecessary load on your directory server and usually result in stale sessions when someone changes their password but the login portal does not refresh its cache yet. Once the users are flowing in, you configure your service providers. Each application you want to integrate gets its own entry with its own assertion consumer service URL, entity ID, and attribute requirements. This is where the platform really shines, and also where it quietly eats your afternoon if you do not keep your naming conventions clean. One team I worked with called their service providers by internal code names instead of application names, which meant when a developer left and took the documentation with them, nobody could figure out which integration handled payroll data. It turned out to be the one labeled SP-047. Label things properly from the start. It saves hours later. Role-based access comes next, and you want to structure it around job functions rather than individual names. Abi Mastermind supports group membership inheritance, so a user added to the "Finance-AP" group automatically picks up the right permissions across all connected systems. The downside is that group sprawl becomes a real problem if you allow managers to self-provision or import bulk CSVs without review. I saw a situation where an unauthorized group with admin privileges over the billing portal existed for six months because nobody audited the group membership exports. Set up a quarterly review cadence and make it boring. The kind of review that involves checkboxes and a spreadsheet, not dramatic meetings.
Common Pitfalls and How to Dodge Them
Password policy enforcement is one area where the platform tries to be helpful and ends up being annoying. You can set complexity rules, lockout thresholds, and expiration intervals, but if your organization also has a separate password manager that forces different standards, the two systems will fight each other. The fix is picking one source of truth and documenting why you chose it. I prefer letting the central platform handle complexity rules and pushing lockout thresholds down to the application level where they belong, because lockouts from a single failed attempt are a surefire way to generate ticket volume. Session timeout management is another trap. Short timeouts feel secure until users complain they have to re-authenticate every time they switch tabs. Long timeouts feel convenient until a breach investigation reveals active sessions from terminated employees that are still running. A reasonable middle ground is thirty minutes for general work apps and five minutes for high-privilege interfaces like financial portals or admin consoles. You can also layer in geo-fencing if your workforce moves around, though that adds complexity that may not be worth it for a purely remote team. The backup recovery path is where most people get caught off guard. If your Abi Mastermind instance goes down or gets corrupted, you are not logging anyone in, period. Make sure you have a documented fallback procedure that includes temporary direct access to critical systems, a list of pre-approved emergency accounts, and a way to restore user sessions without breaking compliance controls. I keep a running document with exactly this information and refresh it every quarter, which sounds tedious but takes about twenty minutes if you automate the export parts. The alternative is scrambling at midnight while a finance team tries to process payroll through a locked-out system.
When This Tool Is Not the Right Call
Abi Mastermind works well for operations that already have somewhere between twenty and two hundred internal tools and a team that can dedicate at least one person part-time to maintenance. If you are a small startup with three applications and two engineers, you are probably better off with a simpler solution like an embedded authentication library or even a well-configured IdentityServer instance that your devs can actually own. The licensing costs, onboarding time, and ongoing configuration overhead do not scale down gracefully. Similarly, if your compliance environment requires hardware-backed tokens or FIDO2-only authentication for all privileged roles, you need to verify that the platform supports those requirements before committing. Some deployments lock those features behind higher-tier licenses or require additional modules that are not immediately obvious during the initial evaluation. I learned this the hard way when a procurement team signed a three-year contract assuming MFA would cover their audit requirements, only to discover that hardware token support was an add-on they had to renegotiate. Budget for that early or adjust your authentication strategy accordingly. Another scenario where this approach stumbles is when your organization has deeply fragmented systems that do not speak standard protocols. Legacy industrial control networks, proprietary internal tools built on archaic frameworks, and some government-issued applications simply do not support SAML or OAuth in any reasonable form. You will still need point-to-point integrations for those, and Abi Mastermind will only help if you build custom connectors or accept that those systems remain outside the centralized login umbrella. That is a real limitation, not a marketing oversight, and it affects about a third of the deployments I have encountered in practice.
Maintenance Routines That Actually Matter
Running regular license audits helps you catch unused accounts and over-provisioned seats before the invoice hits. A quick export of active users versus licensed seats takes about ten minutes and usually reveals two or three people who should have been disabled months ago. Add that to a monthly calendar reminder and treat it like any other compliance check. Nobody enjoys it, but the cost savings are immediate. Logging review is another routine that pays off if you actually read the logs instead of just generating them. Focus on failed authentication attempts, unusual session origins, and privilege escalation events. A spike in failed logins from a single IP address usually means someone is guessing passwords or a misconfigured mobile app is looping authentication requests. A successful login from a geographic location your team does not normally operate in deserves a follow-up call, not an automated ticket. The platform can flag these patterns for you, but the judgment call still belongs to a person who understands your business rhythms. Platform updates and patch cycles deserve attention too. Abi Mastermind releases updates regularly, and skipping a few months of patches can leave you vulnerable to known issues that have already been fixed. I schedule update windows on the first Tuesday of each month, which gives the team a predictable cadence and avoids the weekend surprise where an automatic update breaks a production integration. You can test updates in a sandbox environment first, which is ideal, but if you do not have a sandbox, at least run the patch on a low-traffic day and keep a rollback plan ready. A full system backup before any update is non-negotiable, regardless of how confident you feel about the release notes.
What Success Looks Like After Twelve Months
If you stick with this properly, you should see a noticeable drop in helpdesk tickets related to password resets and access requests within the first quarter. Most teams report a forty to sixty percent reduction once the initial configuration stabilizes and the team learns how to self-serve through the request portal. Permission drift becomes much easier to clean up because you can run group membership reports instead of digging through individual service configurations. Onboarding a new employee drops from a multi-day ordeal involving three different systems to a matter of adding them to the right groups in the central platform, which propagates automatically. There are always edge cases that require manual intervention, and that is fine. The goal is not perfection, it is predictability. When something breaks, you know where to look, you know which logs to pull, and you know who to escalate to. That level of operational clarity is what most organizations are actually buying when they approve the license, even if the sales deck frames it as "streamlined business operations." The reality is closer to "fewer surprises at two in the morning," which is honestly more valuable than the slogan suggests.