How FIUs Actually Work When They Trace Digital Crime
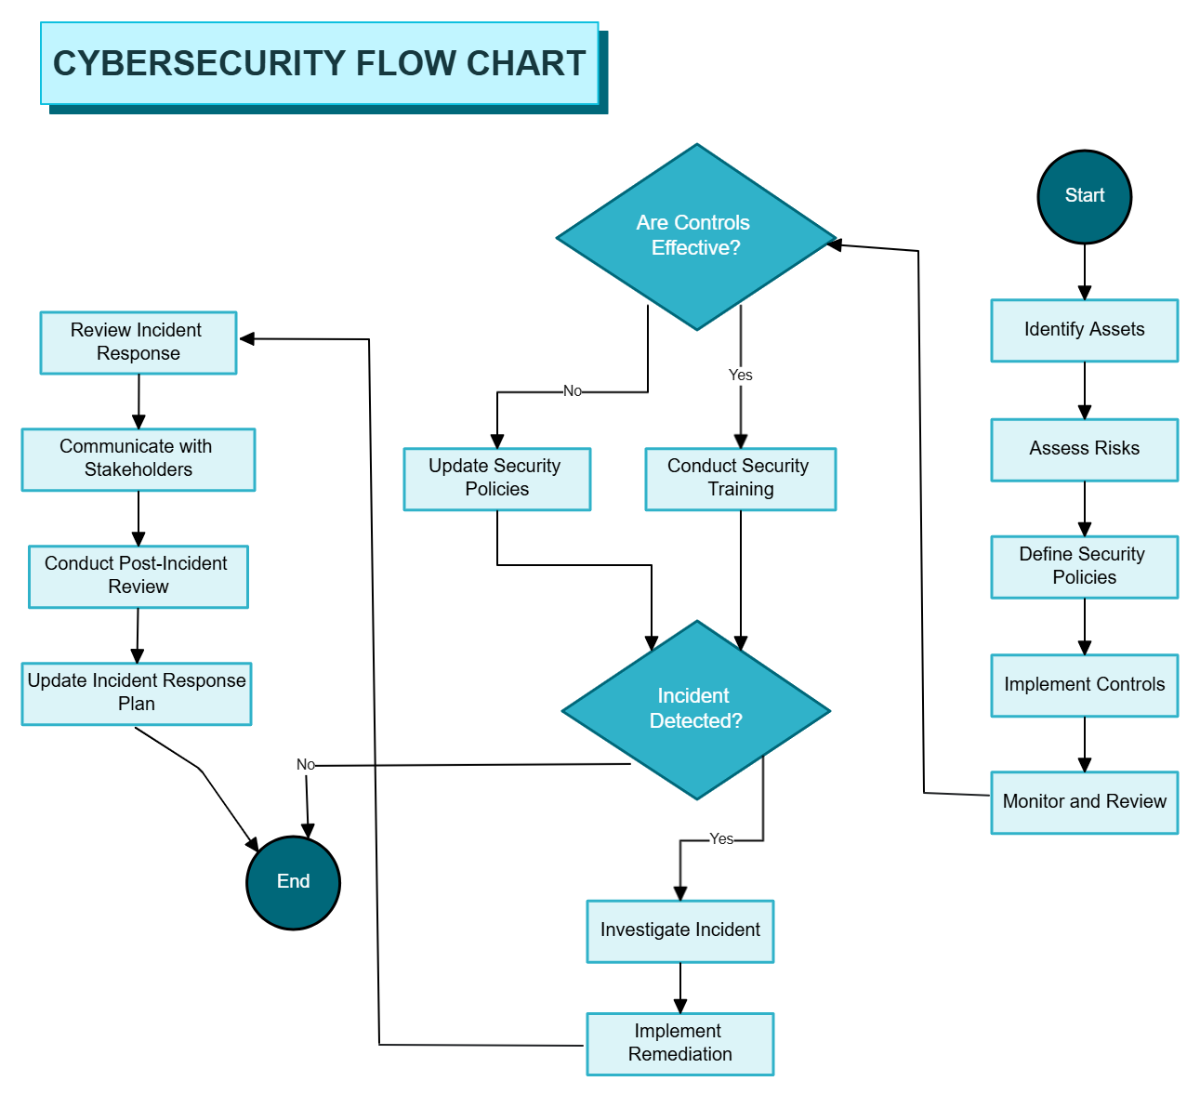
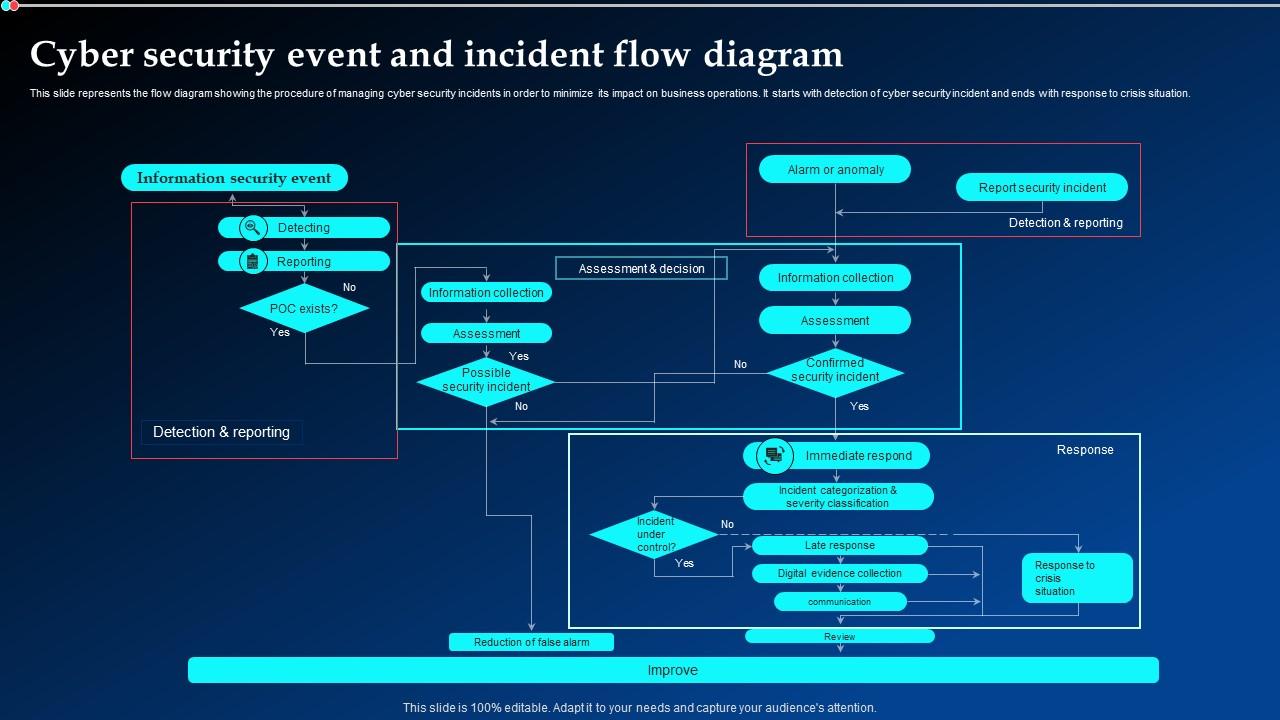
Financial Intelligence Units don't operate like they do in movies. There's no dramatic moment where a single suspicious transaction report triggers an immediate shutdown of criminal operations. The reality is slower, messier, and depends heavily on whether the institution filing the report actually knows what it's looking at. The flowchart begins with a Suspicious Activity Report or SAR. In practice, most of these come from banks, payment processors, and cryptocurrency exchanges. The FIU receives the filing, assigns it a reference number, and puts it in a database that analysts will review when something connects to existing cases. That connection step is where the real work happens, and it's also where the majority of reports go nowhere. A typical FIU triage process runs like this. The report gets a preliminary risk score based on the typology involved — money laundering, terrorist financing, sanctions evasion, fraud. High-risk typologies move to tier one analysis within hours. Lower-risk filings might sit in a queue for weeks. I worked with a system where SARs flagged for crypto mixing services were auto-routed to a senior analyst overnight, while standard structuring reports from retail banks would pile up in a backlog that could take 45 days to clear. The turnaround time alone determines whether an investigation catches a live threat or reconstructs a completed crime.
During the analysis phase, FIU analysts pull transaction data across multiple reporting institutions if the same subject appears elsewhere. They layer in KYC records, beneficial ownership data, and external intelligence feeds. What separates a competent FIU from a struggling one isn't the technology — it's whether the analysts understand the difference between a legitimate business that moves a lot of money and a layering scheme designed to obscure ownership. The patterns look superficially identical in raw data. When the FIU reaches a threshold of suspicion, it either refers the case to law enforcement or compels additional information through the reporting entity. Some jurisdictions give FIUs direct investigative powers. Most do not. This structural difference matters more than people realize. A FIU that can only share information with police departments operates on whatever speed law enforcement decides to move at. If the receiving agency has three thousand open financial crime cases and your referral is priority fourteen hundred and sixty-seven, you're not getting fast action. On the tracing side, the most effective tool isn't proprietary software. It's standardized transaction narratives. When banks file SARs using free-text fields without any consistent format, the FIU loses the ability to pattern-match across thousands of filings. I spent months trying to correlate a series of transactions involving a shell company network, and the primary bottleneck was that each bank described the same behavioral pattern in completely different language. One called it "unusual cash deposits inconsistent with business profile." Another flagged it as "rapid movement of funds through multiple accounts." The underlying activity was identical, but the narrative mismatch made automated matching nearly impossible until someone manually reviewed both reports.
Chain analysis in cryptocurrency cases follows a different logic than traditional banking investigations. Every bitcoin transaction is publicly visible, which should make tracing straightforward. It isn't. The privacy layer comes from exchange withdrawals, mixing services, and cross-chain swaps. I once tracked a $200,000 scam proceeds chain that moved through six different wallets, two centralized exchanges, a decentralized mixer, and three Ethereum-to-Solana bridges before landing in a privacy coin. The on-chain portion was traceable. The bridge and mixer hops created the gap where the trail went cold. Working with a blockchain analytics firm eventually mapped the mixer outputs, but that required a formal data-sharing request that took three weeks to process. During those three weeks, the funds had already been converted through multiple layers and dispersed across twelve final wallets. The investigation phase for FIUs usually involves coordinating with foreign counterparts when the crime crosses borders. The Egmont Group facilitates information sharing between FIUs, but the practical reality is slower than the framework suggests. Different countries have different legal thresholds for what constitutes suspicion. A pattern that meets the reasonable grounds standard in the UK might not clear the probable cause bar in another jurisdiction, even when the underlying facts are identical. Mutual legal assistance requests add months to any cross-border investigation. FIUs that have established direct secure messaging channels — like the SWIFT-based network some larger units use — move significantly faster than those that must route everything through law enforcement diplomatic channels. Digital crime stops happening through asset freezing more often than through prosecution. When an FIU identifies active criminal accounts before the funds move offshore, a rapid response mechanism can lock the money in place. Some jurisdictions have emergency disclosure request processes that let police contact a financial institution directly within hours. Others require a court order that takes days to obtain. The difference between those two models determines whether a cryptocurrency scam victim recovers any funds at all.
Get the Full Details

There are real limitations to how much FIUs can accomplish. The first is the quality of incoming reports. Many smaller banks and payment service providers file SARs with minimal detail because their compliance teams lack specialized training. Generic SARs that describe the reporter's own uncertainties rather than concrete suspicious patterns waste analyst time and provide almost no investigative value. The second limitation is data fragmentation. Even within a single country, customer transaction data is spread across hundreds of reporting entities that don't share databases. An FIU needs every participating institution to file complete, timely reports for the system to function. Missing data from even a few major players creates blind spots. The third limitation, and the one nobody wants to discuss openly, is that FIUs investigate past transactions. They are fundamentally reactive by design. By the time a SAR is filed, the money has usually already moved through the initial layering stages. The investigation reconstructs what happened rather than preventing it. This is why newer approaches around AI-driven transaction monitoring and real-time anomaly detection exist — they attempt to shift the timeline forward, flagging suspicious patterns while funds are still in transit. The accuracy trade-off is significant. Aggressive real-time blocking generates massive false positive rates that disrupt legitimate commerce and create customer service crises. Conservative thresholds catch fewer crimes but avoid flooding support channels with reversal requests. For organizations building internal cybersecurity frameworks around FIU reporting, the practical takeaway is that your SAR quality determines how useful you are to the system. Detailed narrative with specific dates, amounts, account numbers, and behavioral observations beats a checkbox-style filing every time. Include the customer's expected activity profile and explain precisely how the actual behavior deviated from it. Analysts at the FIU need enough information to determine whether the deviation is meaningful without having to request supplementary data that may no longer be readily available.
The flowchart doesn't end when the case closes. Closed cases feed typology research, which updates the thresholds and indicators that determine what gets reported in the first place. This feedback loop is where the system improves, but it only works if analysts document their findings thoroughly. A case dismissed for insufficient evidence should still generate a note about what evidence would have been useful. That documentation shapes future SAR expectations and ultimately determines what the next analyst sees when a similar pattern surfaces.