Why the Human Layer Keeps Getting Ignored Until It Breaks
I spent over a decade in security operations, and the thing that consistently trips up organizations isn't a zero-day or a misconfigured firewall. It's the gap between the tools you buy and what your people actually do when they get an email at 4:47 PM on a Friday. Michael Pagan built his entire approach around closing that gap, and it changed how a lot of us think about defense-in-depth. Pagan's framework isn't some abstract theory. It's practical, operationally focused, and it came out of watching companies throw budget at technical controls while their employees kept clicking through phishing simulations like it was a habit nobody ever addressed. His approach centers on treating the human layer as a measurable, trainable, continuously improved component of security architecture rather than an afterthought you handle with an annual compliance video. The core idea is that your security stack is only as strong as the weakest behavioral link in it. You can have endpoint detection, network segmentation, MFA, SIEM correlation, and all of that working perfectly. One employee in finance who resets their password because they think they need to to "keep their account secure" and hands their credentials to a lookalike domain and you've just walked a threat actor through your front door. This isn't hypothetical. I've lived it.
What Makes This Approach Different From Generic Security Awareness
Most companies treat security awareness like a checkbox. They run an annual training module, track completion rates, and call it done. Pagan's vision pushes past that because completion rates are a vanity metric. The question isn't whether someone watched the video. The question is whether their behavior changes when they see a real phishing attempt in their inbox. His model emphasizes continuous reinforcement, behavioral psychology, and measurable outcomes. That means regular simulated campaigns, not to catch people but to identify patterns and target interventions where they matter most. It means measuring click rates, report rates, credential submission rates, and time-to-report across different departments. It means understanding that the marketing team responds differently to social engineering than the engineering team does, and adjusting your approach accordingly. I remember running a phishing simulation for a mid-size company where our report rate was sitting at about 62 percent overall. That looked good on paper. But when we drilled into the data, the sales department had a report rate of under 18 percent. Those guys were getting hammered with spear-phishing attempts daily because their names and titles were publicly available on LinkedIn. Our generic "report suspicious emails" messaging wasn't landing with them. We shifted the messaging entirely for that group, tied it to real examples of attacks targeting sales specifically, and within two quarters their report rate climbed to around 71 percent. That's the kind of specificity the framework demands.
How to Actually Implement This Without Turning It Into Another Checkbox Exercise
Start with measurement. You need a phishing simulation platform that gives you detailed reporting, not just aggregate numbers. KnowBe4, Cofense, Proofpoint — they all have capabilities in this space. The tool matters less than how you use it. Run simulations quarterly at minimum. Test different attack vectors: credential harvesting, malware delivery, business email compromise, QR code phishing, even voice-based social engineering if your industry is targeted for vishing. Track everything by department and role. Your C-suite needs a completely different training path than your helpdesk team. The helpdesk folks are your first line of defense against social engineering over the phone. They need specialized training on verification protocols. Executives are high-value targets for BEC attacks and need targeted, frequent, short interventions rather than hour-long training sessions that nobody watches. Build a reporting culture. Make it easy and frictionless for employees to report suspicious activity. If the process requires more than two clicks or a phone call to IT, people won't use it. I've seen companies implement a simple "Report Phish" button in Outlook that routes directly to the security team. That alone increased their real-world phishing detection rate by roughly four times within three months. The technology wasn't the breakthrough. Removing friction was.
Get the Full Details
Integrate with your incident response pipeline. When someone clicks a simulated phishing link, the response shouldn't just be "here's a training module." It should be immediate, contextual education that explains exactly what they encountered and why it was dangerous. The learning happens in the moment of mistake, not in a quarterly training session weeks later.
Where This Approach Falls Short
It doesn't fix every problem. Behavioral training can't stop a sophisticated nation-state actor using custom malware and multi-week compromise chains. It can't eliminate insider threats from disgruntled employees who already have access. It won't compensate for a complete lack of technical controls, either. I've worked with organizations that treated security awareness as their entire cybersecurity strategy, which is like putting a bandage on a bullet wound and calling it treatment. There's also the measurement problem. Report rates go up, but that doesn't always mean behavior improves in the wild. Some people learn to report everything including legitimate emails, which creates noise for your security team. Others become overly confident after a few successful detections and start taking risks again. The data you collect can give you a false sense of security if you aren't digging into it honestly. The biggest bottleneck is executive buy-in sustained over time. This isn't a project you complete. It's a continuous operational discipline. Leadership needs to understand that the ROI isn't a single metric but a gradual reduction in successful phishing compromises and security incidents over months and years. Getting that kind of patience and funding is harder than most people expect.
A Practical Workflow That Actually Works
Here's what a mature implementation looks like in practice. You run simulated phishing campaigns every six to eight weeks with increasing sophistication. Each campaign targets specific groups based on your threat intelligence. Someone in accounting gets a fake vendor payment request. Someone in HR gets a fake benefits enrollment link. The simulations mirror what your industry actually sees in the wild. People who fail the simulation get immediate, brief, non-punitive training. Not a 45-minute course. Three minutes of targeted content explaining the specific attack they encountered. The goal is recognition, not compliance theater. You hold monthly reviews with department heads showing their team's metrics. Not to shame anyone, but to create accountability and awareness at the management level. Managers who understand their team's vulnerability patterns can reinforce the right behaviors in their daily operations.
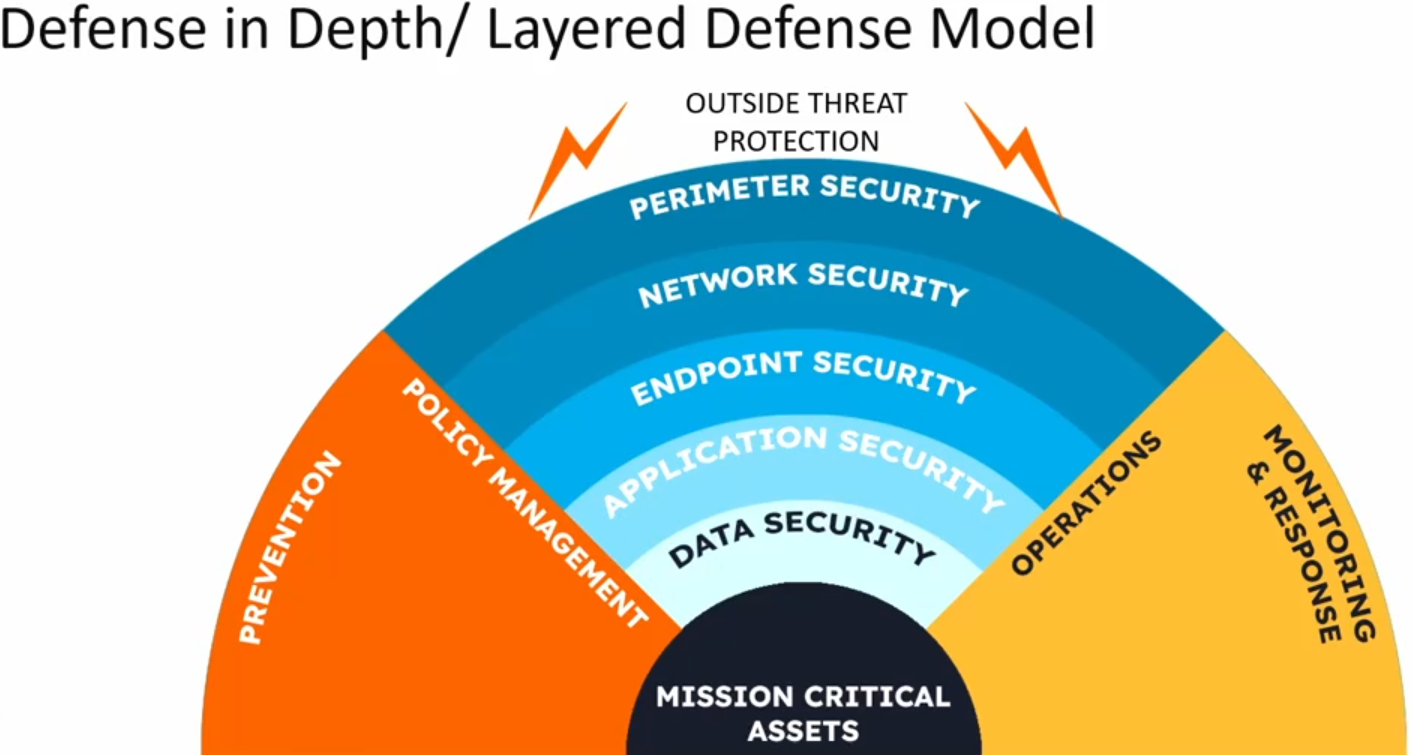
Quarterly, you update your simulation scenarios based on current threat intelligence. If ransomware groups are targeting your sector with a new lures, your simulations should reflect that within a month, not six. The threat landscape moves fast. Your training program needs to move at least as fast. Once a year, you conduct a full table-top exercise that includes a realistic phishing-driven breach scenario across your incident response team. This tests whether your technical controls, your communication plans, and your decision-making chains actually work when someone falls for a sophisticated attack. I learned through one of these exercises that our backup restoration process would have taken 72 hours instead of the estimated 8 during a live incident. That discovery saved us from a much worse outcome when we actually faced a real ransomware event fourteen months later.
The Bottom Line
Pagan's vision works because it treats human behavior as a core security control rather than a soft skill adjunct. It requires investment, honest measurement, and continuous refinement. Most organizations will underinvest and over-simplify. The ones that do it right see real, measurable improvements in their security posture within the first year. The ones that treat it as another compliance checkbox will keep having the same problems year after year. Start where you are. Get your baseline measurements. Build your simulation program. Make reporting easy. Keep refining. The attackers aren't waiting for you to finish your strategic plan before they try something new.