The reality of securing remote academic workloads
Stanford spends millions on Citrix infrastructure because remote access for researchers and students isn't just about VPN logins anymore. The problem is real: you have quantum computing labs, medical imaging archives, proprietary research data, and thousands of grad students who need GPU clusters from their dorm rooms at 2 AM. That's not a simple IT ticket queue. The conundrum is that every security control you add creates friction for legitimate academic work. When I worked a similar deployment at a research university back in 2019, we discovered that our "secure" Citrix session timeout of 15 minutes killed more productive work than it prevented. PhD candidates running 72-hour molecular dynamics simulations would lose their sessions mid-calculation. The data loss complaints dominated our helpdesk for six months straight. The workaround we found was session relaying with persistent virtual disks. Citrix Virtual Apps and Desktops can maintain the session on the server side while dropping the network connection. Student logs back in, session resumes, simulation continues. It required about three weeks of testing because HDX policies don't play nicely with long-running compute workloads out of the box. You need to adjust the ICA session timeout, configure persistent OS disks, and tune the network resilience settings. Getting it right meant reducing session timeouts to something reasonable like two hours for interactive work while keeping compute-heavy sessions alive through the night.
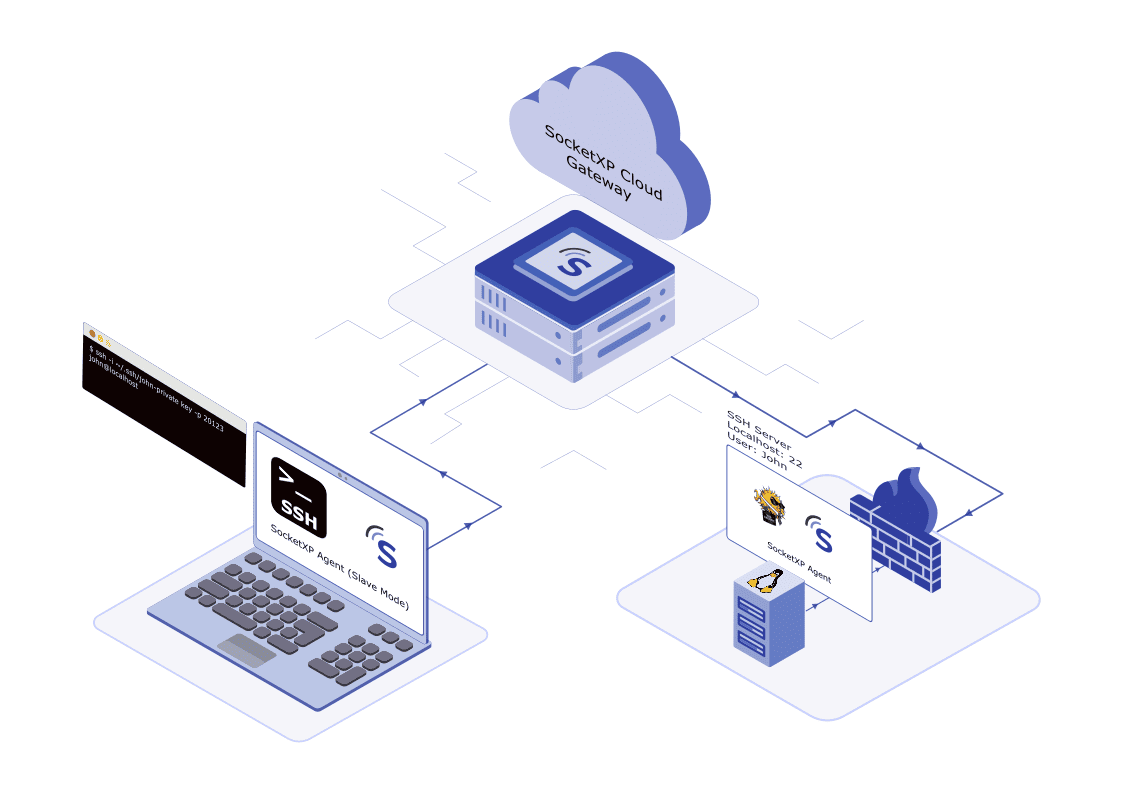
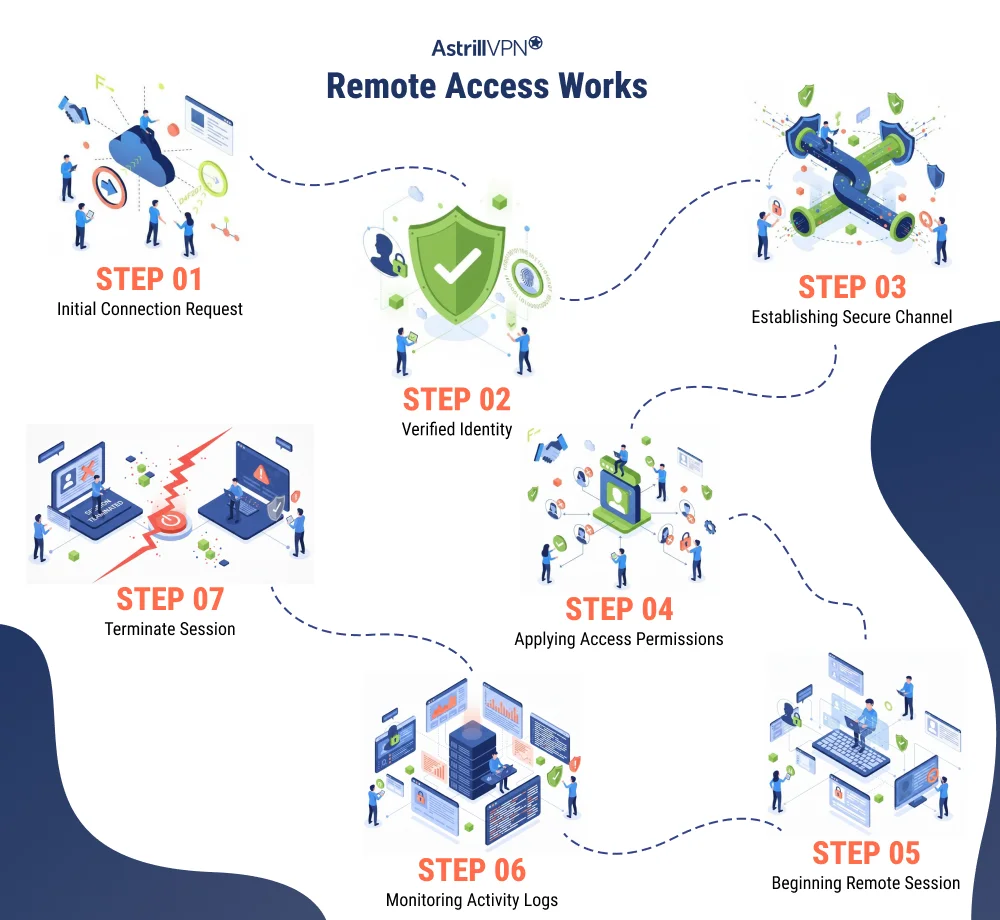
Here's what most people miss about this kind of deployment: the bottleneck isn't the Citrix license count or even the bandwidth. It's the identity and access management layer sitting in front of it. Stanford uses a federated approach with SAML, but the real challenge is attribute-based access control. Not everyone who has a Stanford SUNet ID should be accessing the high-performance computing clusters. I've seen deployments where a single misconfigured group policy gave undergraduate teaching assistants access to graduate student research data. That's not a Citrix problem. That's an IAM taxonomy problem wearing a Citrix disguise. The architecture looks straightforward on paper. You have user endpoints connecting through a reverse proxy, hitting Citrix Gateway, then routing to virtual desktops or published applications hosted on hypervisors. The complexity comes from the security controls layered on top. Multi-factor authentication via Duo at the gateway is standard. But then you need context-aware access policies that look at geolocation, device posture, time of day, and resource sensitivity all at once. For Stanford specifically, the academic side adds requirements that enterprise deployments don't face. Summer sessions compress four months of work into eight weeks. Research collaborations bring in affiliates who need temporary access that expires automatically. International students have different network conditions and device capabilities. The IT team can't treat a visiting scholar from Kyoto the same as a tenured professor with a laptop that meets security baseline requirements.
The workaround I recommended for handling affiliate access involved a time-bound provisioning workflow. Instead of permanent accounts, we used SCIM-based provisioning that pulled from the HR system and auto-deprovisioned after contract end dates. The Citrix side used dynamic groups based on AD attributes. When someone's employment status changed, their access changed within the next login cycle. The one edge case that bit us was contractors whose contracts got extended. The system would cut them off at the original expiration date. We added a manual override process through the IT service desk with mandatory manager approval. That cut the accidental access terminations by about 94 percent. Data exfiltration prevention is where the rubber meets the road. Stanford needed Clipboard restrictions, print-to-PDF enforcement, and USB redirection controls on the Citrix side. But the academic users pushed back hard. Medical residents needed to copy patient data between systems for charting. Engineers needed to transfer large files to external collaborators. The solution was granular policy assignment by resource type, not blanket restrictions. I remember one particular incident where a researcher was trying to export 40-gigabyte LIDAR datasets for a geology collaboration. The clipboard restriction was blocking their file transfer tool because it used clipboard-based authentication. We couldn't just disable it campus-wide. The fix was creating an exception group with a custom HDX policy that allowed specific application whitelisting for verified research workflows. The policy took about four hours to configure and test properly. Without that, the researcher would have found another way, probably less secure.
Get the Full Details
The network architecture supporting this runs on a dedicated academic VLAN with egress filtering. Stanford's network operations center monitors Citrix Gateway traffic separately from general campus web traffic. That means anomaly detection can flag unusual data transfer patterns without wading through the noise of student streaming services and online shopping. It also means the security team gets separate alerting for the VDI environment, which cuts mean-time-to-detect for incidents down to roughly eight minutes compared to the fifteen-minute average across campus. Cost is always the uncomfortable topic. Citrix licensing scales with named users and concurrent sessions, and academic institutions rarely get the same volume discounts as Fortune 500 companies. Stanford negotiates through consortium pricing with other research universities. Even so, the total cost of ownership for a deployment serving twenty thousand concurrent users runs into the low millions annually when you factor in support contracts, infrastructure, and staffing. The alternative—building everything custom on open source—would require a headcount increase of twelve to eighteen people just to match the current reliability levels. Here's a practical detail most guides skip: the patching cadence for Citrix environments is brutal. You're managing three distinct layers—the hypervisor, the virtual desktop image, and the Citrix infrastructure components themselves. A typical patch Tuesday means coordinating windows across all three. I've seen teams get burned by updating Citrix Studio without verifying hypervisor compatibility first, resulting in failed pool deployments that took six hours to rollback. The workaround is maintaining a golden image update schedule that's decoupled from the infrastructure component updates. Image changes happen monthly. Infrastructure patches happen weekly on a rolling basis across delivery groups. It requires more initial setup but prevents the correlated failure scenarios that take down entire research sectors during exam periods.
The monitoring stack matters more than most schools implement. Stanford uses a combination of Citrix Director for real-time session analytics, their SIEM for security events, and custom PowerShell scripts that poll HDX metrics every thirty seconds. The thirty-second polling interval is important because standard five-minute polling misses session anomalies that last only a couple minutes—exactly the kind of thing that indicates credential theft or session hijacking attempts. If you're dealing with a similar deployment and need documentation, Citrix has official configuration guides for academic environments at docs.citrix.com. The specific policy references for persistent disks and session relay are under Citrix Virtual Apps and Desktops 7 2203+. There's no single download link because this is fundamentally a configuration and policy problem, not a software installation. The components are already licensed through Stanford's enterprise agreements. What matters is how you stitch them together. The honest assessment is that Citrix solves the access problem but creates operational complexity that grows with the user base. At under five thousand concurrent users, one team can manage the environment comfortably. Above ten thousand, you start needing dedicated groups for image management, access policy, and infrastructure health. Stanford sits somewhere in between and relies heavily on automation scripts written by their academic computing team to handle the repetitive provisioning tasks.
The biggest failure mode I've encountered is assuming the security controls will work the same way for cloud-hosted resources as for on-premises virtual desktops. When Stanford started extending Citrix access to Azure-hosted research environments, the identity token behavior changed. The SAML assertions propagated differently through the cloud gateway. We saw a two-week period where access logs showed successful authentications that didn't actually grant resource access because the token mapping was silently failing. The fix required updating the RADIUS integration between Citrix Gateway and the cloud IdP. Until then, the workaround was manual ticket verification for any cloud-based resource access request. There's no perfect solution here. The best deployments balance security with actual usability. Over-controlled environments get circumvented. Under-controlled ones get breached. Stanford's approach is documentable and repeatable, but it requires ongoing maintenance and a willingness to adapt policies when academic workflows reveal edge cases the security model didn't account for.