Understanding Identity Theft Vectors in Modern Cybercrime
I spent about three years working identity fraud cases before moving into prevention consulting. The work was grim but it taught me how actual attackers operate. Most people have no idea how easy it is to strip someone down to their bare identity. Let me walk through what actually happens and what you can do about it. Cyber criminals don't need to hack your computer directly anymore. That was the old model, brute forcing passwords or planting malware through shady downloads. Now they use aggregated public data, social engineering, and credential stuffing on an industrial scale. The average stolen identity record sells for between $1 and $50 on underground markets depending on completeness. A full SSN with date of birth and address goes for more than a half-empty email login. Here's the mechanism most people miss. Data brokers compile profiles from thousands of sources: public records, loyalty programs, subscription services, social media, court documents, property records. They sell these packages without your consent. A criminal buys your compiled profile from a data broker for maybe twenty dollars and now they know your mother's maiden name, your childhood address, your birthday, and where you work. That's enough to reset passwords on most banking and utility accounts because those are the questions they use for verification.
I ran into a case last year where a client had her identity stolen through exactly this pipeline. Someone used her data broker profile to call her electric company, answered the security questions perfectly, and switched her account to a new address. By the time she noticed, the thief had racked up over four thousand dollars in charges and disappeared. The damage wasn't from a website breach or a phishing email. It was from publicly available information someone took the time to assemble. The workaround that actually worked was brutal but effective. She froze her credit at all three bureaus, filed police reports, flagged every account, and then spent roughly sixty hours on hold with various institutions. I still tell people to do this proactively instead of reactively. The freeze takes five minutes and saves you weeks of recovery.
What Attackers Actually Use Today
Credential stuffing dominates. People reuse passwords across dozens of sites. When one site gets breached, automated tools try those credentials everywhere else. The Have I Been Pwned database tracks over fourteen billion compromised records. If you've used the same password since 2016, there's a very good chance it appears in that dataset. Phishing has evolved too. It's less about generic lottery scams and more about highly targeted business email compromise or cloning legitimate login pages with perfect SSL certificates. I've seen phishing kits that replicate the exact interface of major banks, including proper domain names that differ by only one character. The typosquatting looks legitimate to anyone glancing quickly. SIM swapping is another vector worth understanding. Attackers call your mobile carrier pretending to be you, claim you lost your phone, and request a number port to a SIM they control. Once they have your number, they intercept two-factor authentication codes and gain access to email, banking, and social media. This happened to a crypto investor I consulted for a few years ago. He lost roughly eighty thousand dollars in a single afternoon because his phone number was his primary second factor for everything.
Get the Full Details

The fix there is straightforward but most carriers don't advertise it prominently. Set a PIN or passcode on your mobile account that must be provided before any changes are made. Call your carrier and ask for it. It takes about ten minutes on the phone and adds a layer that stops SIM swap attacks cold.
Practical Steps That Actually Matter
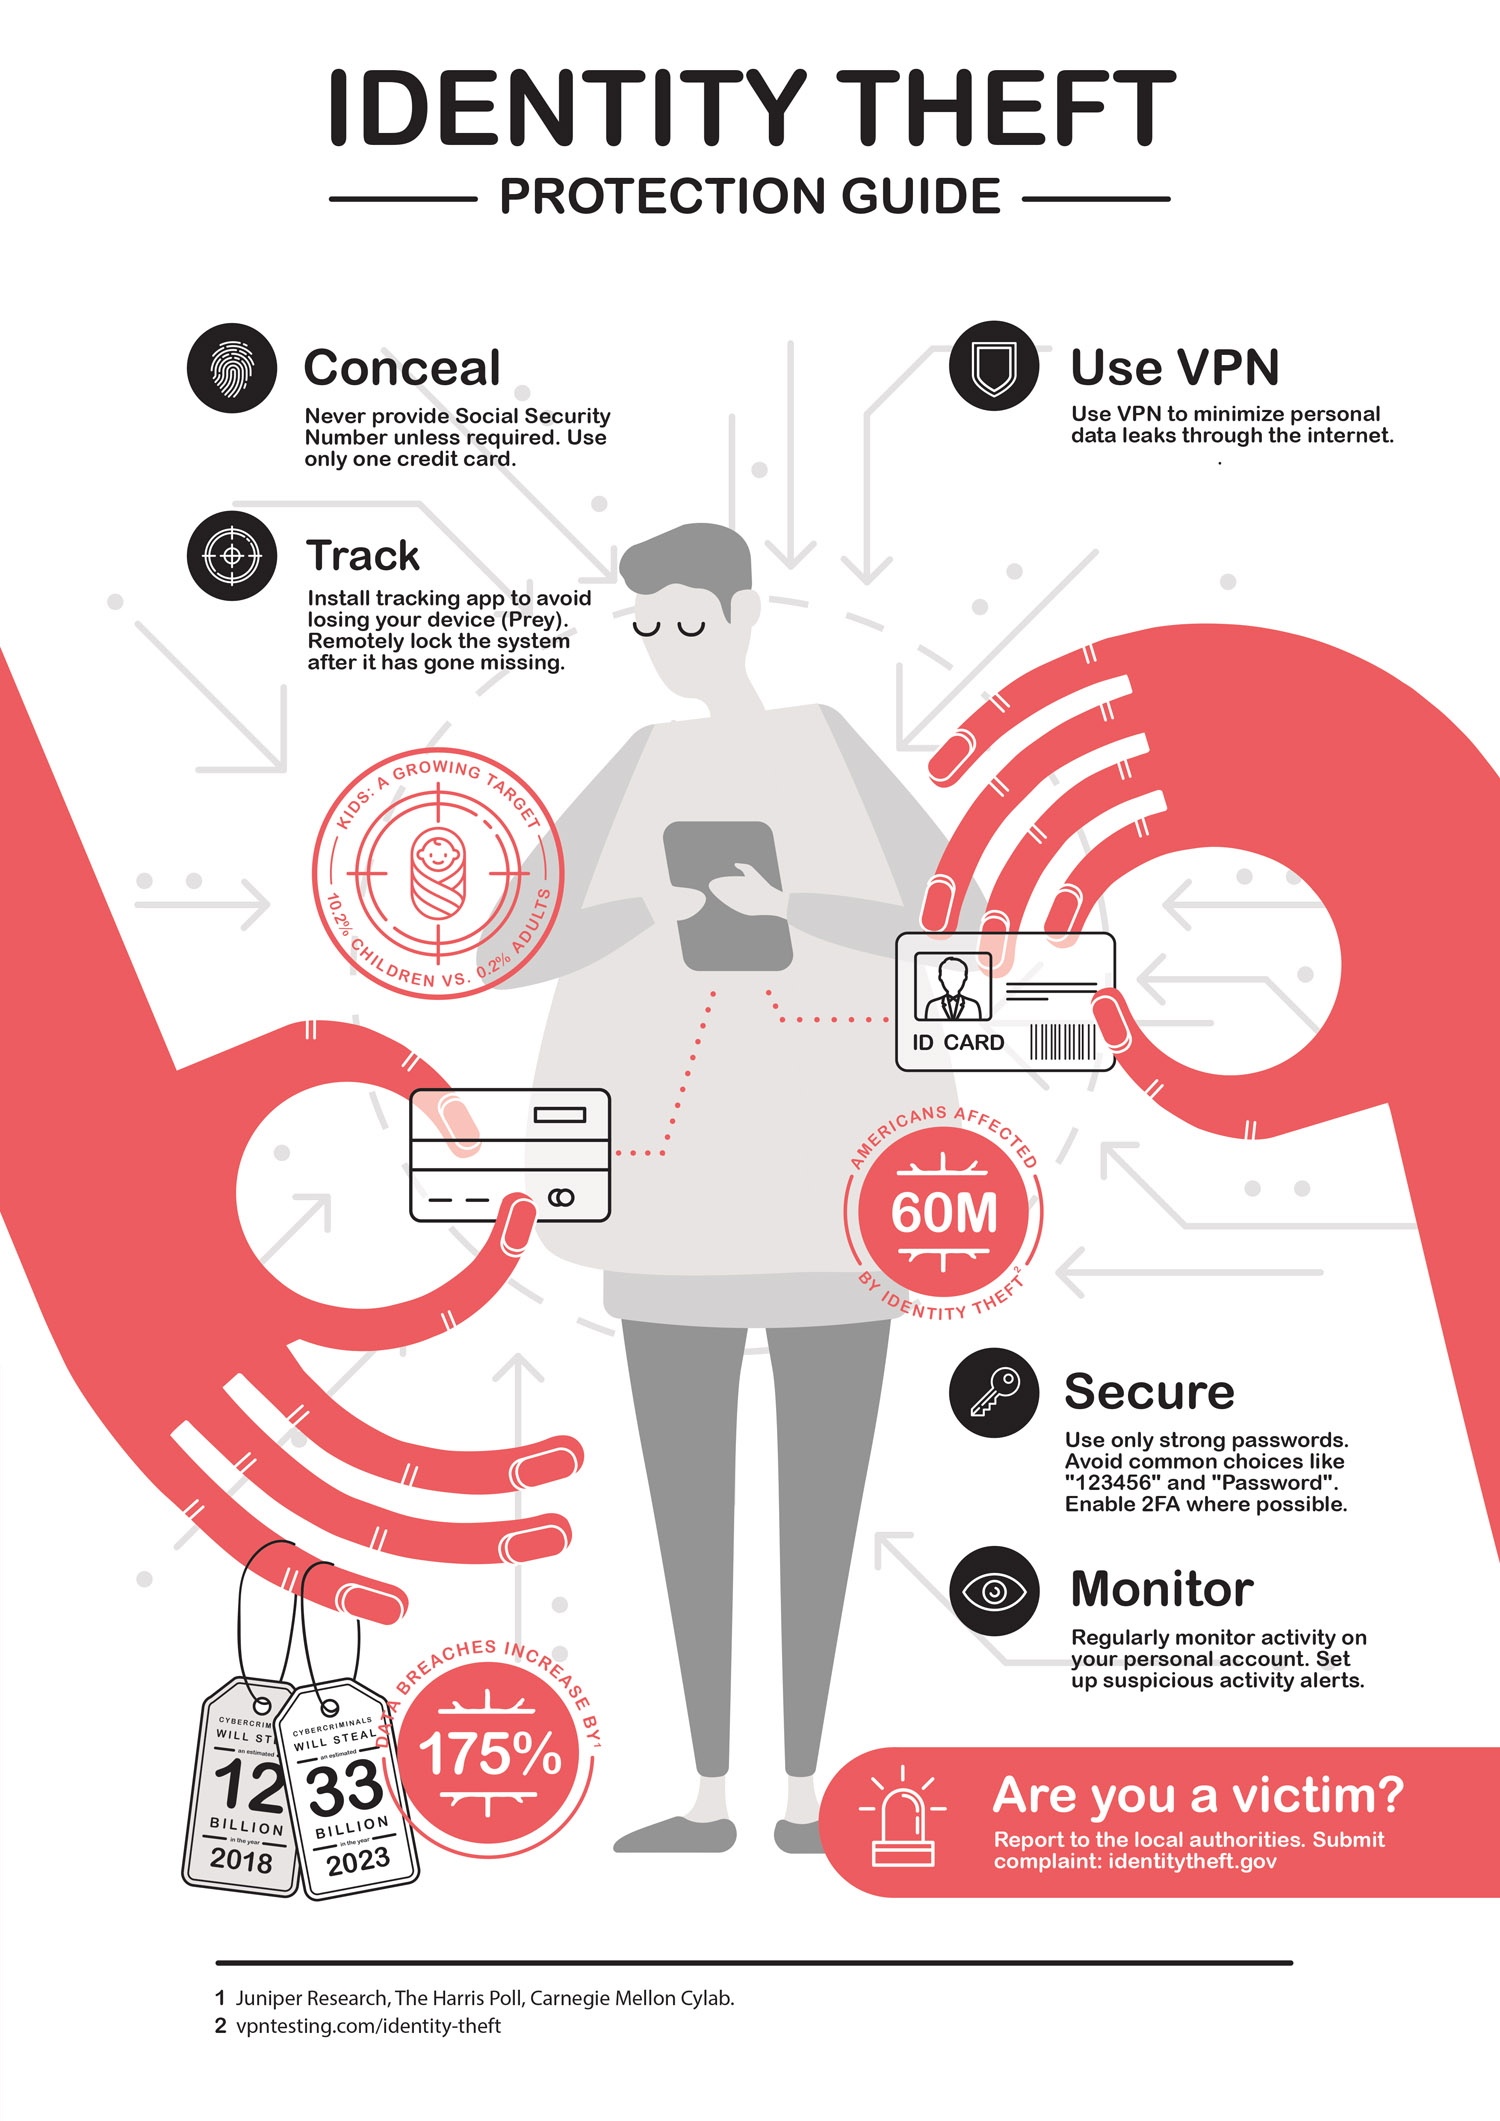
Use a password manager. Yes, it sounds obvious. But most people still reuse passwords or write them down. A password manager generates unique complex passwords for every site and stores them encrypted. Bitwarden is free and open source. 1Password costs about ten dollars a month but has better family sharing features. Pick one and use it consistently. Enable two-factor authentication everywhere possible. Prefer app-based authenticators or hardware keys over SMS when available. SMS is vulnerable to SIM swaps and SS7 network attacks that carriers generally don't protect against. YubiKeys cost around twenty-five dollars each and are virtually unhackable. I keep one attached to my keychain for anything financial. Freeze your credit. This is the single most effective step you can take. A credit freeze prevents anyone from opening new accounts in your name because lenders can't pull your credit report. It costs nothing and can be lifted temporarily when you actually need to apply for something. All three major bureaus support this: Equifax, Experian, and TransUnion.
Monitor your accounts regularly. Set up alerts on your bank and credit card accounts for unusual activity. Check your credit reports annually at AnnualCreditReport.com which is the official government-authorized site. You get free weekly reports now through 2026. Review them for accounts you didn't open or inquiries you didn't make. I should mention the limitation here. Credit monitoring services that advertisers push heavily don't actually prevent identity theft. They notify you after the damage is done. A freeze prevents the theft from happening in the first place. Monitoring is useful as a backup layer but it's not a solution. Spending money on a monitoring service while skipping the freeze is backwards.
What to Do If You're Already a Victim
Move fast. Time matters because thieves maximize damage before you catch wind. Call your banks and freeze every account. Place a fraud alert or security freeze on your credit. File a report at IdentityTheft.gov which creates a personalized recovery plan and generates letters you can send to creditors. File a police report locally even if they tell you it's not a local crime. You need the report number for certain institutions. Document everything. Keep a log with dates, times, names of representatives you speak with, and reference numbers. I've seen people recover funds successfully because they had detailed records that proved the timeline. Without documentation, institutions treat you as just another complaining customer and the process drags on indefinitely. Expect the long tail. Identity theft recovery isn't resolved in a week. It can take months or years to fully clear fraudulent accounts and restore your financial standing. Stay persistent. Follow up weekly. Escalate to supervisors when front-line representatives say they can't help. Most of the time there's a path forward if you refuse to stop pushing.
There's no perfect defense against this. Attackers have more resources and patience than any individual. But the steps above dramatically reduce your risk profile. Most identity theft is opportunistic, not targeted. Make yourself a harder target and move on with your life.