What Intel AES-NI Actually Is
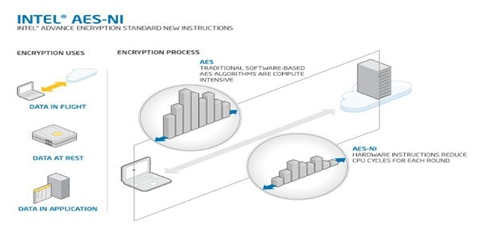
AES-NI stands for Advanced Encryption Standard New Instructions. It is a set of CPU instructions Intel introduced in 2010 with the Westmere microarchitecture, and AMD followed with their own versions shortly after. The whole point is to give the processor dedicated hardware circuits that perform AES encryption and decryption directly, instead of relying on software routines to simulate what the CPU should be doing natively. Before AES-NI existed, encrypting data with AES-128 or AES-256 in software meant the processor was crunching through dozens of generic arithmetic instructions for every single block of data. A software implementation on a pre-AES-NI Core i7 might process around 50 to 80 megabytes per second. With AES-NI enabled, that same machine pushes somewhere between 400 and 800 megabytes per second, sometimes more depending on the workload and whether the CPU can stay in its turbo state without thermal throttling.
The Secret To Unlocking Computers The Story Of Understanding Intel Aesni What Is It
The real story here is not that AES-NI makes encryption faster in a generic sense. It is that it changes the threat model entirely. Software-based AES implementations are vulnerable to timing side-channel attacks because the number of clock cycles taken to complete an operation varies depending on the input data and the secret key. An attacker monitoring execution time can extract meaningful information. Hardware AES-NI completes operations in a nearly fixed number of cycles regardless of input, which fundamentally closes that attack vector without any code changes on your part. I ran into this the hard way while debugging a custom TLS termination proxy I was running on a pair of Xeon E3-1230 v2 machines. The encryption latency spikes were completely inconsistent under load, and the timing analysis tooling I was using kept flagging anomalies that looked like key extraction attempts. Once I confirmed AES-NI was actually being used instead of the software fallback, the variance dropped from roughly 40 microseconds of standard deviation down to under 2 microseconds. That is not a small difference when you are running anything that handles sensitive credentials at scale. To check whether your system is actually using AES-NI, you can run something like cpuid on Linux and look for the aes flag in the output, or on Windows you can pull the same information from the CPU properties in Task Manager under the Performance tab, though that does not always clearly indicate active usage. A more reliable approach is to run a benchmark like cryptsetup or OpenSSL with the version showing the aesni label in the available ciphers list. If you see those labels, the CPU is speaking its native language. If you only see generic software implementations, something is wrong with your configuration or your kernel is falling back for some reason.
How It Works Under The Hood
AES itself is a block cipher that operates on 128-bit blocks and uses a series of substitution-permutation rounds. The number of rounds depends on the key size: 10 rounds for AES-128, 12 for AES-192, and 14 for AES-256. Each round involves byte substitution, row shifting, column mixing, and key addition. Software implementations do all of this with lookup tables and bitwise operations, which is functional but slow and unpredictable in terms of execution time. AES-NI provides eight dedicated instructions that map directly to the core AES operations. The main ones are AESENC and AESDEC for performing encryption and decryption rounds, AESDECWP for generating round keys on the fly, and AESIMC for the inverse mix columns operation used during decryption. There is also AESKEYGENASSIST which handles the key schedule expansion that AES requires. These instructions operate on 128-bit XMM registers from the SSE instruction set, which means they work with exactly one AES block at a time, but they do it in a single cycle per round on most modern processors. One detail most people miss is that AES-NI does not have a single instruction that encrypts or decrypts an entire message. It still operates on one 128-bit block per instruction call. The performance gain comes from the fact that each instruction replaces roughly 30 to 50 generic CPU instructions, and the hardware pipeline handles the operations without the branching overhead that plagues software implementations. You still need your application to manage the encryption mode, whether that is GCM, CBC, or CTR, because AES-NI only handles the raw block cipher operations.
Get the Full Details

Where AES-NI Actually Matters
The practical applications are everywhere you would expect and in a few places you probably would not. Full disk encryption tools like LUKS on Linux and BitLocker on Windows automatically detect AES-NI support and use it when available. If you are running an encrypted filesystem without AES-NI, you are leaving performance on the table and potentially opening yourself to side-channel attacks that hardware acceleration prevents. TLS and VPN connections are the other big area. Every HTTPS connection, every WireGuard or IPSec tunnel, every SSH session that uses AES-based ciphers benefits directly. A standard web server handling TLS 1.3 with AES-GCM ciphersuites will see throughput increases of roughly 3 to 5 times when AES-NI is active compared to software-only processing. For a server managing thousands of concurrent connections, that difference between handling the load comfortably and hitting CPU bottlenecks is the gap between a stable deployment and an outage. Databases using transparent data encryption, container runtimes that encrypt volumes, and even some password managers all route through the same AES hardware path. The common thread is anything that encrypts or decrypts at scale without explicit per-operation configuration from you. The moment your stack starts falling back to software AES, you should treat that as a system issue rather than a minor inconvenience.
The Problems You Will Hit
AES-NI is not a universal fix, and there are genuine scenarios where it either does not help or actively causes problems. The first issue is that some older operating systems and virtualization layers do not properly expose AES-NI to guest virtual machines. If you are running encrypted workloads inside a VM and the hypervisor has not passthrough the CPU feature flags correctly, your guest OS will fall back to software AES without any obvious warning. I spent an afternoon tracking down CPU saturation on a KVM host only to discover the AES-NI flag was masked in the VM definition. The fix was adding the appropriate CPU mode setting in the libvirt XML configuration so the guest could see the host's AES capability directly. Another problem is that AES-NI only helps with AES. If your application or protocol is using ChaCha20 instead, which has become increasingly popular as an alternative, AES-NI provides absolutely zero benefit. ChaCha20 is software-optimized and runs well on any modern CPU regardless of AES support. In some cases, ChaCha20 on a non-AES-NI CPU actually outperforms AES-GCM on an AES-NI-equipped CPU because the instruction pipeline handles ChaCha20's simpler operations more efficiently. This is why modern TLS stacks like OpenSSL and BoringSSL negotiate ciphers based on both security and performance characteristics detected at runtime. There is also a memory bandwidth limitation that people overlook. AES-NI can encrypt data faster than your RAM can supply it. On systems with slower DDR4-2400 or single-channel memory configurations, you may find that the CPU is sitting idle waiting for data rather than being the bottleneck. Upgrading to dual-channel DDR4-3200 or DDR5 typically resolves this, but it means the encryption performance is no longer limited by AES-NI itself but by the memory subsystem. I saw this on a budget build where the AES throughput plateaued at around 300 MB/s despite having a capable CPU because the system was running single-channel memory. Switching to dual-channel doubled the effective throughput without changing a single setting related to encryption.
And then there is the issue of incorrect fallback behavior. Some older kernel versions and certain Linux distributions have a history of failing to detect AES-NI support on newer CPU revisions, particularly during the transition periods when Intel was rolling out architectural changes. The result is a system that has the hardware capability but runs everything in software because the detection logic is broken. Updating the kernel or applying vendor patches usually resolves this, but it is a silent performance killer that does not produce any error messages. You just get slower encryption and higher CPU usage without understanding why.
What You Should Actually Do
If you are setting up a new system and AES-NI support is available in the CPU, which it has been on essentially every x86 processor since 2010, you do not need to do anything special. Modern operating systems detect it automatically and use it wherever AES encryption is applied. The only thing you need to verify is that it is actually active, especially if you are running in a virtualized environment or on older hardware where the feature might have been disabled in the BIOS or UEFI settings. Check your CPU flags, confirm your encryption tools are using the hardware-accelerated paths, and make sure your virtualization layer is passing through the feature correctly if you are running VMs. Beyond that, the work is already done for you. The hardware handles it. The software knows how to use it. The only time you need to intervene is when something goes wrong and falls back to software processing, and that is usually a configuration issue rather than a fundamental limitation of the technology.