Parrot OS: What It Actually Is and Who It's For
Parrot OS is a Debian-based Linux distribution developed by the Italian company Parrot Security. It's aimed primarily at cybersecurity professionals, developers, and privacy-conscious users. Unlike Kali Linux, which leans heavily toward offensive security, Parrot positions itself as a multi-purpose workstation that happens to be excellent for security work. It runs on Debian stable, which means updates are generally more reliable than rolling-release distros that sometimes break between versions. The core architecture follows a lightweight design philosophy. The default desktop environment is MATE, though they also offer KDE Plasma and GNOME flavors. The security-focused edition comes bundled with over 400 tools for penetration testing, digital forensics, reverse engineering, and cryptography. That list includes standard tools like Nmap, Burp Suite, John the Ripper, and Wireshark, but it also includes less common utilities that you'll only find in specialized distributions.
The Rise Of Parrot Operating System Revolutionizing Linux Distributions
The narrative around Parrot's growth is interesting because it fills a gap that existed between Kali's heavy security focus and Tails' anonymity-only approach. Users who wanted a system that could handle daily development work AND security testing found Parrot to be the bridge. The rise has been steady rather than explosive. It hasn't had the viral moments that some newer distros get, but the community has grown organically through forums, GitHub contributions, and word of mouth among security practitioners. What distinguishes Parrot from its competitors is the documentation approach. The official wiki covers both basic setup and advanced configuration scenarios. The community actively maintains GitHub repositories for tool updates and custom scripts. This matters because security tools become obsolete quickly, and a distro that doesn't keep pace will frustrate users within months.
Installation and Initial Setup
Download the ISO from the official Parrot website. They offer both the full security edition and the lighter Home edition. For security work, grab the full version. The file is approximately 4.5 GB, so plan for that bandwidth. Write it to a USB drive using balenaEtcher or dd, depending on your host system. The standard partitioning scheme works for most installations: single partition with ext4, or LVM if you want encryption from the start. One thing worth noting about the installation process: the default disk encryption setup uses LUKS, which is solid. But the passphrase prompts during boot can be confusing if you're not used to reading the GRUB menu carefully. I've seen users enter the wrong passphrase three times and assume the disk is corrupted. It's not. The system is just waiting for the correct key. Take your time with the bootloader. After installation, the first thing I'd recommend is running a full system update. Open a terminal and execute:
Get the Full Details
sudo apt update && sudo apt upgrade -y This pulls the latest security patches and tool versions. The process typically takes 10 to 15 minutes on a decent connection, depending on how much has accumulated since your ISO was built.
Navigation and Tool Organization
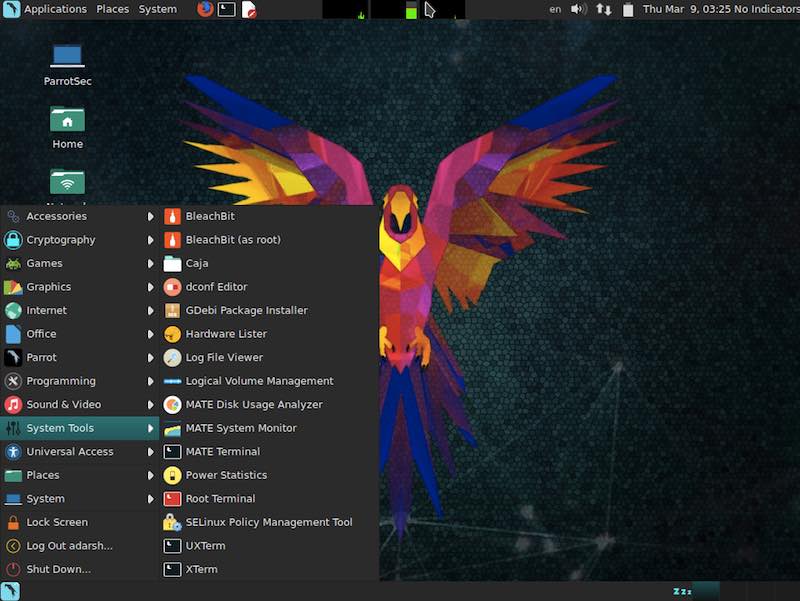
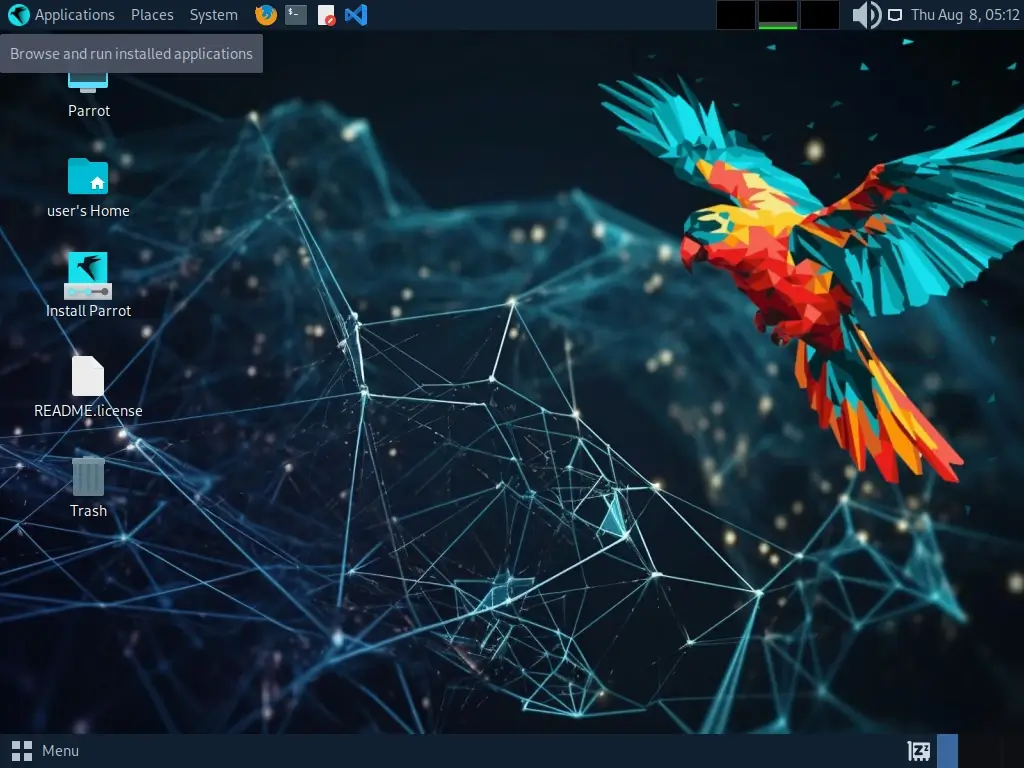
Parrot uses a menu-driven approach for its toolset. The main application menu is divided into categories: Information Gathering, Vulnerability Analysis, Web Applications, Password Attacks, Reverse Engineering, Forensics, and Sniffing & Spoofing. Each category contains relevant tools organized alphabetically. The interface is functional rather than flashy. If you're coming from Kali's Xfce-based layout, the MATE environment might feel slower initially. It's not actually slower—MATE is well-optimized—but the visual language is different. Give it a few days to feel natural. The toolbar and sidebar layouts are customizable if you want to reorganize things.
Practical Use Cases and Real-World Workflow
Here's how Parrot typically gets used in practice. A penetration tester might boot the system from USB for a one-off engagement, or install it permanently on a dedicated machine for ongoing security work. The portable nature of the live USB with persistence is one of its stronger features. You can carry your entire toolkit and configurations on a thumb drive. For virtual machine use, Parrot runs well in VirtualBox and VMware. Enable nested virtualization if you need to run containers or additional VMs inside the guest. The guest additions installation is straightforward: mount the ISO, run the VBoxLinuxAdditions.run script, and reboot. Network performance improves noticeably after this step. I once encountered a specific issue where the Broadcom WiFi driver wouldn't cooperate on a laptop during a wireless assessment. The system detected the hardware but couldn't associate with any networks. The workaround was installing the proprietary brcmfmac driver through the restricted drivers menu, followed by a firmware package reinstall: sudo apt install --reinstall firmware-brcm80211. After that, the adapter worked reliably. This isn't a Parrot-specific problem—it's a Linux WiFi driver issue that shows up across many distros—but it's worth knowing the fix is accessible without leaving the system.

Common Pitfalls and Counter-Intuitive Truths
One thing beginners often miss: Parrot is not designed to be a primary daily driver for most people. The pre-installed toolset is extensive, but it's also resource-heavy. If you're running this on older hardware with 4 GB of RAM or less, expect slowdowns, especially when multiple tools are open simultaneously. The Home edition exists for this reason—it strips out the security tools and focuses on productivity. Another pitfall is the assumption that all installed tools work out of the box. Several tools require additional configuration or dependencies that aren't installed by default. For example, setting up a proper SQLmap environment might need additional Python packages. Running sudo apt install python3-pip and then using pip to install missing dependencies usually resolves these gaps. The documentation links from the Parrot website can point you to the right place, but you'll encounter situations where you need to troubleshoot independently. A less obvious limitation: Parrot's approach to package management means you have access to both Debian's repositories and Parrot's custom repository. Mixing sources can occasionally cause dependency conflicts, especially if you pull packages from third-party APT sources. It's safer to stick with the official repositories unless you have a specific reason to add external sources.
Performance Considerations
On a modern system with 8 GB RAM and an SSD, Parrot boots in roughly 20 to 30 seconds and handles multitasking well. With 4 GB RAM, you'll notice the difference when running memory-intensive tools. The MATE desktop is lighter than KDE or GNOME, but it still consumes around 600 MB to 1 GB of RAM at idle. Factor that into your hardware planning. For hardware that's too old for comfortable Parrot use, consider lighter alternatives. AntiX or LXLE might serve you better on machines with 2 GB or less. These distros sacrifice some of Parrot's polish and tooling for genuine performance gains on aging hardware.
Community and Ongoing Support
The Parrot community is active but not massive. The GitHub organization has numerous repositories for tools, scripts, and documentation. The mailing list sees regular traffic on technical questions. The Discord server is more casual but useful for quick help. Response times vary—sometimes within hours, sometimes a day or two—but the quality of answers tends to be high because the contributor base includes actual security professionals. The official documentation is comprehensive for core functionality but can be thin on edge cases. This is common across security-focused distros. The workaround is combining the wiki with general Linux knowledge and the Debian documentation, which Parrot inherits as its foundation.
When Parrot Makes Sense and When It Doesn't
Parrot is a strong choice if you need a system that balances daily computing with security work. The toolset is current, the Debian base is stable, and the documentation is adequate. It's less ideal if you're looking for a purely offensive security distro with the deepest Kali toolchain, or if you need maximum anonymity and prefer Tails' circuit-based networking model. The system works best when you understand what it is and what it isn't. It's a security workstation, not a magic bullet. The tools still require knowledge to use effectively. The documentation is a starting point, not an encyclopedia. And like any Linux system, it will demand your attention when things don't go as planned—which they won't, occasionally. If you're willing to invest time in learning the toolset and the underlying Linux environment, Parrot delivers consistent performance and a reliable foundation for security-focused work. The rise has been measured because the product speaks for itself through utility rather than marketing. That's typically the more sustainable path for a distribution in this space.


