So You Want to Understand What Is Actually Happening in Banking Right Now
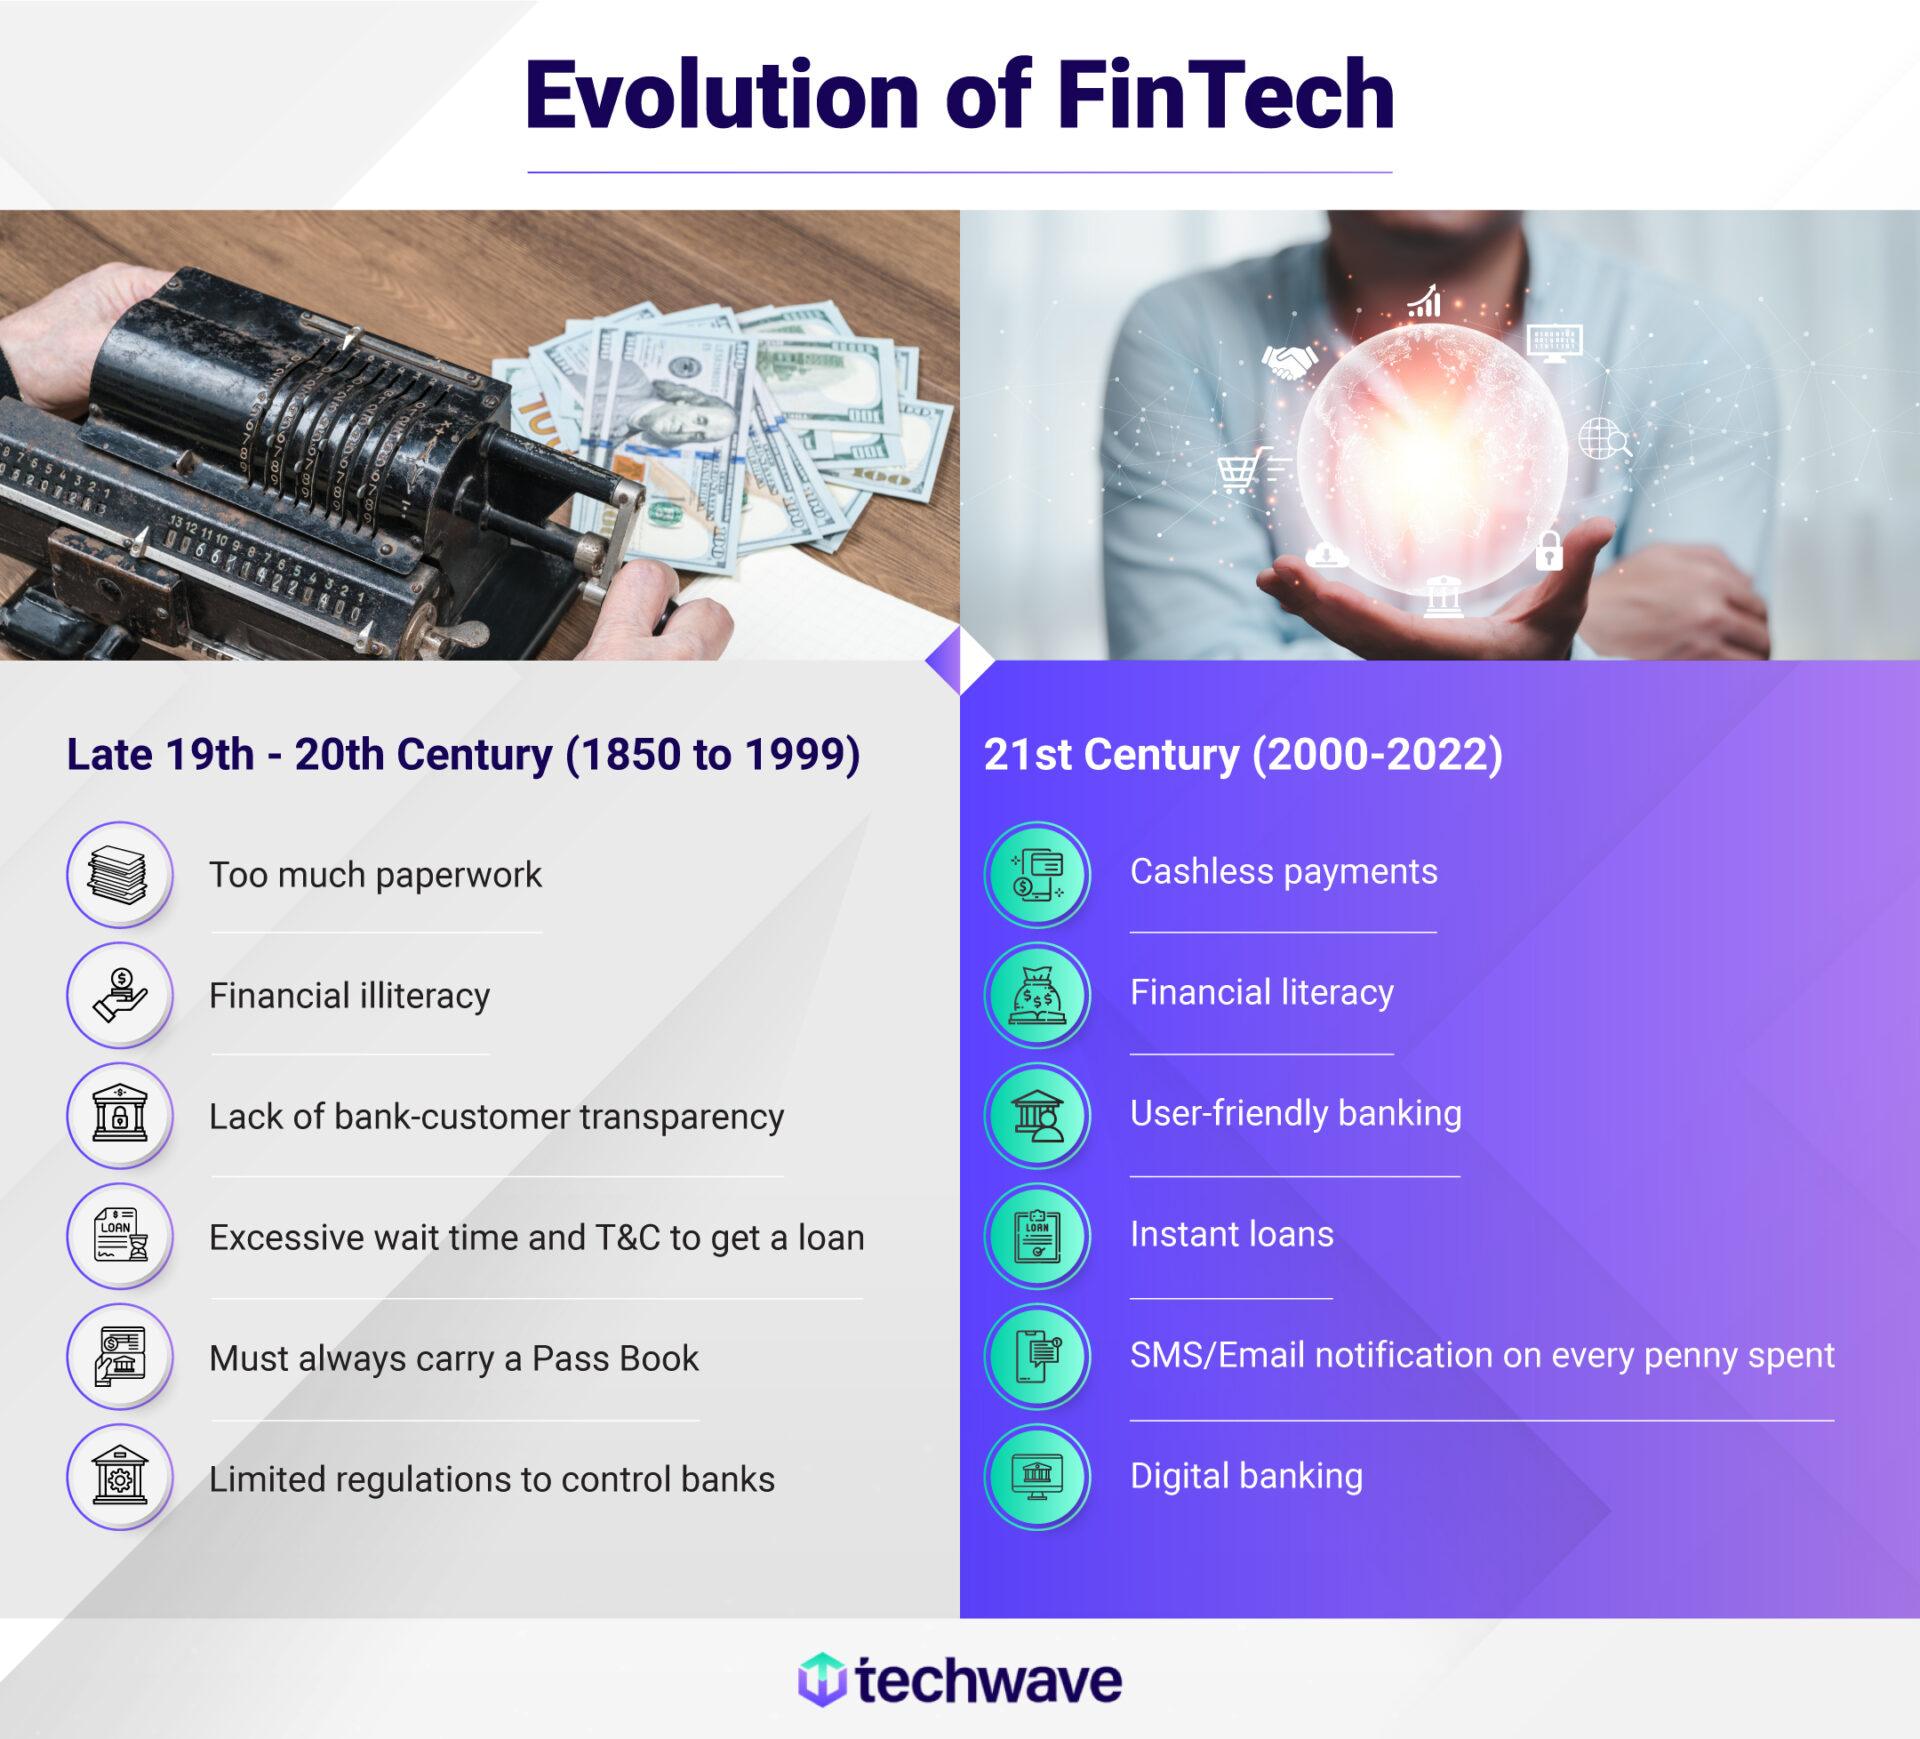
Most people think fintech is just apps with nice logos and instant transfers. It is more than that. The banking industry is going through a structural shift that has been underway since roughly 2015, and it is not slowing down. Legacy systems built on COBOL are colliding with cloud-native architectures, and the friction between those two worlds is where the real story lives. I spent years embedded in payment integration projects across mid-tier banks, so I have seen what happens when these systems try to talk to each other. The revolution is not happening because fintech companies are out-innovating banks. It is happening because they stopped trying to replicate the entire banking stack and instead focused on single points of failure. Open banking APIs changed the economics of customer acquisition overnight. Before that, a bank needed a physical branch, marketing spend, and months of compliance review to gain a new retail customer. Now a neobank can acquire the same customer through an API handshake and a well-designed onboarding flow in about eight minutes. That compression of the customer journey is what actually broke the old model. But here is the part nobody talks about enough. The technology itself is usually not the bottleneck. The bottleneck is data residency compliance, legacy core banking middleware, and the fact that most banks still route critical transactions through batch processing windows that close at specific times. I once worked on a project where a fintech partner claimed their API could settle funds in under three seconds. The API absolutely could do that. The problem was the bank's core system only processed incoming payment feeds at 2:00 AM and 8:00 AM. So the "real-time" settlement became a four-hour wait depending on when the request landed. No amount of API optimization fixes a core that processes in batches. You either replace the core or you accept the latency.
Let me give you a concrete example of how this plays out in practice. A mid-sized regional bank I consulted for wanted to launch a digital lending product. Their plan was to use an external credit scoring engine instead of their legacy underwriting system. The external engine returned decisions in 900 milliseconds. The bank's internal system took fourteen minutes and still required manual review for anything above fifty thousand dollars. They went with the external engine. What they did not account for was that the external engine had no visibility into the customer's existing deposit relationships, which their legacy system tracked but the API gateway did not expose. They approved three hundred loans in the first month that should have been declined based on existing overdraft exposure. They lost about two percent on the first quarter's books. The workaround was straightforward but expensive: they built a reconciliation layer that pulled nightly from the core system and cross-referenced it against approved applications before disbursement. That added about forty-five seconds to the decision flow. It also eliminated the loss entirely.
How the Architecture Actually Works Under the Hood
A modern fintech banking stack typically consists of four layers. The first is the customer-facing layer, which includes mobile apps, web platforms, and increasingly voice or chat-based interfaces. The second is the API gateway, which handles authentication, rate limiting, and request routing. This is where Open Banking compliance happens through PSD2 or equivalent frameworks depending on your jurisdiction. The third is the orchestration layer, which coordinates between different microservices for identity verification, credit checking, transaction processing, and compliance screening. The fourth is the data layer, which includes both the real-time event stream and the persistent ledger. What most people miss is that the orchestration layer is where most failures occur. Not because the code is bad, but because the services are designed by different teams with different assumptions about data format, timing, and error handling. I have seen production incidents where a fraud detection service and a transaction processing service disagreed on the timestamp of a disputed charge because one used server time and the other used a blockchain-anchored consensus time. The dispute resolution took six weeks to untangle. Neither team was wrong. They were just using different time sources without a shared reference frame. The fix was implementing a canonical timestamp layer at the orchestration level. Standard solution, but you would not know that reading any marketing material about the product. There is also a common misconception about blockchain and distributed ledger technology in banking. It solves specific problems very well, primarily double-spend prevention and audit trail immutability. It does not solve latency, and it does not solve compliance. A bank that implements a blockchain-based settlement layer without also building the regulatory reporting infrastructure around it will have a beautifully transparent system for moving money that still cannot produce the daily filings its regulators require. I watched one institution spend eighteen months and approximately four million dollars on a DLT pilot that got shelved because the compliance team could not map the ledger entries to their reporting schema. The technology worked perfectly. That was not the problem.
Get the Full Details

What Actually Works When You Are Building This Stuff
If you are evaluating fintech solutions for a banking environment, start with the integration layer, not the product features. Most vendors will show you a polished dashboard and a demo that runs on pristine test data. Ask them to show you their error handling for rejected API calls, their retry logic, and their data format when things go wrong. The way a system behaves when it fails tells you more than anything it does when it succeeds. I once rejected a vendor whose documentation claimed 99.99 percent uptime but whose error responses returned null values instead of structured error codes. Structured errors matter when you are debugging a transaction that failed at 3:14 AM on a Saturday and you have forty-five seconds to decide whether to escalate it. Another practical consideration is the difference between sandbox environments and production parity. Many fintech platforms offer sandboxes that behave differently from their production systems in ways that are not documented. Currency conversion rates, fee calculations, and retry timing can all shift between sandbox and production. I had a client who built their entire integration in sandbox, passed all their tests, and then spent three weeks in production debugging why their fee calculation was off by 0.03 percent. The sandbox used rounded exchange rates and production used mid-market rates with different rounding rules. The documentation mentioned rounding behavior in a footnote on page forty-seven of the API reference. Something easy to miss. Regulatory compliance should be treated as a first-class requirement, not an afterthought. When you integrate a fintech solution, you need to understand which party holds the regulatory license for each part of the transaction flow. Is the bank the licensed entity, or is the fintech partner acting as a delegate? This distinction affects everything from AML monitoring obligations to data protection responsibilities. I worked on a project where both parties assumed the other held the licensing responsibility for cross-border payment reporting. The transaction went live for six months before anyone realized neither party had filed the required reports. Both were wrong. Both were also technically correct based on the contract language they signed. It got resolved, but it cost the bank a compliance review that took four months and required external legal counsel at about three hundred fifty dollars an hour.
The Limitations Nobody Highlights
Fintech solutions introduce new risks even as they solve old ones. Real-time payment processing means real-time fraud exposure. A system that approves transactions in under a second does not have time for the multi-layered review process that batch systems implicitly provided. Fraud rates on instant payment platforms are measurably higher than on traditional card networks because the window for chargeback and reversal is dramatically shorter. Some institutions have seen fraud rates increase by one to two percentage points when switching from batch to real-time processing. That is not a theoretical concern. It happened at a credit union I advised in the Midwest when they moved to instant payment rails without adjusting their fraud scoring thresholds accordingly. Another limitation is vendor lock-in disguised as convenience. Many fintech platforms use proprietary data formats and API structures that make migration difficult. When you build your integration around a specific vendor's implementation, switching costs compound over time. I saw a bank evaluate migration away from a major fintech provider after three years and find that their historical transaction data was stored in a format that required custom extraction scripts to interpret. The vendor's export tool only supported their current format, not the one they used two years ago when the schema changed. They spent about sixty engineering hours rebuilding their data pipeline just to compare records. There is also the question of concentration risk. The banking industry has ended up relying on fewer fintech providers than appears on the surface. A surprising number of banks use the same three or four infrastructure vendors for core services like identity verification, payment routing, and compliance screening. When one of those vendors experiences an outage, multiple banks feel it simultaneously. The 2023 incident where a major identity verification provider had a fourteen-hour outage is a good example. It took down onboarding flows at roughly a dozen financial institutions at the same time. There is no easy fix for this beyond diversification, and diversification is expensive because building alternatives in-house requires significant engineering investment that most banks would rather put elsewhere.
API fatigue is a real issue for development teams. A typical modern banking integration might connect to twelve to twenty different external services, each with their own authentication method, rate limits, documentation quality, and support responsiveness. Maintaining those connections is a continuous effort, not a one-time setup. Teams that treat API integration as a deploy-and-forget activity usually find themselves playing technical debt catch-up within six months. I recommend budgeting for ongoing API maintenance at roughly twenty percent of the initial integration effort per year. That covers documentation drift, authentication rotation, deprecation notices, and the inevitable emergency migration when a vendor changes their API without adequate notice.

Where the Industry Is Actually Going
Embedded finance is probably the biggest structural trend shaping the next phase. Banking services are moving out of banks and into non-financial platforms. A ride-sharing app offering instant payouts, a retail platform providing point-of-sale financing, a healthcare portal handling insurance claims processing. The technology enabling this already exists. What is still emerging is the regulatory framework for it, and that framework is developing slower than the technology is advancing. Institutions that move quickly on embedded finance without adequate regulatory alignment are taking on risk that may not be visible until a regulator decides to look closely. Real-time gross settlement is expanding globally but at different speeds in different jurisdictions. The US Federal Reserve's FedNow service, the UK's Faster Payments, the EU's SEPA Instant Credit Transfer, India's UPI. Each operates on different timelines, cost structures, and dispute resolution mechanisms. For institutions operating across borders, interoperability between these systems remains one of the hardest engineering problems in the industry. There is no universal standard yet. The SWIFT GPI network attempts to address this, but it covers only a subset of the transaction types that domestic real-time systems handle, and the coverage is uneven. Artificial intelligence in banking is getting a lot of attention, but the practical applications that are actually moving the needle are narrower than the hype suggests. Credit scoring, fraud detection, and customer service automation are the areas with proven ROI. Generative AI for code generation and documentation is real but still early in terms of production reliability. Most banks are running AI initiatives in controlled environments rather than deploying them into customer-facing decision loops. That is probably the correct posture given the current state of explainability requirements in financial regulation. If you cannot explain why an AI model declined a loan application, you cannot use it for loan decisions in most regulated markets today.
The infrastructure beneath all of this is slowly modernizing, but it is happening at the speed of bureaucratic processes and risk aversion. Core banking system replacements take three to seven years on average. Many of the systems still running were designed for an era before real-time processing, before mobile banking, before open banking. They work, which is the main thing keeping them in place. The replacement decision is rarely about whether the new system is better. It is about whether the institution can absorb the cost, risk, and operational disruption of the transition. Most decide to patch the existing system until something forces their hand. Usually it is a regulatory requirement or a competitor doing something the existing system cannot support. The banking industry is not being replaced by fintech. It is being absorbed by it, piece by piece, through integration rather than takeover. The institutions that understand this and plan their integration strategy accordingly are the ones that will remain relevant. The ones that treat fintech as either a threat or a novelty tend to fall behind when the next cycle of regulatory change or competitive pressure arrives. The technology keeps improving. The question is whether the organizations building with it are thinking about what comes after the integration works on the first try.