Why Your Security Budget Keeps Expanding
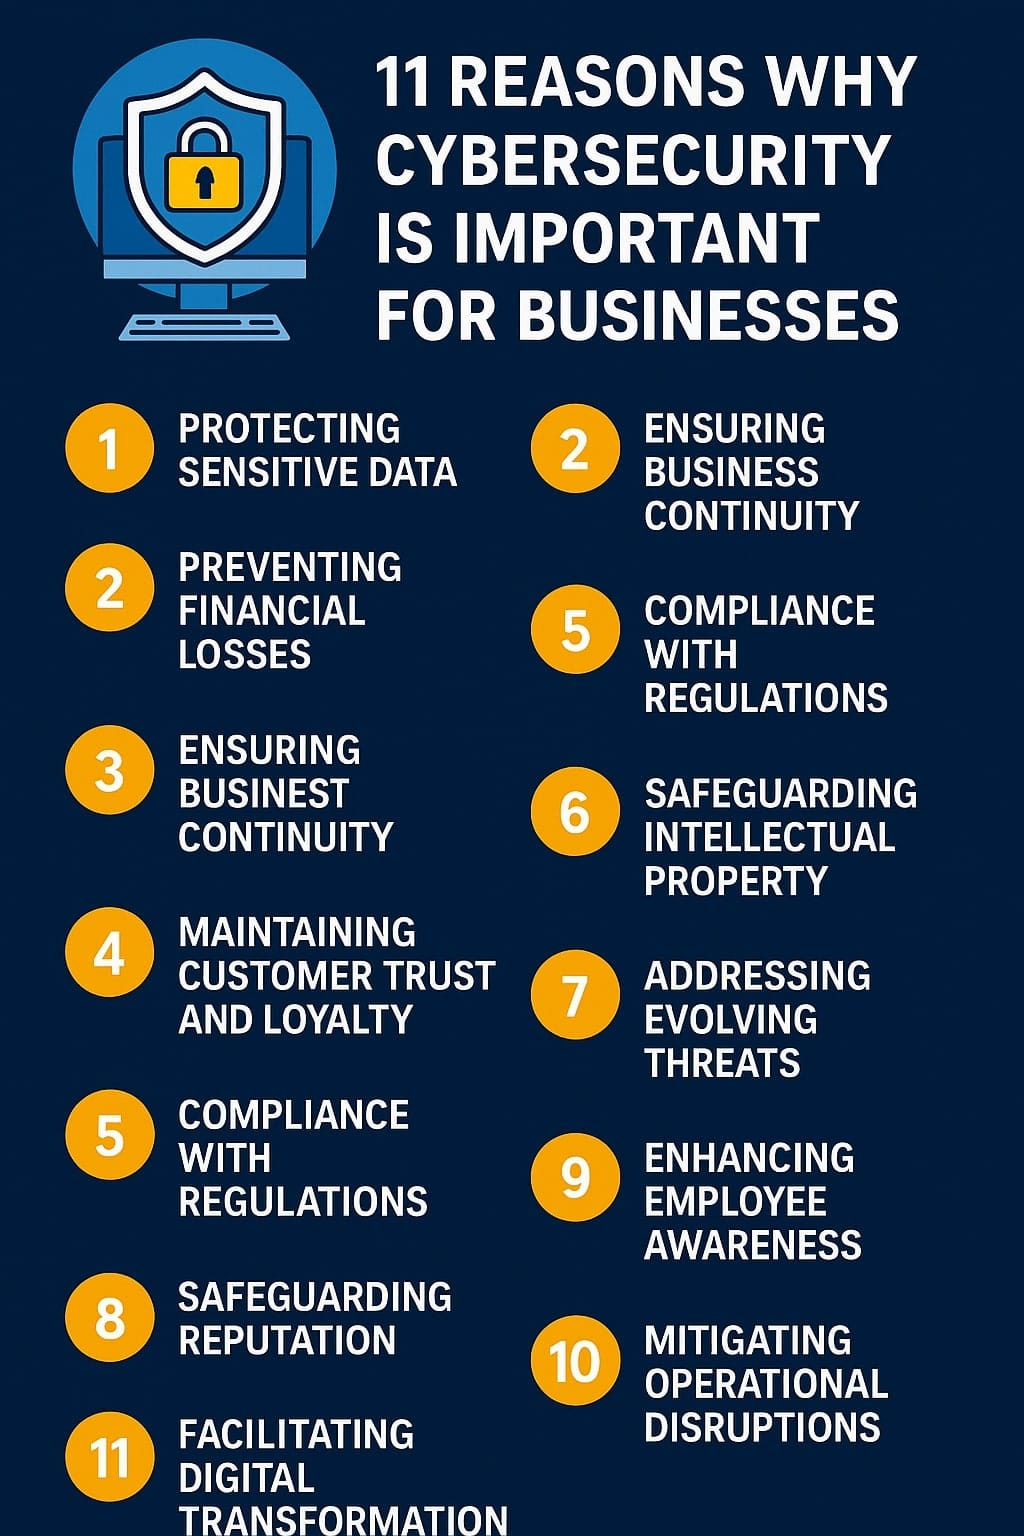
I have been in the security procurement room for over a decade, and the conversations always follow the same arc. First comes the denial phase, where someone swears the last ransomware attempt was just a glitch. Then comes the compliance audit, which inevitably surfaces at least three gaps the vendor promised to fix. Finally, someone points to a competitor's press release and suddenly the board approves triple the previous year's budget. This is how it works everywhere. The driving force is not one single threat. It is the overlap between regulation, attacker capability, and supply chain exposure. The SEC's 2023 cybersecurity disclosure rule forced public companies to admit they had material incidents or face fines. That alone pushed board-level attention upward. Around the same time, ransomware groups shifted from spraying and praying to targeted supply chain attacks, meaning your security posture is now only as good as your weakest vendor's patch cycle. Regulators responded with framework mandates. The market responded with tooling. Everyone responded by hiring more people, which is the most expensive line item in every stack I have ever audited. Here is the practical breakdown of what that investment actually buys you and where it gets wasted.
What The Investment Actually Funds
Most budgets fall into four buckets. The first is detection and response tools, which means EDR, XDR, SIEM, and a SOC either staffed internally or contracted as MDaaS. The second is identity and access governance, because zero trust without continuous verification is just a marketing slide. The third is encryption and data loss prevention, which matters mostly when you need to pass a customer audit for SOC 2 Type II or ISO 27001. The fourth is the least glamorous: training and incident response retainers. That last bucket is the one executives always want to cut first, then panic about when the breach happens. I recently worked with a mid-market manufacturer that had spent nearly two million dollars annually on cybersecurity tools. They had fifteen different dashboards, eight point solutions, and a SIEM that ingested forty terabytes per day but produced fewer than twenty meaningful alerts weekly. The problem was not the spending. It was the alert fatigue and the absence of a unified workflow between the tools. What actually moved the needle was not buying another product. It was consolidating to three platforms, automating the triage playbooks, and paying for a dedicated security operations analyst instead of splitting that role across IT support. The annual cost dropped by thirty percent and mean time to contain went from six hours to under forty minutes.
The Hidden Layer Nobody Talks About
There is a category of spend that rarely appears in board presentations but dominates real operational risk. It is third-party risk management and continuous vendor monitoring. A lot of organizations treat vendor security as a checkbox exercise, sending a sig fig and filing it away. That approach fails because most breaches enter through vendors who were deemed low risk six months ago and then suffered their own compromise. The workaround is to require API-based security attestations from vendors, not PDF questionnaires. You want to pull real-time data from their Attivo or Prescout dashboards, not read about their controls in a static document. I encountered a specific case where our client had a vendor that passed every quarterly assessment but was using an outdated version of a logging agent with a known CVE. The CVE had a published exploit three weeks before the next assessment window. If we had only reviewed the annual report, we would have missed it entirely. The fix was switching to automated continuous monitoring with a thirty-day remediation SLA for critical findings. That single change prevented an incident that would have taken us approximately two weeks to detect and at least four weeks to fully clean up.
Get the Full Details
Counter-Intuitive Points Beginners Miss
People assume more security tools equal better protection. They do not. The correlation between tool count and breach likelihood is actually positive, not negative. Every additional tool introduces configuration complexity, log volume, and attack surface. A properly tuned environment with five integrated platforms beats an unmanaged sprawl of fifteen tools nine times out of ten. The reason is that detection quality depends on signal-to-noise ratio, not raw data volume. Another misconception is that compliance equals security. SOC 2, HIPAA, PCI DSS, NIST 800-171, GDPR, CMMC, ISO 27001, FedRAMP. Each framework has a different scope and different controls. Running a gap analysis across them simultaneously will show you that roughly forty percent of the controls overlap, but the remaining sixty percent are non-overlapping. Most organizations pick one primary framework and map the rest on top. This is practical. It is also why some smaller companies skip compliance entirely until a customer forces their hand. Compliance buys you insurance, not invincibility. I have seen SOC 2 certified companies get phished through a vendor portal because the certification process never tested their external attack surface.
How To Allocate Budget Without Getting Burned
Start by mapping your asset criticality. Not all data deserves the same level of protection. Classify your data into tiers, then allocate detection coverage proportionally. A database holding customer PII should have real-time behavioral monitoring and encryption at rest. An internal wiki page does not. This is where data discovery tools earn their keep, because you cannot protect what you cannot find. I use automated scanning combined with a lightweight classification workflow. It takes about a day to set up and then runs weekly without human intervention. For detection tools, prioritize coverage of your identity infrastructure before endpoint detection. The majority of enterprise breaches start with credential compromise, not a malicious download. Privileged access management, conditional access policies, and certificate transparency monitoring should sit ahead of EDR in your priority list if your identity environment is large and hybrid. EDR still matters, but it is the second line, not the first. Incident response retainers are not optional. They cost between fifteen thousand and fifty thousand dollars annually for reputable firms, depending on geography and scope. During a real breach, the difference between having a retainer and negotiating one from scratch is measured in days of downtime. I have watched two separate clients spend forty-eight hours just drafting statements of work while their attackers were already moving laterally. That is not speculation. That is the timeline.
Where Budgets Fail
The biggest failure mode is purchasing decisions driven by fear rather than risk assessment. When a major breach hits the news cycle, every CISO in the sector gets an emergency budget meeting. That is when you see inflated pricing for tools that solve a different problem than the one you actually have. Vendor sales cycles intentionally compress around these events. Wait two weeks after the next headline before committing to a new platform. Most of the panic budget evaporates once the news cycle moves on, and you can evaluate your actual gaps without the emotional pressure. Another failure mode is outsourcing detection without owning the response. MDaaS is legitimate and useful, especially for smaller teams. But if your managed provider triages alerts without context about your business workflows, they will either over-alert and exhaust your team or under-alert and miss nuanced threats. I recommend keeping triage outsourced but response and investigation in-house, or at minimum co-located. The handoff point matters more than the tool.
A Realistic Timeline For Implementation
If you are starting from scratch, expect a twelve to eighteen month rollout for a mature program. Months one through three go to asset discovery and data classification. Months four through six cover identity hardening and access governance. Months seven through nine focus on detection tool deployment and tuning. Months ten through twelve handle integration and automation. Months thirteen through eighteen are dedicated to red team exercises, table-top drills, and continuous improvement. This timeline assumes you have dedicated internal staff. If you are relying solely on vendors to fill the gaps, double it. The organizations that move faster do so by skipping phases they consider non-critical. They tend to regret that later. There is no shortcut around asset discovery. You cannot secure what you do not know exists. I have seen teams try to launch EDR before inventorying their endpoints. The result is typically a fragmented deployment where shadow IT devices remain unmonitored and become the initial access vector.
The Bottom Line On Spending
Budget growth in cybersecurity is structurally inevitable. Attack surface expands with cloud adoption, remote work, and third-party dependencies. Regulation multiplies compliance overhead. Tool ecosystems fragment further each year. The goal is not to control the cost curve. It is to direct spending toward the controls that actually reduce measurable risk. Track metrics that matter: mean time to detect, mean time to contain, percentage of assets covered by detection, and percentage of critical vulnerabilities remediated within SLA. Those numbers tell you whether the budget is working. Everything else is theater. If you want a concrete starting point, audit your current tool inventory against your top five threat scenarios. Map each tool to at least one scenario. Any tool without a clear mapping is a candidate for consolidation or removal. This exercise alone typically reveals twenty to thirty percent redundant spend in environments I have reviewed. The savings fund the gaps.