Why Your Security Posture Is Already Behind
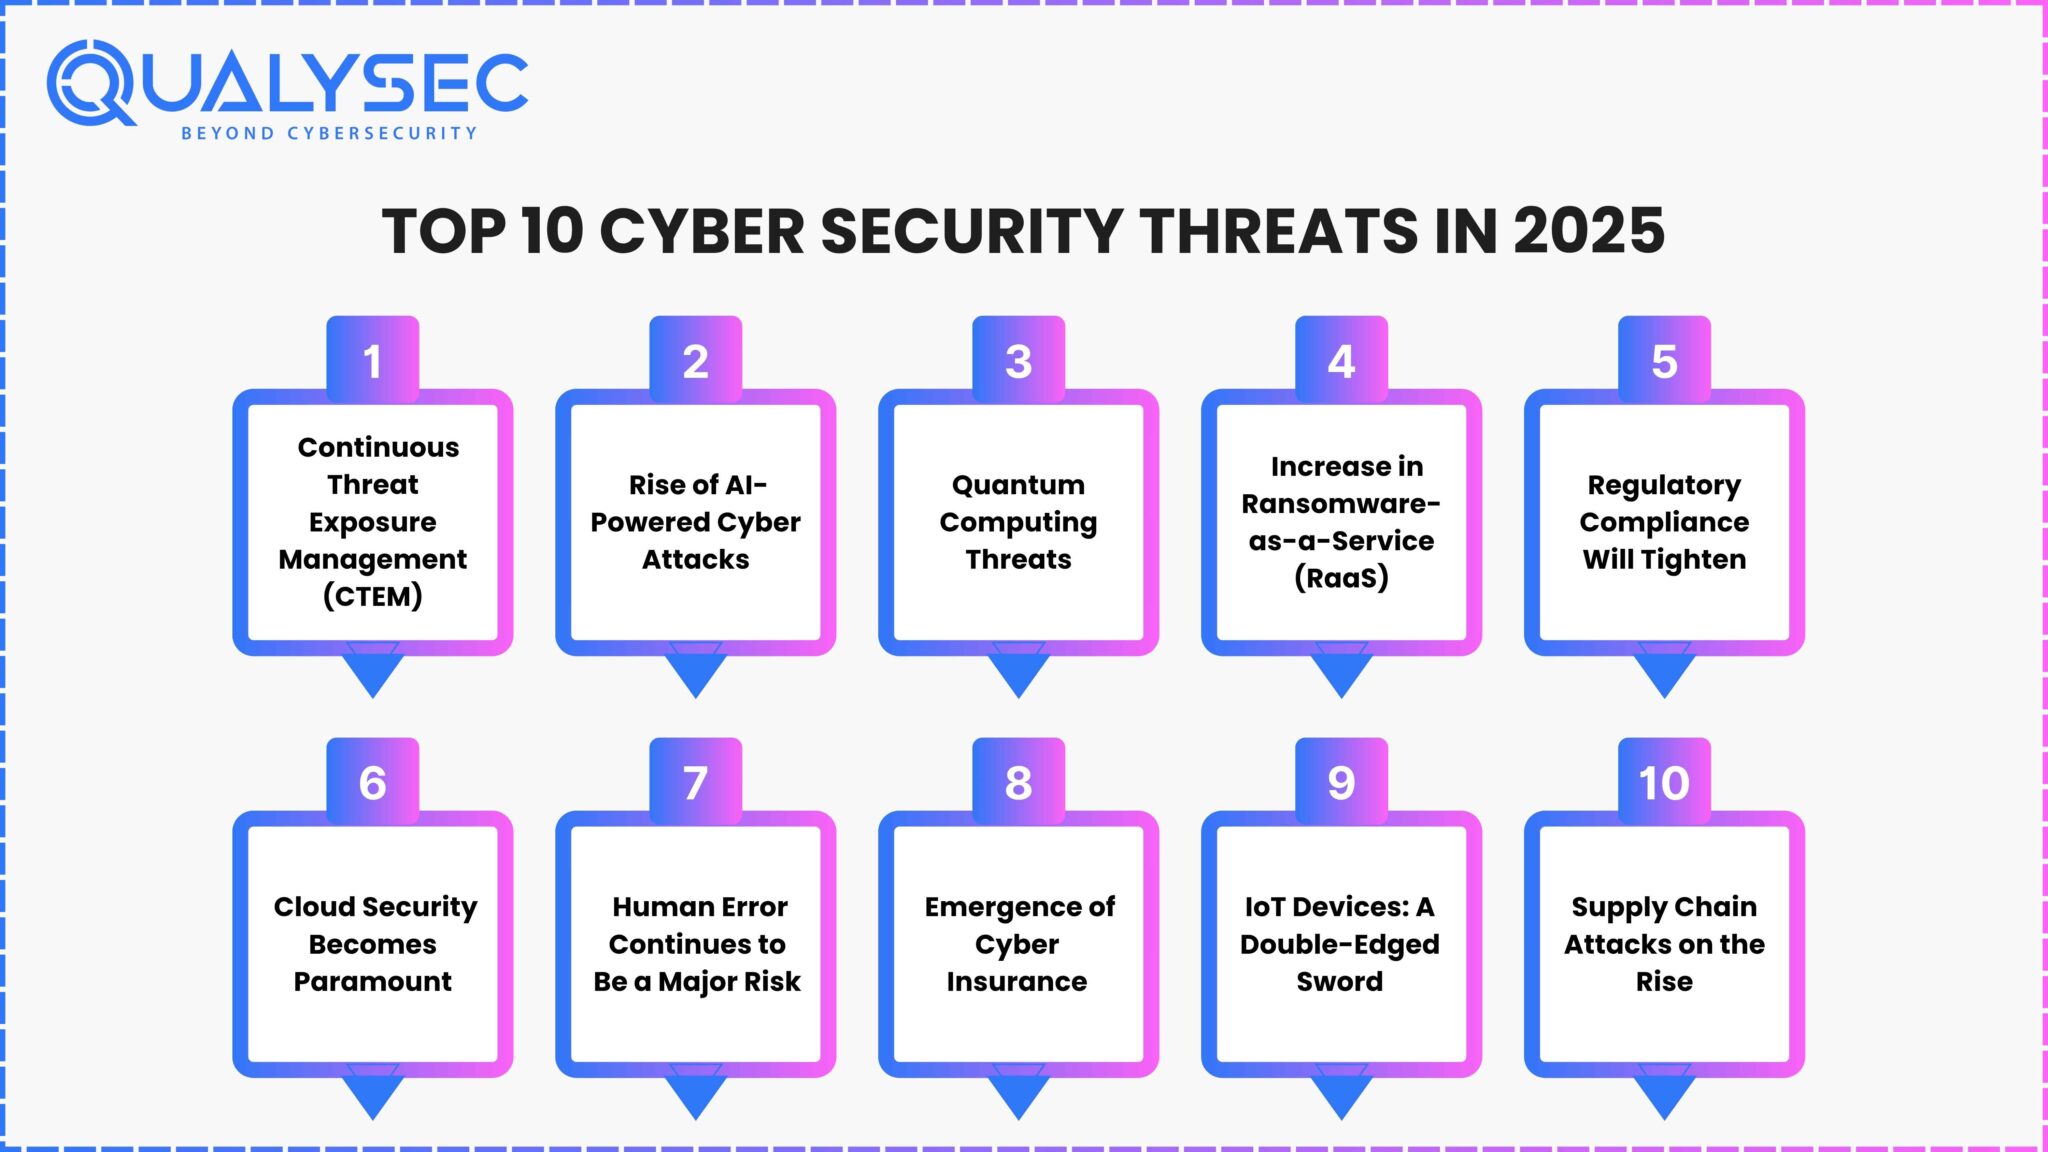
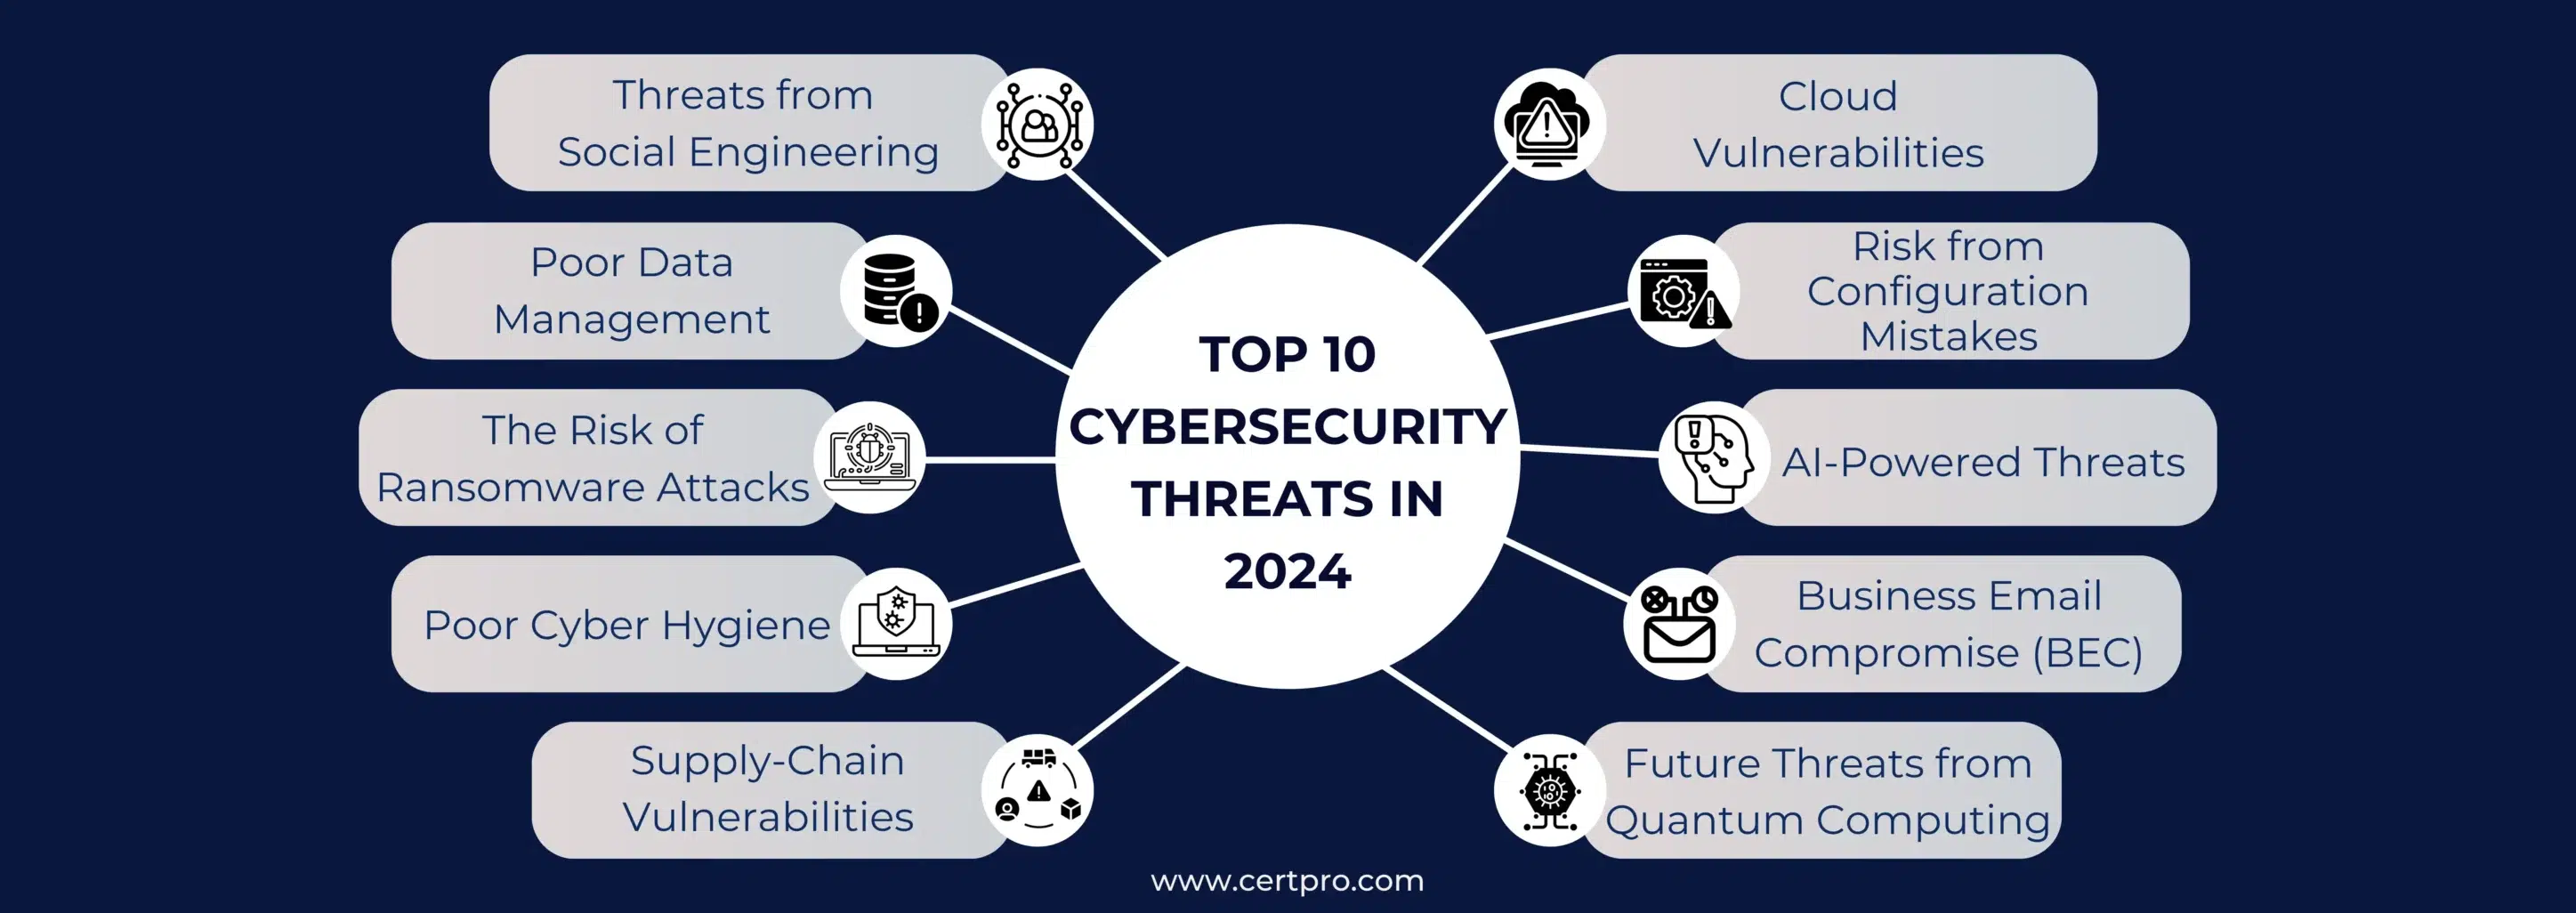
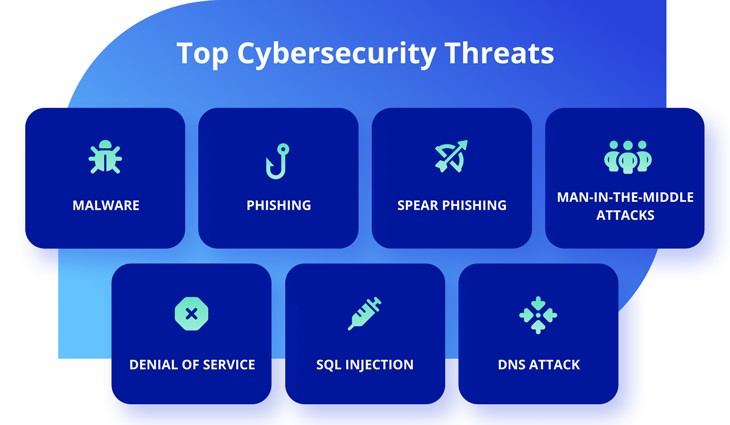
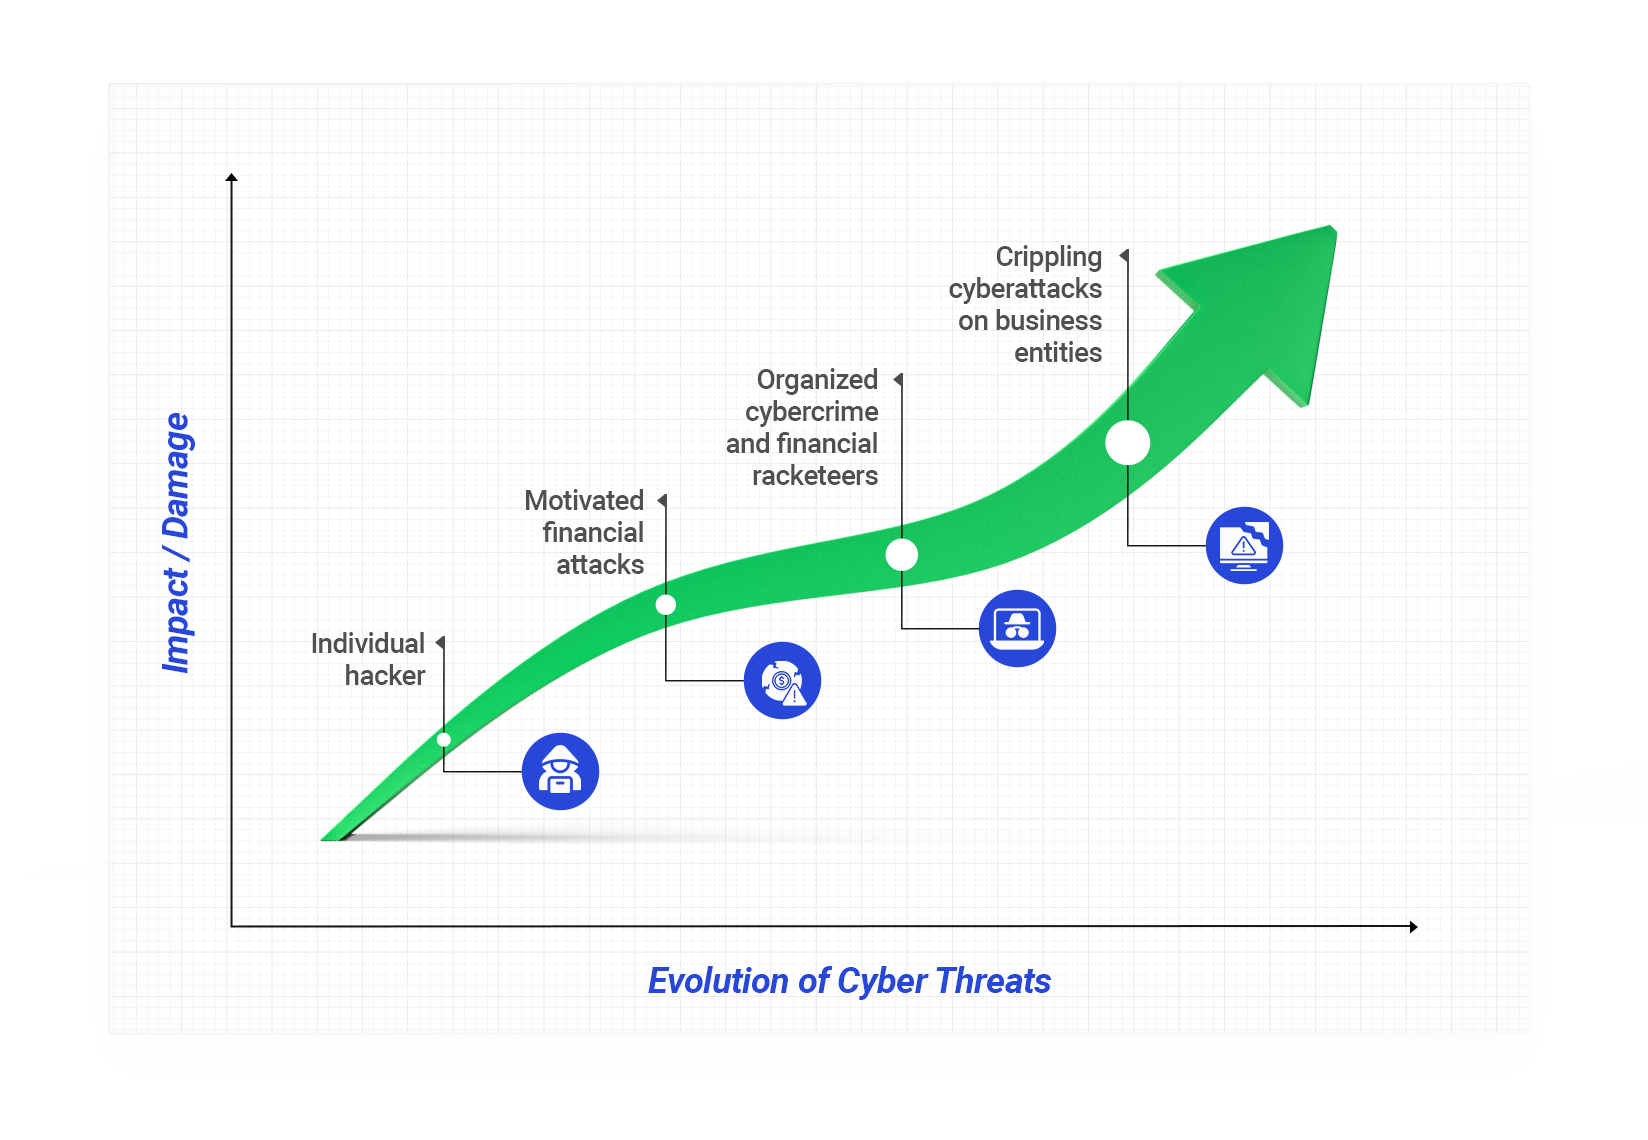
The last quarter alone saw ransomware payouts exceed 2.4 billion dollars globally, and that number doesn't include the companies that simply shut down rather than negotiate. I've been watching this space since the early 2010s when a good firewall and some antivirus software was basically a security strategy. That hasn't been true for well over a decade, but you'd be surprised how many organizations still operate under that assumption. Cybersecurity threats have evolved from opportunistic hacking into structured, well-funded operations that mirror corporate hierarchies. Ransomware-as-a-service (RaaS) platforms like LockBit and BlackCat operate with affiliate networks, customer support ticketing systems, and profit-sharing models. The barrier to entry has dropped so dramatically that threat actors can lease sophisticated tooling for as little as a few hundred dollars per month. This democratization of attack capability is the single biggest factor driving the threat landscape forward. The real concern isn't just the volume of attacks. It's the shift toward supply chain compromise and credential-based entry points. Attackers stopped hammering on the front door years ago. They went around through third-party vendors, software dependencies, and stolen credentials sold on underground forums. The MOVEit Transfer vulnerability in 2023 affected over 2,700 organizations globally because one file transfer application had a SQL injection flaw. Your security team might be locking down your perimeter while your vendor's patch management situation looks like a horror story.
I dealt with this directly during a breach investigation last year. A mid-sized logistics company reported unusual network activity that their SIEM flagged as anomalous. The initial assessment pointed toward a compromised employee workstation. Standard procedure would have been to isolate the machine and begin forensic analysis from there. Instead, I spent three days tracing lateral movement through their VPN gateway, only to discover the actual entry point was a forgotten admin account on a legacy inventory management system that hadn't been updated since 2019. The attacker had been moving laterally for eleven days before detection. Their EDR solution had generated 847 alerts during that window. None of the on-call analysts had connected the dots because the alerts were spread across four different security tools that didn't share context. This is the operational reality most people don't see. The tools exist. The visibility exists. The problem is alert fatigue, siloed systems, and understaffed security operations centers making triage decisions at 3 AM. A 2024 industry report found that the average time to identify a breach is 204 days. That's not because attackers are invisible. It's because the volume of noise makes it nearly impossible to distinguish signal from garbage without significant investment in automation and skilled personnel.
How To Actually Assess Your Exposure
Most organizations approach threat assessment the wrong way. They start with compliance checklists or run vulnerability scanners and call it a day. A vulnerability scan tells you what holes exist. It doesn't tell you which holes someone is actively exploiting or which ones actually matter for your specific environment. Here's what actually works, and I'm going to be blunt about what doesn't. Start with an asset inventory that you actually trust. I can't stress this enough. During that same investigation I mentioned, the organization's CMDB listed 340 devices. The actual count on the network was closer to 600. The missing 260 included contractor laptops, IoT devices on the OT network, and a decommissioned server that someone forgot to unplug. Every unknown asset is a potential entry point that your security controls don't cover. Conduct a proper attack surface assessment that distinguishes between external and internal exposure. External attack surface management (EASM) tools like AttackSurfaceAnalyzer or commercial platforms can map your internet-facing assets. But the internal attack surface is where most breaches actually cause damage. An attacker who gets one workstation often has a path to everything else if you're running a flat network with broad lateral movement capabilities. Segment your network. Really segment it, not just VLANs that everyone has access to through default routes.
Get the Full Details
Implement continuous monitoring with a focus on detection engineering rather than just alert volume. Most SOCs are drowning in alerts and starving for insights. I've seen teams configure rules that generate thousands of events daily with maybe two or three that warrant actual investigation. The fix isn't more tools. It's writing detection logic that reflects how real attackers operate. The MITRE ATT&CK framework is useful here, but most organizations implement it as a reference document rather than a practical detection guide. Map your critical assets to specific ATT&CK techniques, then build detections around the techniques that matter for your environment. Run threat hunting exercises on a regular cadence. Not annual tabletop exercises that feel like box-checking. Actual proactive hunting where your team assumes a breach has occurred and tries to find evidence of it. I've found that these exercises reveal gaps in detection coverage that no tool configuration process ever surfaces. During one exercise, our team discovered that an attacker using standard Windows command-line tools could operate undetected for approximately 72 hours given our logging configuration. That's not an anomaly. That's typical for organizations without endpoint telemetry that captures command-line arguments and parent-child process relationships.
Where Current Approaches Fall Short
I need to be honest about the limitations of what most organizations are doing. Security awareness training has marginal impact on preventing credential phishing. Studies consistently show that even after training, phishing click-through rates remain between 15 and 30 percent for simulated campaigns. Multi-factor authentication reduces this dramatically, but MFA fatigue attacks and token interception are becoming common workarounds that most organizations don't monitor for. Zero Trust architecture is frequently misimplemented as a marketing term rather than a security model. Real Zero Trust requires continuous verification, least-privilege access, and microsegmentation. What most companies implement is just better identity management with some SSO thrown in. That's useful, but calling it Zero Trust creates a false sense of security. The gap between advertised Zero Trust and actual implementation is substantial. Endpoint Detection and Response (EDR) tools are necessary but insufficient on their own. Modern EDR solutions can detect many attack techniques, but they miss fileless attacks, living-off-the-land binaries, and attacks that operate entirely within legitimate administrative tools. I've deployed EDR across multiple environments and the blind spots are consistent: attacks using PowerShell, WMI, and scheduled tasks that match normal administrative behavior. Effective detection requires combining EDR with network telemetry, DNS logging, and sometimes custom detection scripts.
The talent shortage remains a structural problem that no amount of tooling will solve. Security operations require people who understand both the technology and the adversary mindset. These skills don't appear through certification programs or bootcamps. They develop through years of hands-on incident response and threat intelligence work. Organizations that rely solely on tier-one SOC analysts rotating through shifts will always be behind. I've recommended external managed detection and response (MDR) services for this reason, but even MDR providers vary widely in quality. Some are just monitoring dashboards with offshore analysts following playbooks written by people who've never seen your environment.

Practical Steps You Can Take This Week
Audit your privileged access. How many accounts have domain admin or equivalent privileges? Most organizations I've assessed have between 50 and 200 privileged accounts, and the vast majority of those are static service accounts that haven't been rotated in years. Implement privileged access management with just-in-time access where possible. Require break-glass procedures for emergency administrative access with mandatory logging and review. Enable logging that you actually use. Default Windows logging captures event IDs that most analysts ignore. Focus on Event ID 4624 (logons), 4625 (failed logons), 4688 (process creation with command line), and authentication events from your identity provider. If your logging infrastructure can't handle the volume, prioritize critical servers and domain controllers first. Better logging on five key systems beats no logging on fifty. Test your incident response plan by actually triggering it. I've seen incident response plans that are four hundred pages long and haven't been updated in three years. The plan matters less than the muscle memory your team builds through practice. Run a focused tabletop exercise once a month covering a single scenario: ransomware on the file server, compromised credentials in the cloud environment, supply chain attack through a software update. Keep it narrow. Keep it regular. Document what broke and fix it.
Review your backup recovery process quarterly. Backups that can't be restored are worse than no backups because they create false confidence. I've encountered environments where the backup system reported successful copies for months while the restore tests consistently failed due to corrupted media or misconfigured retention policies. Validate restores, not just backup success messages. Test restoration to an isolated environment that proves you can recover without the compromised infrastructure. The threat landscape isn't getting easier to manage. It's getting more organized, better funded, and more patient. The organizations that stay secure aren't necessarily the ones spending the most money. They're the ones that understand their actual risk, maintain honest visibility into their environment, and practice responding to incidents until the process stops feeling chaotic when it happens for real.