Understanding DDoS Attacks: A Decade in Review
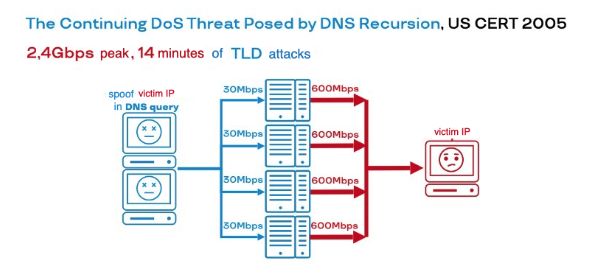
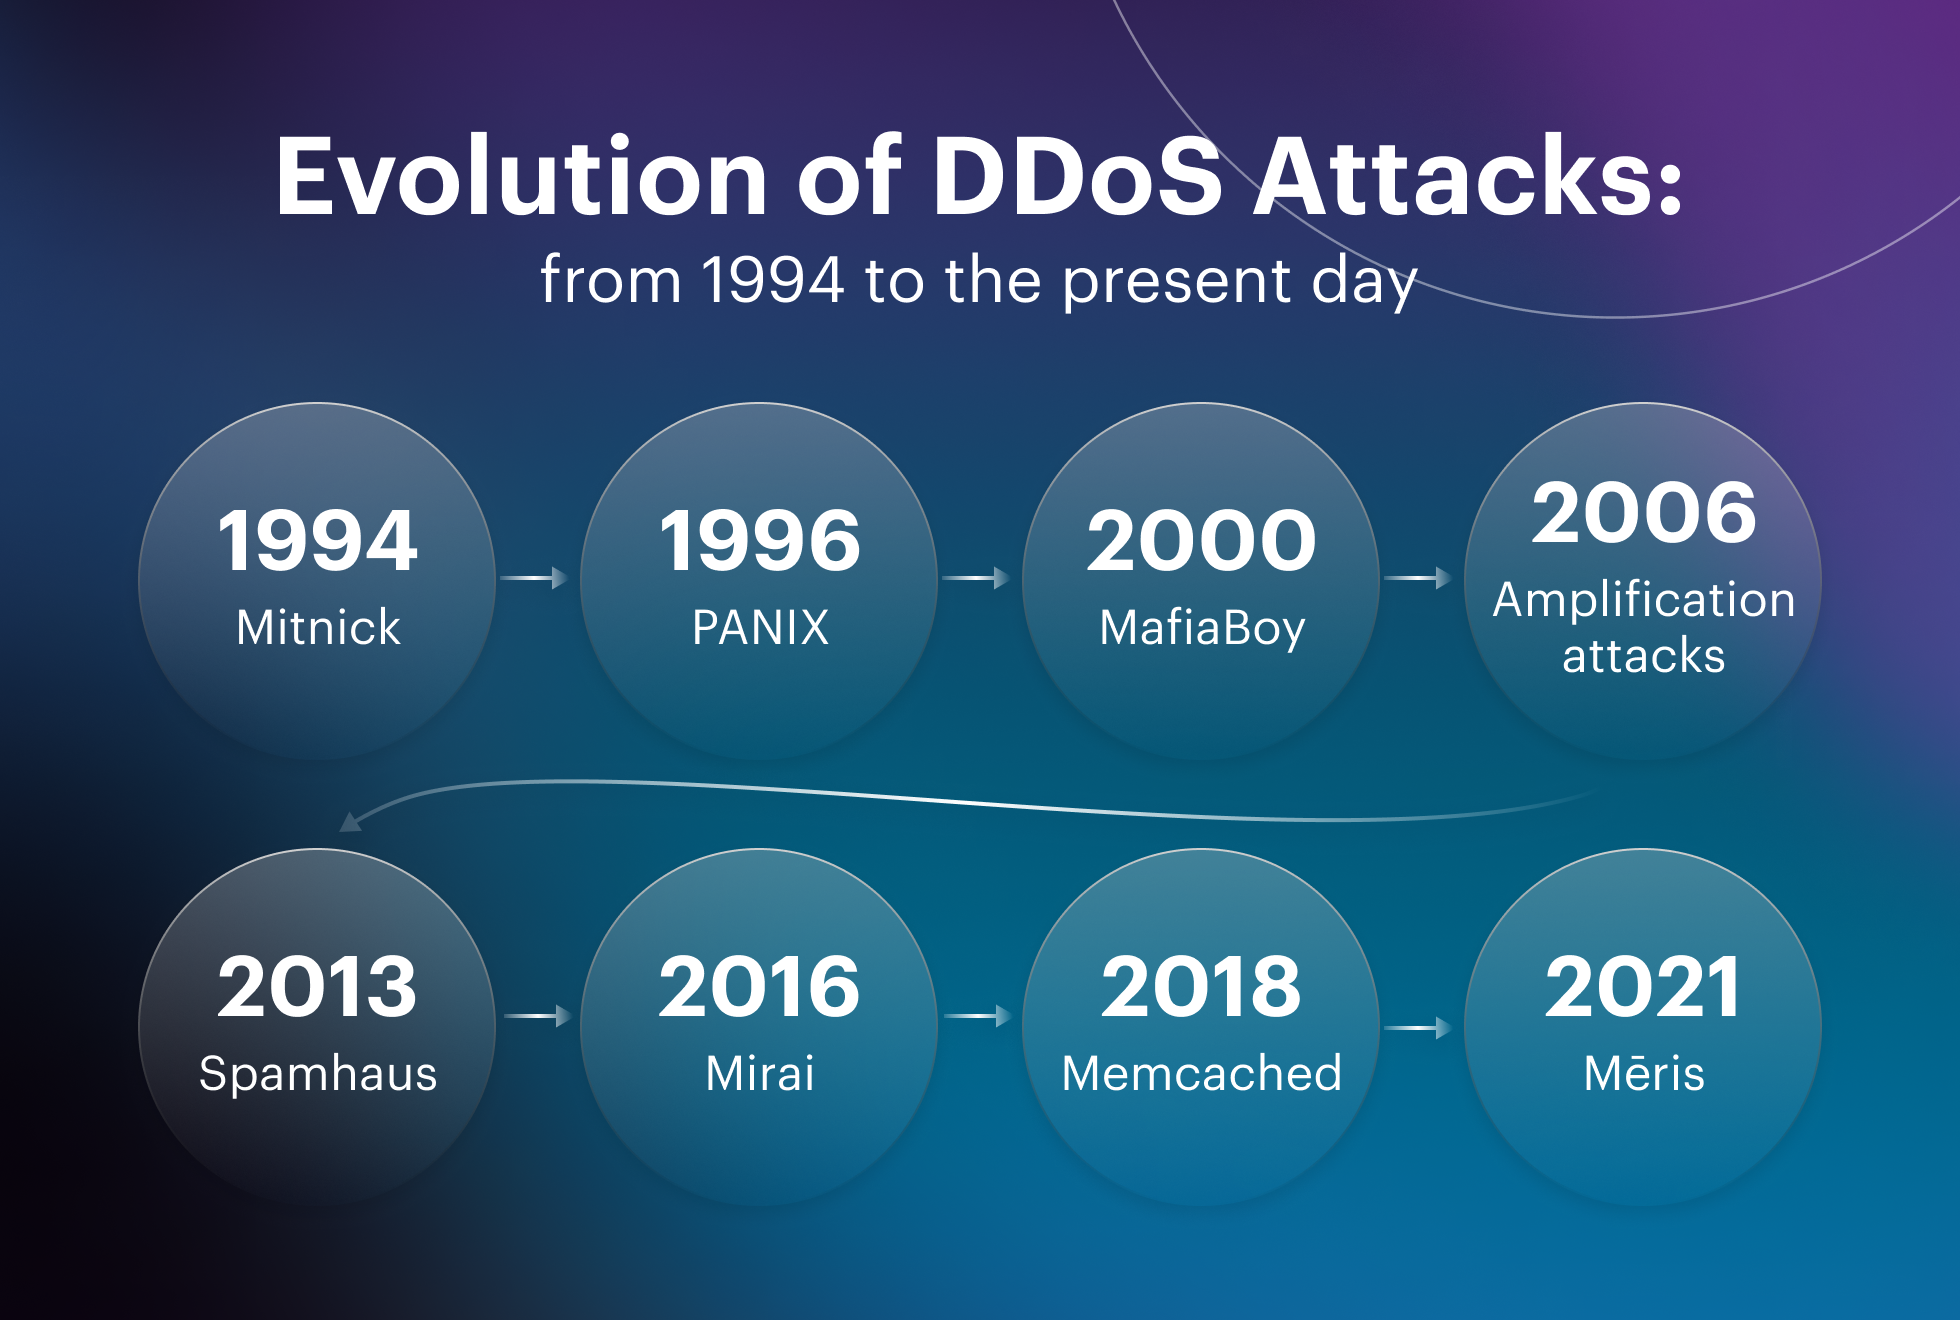
The landscape of distributed denial of service attacks has shifted dramatically since 2015. I remember watching traffic spikes that made no sense during my early days in security operations. Servers would go down without warning, and troubleshooting felt like searching for a needle in a haystack made of needles. The tools available then were crude compared to what we face today. Back in 2016, most attacks under 1 Gbps were dismissed as noise. I spent three weeks investigating what turned out to be a simple UDP flood from a compromised IoT device. The attacker had purchased bandwidth for roughly forty dollars on a Russian forum. Today, those same attacks routinely exceed 1 Tbps. The barrier to entry dropped while the ceiling disappeared simultaneously. The early years relied heavily on HTTP floods and SYN packets. Attackers understood basic TCP handshakes and exploited them systematically. Defense mechanisms from that era focused on rate limiting and IP blacklisting. Neither strategy survived when attackers discovered reflection amplification techniques. Once DNS and NTP servers started being weaponized, the math changed entirely. A single Gbps upstream connection could generate ten Gbps of outbound traffic using amplification factors that made defensive capacity planning nearly impossible.
I encountered a particularly nasty edge case around 2018. An attack mimicked legitimate traffic patterns so closely that our WAF rules kept blocking real customers instead of the attack traffic. The problem was a slow-rate application layer attack hitting specific API endpoints with human-like request intervals. It took me about six hours to realize the pattern. The workaround involved implementing behavioral analysis based on TLS fingerprinting rather than relying on request signatures or rate thresholds alone.
The Evolution Made Things Worse Before They Got Better
Mid-decade saw the rise of botnet-as-a-service models. Attackers no longer needed infrastructure or technical knowledge. They simply subscribed to a service, selected a target, and watched the chaos unfold. Payment processing moved to cryptocurrency mixers. Attribution became nearly impossible because the money trail dissolved within minutes of payment. This commercialization fundamentally changed who was launching attacks and why. The Mirai botnet changed everything in late 2016. Default credentials on routers and cameras created a zombie army that overwhelmed Dyn's DNS infrastructure. Major websites went dark not because of sophisticated exploit chains but because someone remembered the factory password on a $15 baby monitor. This period exposed how unpatched ecosystems could cascade into national-level incidents. ISPs quietly started implementing upstream filtering because the alternative was watching their customers become attack vectors without knowing it. Government response lagged behind the technology. The CISA formed in 2018, but meaningful regulation didn't materialize until years later. Laws criminalizing DDoS tools existed, but prosecuting someone in another continent selling access to attack infrastructure rarely happened. The best defense became technical rather than legal. BGP flowspec, SCADA protocols for scrubbing centers, and anycast networks distributed attack traffic before it reached target infrastructure.
Get the Full Details
What Actually Worked and What Failed Completely
Hardware-based mitigation appliances dominated the early market. Companies sold boxes that claimed to filter malicious traffic automatically. In practice, these devices often introduced latency and occasionally created single points of failure during massive attacks. The vendor lock-in was brutal. Once you bought into a platform, switching costs were enormous. Cloud-based scrubbing services proved more effective for most organizations. Traffic gets rerouted through cleaning centers that analyze packets before forwarding legitimate traffic downstream. The downside is cost. Egress fees from scrubbing centers during sustained attacks can exceed fifty thousand dollars monthly for enterprises. Small businesses simply cannot absorb that expense, which explains why they remain disproportionately vulnerable. CDN providers became accidental DDoS defenders when they realized their network architecture inherently absorbed attack traffic better than point-source servers. Cloudflare, Akamai, and similar platforms built redundancy and capacity specifically for this purpose. The ironic result is that many organizations now depend on third-party infrastructure they do not control for basic availability. Trusting providers with security-critical routing decisions creates its own set of risks that rarely get discussed openly.
Current State and Practical Recommendations
Today's attack surface includes IoT devices, cloud instances, and container workloads. Attackers exploit misconfigured Kubernetes clusters and exposed cloud storage buckets. The average residential broadband connection can still generate enough bandwidth to disrupt small services. Network segmentation remains the most effective mitigation strategy, yet many organizations skip it because configuring VLANs and firewall rules feels expensive during budget cycles. I recommend starting with basic hygiene before investing in expensive solutions. Disable unused ports, enable logging on all perimeter devices, and establish relationships with your ISP before an attack occurs. Having someone to call at 3 AM during a crisis matters more than any tool you purchase. Document your network topology, identify critical assets, and practice your incident response plan regularly. Most teams skip the practice portion entirely. Monitoring should focus on anomalies rather than absolute thresholds. Normal traffic patterns vary by business type, season, and time of day. Baseline measurements taken over ninety days provide context that sudden spike detection alone cannot. The best alerting systems combine statistical deviation with known attack signatures and geolocation data. False positives remain frustrating but better than missing an actual incident.
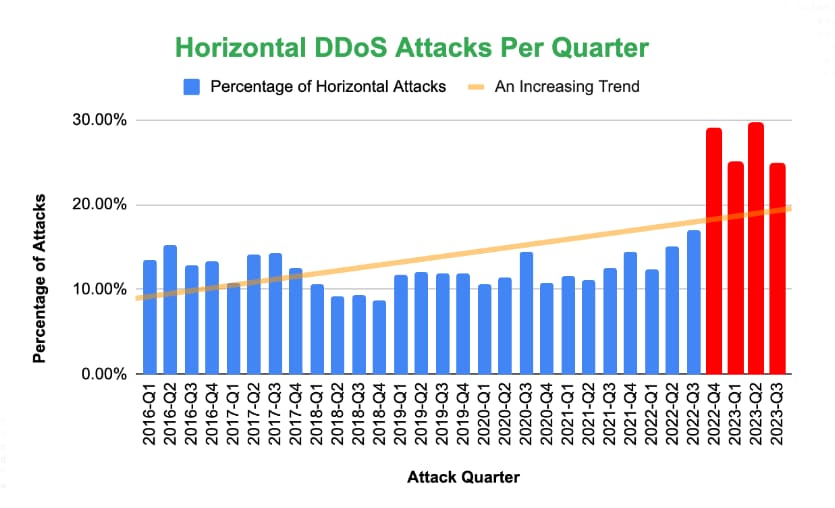
The trajectory over the past decade suggests attacks will continue growing in both volume and sophistication. Defensive capabilities have improved proportionally, but the economics favor attackers. Building attack infrastructure costs less than configuring proper defenses. This asymmetry will persist until regulatory frameworks create meaningful consequences for attack operations or until organizations treat DDoS resilience as foundational rather than optional.