HTTP Dying Out And What That Actually Means
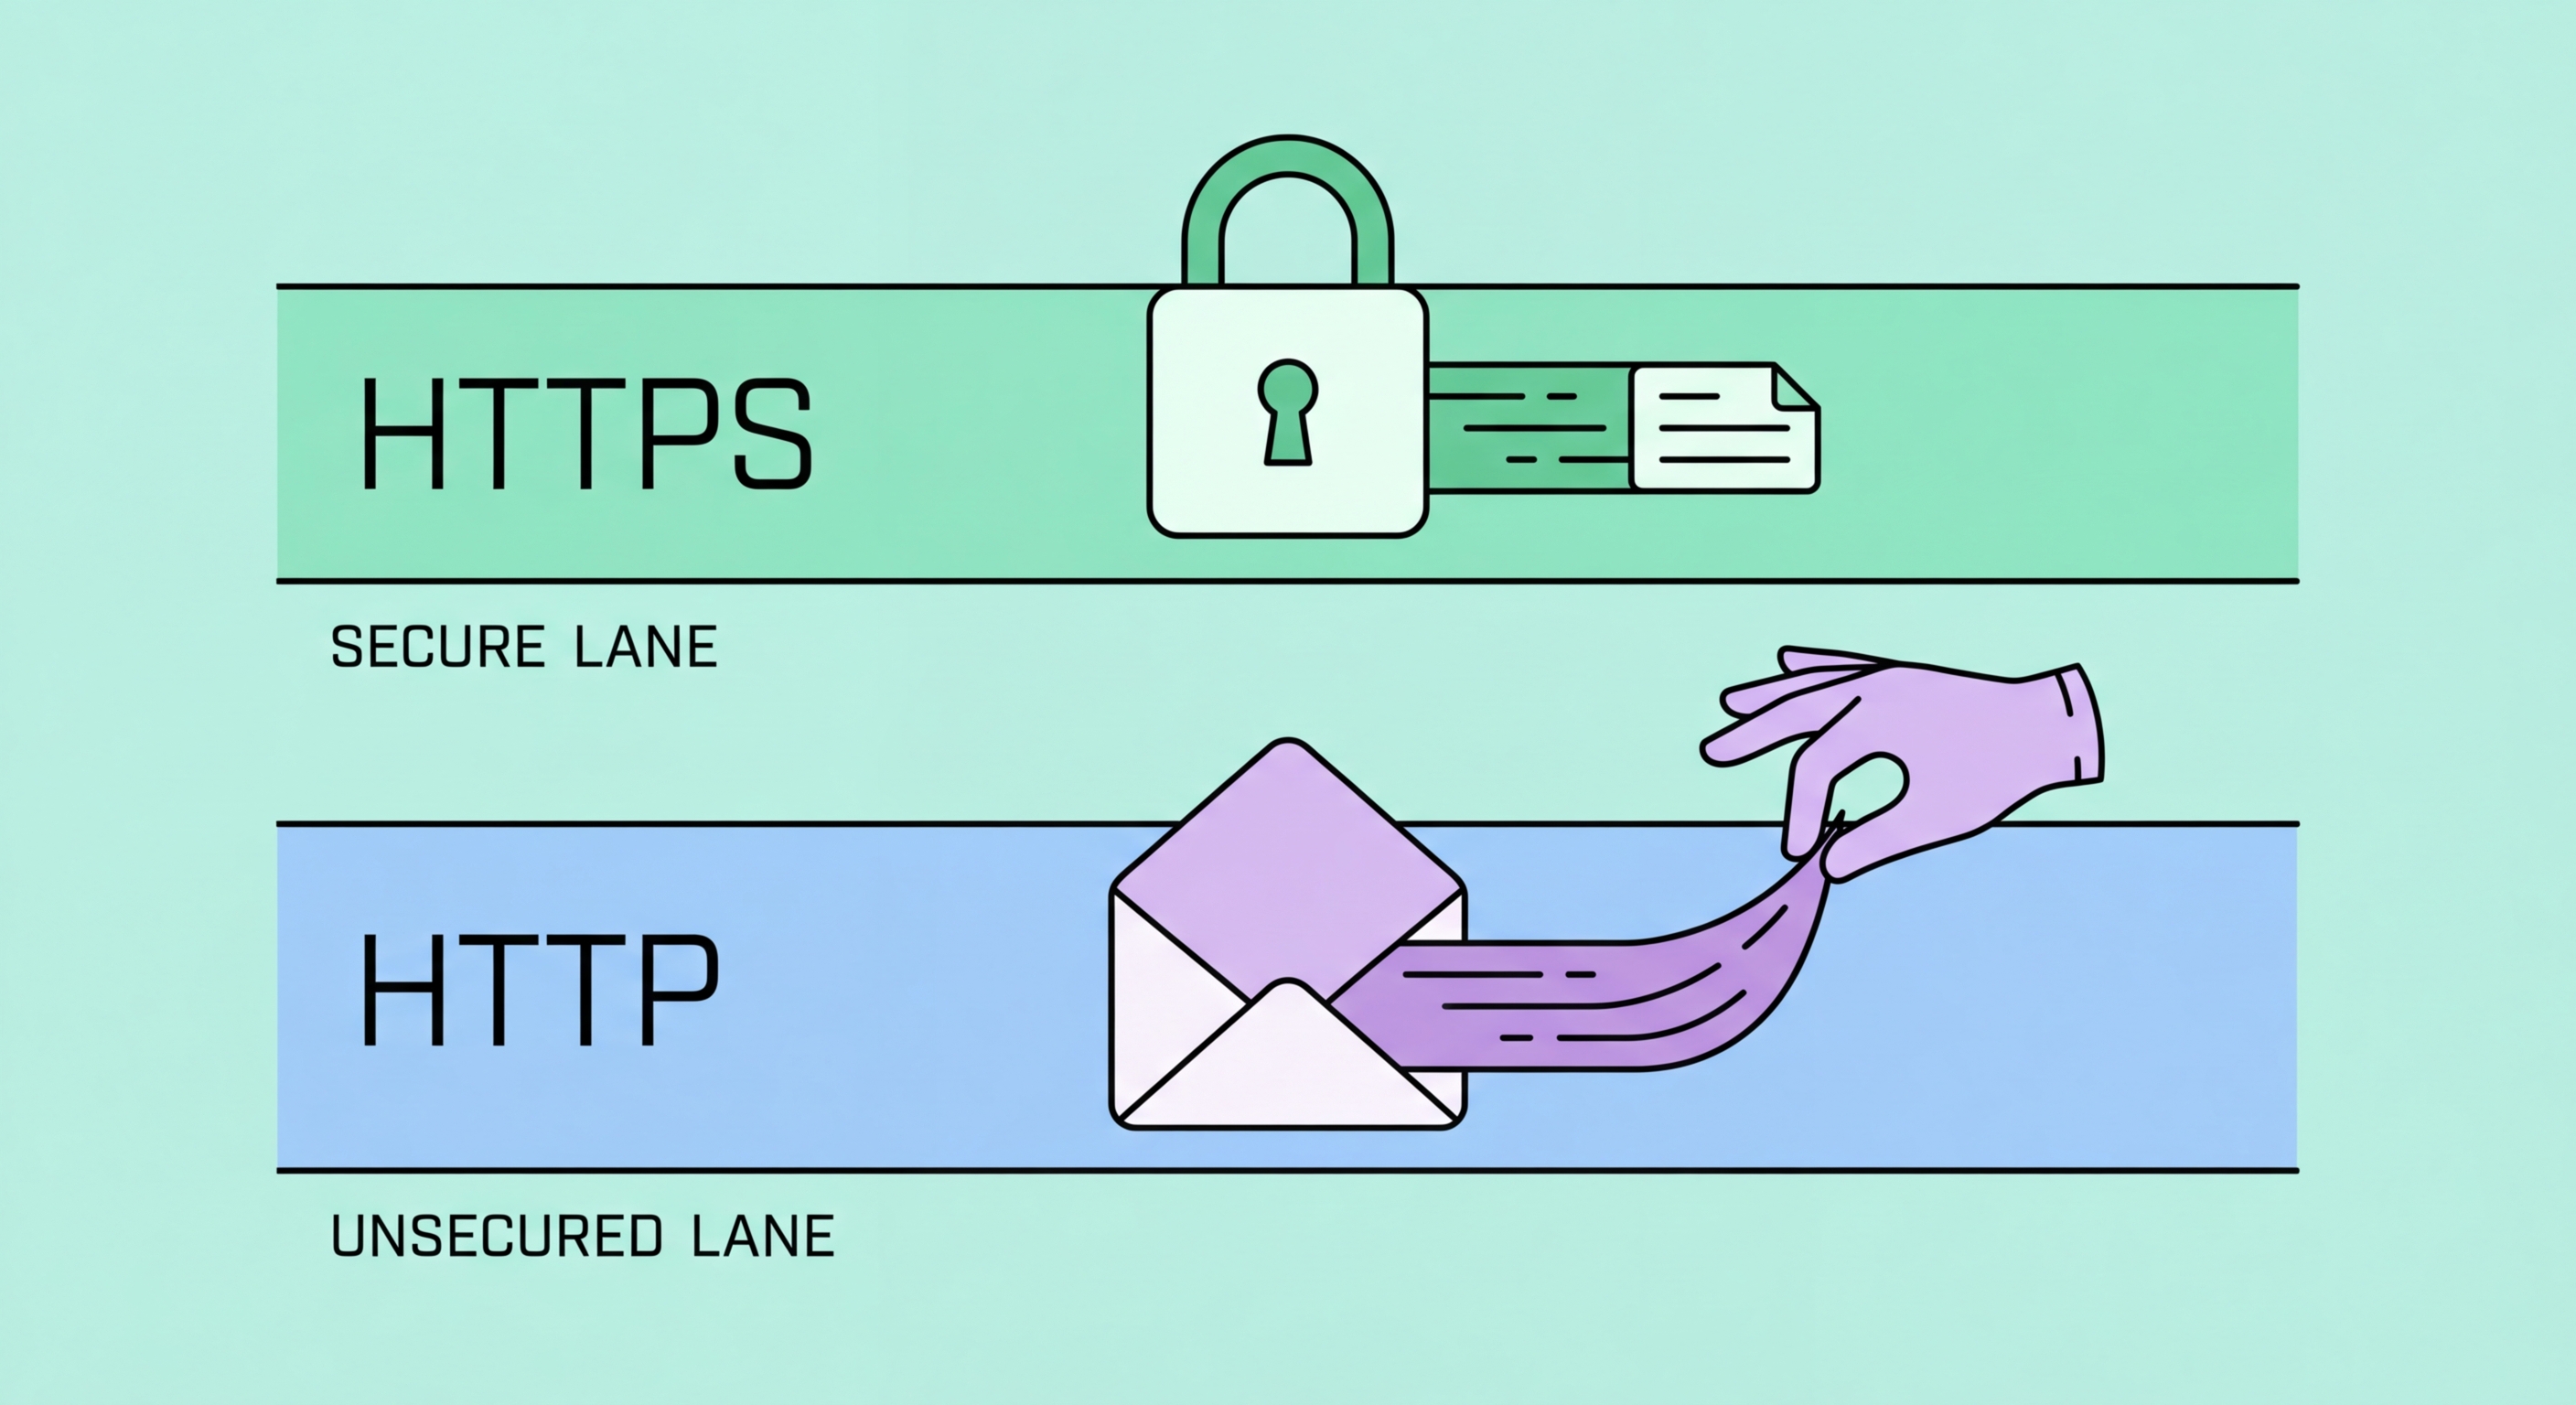
The switch from HTTP to HTTPS wasn't some sudden overnight event. It was a slow bleed over the better part of a decade, and the infrastructure changes underneath it are probably more important than most people realize. When you look at the Revolution Of HTTPS Understanding The Impact On Online Security And Communication, you have to separate the marketing from the actual technical shifts. HTTPS is not a magic security blanket. It encrypts traffic between your browser and the origin server. That is it. It does not protect you from phishing, it does not validate website authenticity beyond the certificate authority chain, and it absolutely does not mean the site owner is trustworthy. It just means a middleman cannot read the bytes passing through. Most users conflate encryption with trust, and that distinction causes real problems in production environments. The core mechanism is the TLS handshake. Client hello, server hello, certificate exchange, key agreement, encrypted channel established. In TLS 1.3, this got trimmed down significantly. The old RSA key exchange is gone from the default profile. Now it is mostly ECDHE or X25519 for forward secrecy. Forward secrecy is the part people always forget to configure correctly. If your server is set up with a static RSA cipher suite, someone who compromises the private key later can decrypt every recorded session from the past. That is not theoretical. It has happened.
I ran into this exact issue around 2019 when auditing a payment gateway. The TLS configuration looked fine on the surface. Certificates were valid, the handshake completed, everything checked out in Qualys SSL Labs with an A grade. But the cipher suite preference list had DHE_RSA matching over ECDHE. The server was falling back to a non-forward-secret suite for any client that supported it, and most enterprise clients do. After rotating the private key, I pulled six months of PCAP data from the core router and spent a solid afternoon replaying the TLS sessions against the new key. All of them decrypted cleanly. The workaround was forcing the cipher suite order and disabling DHE entirely, then running penetration tests against mobile clients that had aggressive fallback behavior. This is where the security impact gets specific. HTTPS eliminated passive eavesdropping as a trivial attack. You cannot just tap a trunk line and read credentials anymore the way you could with HTTP. But it introduced an entirely different class of problems. Certificate transparency logs are useful but most organizations treat them as a checkbox. OCSP stapling is mandatory, not optional, and the revocation checking behavior in browsers is inconsistent. Chrome moved to dropping cert pinning after the DigiNotar and Comodo incidents. Safari and Firefox have their own approaches. The ecosystem is messy.
What HTTPS Actually Changed In Practice
Content delivery networks had to adapt first. Early CDN implementations treated HTTPS as a secondary concern because SSL termination added CPU overhead. That changed when Let's Encrypt launched in 2016. Automated certificate provisioning removed the operational friction. Suddenly any operator could run a fully encrypted stack without paying for a commercial certificate or managing renewal calendars manually. The performance side is worth discussing because it is misunderstood. The TLS handshake adds latency, particularly on first visit. TCP slow start and TLS round trips compound on mobile networks with high round-trip time. But HTTP/2 multiplexing over TLS roughly compensates for the handshake cost after the initial connection is established. QUIC and the upcoming TLS 1.3 0-RTT resumption attempt to address the remaining friction, though 0-RTT introduces replay attack vectors that most implementers should ignore unless they have a specific mitigation strategy. Search engines publicly announced HTTPS as a ranking signal in 2014. That pushed adoption faster than the security argument alone would have. The result is that unencrypted HTTP is now the exception rather than the norm for consumer-facing applications. Internal tools and legacy systems are where HTTP still survives, usually because nobody remembered to configure TLS on them and now they are too ingrained to change.
Get the Full Details

Where HTTPS Falls Short
End-to-end encryption stops at the origin. If your application sits behind a reverse proxy or load balancer, the traffic between the edge and the backend is often still plaintext. This is standard practice for many infrastructure setups and it is not a flaw in HTTPS itself, but it is a gap that operators need to be explicit about. Some cloud providers offer encrypted backend connections now, but if you are running bare metal or on-prem, you are responsible for that configuration. Metadata leakage is another blind spot. HTTPS hides the payload but not the domain name being accessed. DNS queries, SNI fields in the TLS handshake, and connection timing patterns all leak information. Encrypted SNI is rolling out slowly. Most browsers still send the hostname in plaintext during the handshake. If privacy is the concern, this remains an unresolved problem at the protocol level. The certificate authority model is inherently centralized. A compromised CA can issue fraudulent certificates for any domain. The industry has tightened validation procedures, but the structural risk remains. Certificate transparency helps with detection after the fact. Prevention still relies on trusting a small number of organizations that operate under varying security standards. There is no widely adopted alternative to this model right now.
Practical Configuration Notes
If you are managing HTTPS endpoints, the things that matter most are the cipher suite selection, HSTS headers, and certificate renewal automation. A modern configuration should exclude RSA key exchange, disable TLS 1.0 and 1.1, and use only AEAD cipher suites like AES-GCM and ChaCha20-Poly1305. HSTS with a reasonable max-age and includeSubDomains prevents downgrade attacks on subsequent visits. The value should be at least one year for production services. Certificate renewal is where most failures happen. Manual renewal schedules get forgotten during staff transitions. Automation through ACME clients like certbot or acme.sh eliminates that vector, but you still need monitoring that alerts when renewal fails. I run a simple cron job that checks certificate expiry dates across all managed domains and sends a Slack alert if anything is below 30 days. The alert runs regardless of whether automation is in place. Redundancy matters. The broader impact of HTTPS adoption is measurable but not uniform. Encryption coverage is higher for major platforms than for small business sites. The digital divide in security posture still exists because operational cost, not technical knowledge, is the bottleneck. Moving from HTTP to HTTPS is straightforward for most applications. Maintaining a correct and secure configuration over time is where the actual work lies.