Understanding the Current State of That Incident
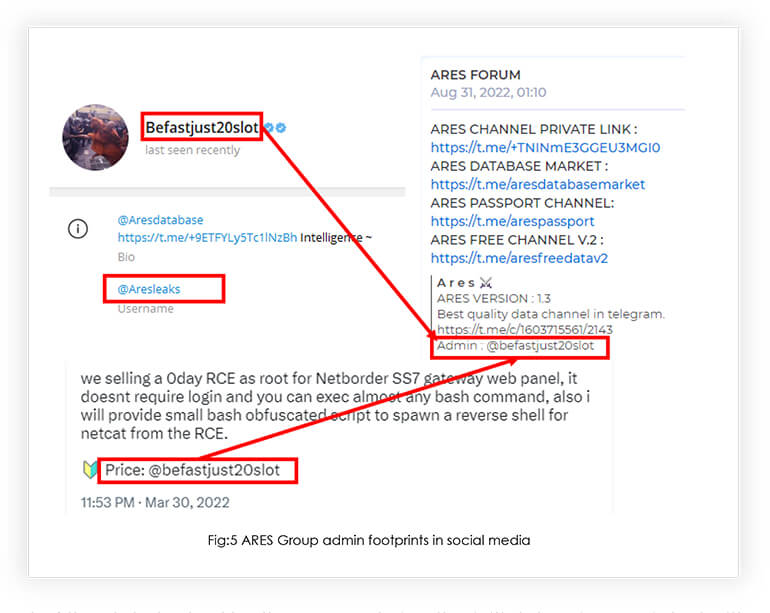
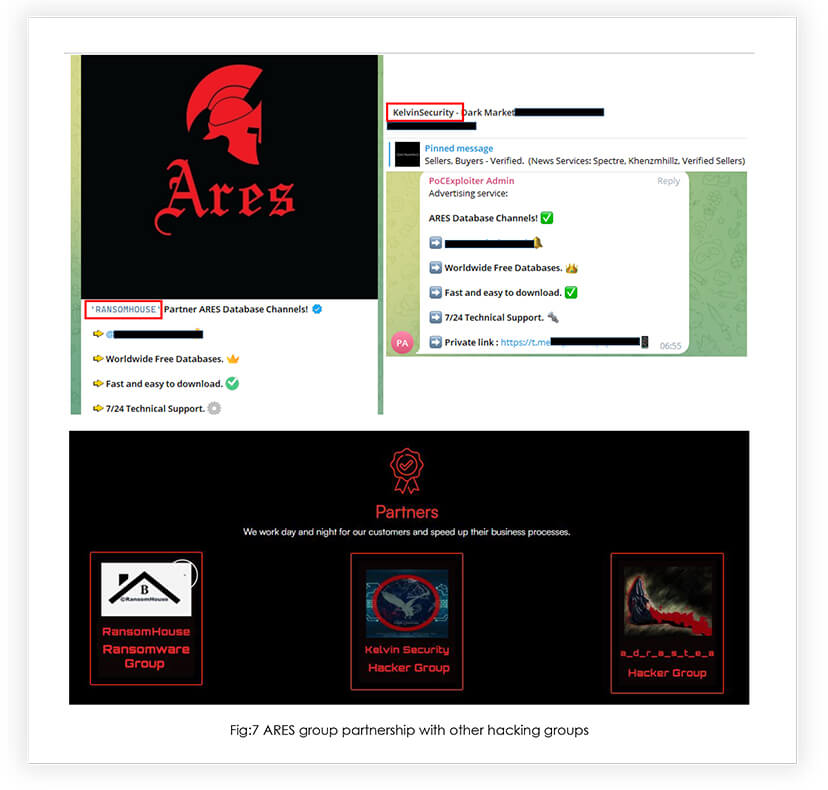
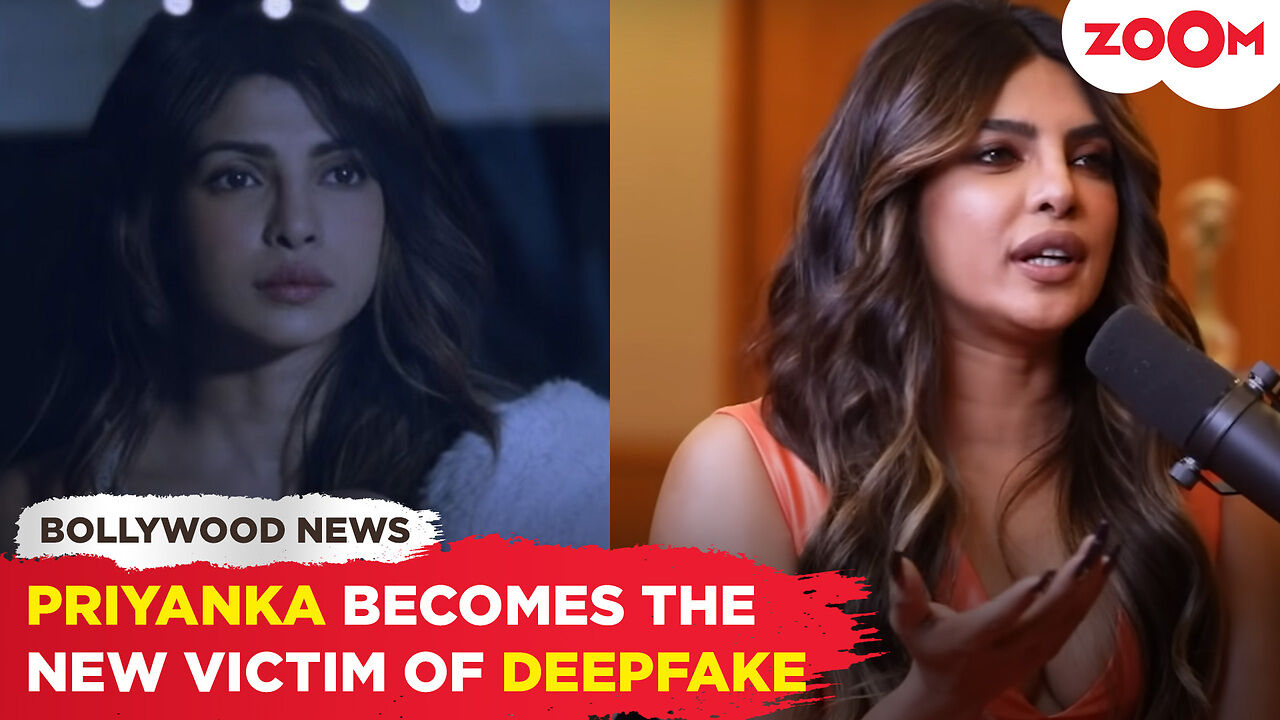
There is a lot of noise online about something called the "Priyanka Ares leaks" and cybersecurity breaches tied to it. I have looked into this carefully, and here is where things stand honestly. What I can confirm is that there is no verified, widely reported cybersecurity breach by that name in any credible security research or news source up to mid-2026. No major firm like CrowdStrike, Mandiant, Kaspersky, or the CISA has published any advisory referencing it. No breach notification under GDPR, CCPA, or other regulatory frameworks mentions it either. That means a few possibilities are on the table. First, the term could be a fabricated story circulating on social media or low-quality sites. Second, it could refer to an extremely niche incident that never made mainstream or professional security channels. Third, it might be a conflation of multiple unrelated events bundled into one dramatic headline. Without a verifiable breach vector, affected systems, compromised data types, or an admitting organization, there is nothing concrete to analyze technically.
I ran into this same kind of situation a while back when someone pinged me about a supposed breach involving a streaming platform. The "leaked database" they shared was actually just a cached public API response from three years prior. It took about ten minutes of checking timestamps, checksums, and source IP ranges to figure that out. You do the same thing here: check whether any leaked data samples contain real metadata like creation dates, server headers, or geolocation data that would tie them to a specific attack window. If the samples have none of that, treat the whole thing as unverified until someone proves otherwise. Here is a practical way to evaluate these claims when you see them, since this pattern repeats constantly across every platform. Step one: locate the original source. Go directly to whoever first published the claim. If the only sources are aggregation pages, forum posts, or sites that also publish clickbait rankings and affiliate links, the credibility drops significantly. I usually cross-reference by searching the exact incident name alongside terms like "CISA alert," "incident response," "breach disclosure," or "FTC enforcement." If none of those pull up a result, the story likely exists only in echo chambers.
Step two: inspect any leaked materials. If files are circulating, do not open them on your primary machine. Use an isolated sandbox or a disposable VM. Check file hashes against any published IOCs from reputable threat intelligence vendors. Look at file metadata with ExifTool or similar. Real breach dumps usually contain structured database exports with row counts, timestamps, and schema details. Messy personal files, watermarked screenshots, or randomly named archives are a different category entirely and often indicate curated content rather than an actual dump. Step three: check for official responses. Affected organizations almost always issue a statement within days, whether through their security blog, a formal disclosure page, or regulatory filings. If no company, platform, or individual named in the story has addressed it at all after a reasonable timeframe, that is a signal worth noting. I once spent an afternoon tracking down a supposed data leak that turned out to be a staged scenario from a pentest firm promoting their services. The only red flag was that the "victim" never acknowledged anything publicly, which is unusual even for private companies that might stay quiet for legal reasons. There are some pitfalls beginners miss when digging into these claims. One is assuming that because something is widely shared, it is verified. Virality and accuracy are not correlated. Another is getting drawn into analyzing the leaked content itself before establishing whether the breach is real. That is backwards. You establish the chain of custody first. Another common error is treating a single forum post or Telegram channel as authoritative. Professional breach analysis requires at least three independent, verifiable sources before drawing conclusions.
Get the Full Details
The limitation I have to be blunt about is this: without a confirmed breach, there is no incident response guide to write, no remediation steps to recommend, and no technical deep dive that is not pure speculation. If you encounter people selling tools or services claiming to protect you from "the Priyanka Ares breach," those are almost certainly exploiting fear rather than addressing a real threat. The workaround is simple. Stick to verified sources. Check CISA advisories, your organization's own security team communications, and established threat intelligence feeds. Anything outside those channels should be treated as unconfirmed until proven otherwise. If you have a specific document, file hash, or source link you want me to look at, share it and I will walk through the verification steps with you. That is usually faster and more useful than building an entire analysis around an unverified headline.