Let Me Explain How Blockchain Actually Works When You Stop Reading Medium Articles
Blockchain isn't magic. It's a distributed ledger with cryptographic guarantees, and it solves real problems if you know what problems it actually solves. Most people I talk to have a vague notion that blockchain is "transparent and secure" because they read a headline somewhere. That's not enough. You need to understand the mechanics before you trust it with anything. I spent three years building supply chain verification systems for a mid-sized logistics company. We deployed on Ethereum sidechains first, then migrated to a Hyperledger Fabric network. Here's what I can tell you from actual production experience, not theory.
The Power Of Blockchain Unlocking A New Era Of Transparency And Security
The fundamental mechanism is simple enough that it's almost insulting. A block contains a batch of transactions. Each block references the previous block by its cryptographic hash. Chain them together and you get something tamper-evident. If someone alters a transaction from six months ago, they'd need to recompute every single hash after that point across more than 51% of the network's computing power. In practice, for a sufficiently large network, that's computationally infeasible. That's the entire security model. Transparency works differently depending on the type of blockchain you're dealing with. Public blockchains like Ethereum make every transaction visible to anyone. Private or consortium blockchains restrict visibility through permissioned nodes. This is where most enterprise projects get it wrong. They build a private chain when they actually need a public one, or vice versa. The choice has massive implications for cost, speed, and legal compliance. I want to walk through a specific scenario because abstract explanations don't help much. Say you're building a system to track pharmaceutical shipments from manufacturer to pharmacy. Here's what that actually looks like in practice.
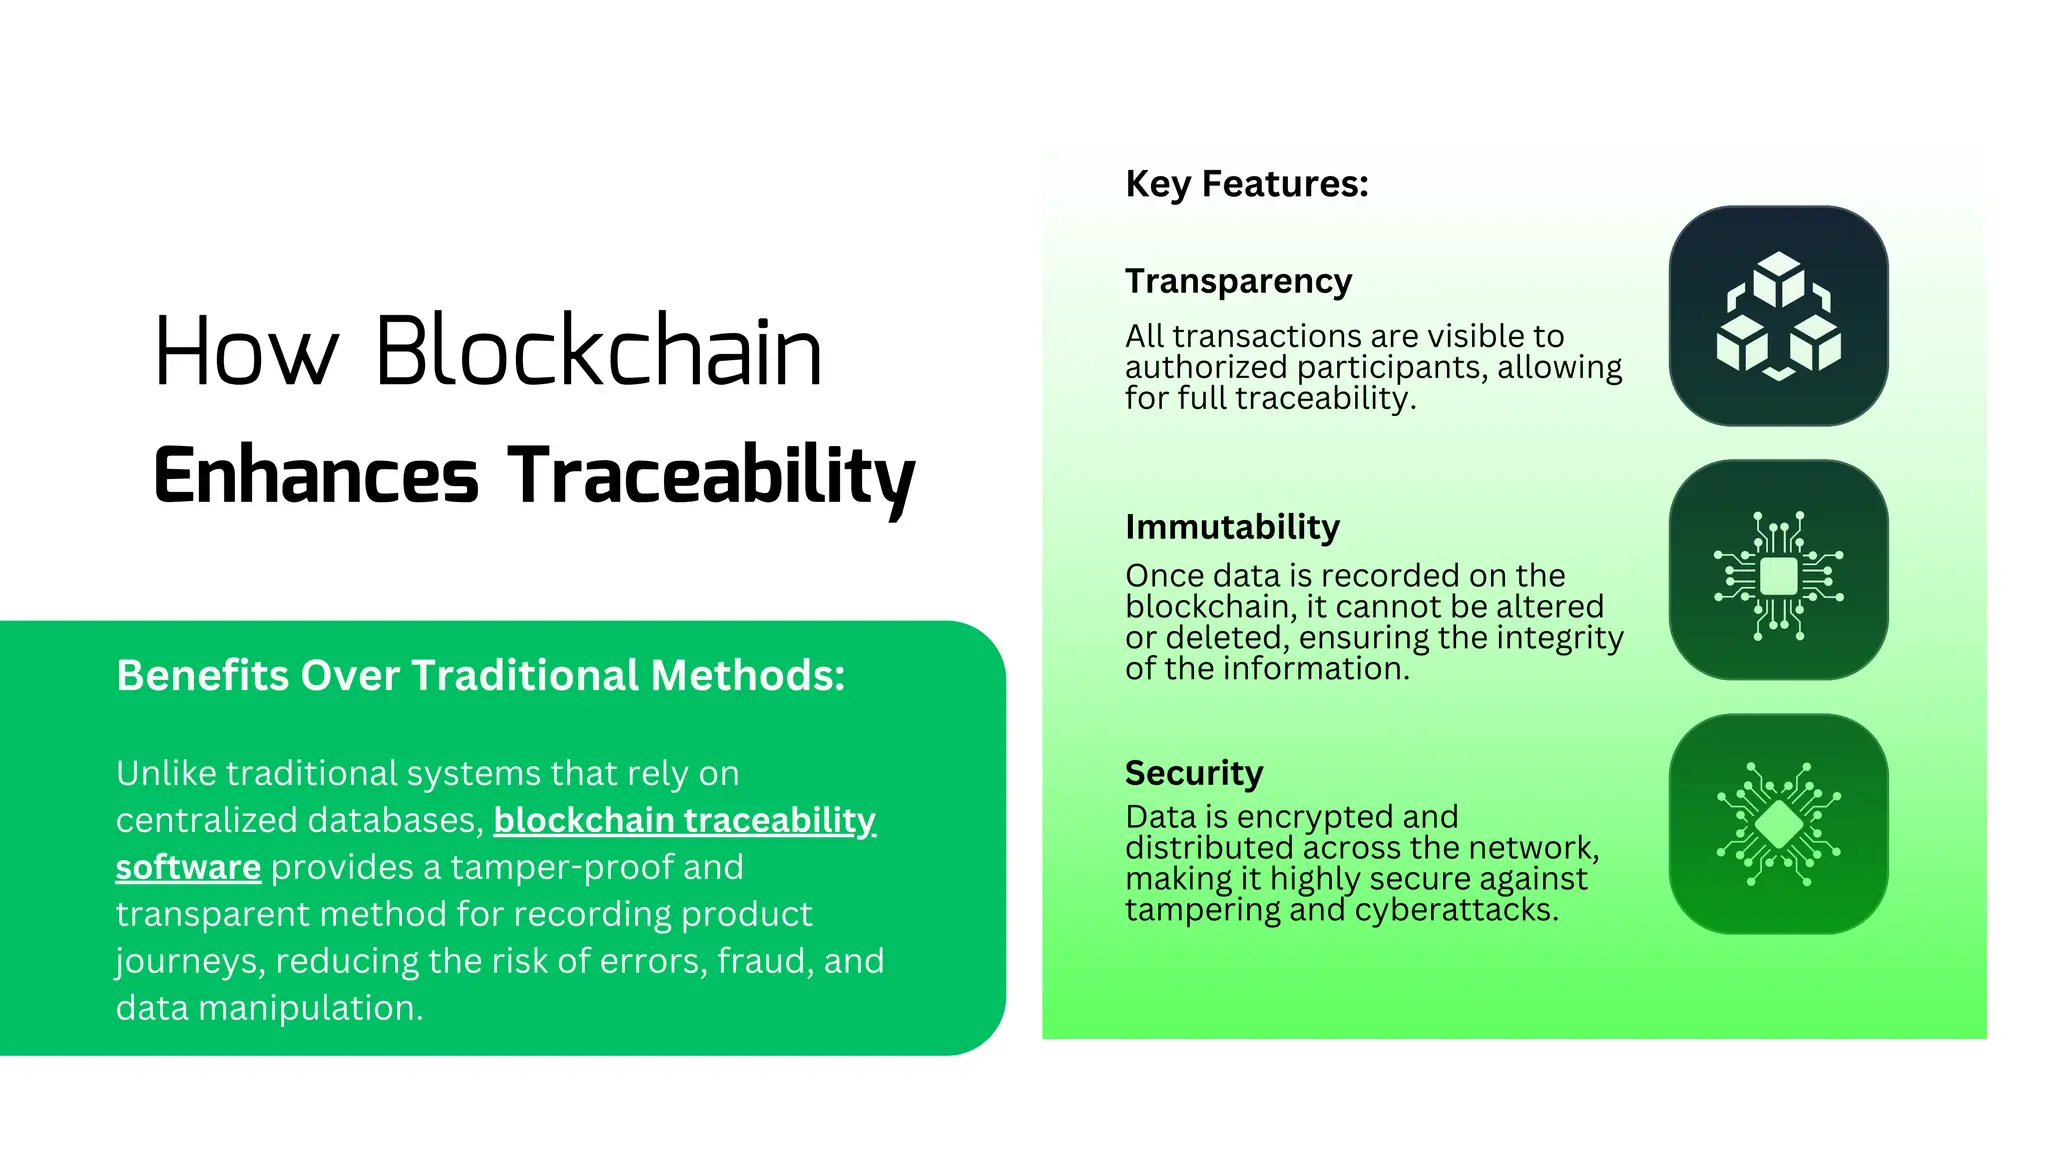
You start by defining your data model. Every shipment gets a unique identifier. That identifier is hashed and recorded on-chain. The actual shipment details - temperature logs, timestamps, handler signatures - live off-chain in a database or IPFS. Only the hash goes on the blockchain. This is critical because storing large data on-chain is enormously expensive and fundamentally unnecessary. A SHA-256 hash is 64 characters. A full shipment manifest with temperature readings could be megabytes. You put the 64-character fingerprint on-chain and the megabytes off-chain. Anyone can verify the data hasn't been altered by recomputing the hash and comparing it to what's stored on the ledger. Here's the edge case that nearly killed our project. We had a pharmacy in Ohio that received a shipment where the temperature log showed a 47-minute gap. The hash verified perfectly. The blockchain said everything was fine. But the gap meant the refrigeration unit had been offline for nearly an hour during transit, and we had no way to know from the on-chain data alone. What we should have done was require continuous GPS and temperature telemetry with cryptographic signatures at regular intervals, not just a single hash at delivery. The workaround was implementing a second verification layer using oracle feeds that cross-referenced the shipment's location data against known carrier routes. It added complexity but caught the gap. I wish we'd designed it properly from the start instead of learning the hard way. Another thing nobody tells you about blockchain transparency: it works both ways. Everything on a public ledger is permanently visible. That's the transparency part. The problem is that pseudonymity isn't anonymity. Address clustering algorithms can link multiple wallet addresses to single entities with reasonable accuracy. If your supply chain participants use public blockchains and their transaction patterns are visible, competitors can analyze the flow of goods through your system just by watching the chain. We saw this happen. A competitor mapped our entire distribution network by analyzing transaction patterns over four months. It took them about two weeks of focused analysis. After that, we moved our critical supply chain operations to a permissioned network where only authorized participants could see transaction data.
Get the Full Details

Let me address security in a way that might surprise you. Blockchain networks are generally more secure than traditional databases for certain use cases, but they introduce entirely new attack vectors. Smart contract vulnerabilities account for the vast majority of blockchain-related losses. The infamous DAO hack in 2016 resulted in approximately 3.6 million Ethereum being stolen, worth roughly $60 million at the time. More recently, the Poly Network hack in 2021 saw around $611 million in assets drained before being partially returned. These aren't blockchain failures. They're smart contract failures. The underlying ledger remained intact. The code governing the contracts had flaws. When I review smart contracts before deployment, I look for three categories of vulnerability: reentrancy attacks, integer overflow and underflow, and logic errors in access control. Reentrancy is still the most common issue in production contracts. It happens when a contract calls an external contract before updating its own state, allowing the external contract to loop back and drain funds. The fix is well-known - use the checks-effects-interactions pattern. Check your conditions, update your internal state, then interact externally. Most modern frameworks handle this for you, but you still need to verify. There's a significant trade-off you need to understand before committing to any blockchain solution. Decentralization reduces single points of failure but increases operational complexity dramatically. A traditional database admin can restore a backup in minutes. A blockchain incident requires coordination across multiple validator nodes, potential hard forks, and community consensus. Our team once spent three days resolving a consensus issue on our testnet caused by a faulty validator configuration. Three days. In a centralized system, that would have been a restart and a configuration reload taking maybe ten minutes.
Gas fees on Ethereum mainnet can also make certain applications economically unviable. During high-traffic periods, transaction fees have exceeded $100 for simple operations. If you're processing thousands of micro-transactions, this cost structure destroys the business case. Layer 2 solutions like Optimism, Arbitrum, or zk-Rollups reduce fees significantly, sometimes by a factor of 100x or more. But they introduce their own complexities around bridge security and finality assumptions. Our team evaluated five different L2 solutions over six months before settling on Arbitrum for our production system. The decision wasn't trivial and required load testing each option against our specific throughput requirements. If you're considering implementing blockchain for transparency and security, here's what I'd suggest based on actual implementation experience rather than enthusiasm. Start with a clear problem statement. Blockchain adds overhead. It's slower and more expensive than a traditional database for write operations. You should only use it when you need properties that traditional databases don't provide natively - decentralization, immutable audit trails, multi-party consensus without a trusted intermediary. If a single organization controls the database and all parties trust that organization, a blockchain probably isn't necessary. This is the single most important decision and the one most projects get wrong.
Choose your consensus mechanism based on your actual requirements. Proof of Work provides the strongest security guarantees but requires enormous computational resources. Proof of Stake is more energy-efficient but introduces different attack vectors like nothing-at-stake problems and stake centralization. Practical Byzantine Fault Tolerance works well for consortium blockchains with known participants. We used PBFT for our supply chain network because we had five known participants who all needed to validate transactions. It gave us fast finality - typically under two seconds - without the energy cost of mining. Implement proper key management from day one. I cannot stress this enough. Lost private keys mean lost assets permanently. There is no password reset on a blockchain. We lost approximately $40,000 in test transactions when a developer accidentally deleted his hardware wallet configuration file. The funds were gone forever. Use hardware security modules, implement multi-signature wallets, and maintain secure key recovery procedures. This isn't optional. It's fundamental. For development, get started with the tools that matter. Solidity is the primary language for Ethereum smart contracts. Rust is increasingly popular for Solana and near-symmetric chain development. Python with Web3.py or ethers.js for JavaScript environments handles the client-side interaction. Set up your development environment with Hardhat or Foundry for testing. Foundry has become my preferred tool - it's faster than Hardhat for compilation and its fuzzing capabilities catch edge cases that traditional unit tests miss. I ran our entire smart contract test suite through Foundry's fuzz tester and found three vulnerabilities that conventional tests completely missed.
Don't skip formal verification. It sounds academic but it's practical. Tools like Certora and Keccak can mathematically prove properties about your smart contracts. The cost is higher upfront but it catches issues that auditing alone might miss. We used formal verification on our critical payment contracts and caught a subtle race condition that could have allowed double-spending under specific timing scenarios. Standard testing wouldn't have caught it because it required a very specific sequence of concurrent transactions. The honest assessment: blockchain is not the answer to every transparency problem. It's a tool with specific strengths and real weaknesses. It excels at creating tamper-evident records across multiple untrusted parties. It struggles with privacy, scalability, and the oracle problem - getting real-world data onto the chain reliably. If you need to prove that records haven't been altered after the fact, blockchain is excellent. If you need real-time high-throughput processing, it's often the wrong choice. The landscape is moving fast. Zero-knowledge proofs are becoming practical for private transactions on public ledgers. Interoperability protocols like Cosmos and Polkadot are reducing the fragmentation problem. Regulatory clarity is slowly improving in major jurisdictions. But these are trends, not solutions you can implement today. Build on what works now, plan for what's coming, and never confuse the technology with the outcome you actually need.