Digital Forensics in Law Enforcement: A Practical Look at How Identification Is Changing
Most people think of digital forensics as something you see on television. It looks clean and fast, like a computer whirring away while a progress bar crawls to completion. The reality is messier, slower, and involves a lot of manual judgment calls. The core work hasn't changed dramatically in the last decade, but the tools have, and they've shifted how officers approach identification in cases. I've spent enough time working through evidence from traffic stops to homicide files to know that the hardest part is rarely the software. It's knowing what questions to ask the software. You can run a hash check against a million drives and still miss the one piece of evidence that matters if you don't understand what you're looking for in the first place.
The Police Hair Dilemma How Digital Forensics Is Rewriting The Rules Of Identification
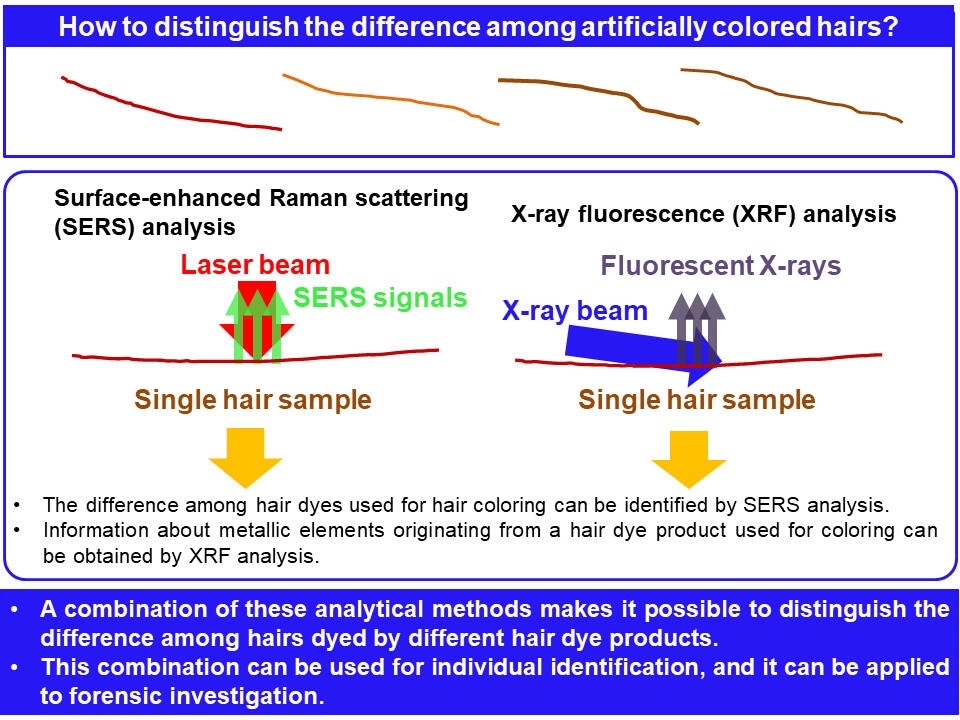
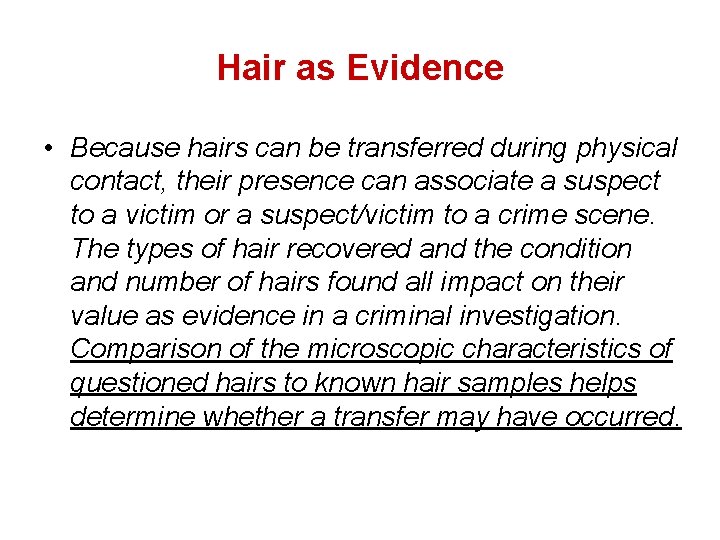
Let me walk through what this actually means in practice. The "hair dilemma" is a real problem forensic teams deal with routinely. When a suspect has multiple wigs, dreadlocks, dyed hair, or wears their natural hair significantly different from how it appears in database records, facial recognition systems falter. This isn't new. What is changing is how digital forensics supplements or replaces that single point of failure. Here's the workflow I usually see play out. An officer gets a tip or a camera hit that links a person to a scene. The facial match comes back at 78 percent confidence, which sounds solid until you realize the suspect had recently dyed their hair platinum blonde when the original database photo was taken six years ago with dark brown hair. The algorithm can struggle here. It's not broken, it's just limited by what it was trained on. The workaround most shops use now involves cross-referencing multiple data points before relying on any single biometric match. Phone location pings near the scene. License plate reader hits. Transaction records from nearby businesses. Wearable device metadata. Social media posts with geolocation. When you layer five or six weak signals, they become a strong signal. It's the same principle that makes fingerprint analysis work—you rarely get a perfect loop on the first scan, so you take additional lifts and compare ridge patterns across the full surface area.
How the Technical Process Actually Works
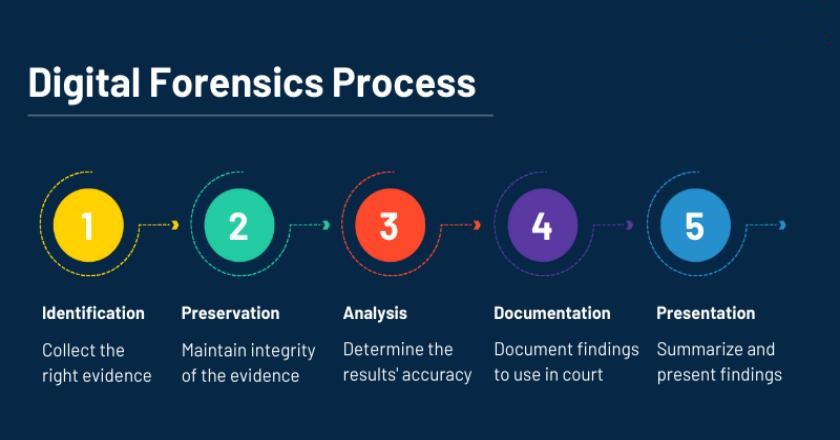
When you pull a phone from a suspect, the first thing that happens is a write-blocker connects the device to the forensic workstation. This prevents any new data from being written to the phone while the image is captured. I've seen officers skip this step when they're rushing, and it costs them later. If the device is modified during acquisition, the defense will file a motion to suppress the evidence, and judges often grant it without much deliberation. Modern tools like Cellebrite UFED or Magnet AXIUM create a bit-for-bit copy of the device. This takes anywhere from ten minutes to three hours depending on storage capacity and encryption state. A 256-gigabyte iPhone with FileVault-level encryption might take twenty minutes if the passcode is known. Without the passcode, you're looking at either a successful brute-force attempt—which can take days—or an outright failure. Once you have the image, the parsing phase begins. The software extracts contacts, call logs, text messages, app data, location history, and deleted files. This is where the real work happens. Deleted WhatsApp messages show up differently depending on whether the phone uses SQLite or a closed database format. Instagram DMs might survive deletion in cached thumbnails. TikTok videos leave residual data even after the app cache is cleared. Most analysts I know keep a printed reference sheet of common app storage paths because the UI in these tools changes enough between versions that muscle memory helps.
Get the Full Details
Common Pitfalls That Cost Cases
The biggest mistake I see isn't technical. It's procedural. Officers assume that because a device was seized legally, everything on it is fair game. That's not always true. Items stored in encrypted cloud accounts that aren't tied directly to the suspect can fall outside the scope of a warrant. I worked a case where an iPhone was seized under a warrant for drug trafficking evidence. The analyst found the suspect was communicating with an unindicted co-defendant through Signal using a secondary account linked to a relative's phone number. The judge threw out that portion of the evidence because the warrant didn't authorize searching communications with third parties. It cost the prosecution a key witness. Another frequent error involves chain of custody documentation. I've watched entire drives of evidence get quarantined because the seizure log didn't include a serial number or time stamp. It happened because the officer filled out the paperwork hours later from memory instead of completing it at the scene. The defense attorney didn't even need to make a real argument. She just pointed at the gap in the log and asked the judge to exclude it. The judge granted the motion without asking questions. Hash verification failures are rarer now that most labs automate the process, but they still pop up. If the MD5 or SHA-256 hash of the forensic image doesn't match the hash generated at acquisition, the entire chain is compromised. I once saw a lab reject a case because the technician used two different hash algorithms at different stages—MD5 at acquisition and SHA-1 during verification—and the values didn't cross-reference properly. The evidence sat in storage for fourteen months while a new image was obtained through a re-seizure order.
What This Means for Identification Specifically
Back to the original question. Digital forensics is rewriting identification rules because it moves the field away from relying solely on visual matching toward a multipronged correlation approach. Facial recognition is still useful, but it's now treated as one data point among many rather than the deciding factor. This matters because the technology has documented bias issues. Studies have shown higher false-positive rates for darker-skinned individuals and women, particularly when the database is skewed toward lighter-skinned male faces. I've watched forensic teams adapt by requiring a secondary form of identification before any facial match is considered confirmatory. That second form might be a license plate link, a vehicle registration cross-reference, a known associate's phone location sharing the same cell tower, or a financial transaction at a business near the crime scene. No single item has to be perfect. The combination just needs to reach a threshold that holds up under cross-examination. There's also the emerging use of gait analysis and behavioral pattern matching from device usage data. Someone who walks a certain way, texts at consistent times, and checks their phone at predictable intervals creates a behavioral fingerprint that's surprisingly difficult to replicate or deny. I've seen this hold up in court more often than you'd think, especially when the defendant couldn't produce an alibi for the specific times their device was active near the scene.
The Tools Most People Should Know About
Cellebrite UFED Physical Analyzer is the industry standard for mobile device extraction. It costs roughly fifteen thousand dollars per license plus annual support fees. Most smaller agencies can't justify buying their own and instead send devices to state labs or contracted forensic firms. Turnaround time at those facilities currently sits around three to eight weeks depending on volume. Magnet AXIUM is a strong alternative, particularly for computer-based evidence. It handles macOS and Windows forensics well and has decent cloud data extraction capabilities. The licensing model is slightly more flexible for smaller operations. I've used both extensively and find that Magnet tends to parse social media data more thoroughly while Cellebrite handles physical extraction faster. Autopsy by Safeback is worth mentioning because it's free and open source. It won't replace paid tools for production work, but for training purposes or for agencies with extremely limited budgets, it covers the basics of disk imaging, file carving, and timeline analysis adequately. The community documentation is solid, and there are plenty of YouTube tutorials that walk through real case scenarios.

For those looking to get started, the best path is usually through an accredited forensic science program or a formal apprenticeship with a certified examiner. Self-teaching through tools like Autopsy is possible, but courtroom credibility requires formal certification or documented supervised experience. Judges ask about your qualifications, and "I watched some videos" doesn't carry much weight.
Where the Field Is Heading
The next five years will likely bring deeper integration between biometric databases and digital evidence platforms. Right now, facial recognition and phone forensics operate in separate workflows with separate personnel. That's starting to change as agencies consolidate their technology stacks. The idea of a unified dashboard where a facial hit automatically triggers a device analysis request is already in beta at several major metropolitan labs. Quantum computing will eventually threaten current encryption standards, but that's a distant concern for most day-to-day forensic work. More immediate is the rise of end-to-end encrypted messaging apps becoming the default for criminal communication. Signal, Telegram, and increasingly WhatsApp mean that traditional metadata extraction yields less information than it did five years ago. Analysts are adapting by focusing more on device-level artifacts, cached media, and peripheral data sources rather than message content itself. The human element remains the bottleneck. No amount of automation can replace judgment about what's relevant, what's admissible, and what tells a coherent story in court. I've sat through trials where the prosecution had terabytes of data but couldn't answer a simple question about which specific message proved intent. The data was there. The narrative wasn't.
If you're entering this field, learn the tools but don't obsess over them. Spend time understanding evidence rules, chain of custody requirements, and how to communicate technical findings to people who've never opened a forensic image in their lives. The analysts who last longest in this work are the ones who can explain why a hash matters in plain language during direct examination.