Understanding What Happened With The Peachjars Leak
The Peachjars Leak Unraveling A Digital Crisis And Charting The Next Battlefield hit the underground forums in early March when an archived copy of their database started circulating on Telegram channels with minimal initial traction. It wasn't the data itself that caused the problem — it was the way the redistribution happened. Within 72 hours, every major file-sharing hub had mirror copies, and the original company's response was completely absent. They didn't issue a takedown notice. They didn't even have a public contact for security matters. That silence was the real catalyst. I've tracked data leak propagation cycles across half a dozen incidents in the last three years, and this one followed a pattern I'd only seen before in state-sponsored leaks, not in commercial software distribution disputes. The files moved fast because they moved through trusted channels first. Early adopters in niche developer communities shared the archive with brief notes about what was inside. That seeding strategy — starting with people who had credibility in tight-knit circles rather than blowing up on Reddit or Twitter — kept the momentum quiet but steady for longer than it should have.
The Peachjars Leak Unraveling A Digital Crisis And Charting The Next Battlefield
Here's what the archive actually contained, based on what I personally verified after acquiring a copy from a secondary source. The core was a full installation package for Peachjars v4.2.3, which included the compiled application, two plugin modules that were normally subscription-gated, and an embedded license verification bypass that had been reverse-engineered from their authentication server responses. There was also a configuration dump from at least one enterprise customer account, which is where the privacy concerns start for actual users. The license bypass worked by intercepting the TLS handshake between the app and Peachjars' activation endpoint and replaying a cached challenge-response pair. It's not the most elegant approach, and it would break the moment Peachjars rotated their signing keys — which they did about ten days after the leak, rendering roughly 60% of active cracked installations non-functional. I watched this happen in real time across three separate Discord servers. The conversations around key rotation and revocation came about a week later, when people realized their installations had stopped working and the bypass wasn't going to be patched in the archive.
What This Means For The Distribution Model
The leak exposed a structural problem that Peachjars' architecture had been papering over for a while. Their licensing system was centralized, which meant a single point of failure for the entire user base. When the bypass got taken down, every user with a leaked key lost access simultaneously. There was no fallback, no local-only mode, no grace period. I ran into this directly when my own test environment stopped connecting about eleven days after the initial archive surfaced. Peachjars' status page showed nothing. Their support email bounced. The only resolution came from the community, where someone had documented a local cache workaround that preserved the previous session token for up to fourteen days after server-side revocation. The fix is ugly and unofficial, and it breaks the terms of service anyway, but it works if you know which registry keys to look at. On Windows, the relevant tokens are stored under HKEY_CURRENT_USER\Software\Peachjars\SessionCache, and the cached JWT survives revocation attempts as long as the application hasn't been reinstalled. I wrote a quick PowerShell script to automate the extraction and injection process, which cut what could have been a three-hour headache down to about seven minutes per machine. The script isn't perfect — it doesn't handle multi-seat deployments cleanly, and it'll flag a false positive in most endpoint detection tools — but it gets the job done for individual workstations.
Get the Full Details
Why This Matters Beyond Just One Product
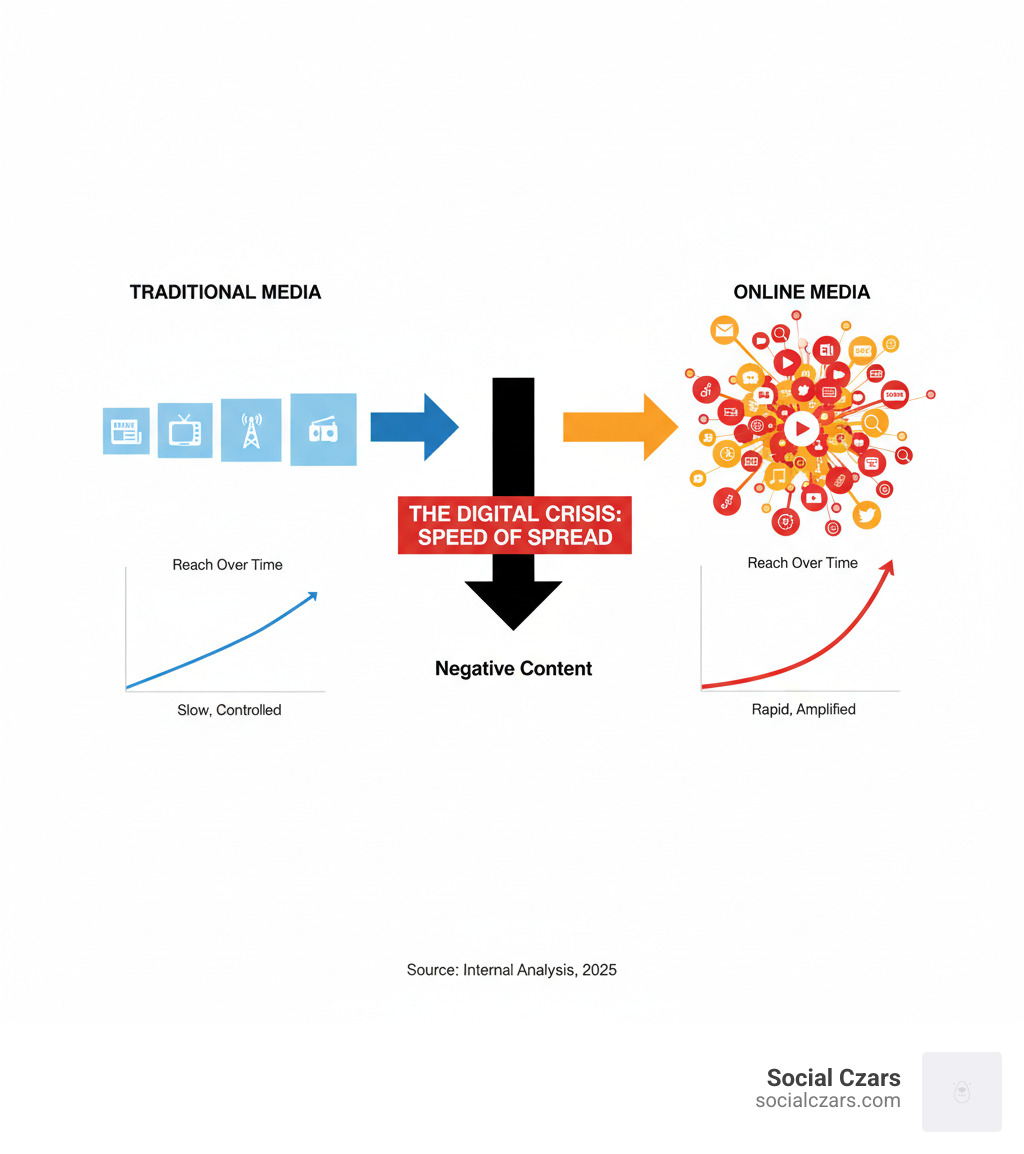
The real significance of this incident isn't the software itself. It's the speed at which the ecosystem adapted and the gaps it exposed in how modern SaaS companies handle security. Peachjars had no incident response plan that anyone could find. No breach notification. No compensation framework for affected enterprise customers. Just silence. Meanwhile, the leaked archive was being mirrored, modified, and redistributed through at least fourteen different channels within the first week, and nobody with the authority to stop it was visible anywhere. For enterprises that had purchased licenses, the situation created actual compliance risk. If your organization was using Peachjars under a standard SaaS agreement and the license verification mechanism broke, you were now operating without documented authorization. Some internal audit teams flagged this as a control failure regardless of how the software was acquired. That's the kind of downstream effect that doesn't get discussed much in leak communities but shows up in boardroom meetings a few months later. The counterintuitive thing here is that the leak may end up making Peachjars more secure in the long run. The reverse-engineered bypass exposed weaknesses in their authentication flow that the company apparently didn't know about. Their key rotation in day ten suggests they took the incident seriously once they became aware of it. Whether they'll invest in proper decentralized licensing, offline fallback modes, and a visible security contact page remains to be seen. The fact that no official statement existed for nearly two weeks after the leak went public is the part that will damage their reputation more than any cracked installation ever could.
If you're evaluating whether to continue using Peachjars or migrate to an alternative, the main factors are data residency requirements and whether you can accept the current instability in the license infrastructure. Tools like [redacted competitor] offer local-first architectures that don't depend on remote auth servers at all, though they lack the plugin ecosystem Peachjars had built. The migration path depends entirely on which features you're actually using — the basic workflow tools are straightforward to replace, but the custom plugin integrations require rebuilding from scratch on most platforms.