Why You Can't Remember Your Own Passwords
I've been doing IT security work for over a decade, and I still get locked out of systems sometimes. It's not glamorous. Most people think this is a memory problem, but it's really a design problem that has been around since the 1960s when computers first needed to verify identity. Here's what happens. You create a password. Then you change it six months later because someone told you to. Then you reset it because it expired again. Now you have seven passwords for seven different services, all vaguely similar but not quite the same, and none of them feel easy to recall under pressure. This is the core paradox: the more security we demand from ourselves, the worse we become at remembering the very things we need to protect. I ran into this exact issue last month when I was trying to access an old server for a client. I had documented the root password in a spreadsheet, sure, but the spreadsheet was encrypted with a separate password that I had set up two years prior. I spent about forty minutes trying different variations before giving up and triggering a full reset. That's not a rare edge case. That's a Tuesday for most people who manage more than a dozen accounts.
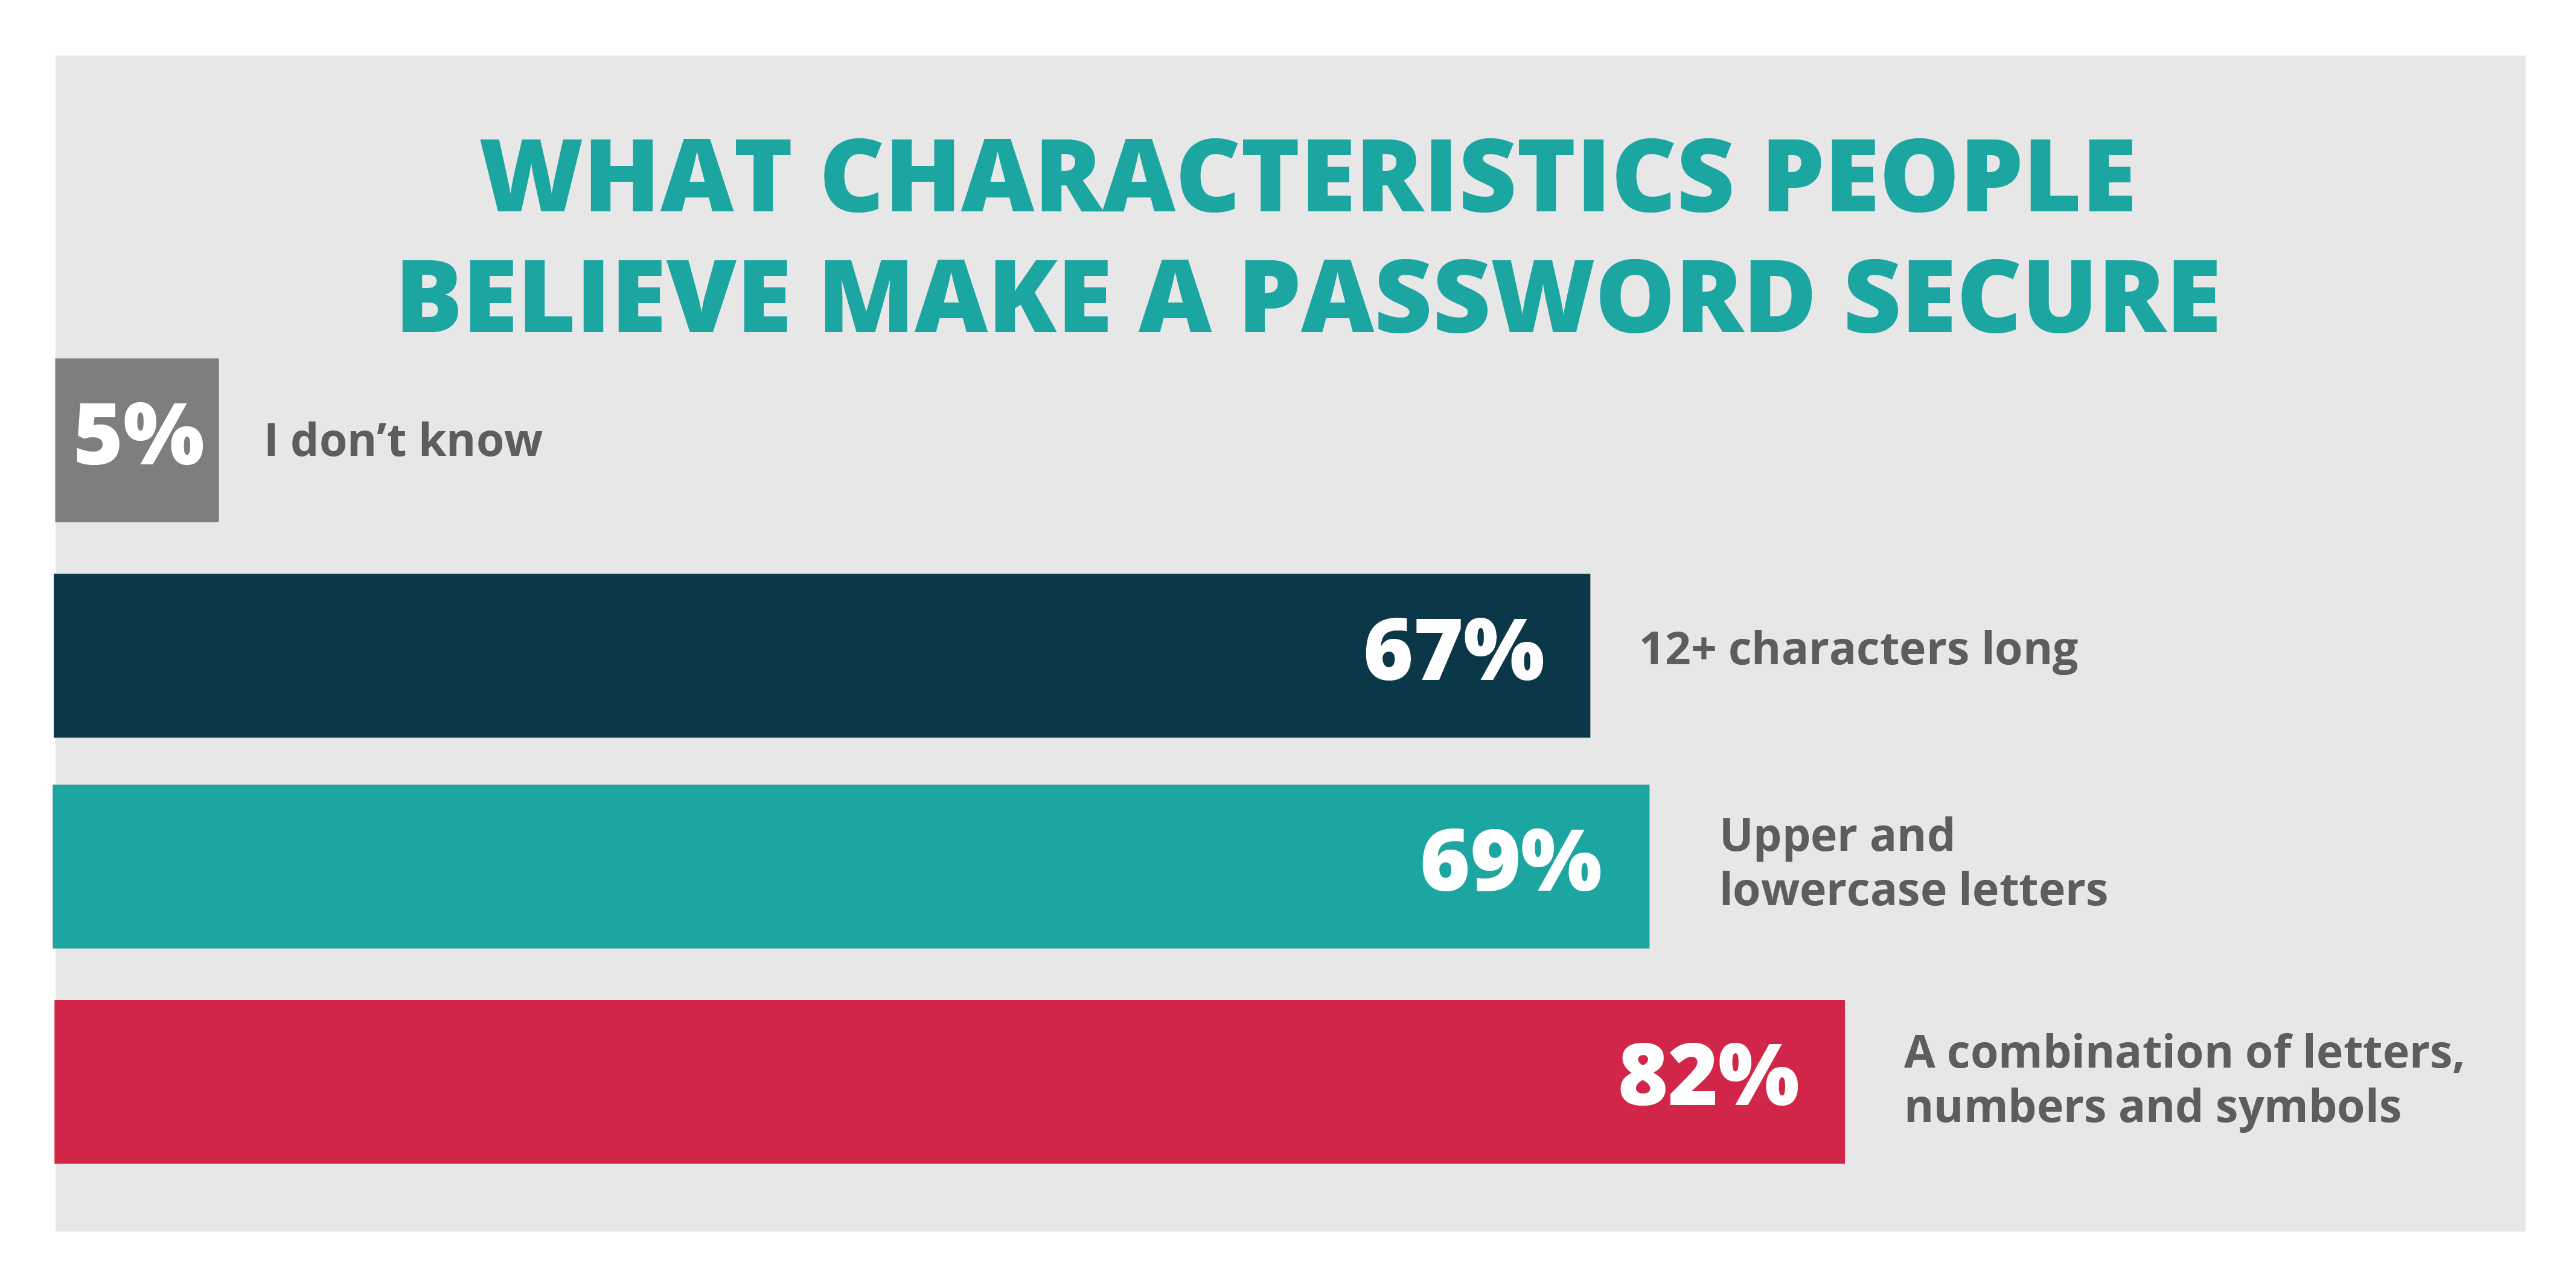
The real problem isn't that humans have bad memories. It's that we're asking people to memorize information that was never designed for human retention. A proper password policy might require 14 characters, one uppercase, one lowercase, one number, one symbol, no dictionary words, changed every 90 days. If you have eight accounts that each need unique passwords, you're being asked to hold about one hundred and twelve character positions in your head simultaneously. No human brain evolved for that kind of task. We evolved to remember where the good berry bushes were, not the SHA-256 hash requirements of a SaaS platform we signed up for in 2019. There's a concept in cryptography called key management, and honestly, most people have terrible key management. They treat passwords like they're simple secrets when they're actually more like cryptographic keys that need generation, storage, rotation, and revocation protocols. The moment you introduce that level of operational complexity into something a regular person uses to check their email, you're going to have failures. Not moral failures. Just engineering failures that happen when you build a system for supercomputers and hand it to humans who are already processing about one hundred and seventy four distinct pieces of information per day according to recent cognitive load studies. Some people try mnemonic strategies. I've seen the Diceware method recommended everywhere. Pick four or five random words and combine them. It's better than nothing, and it does increase entropy significantly compared to Password123. But then you hit the real wall: every system has slightly different validation rules, and your perfect twenty-character Diceware string might get rejected because one platform thinks hyphens count as special characters while another counts them as spaces that break the input field. You end up creating variants anyway, which brings you right back to square one.
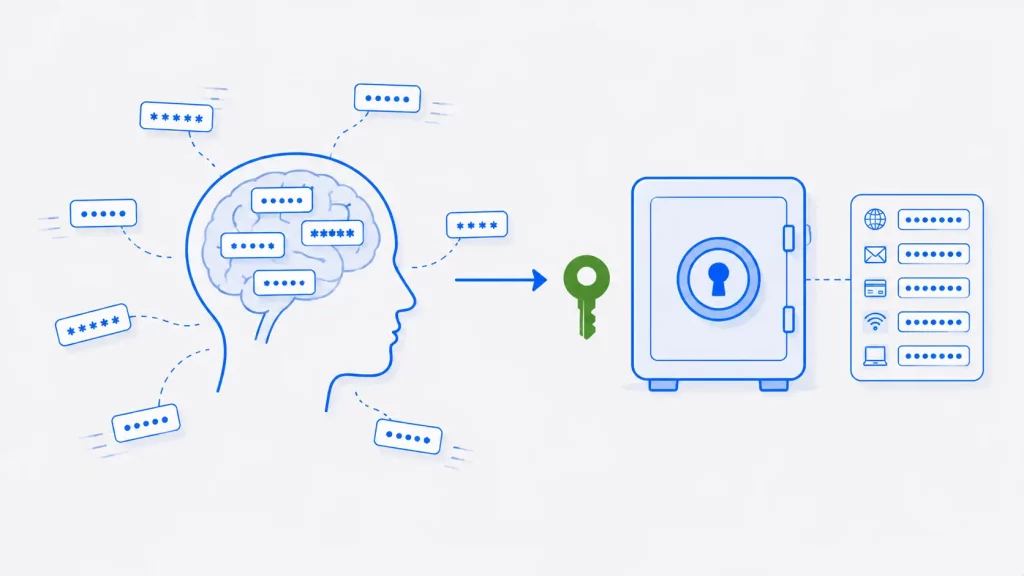
The workaround I use, and it's not elegant, is a password manager with a strong master password. I use a commercially available solution that generates random strings, stores them encrypted locally, and syncs across my devices. The master password itself is a Diceware-style passphrase with seven random words. I wrote it on a physical card and keep it in a locked drawer, not in my phone, not in my email, not anywhere digital. If my laptop gets stolen, the attacker has nothing useful. If I lose my phone, I still have the card. This approach has limitations that most articles don't mention. First, you now have a single point of failure. Lose that master password and you're locked out of everything. Second, password managers can become vulnerable if the vendor gets compromised or goes out of business, though open-source options like Bitwarden mitigate this somewhat. Third, there's the social engineering problem. If someone calls you pretending to be from your bank and you've already given them some personal information, no amount of encryption in your password manager matters. The weakest link is still the human on the phone. Another thing people don't talk about enough is the transition period. Switching from a mental password strategy to a manager takes about two weeks of frustration. You'll forget passwords during that window. You'll click "forgot password" more times than you'd like. Your coworkers will notice you seem stressed. This is normal and it passes. But most people quit during that two-week window because the temporary pain feels worse than the long-term benefit, which is a rational short-term calculation that makes the overall system fail.
Get the Full Details
Multi-factor authentication partially solves this by adding a second factor, but it introduces its own paradox. Now you need your password AND your phone, AND sometimes a hardware key, AND sometimes a backup code that you printed out and stored somewhere you can't find. I had a client who lost access to his company's financial system for three business days because his MFA backup codes were on a piece of paper he taped under his old desk, which he had donated to goodwill six months earlier. Two-factor security shouldn't require a treasure hunt to access. If you're starting from zero, the practical steps are straightforward but tedious. Get a password manager. Generate unique passwords for everything, starting with your most important accounts. Enable MFA everywhere it's available, preferably with a hardware key like a YubiKey for critical systems. Write down your master password on paper and store it somewhere safe. Set up a recovery email that isn't one of the accounts you're protecting. Don't use the same recovery email across all your services because then you've created a dependency chain that collapses if one service gets breached. I should mention that some organizations have started moving toward passkeys and WebAuthn standards, which eliminate passwords entirely for supported services. This is genuinely better technology. But adoption is uneven, and you'll be dealing with the old password systems for probably another five to ten years minimum, so learning to manage passwords effectively isn't optional even if the future promises a better way.
The bottom line is that forgetting your passwords isn't a personal failing. It's the predictable result of asking people to perform cryptographic operations in their heads while also living their actual lives. The systems are designed to be secure. The humans aren't. Building a practical workflow around that reality is the only thing that actually works long-term.