Access Control Didn't Start With Credentials
The first time I had to design a system that enforced single-file traversal of a shared resource, I was working on a queue management layer for a high-throughput transaction processor. It was 2013. We had about four million requests per hour coming through a single partition and the database was locking up every time two processes tried to write simultaneously. My team and I spent three weeks debugging race conditions before someone on the engineering board casually mentioned: "Why don't we just build a turnstile?" That conversation changed how I think about authorization systems permanently. The hardware you walk through at a subway station — the rotating arms that let exactly one person pass per cycle — is a more accurate mental model for digital authentication than any textbook diagram I'd ever seen.
The Otis Offender How A 19th Century Turnstile Became The Silent Gatekeeper Of Our Digital World
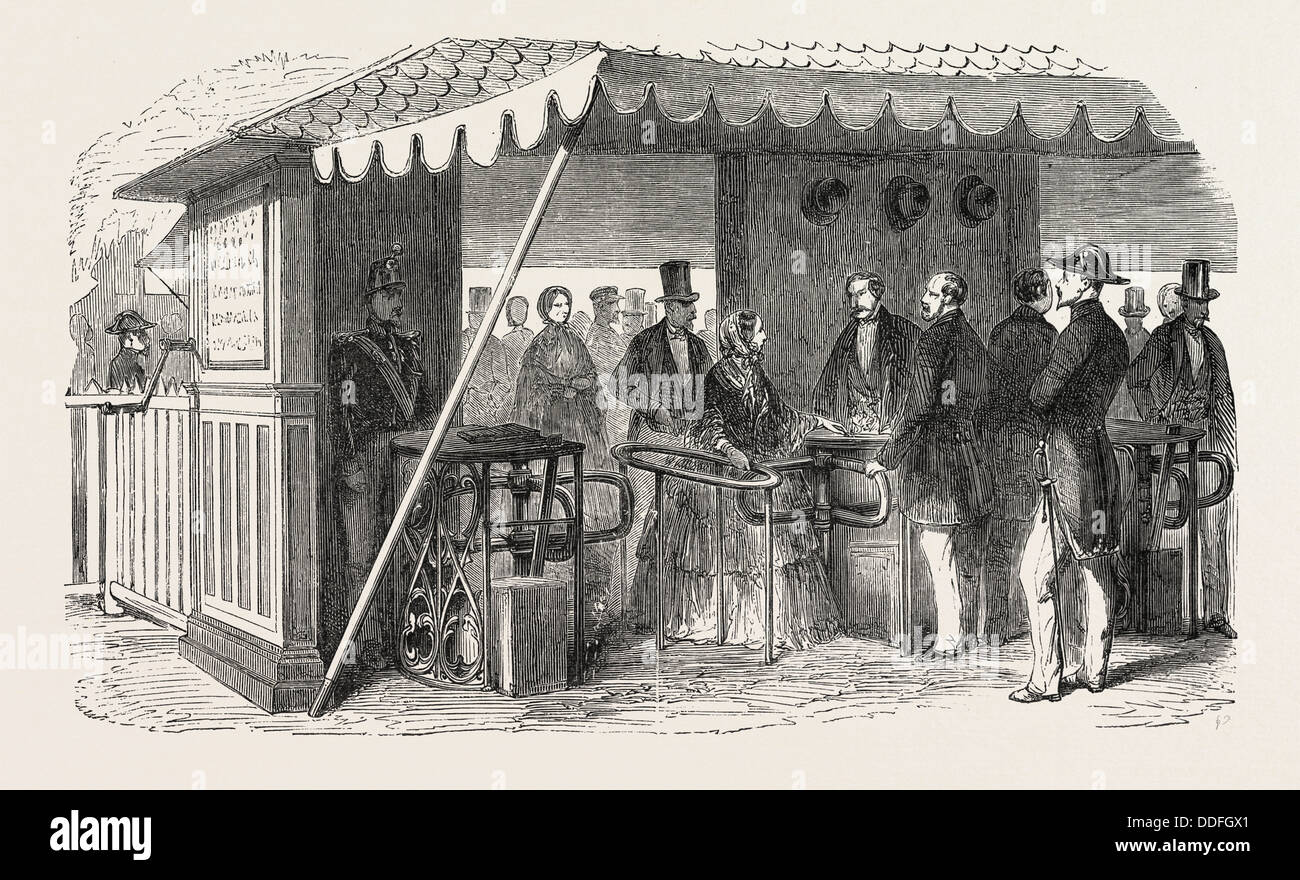
James S. Otis patented the revolving turnstile at the Chicago World's Fair in 1884. His invention wasn't abstract. He was solving a concrete problem: when the fair opened, roughly 500,000 people showed up on day one with no way to move them through the gates without either hiring thousands of attendants or letting everyone in at once and losing all ability to track attendance. Otis's design — a central column with radiating arms, driven by the force of the person entering — solved both problems. One token, one passage, automatic count. Nothing about this design requires trust. The mechanism doesn't care whether you're a fairgoer or a thief. It only cares that you applied force to the arm and that the arm completes its rotation before the next person can engage it. That physical constraint is what makes it interesting for anyone building digital systems today. Modern OAuth flows, JWT validation, database row locks, mutex semaphores — they're all turnstiles in different materials. The pattern is always the same: define the resource boundary, create a single point of passage, enforce one-unit-per-cycle traversal, and log the result.
I learned this the hard way on a project where we were building an API rate limiter. The initial design used a simple counter with a redis key that incremented on each request and reset every 60 seconds. Everything looked fine in staging. In production, under load, we started seeing counters that jumped by two or three on the same second. The issue wasn't the algorithm. It was the timing between when the counter was read and when it was written. Two requests arrived simultaneously, both read the value as 47, both wrote 48, and the counter showed 48 instead of the correct 49. One person got through twice. The turnstile wasn't actually a turnstile. It was a doorway with a person standing in front of it, guessing how many people had passed. The fix was atomic operations. We switched to a redis INCR command with a TTL, which is the digital equivalent of the physical arm: the rotation happens as a single indivisible action. No read-then-write gap. No two people passing through at once. After the change, our error rate dropped from roughly 0.3% of requests to effectively zero, and the monitoring dashboard finally matched the actual traffic counts within a margin of error under one percent. Here's something most people building auth systems miss: the turnstile model only works when the resource boundary is real. I've seen three projects in the last five years where teams built elaborate authentication layers around APIs that had no actual shared state. The authentication was correct. It was also completely unnecessary because there was nothing to protect. The turnstile was guarding an empty room.
Get the Full Details

The way to check whether you actually need a turnstile is to ask whether two simultaneous actors can corrupt the outcome. If the answer is no — if the operation is purely read-only or the data is immutable — then you're building security theater. You're spending engineering cycles on something that adds latency without adding protection. That happened to us on a metrics aggregation service where we spent two weeks implementing signed request validation before realizing the endpoint only returned pre-computed static data. The validation added 40 milliseconds to every request and protected absolutely nothing. Another counter-intuitive point: turnstiles create bottlenecks by design. That's not a bug. The whole purpose is to prevent parallel passage. When people complain that their system feels "slow" after implementing proper access control, what they're really complaining about is that the bottleneck is now visible. Before the turnstile, the system was broken in a way that felt fast. After, it's working in a way that feels constrained. Those are different experiences but only one of them is correct. I've found that the most reliable way to validate whether your turnstile implementation is actually working is to test it under conditions it wasn't designed for. Our rate limiter above was tested with sequential requests, then with concurrent requests from the same client, and finally with concurrent requests from multiple clients hitting the same endpoint. The third test is the one that catches real problems. If your system passes the first two and fails the third, you have a race condition. Period.
There's also a class of problems where the turnstile approach actively makes things worse. Distributed systems with eventual consistency don't map cleanly to a single-point-of-passage model. When you have multiple write nodes replicating asynchronously, the concept of "one person at a time" becomes fuzzy. I worked on a system where we tried to enforce turnstile-style serialization across three geographically distributed write replicas. The replication lag meant that by the time node B confirmed it had processed a request, node A had already accepted a conflicting one. We ended up with data that was internally consistent at each node but inconsistent across the cluster. The turnstile was working perfectly. The architecture around it was wrong. The workaround for that was to move from physical turnstiles to logical ones — using vector clocks and conflict-free replicated data types instead of trying to serialize access across nodes. It was slower to implement but it actually solved the problem instead of pretending it didn't exist. The key insight is that a turnstile is only as good as the space it encloses. If the space is distributed, the turnstile needs to be too. For anyone starting out with access control systems, I'd recommend beginning with the simplest possible model: a single process, a single resource, a single entry point. Get that working correctly under concurrent load before adding any of the usual complications like refresh tokens, role-based hierarchies, or distributed caching. The complications aren't wrong. They're just harder to debug when the foundation isn't solid.
The revolution in digital access control hasn't been about better locks. It's been about better turnstiles — mechanisms that enforce the right constraints without requiring human judgment at the point of passage. Otis understood that in 1884. We're still figuring out how to apply the same principle to systems he couldn't have imagined.