Working with the 172.x.x.x Private Range
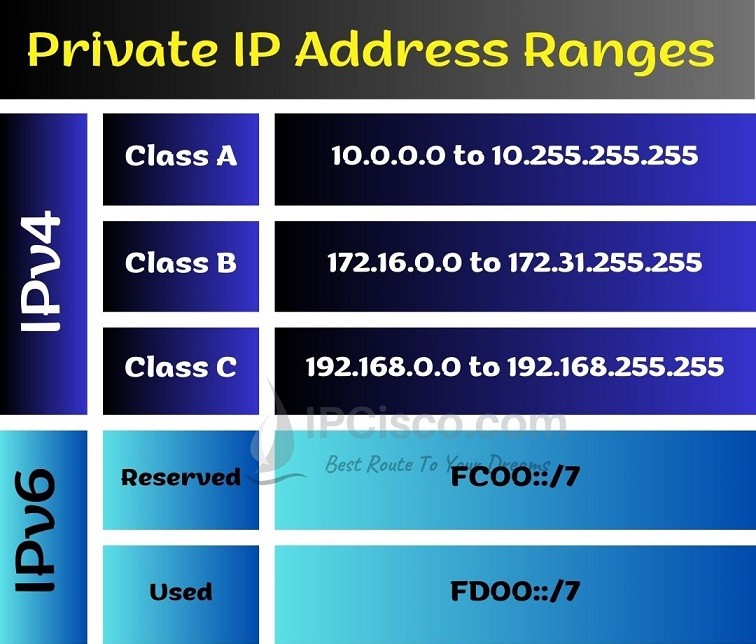
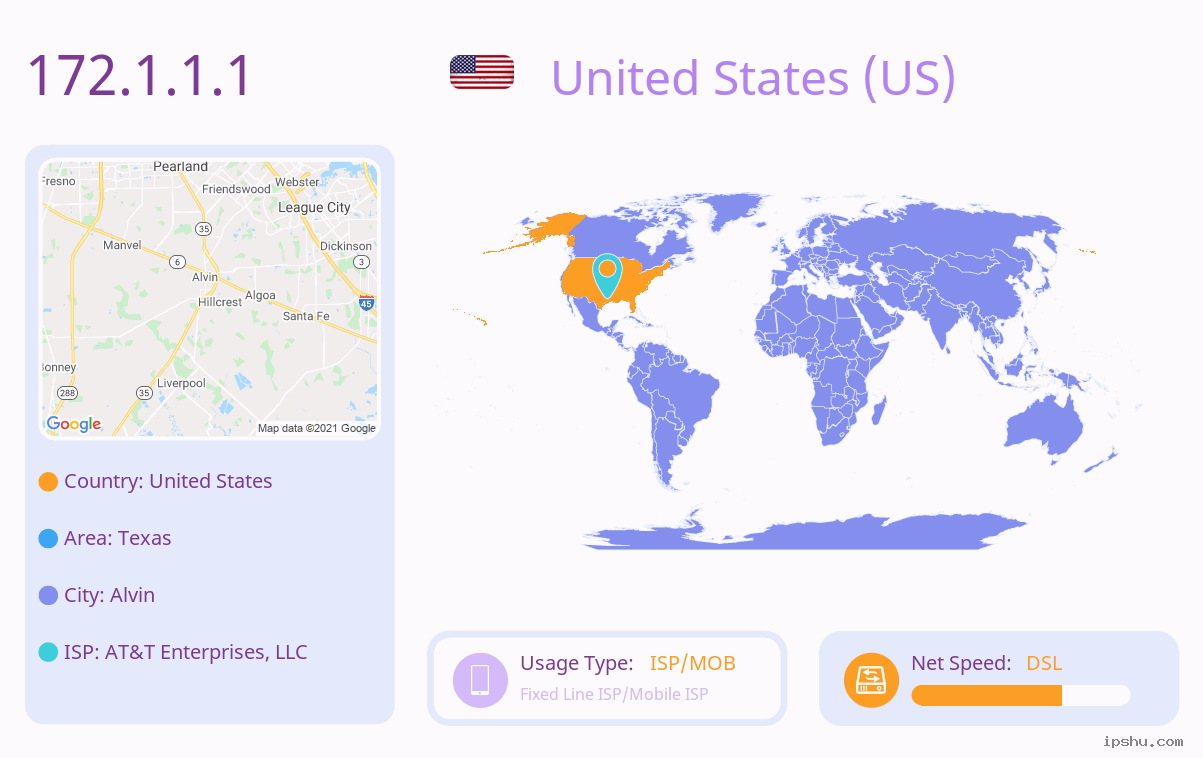
I first ran into the 172.x.x.x space back in the mid 2010s when a client was migrating from a flat /16 network to a segmented environment. They had been using 172.16.0.0/16 across two buildings and it was causing routing confusion because 172.16.0.0/12 is a private range per RFC 1918, but they were also registering public IPs in the 172.0.0.0/8 block on their edge. That overlap made debugging traceroutes a nightmare for about three weeks. Here is what most people miss about this range. The entire 172.16.0.0 to 172.31.255.255 block is reserved for private use. That covers exactly 16 contiguous /16 networks, which gives you over a million unique host addresses. A lot of home routers never touch it, which is why it feels exotic compared to the ubiquitous 192.168.x.x subnet. It is not actually mysterious. It is just less common in residential gear and shows up more in enterprise and datacenter environments where network architects need room to grow. The anomaly most people run into is that the 172.16.0.0/12 range sits inside a larger /8 block, and that causes confusion when you are writing firewall rules or ACLs. If you write a rule like deny 172.0.0.0/8, you are blocking every single IP from 172.0.0.0 through 172.255.255.255. That includes the private range, but it also includes the entire public address space in that /8. I once saw this happen on a corporate LAN where a junior admin wanted to block external traffic hitting the internal segment. He wrote the broad rule, and suddenly the entire corporate VPN dropped because their public-facing mail server was on a 172.x.x.x IP that had been assigned years earlier by mistake. The fix was to scope the deny down to 172.16.0.0/12 only.
The Mysterious World Of 172 Ip Ranges Unveiling The Truth Behind The Anomalies
Another thing nobody warns you about is how DHCP servers handle this range. Many consumer-grade routers default to 192.168.1.0/24. When you switch to 172.16.0.0/24, some older devices that were hard coded with static IPs in the 172.16.x.x space will sit there and refuse to reconnect even after you move them to a new subnet. I spent an afternoon tracking down four network printers that would not pick up addresses on a new /24 because someone had manually assigned them 172.16.0.50 through 172.16.0.53 back in 2014 and never documented it. The solution was not to clear the DHCP lease database. It was to unplug each printer, hold the network reset button for ten seconds, and replug them so they would request a fresh lease. If you are planning a network design that uses 172.16.0.0/12, here is a practical approach that works. Decide how many /24 subnets you think you will need over the next five years. Multiply that by three to account for growth and dead ends. If your number is under 254, you can just use a single /16 like 172.16.0.0/16 and be done with it. The private range is huge, so there is no reason to overcomplicate it early on. Start small. Document everything. Use a consistent naming convention for each VLAN. Write down which /24 is assigned to which floor or function before you start handing out addresses. The biggest pitfall with 172.x.x.x is assuming it behaves differently than 192.168.x.x. It does not. The same rules apply. Same NAT behavior. Same CIDR math. Same broadcast domain limits. The only reason it feels mysterious is that documentation and tutorials favor the more common home router range, so when you hit a problem in 172.16.0.0/16, you cannot find a straight answer online. Try searching for "172.16.0.0/12 RFC 1918" instead of just the IP address, and you will land on the actual spec that governs it.
One more edge case. Some cloud providers and managed hosting companies use 172.16.0.0/12 internally for their backend infrastructure. If you are running a VPN or a site-to-site tunnel and your ISP gives you a public IP that falls in the 172.16.0.0/12 block, your tunnel will fail silently because many VPN implementations treat the entire 172.16.0.0/12 range as local and refuse to route it across the WAN. I ran into this with a client who had a 172.20.0.0/14 internal network and tried to establish an IPSec tunnel to a remote office. The tunnel would negotiate but never pass traffic. The fix was to renumber one side of the tunnel to 10.0.0.0/8 instead. The tunnel came up immediately after. If you want to explore how these ranges work in practice, the best resource is still the original RFC documents. RFC 1918 defines the private address space. RFC 3330 provides additional background. You can find both free on the IETF website. There is no download needed. Just read them directly. The technical content is dense but short enough to get through in one sitting. There are also tools like ipcalc and CIDR calculator that let you test your subnetting against 172.16.0.0/12 without doing the math by hand. These are command line utilities available on Linux and macOS by default. On Windows, you can use the built-in PowerShell cmdlets or download something like SolarWinds Free IP Subnet Calculator. I use ipcalc daily and it cuts my subnet planning time down from about twenty minutes per network to under two minutes.
Get the Full Details
The bottom line is that 172.16.0.0/12 is not mysterious. It is just another chunk of private IP space that gets less attention than 192.168.0.0/16 because most people never touch it. Once you understand the boundaries, the common failures, and the edge cases, it behaves exactly like any other private range. Plan your subnets. Document your assignments. Avoid blanket deny rules on the full /8. And if something breaks, check whether a device has a hardcoded static IP before you assume it is a routing problem.