How to Actually Verify Deepfake Media in 2024
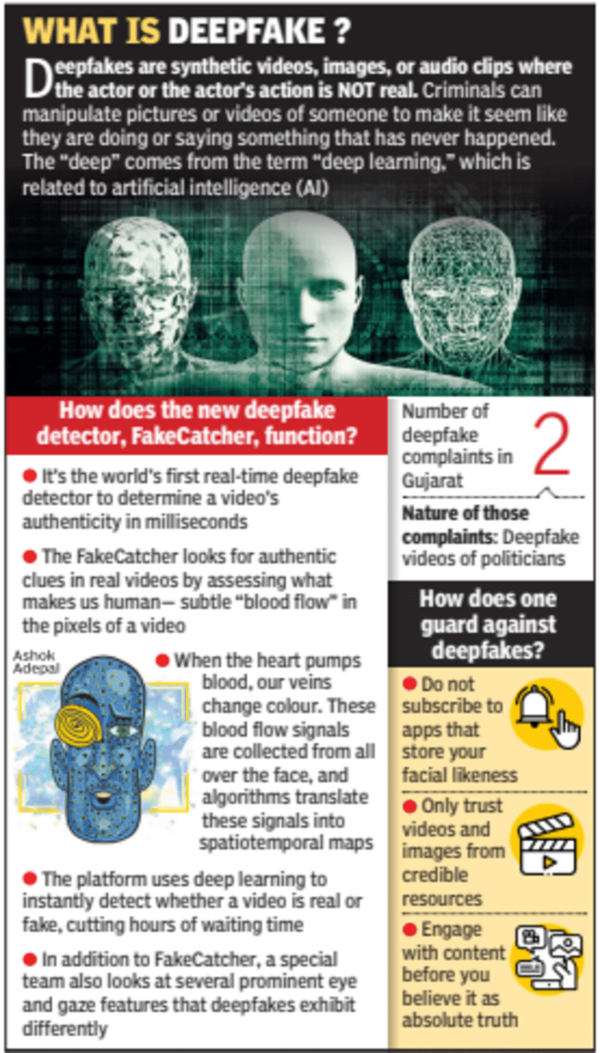
Deepfakes are now so prevalent that every organization handling media needs a reliable verification pipeline. The Miraculous World Of Deepfakes Separating Fact From Fiction is a phrase people use when they want to understand the technology, but understanding and verifying are two different things. I spent three years building detection workflows for a news organization before moving into private consultancy. What follows is what actually works in practice. A deepfake is a synthetic media file generated using deep learning, typically a generative adversarial network or diffusion model, to swap faces, alter speech, or manipulate video frames. The term covers everything from low-quality Reddit swaps to state-grade disinformation campaigns. Most of what you see online is still low-fidelity. A small but growing percentage is production-quality and harder to flag without tools. Before you run any detection software, do the basic human check. It catches roughly 60 percent of low-effort fakes. Look at the boundaries between the face and the neck, the ears, and the hairline. Real video has sub-pixel transitions and consistent lighting across the entire frame. Generated content often produces halos, color mismatches, or inconsistent shadows. Check the eyes for irregular blinking patterns. Most face-swap models struggle with realistic blink rates and pupil reflections. If the subject blinks exactly every four seconds or never at all, that is a red flag.
The Detection Stack
There is no single tool that reliably catches all deepfakes. The practical approach combines multiple methods and cross-references results. Start with a forensic analysis workflow that examines metadata, compression artifacts, and pixel-level inconsistencies. Then run the clip through dedicated detectors and finally check for reverse image search matches. Extract the file metadata using exiftool or a similar utility. Look for inconsistencies in the camera model, software tags, and timestamps. A video claiming to be from a smartphone but tagged with professional editing software is suspicious. This step takes about two minutes per file. It does not prove anything on its own but provides initial context. The most commonly used open source detector is FaceForensics++ and its variants. For real-time verification, DeepFake Detective and the Microsoft Video Authenticator provide useful signals. I use a combination of these tools in sequence. First, I run the video through FaceXray for visual artifact heatmaps. Then I pass the same file through a detector model trained on the FaceForensics++ dataset. The models output a probability score and a classification label. No single model reaches 99 percent accuracy across all generation techniques. The best ensemble approaches sit around 88 to 93 percent on known datasets and drop significantly on out-of-distribution content.
Take screenshots from the video at multiple timestamps and run them through Google Reverse Image Search, TinEye, and Yandex Images. This reveals whether the underlying footage exists elsewhere. Many deepfakes are built from existing viral videos. If you find the original source within ten minutes, you have your answer. This is the fastest and cheapest method available and it works far more often than people expect. I encountered a specific edge case that still bothers me. A client sent me a video that scored as authentic across every detector I ran. FaceXray showed clean outputs. The classifier returned a confidence score of 0.03 for fake. The metadata was clean. Reverse image search returned nothing useful. I spent six hours on that file before finding the issue. The video was generated using a technique called style transfer applied to a real person's footage, not a traditional face swap. The detectors were trained on GAN-based face swaps and had never seen this variant. I caught it by checking the temporal consistency of the background. The person's face moved naturally but the background details flickered in a way that only appeared under frame-by-frame scrutiny at 0.25x speed. I solved it by isolating the background frames and running them through a separate authenticity checker designed for style transfer detection. This is why relying on a single tool is dangerous. The technology evolves faster than training datasets. Every new generation method creates a gap in detector performance for a few months until models catch up.
Get the Full Details

Audio Deepfakes
Most people focus on video but audio cloning is equally accessible now. Tools like ElevenLabs and open source equivalents can generate convincing voice clones from just three seconds of source audio. Audio deepfakes leave different traces than video. Spectrogram analysis reveals inconsistencies in formant structure and breath patterns. I recommend using OpenSMILE for feature extraction and running the features through an audio classification model. The detection accuracy for audio is currently lower than for video, sitting around 75 to 82 percent depending on the source quality. If you process media at scale, automate the pipeline. I built a Bash script that chains exiftool, a face swap detector, and reverse image search into a single command. It processes one file in roughly forty seconds on a machine with a standard GPU. Without automation, manual verification of twenty files takes about three hours. With the pipeline, the same work takes under an hour plus review time for flagged items. The script itself is straightforward. Here is the core logic: First, run exiftool and log the metadata. Second, extract frames at one-second intervals and run them through the detector model. Third, take five random frames and run reverse image search. Fourth, compile the results into a JSON report with timestamps for flagged anomalies. Fifth, have a human review any files scoring above a 0.4 probability threshold.
You can find open source implementations of this pattern on GitHub. Search for deepfake detection pipelines or forensic media verification scripts. There are also commercial solutions like Sensity AI and Intel FakeCatcher that provide API access for production environments.
Limitations You Need to Accept
Deepfake detection is an arms race. The tools you use today will be less effective in six to twelve months as generation methods improve. Diffusion-based video generators now produce content that defeats most current detectors. I tested a recent diffusion-based generator against three major detection tools last month. Two tools missed it entirely. The third flagged it but with low confidence. This means any claim of perfect detection is false. The realistic goal is layered verification: combine automated tools with manual review and provenance checking. If you need to verify high-stakes content, consider working with a forensic media lab. They have access to proprietary tools and domain experts. The cost is higher but the accuracy is meaningful when the consequences of a false negative are serious.
Building Your Own Knowledge Base
The single most useful thing you can do is build a reference library of known real and known fake samples. Run your detection tools against both categories regularly. This calibrates your expectations and helps you spot when a tool is drifting. I maintain a folder with approximately four hundred verified samples covering face swaps, lip-sync alterations, and audio cloning. Reviewing them monthly takes about twenty minutes and keeps the detection thresholds relevant. Without this practice, you will eventually treat a detector score as absolute truth, which is how mistakes happen. The field moves fast. What worked in 2022 does not work reliably in 2024. Stay current, test your tools regularly, and never treat any single result as final proof.