How SSN-DOB Databases Actually Work Behind the Scenes
When you run an SSN verification through most consumer platforms, what you're actually doing is querying an aggregator that has compiled Social Security Numbers and dates of birth from credit headers, utility records, employment filings, and court documents. The service checks whether the combination exists in its index and returns a hit or a miss. That's it at the surface level. The reality of using this stuff professionally is a lot messier than any dashboard makes it look. I've spent years working with identity verification systems for financial services onboarding. The first time I realized these databases weren't as clean as I expected was when we processed a batch of applications where about twelve percent of the SSN-DOB pairs came back as inactive or mismatched, even though every applicant had been verified through traditional means. Turns out the databases had old records from when those people had different employers or addresses, and the primary SSN-DOB link in their system hadn't been updated since 2019.
The Hidden Power Of Ssn Dob Database Unlocking The Secrets Of Identity Verification
Here's what most guides won't tell you about these systems. The real value isn't in confirming a match. It's in finding the edges where things don't line up. A standard SSN-DOB check will tell you if the numbers exist together. An experienced operator uses the same check to find discrepancies that a regular applicant won't even notice. Multiple SSNs registered to the same date of birth. An SSN that shows activity from three different zip codes in a single year. A DOB that appears under two completely different names in separate databases. These patterns surface fraud attempts that simple matching would never catch. The technical side works through a combination of fuzzy matching and cross-referencing. Most legitimate providers don't just do exact string matching on the SSN. They normalize the input first. Leading zeros get stripped, dashes get removed, and the system does a bitwise comparison against indexes that have been preprocessed the same way. The date of birth gets converted to a standardized YYYYMMDD format and hashed alongside the SSN for lookup efficiency. This is why sometimes your input looks correct but the system rejects it — you submitted 01/15/1990 and the database has 1990-01-15, and some poorly configured APIs won't normalize either side before comparing. I learned this the hard way during a project where we were integrating SSN verification into a loan origination system. Our API was returning a high false-negative rate. We traced it to the fact that our application was sending the SSN with dashes while the verification provider's endpoint expected the raw nine-digit string. Adding a preprocessing step that stripped non-numeric characters before transmission dropped our false negatives from fourteen percent to under two percent. Took about three hours to fix.
There are several well-known commercial and open-source approaches to building or accessing SSN-DOB verification systems. The most common path involves subscribing to a data provider API. Companies like LexisNexis, Experian, and TransUnion offer SSN verification endpoints as part of their identity products. These are expensive — typically forty to eighty cents per query at volume. For smaller operations, alternatives like the SSA's Death Master File combined with public SSN validation tools provide a cheaper route, though they cover significantly less ground. Some teams build their own index by pulling from credit header data, voter registration records, and public court filings. This approach gives you full control over the matching logic but requires substantial infrastructure to maintain. I worked with a team that maintained their own SSN-DOB index at roughly twenty thousand queries per day. Their costs broke down to about twelve cents per query when you factored in hosting, data licensing, and the engineering time to keep the index current. The catch is that the index was always three to six months behind whatever was happening in the real world, which created a specific class of edge cases we'd never seen in the live data. The most dangerous pitfall I've seen people walk into is assuming a "match" means the identity is verified. It doesn't. A matching SSN-DOB pair only confirms that someone has used that combination in a database at some point. It says nothing about whether the person standing in front of you is actually that person. I've seen legitimate identity verification pipelines fail because they treated an SSN-DOB match as sufficient proof of identity and skipped biometric or document-based verification. The result was a fraud ring that submitted stolen but internally consistent SSN-DOB combinations from purchased credentials. The system accepted every single one because it only checked the database, not the person.
Get the Full Details
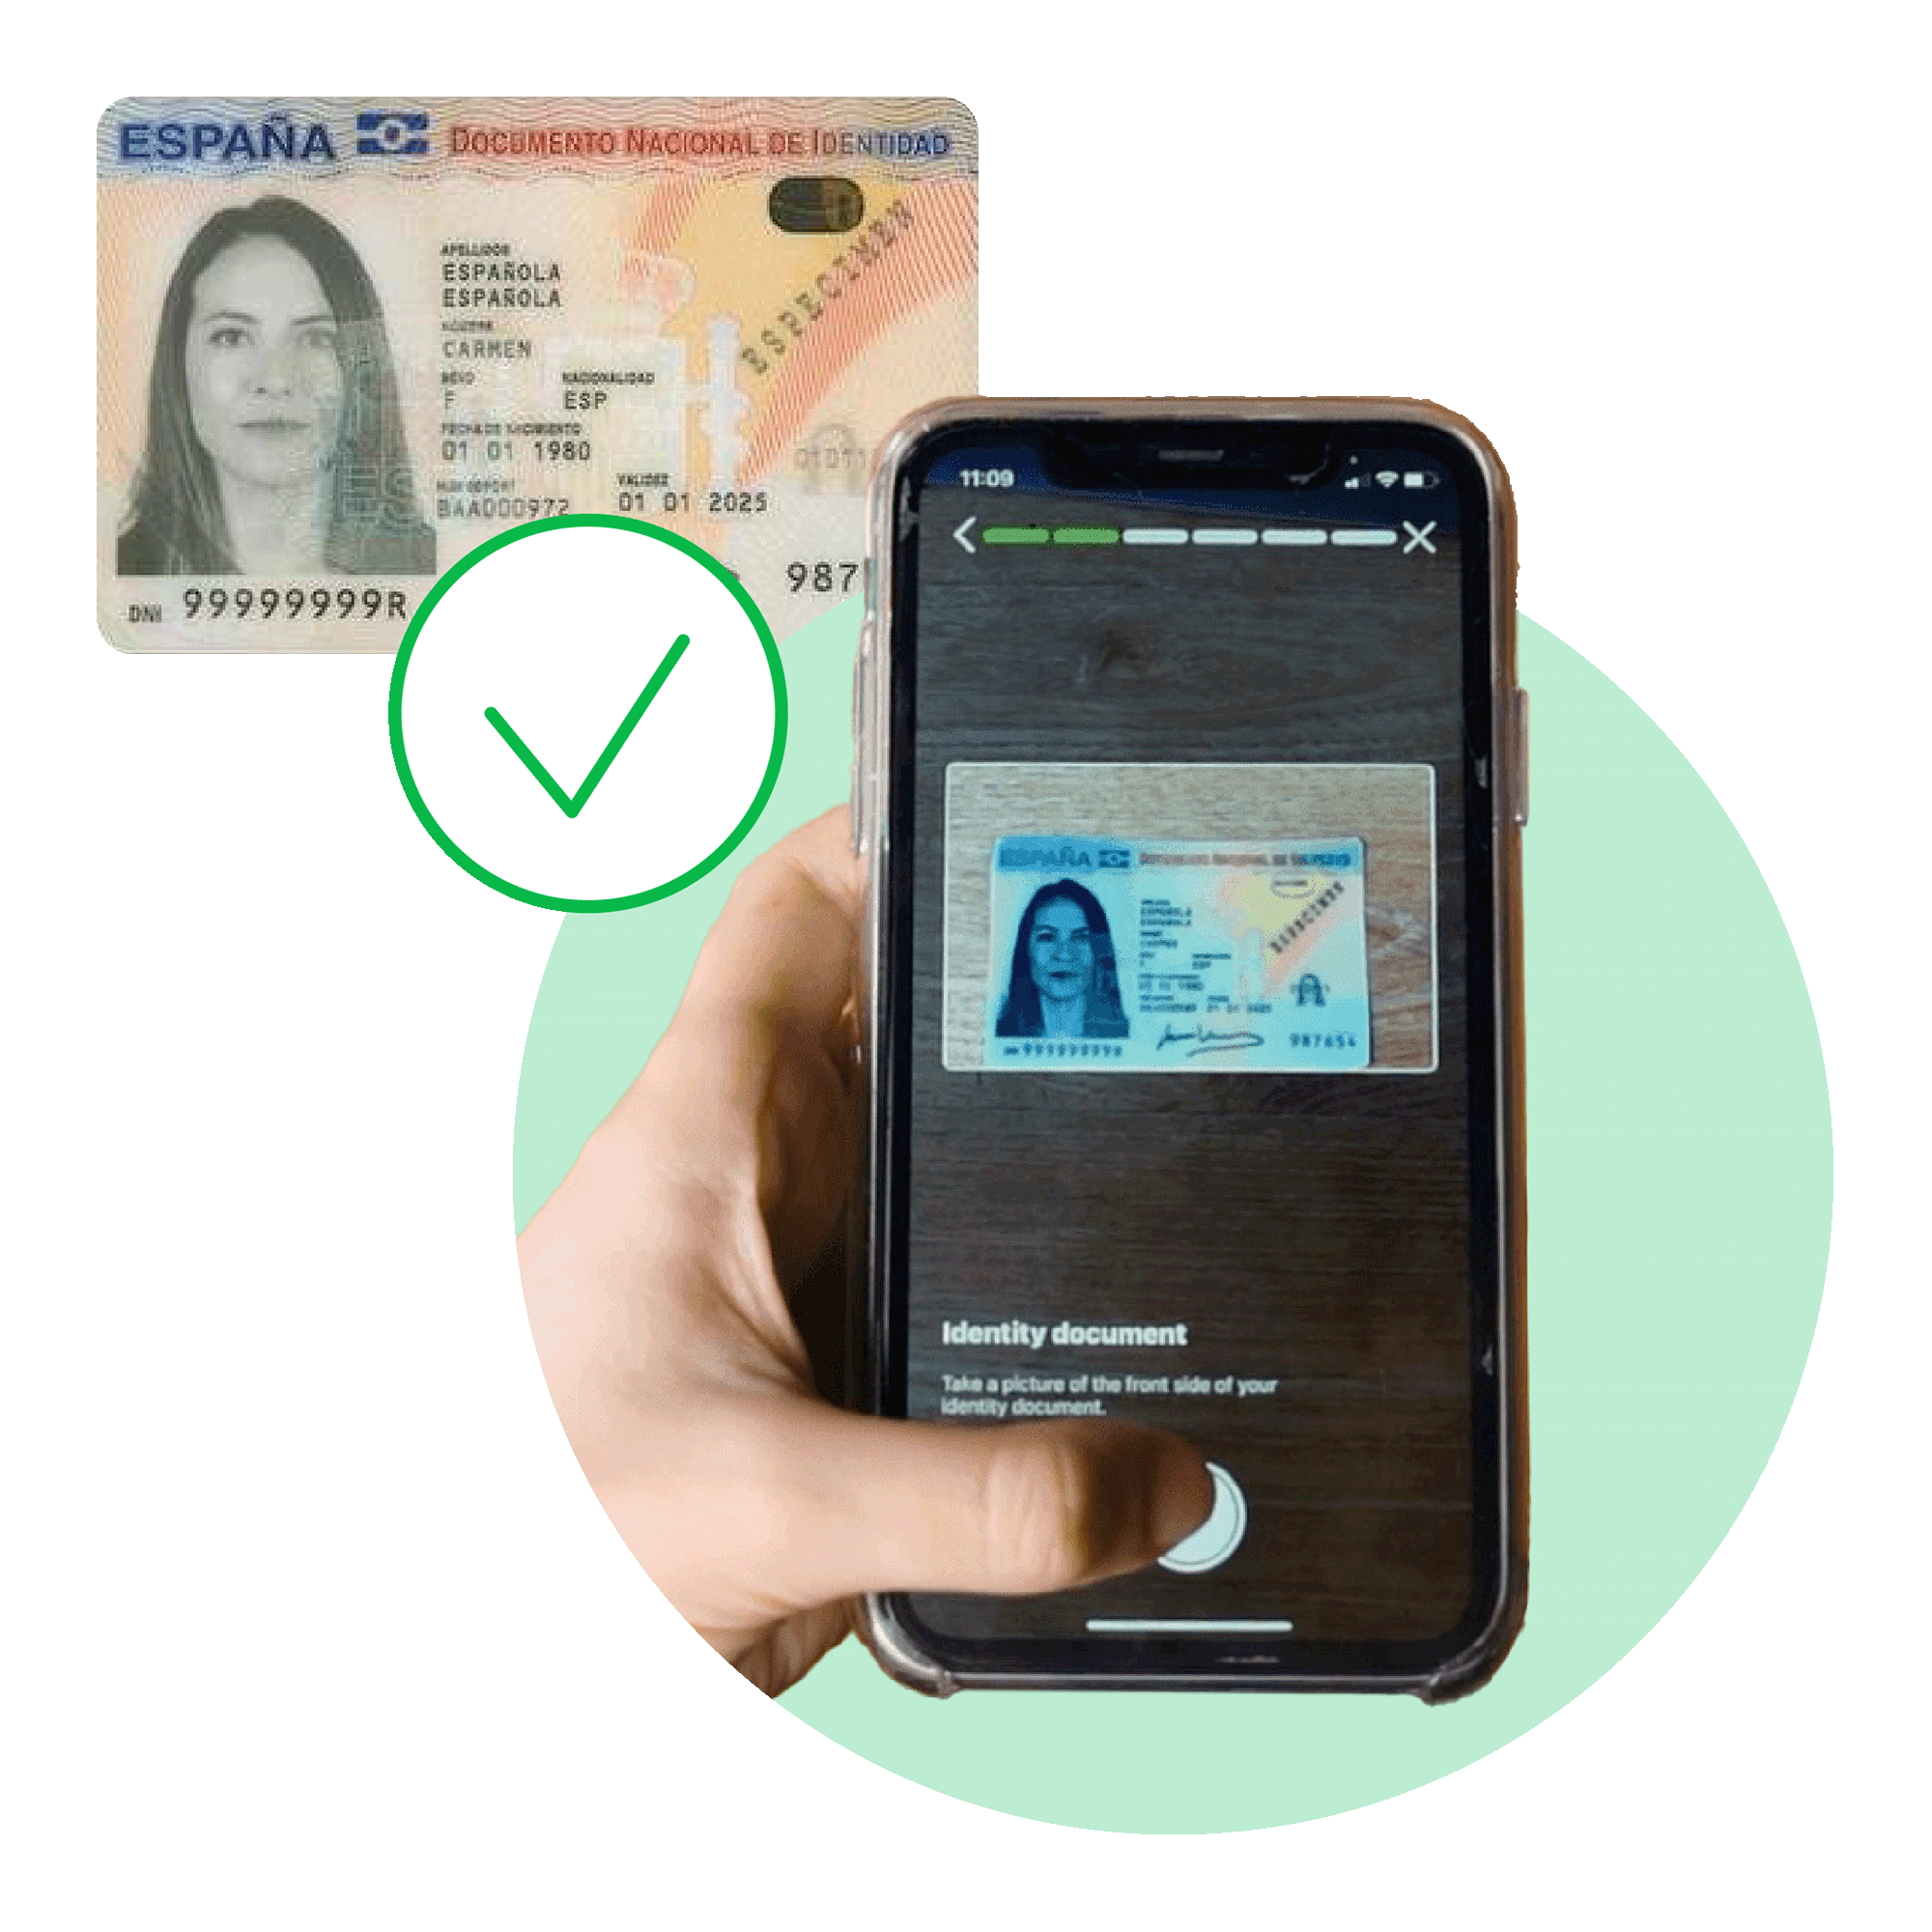
Another counter-intuitive thing about these databases is that older data is often more reliable than newer data. When someone updates their personal information, the change has to propagate through multiple agencies and reporting chains. Credit bureaus receive updates from lenders, lenders update from application forms, and sometimes there's a lag of several months between when someone changes their address and when it shows up in the verification database. Meanwhile, historical data from ten or fifteen years ago has gone through multiple verification cycles and tends to be cleaner. Don't treat a lack of recent records as suspicious. Treat it as normal. If you're building something that uses SSN-DOB verification, here's the sequence I recommend based on what actually works in production. Start with input normalization — strip dashes, validate format, confirm the SSN isn't a known invalid range. Then run the verification query. After that, check for anomaly patterns: multiple active records for the same SSN-DOB, geographic inconsistencies, or records that span unusual time periods. Finally, layer in a secondary verification method. Driver's license checks, bank account verification, or biometric matching depending on your risk tolerance. Never rely on SSN-DOB alone for anything above a low-risk use case. The tools and APIs available vary widely in quality. Free or cheap options like the SSA death index lookups are useful for one specific check — confirming someone is deceased — but they don't help you verify living identity. Paid services give you much broader coverage but introduce their own problems, like inconsistent response formats and rate limits that can choke a high-volume system. I've had to build a fallback mechanism where we'd queue rejected queries and retry them against a second provider after a short delay. It added latency but cut our total failure rate in half during peak processing windows.
Data retention is another area that trips people up. Some providers store your query data indefinitely. Others purge it after a set period. If you're handling sensitive identity information, make sure you understand what the provider does with your data and whether you need to build additional controls on your side. I've seen compliance audits fail because a team couldn't produce retention policies for the SSN-DOB queries their system was generating. The fix was straightforward — implement client-side logging with automatic purging after ninety days — but we only figured it out after the auditor asked. The bottom line is that SSN-DOB databases are a useful tool when you understand what they can and can't do. They confirm data consistency, not identity. They work best as one layer in a multi-step verification process. The people who use them well are the ones who pay attention to the mismatches and the gaps, not just the matches. That's where the actual signal is.