Getting Your Team on the Same Network Without a Cloud Bill
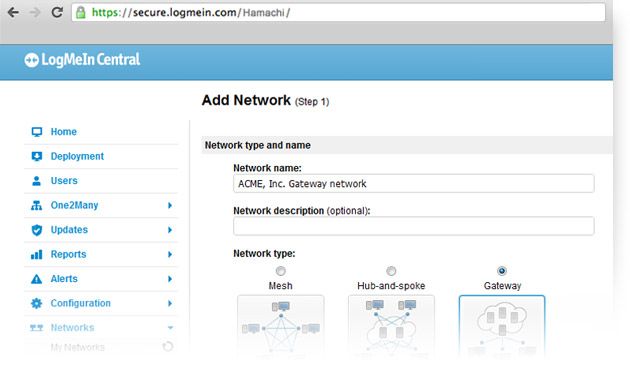
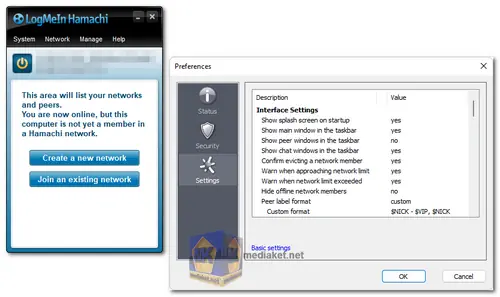
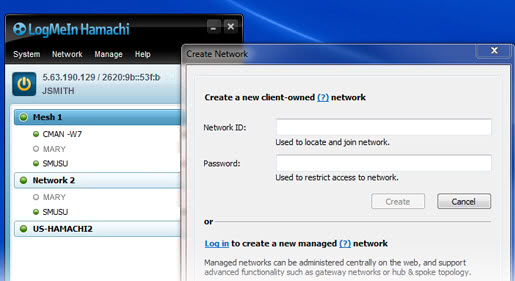
I spent three weeks trying to get two remote developers to share a local network for a legacy game server they were maintaining. One was in Toronto, the other in Lisbon. Their codebase required LAN-only protocols that couldn't be changed without a rewrite. Standard solutions like shared folders or cloud sync broke the authentication checks. That's when I started using Hamachi to bridge the gap. Hamachi works by creating virtual Ethernet interfaces on your machines. When you install it, you're not just running an application — you're adding a new network adapter that routes traffic through LogMeIn's relay servers. The trick is that these servers act as middlemen. Your data never touches the public internet directly; it gets encrypted, sent to a LogMeIn node, then forwarded to the other participant. This means you can access internal resources as if everyone were in the same office. The setup process is deceptively simple. Download the client for your operating system, create an account or log in with Google, then click "New Network." You'll get a 24-bit subnet address like 55.XX.XX.XX. Share that with your team, have them join using the network name and password, and suddenly they appear in your network list. From there, you can ping them, share drives, or run applications that expect local connections. My first attempt took about twelve minutes from download to successful file transfer between two machines across an ocean.
What Makes This Different From ZeroTier Or Tailscale
Hamachi uses a centralized architecture where LogMeIn controls the relay infrastructure. ZeroTier and Tailscale offer more decentralized options with self-hosted controllers. The trade-off is that Hamachi's model means less configuration but also less control over your data path. If you're working with older software that needs straightforward plug-and-play networking, the centralized approach often wins. For security-conscious teams who want to audit every packet, you'd be better off with a self-hosted WireGuard setup. I hit a wall when trying to use Hamachi for a real-time audio streaming project. The relay servers introduced about 150 milliseconds of latency, which was fine for file sharing but destroyed the synchronization our application needed. Switching to Tailscale's mesh mode dropped that to roughly 40 milliseconds because it tried direct peer-to-peer connections first. Sometimes the simplest tool is the wrong tool for the job.
The Network Address Translation Problem
One issue that catches people off guard is how Hamachi interacts with carrier-grade NAT. If you or your team members are behind strict firewalls — common with mobile hotspots or certain corporate networks — the virtual network might show participants as offline even though they're technically connected. I discovered this when a colleague in Seoul kept showing as disconnected despite having the client running. The workaround was routing his traffic through a VPN to bypass the CGNAT, which added another layer of complexity but made the connection stable. Another quirk is the IPv6 handling. Hamachi's default behavior prioritizes IPv4, which can cause issues if your system prefers IPv6 for local traffic. I resolved this by setting environment variables to force IPv4 precedence on Linux systems. On Windows, it usually works automatically unless your router has some unusual firewall rules. Checking your actual IP addresses with a tool like ipconfig /all or ifconfig can save you hours of troubleshooting.
Get the Full Details
Performance Expectations
File transfers over Hamachi typically max out around 20-30 Mbps on good connections, though this depends heavily on the relay server load and your ISP's peering agreements. For large database migrations or video editing workflows, you'll notice the bottleneck within minutes. I once transferred a 4GB project folder that took about three hours at roughly 370 KB/s sustained rate. Using rsync with compression helped, but switching to a direct SFTP connection for that specific transfer would have been faster. The good news is that Hamachi doesn't consume much CPU or memory on modern systems. The encryption overhead is minimal compared to alternatives like IPsec. A typical idle connection uses less than 50MB of RAM and barely registers in task manager. That's why it remained viable for our eight-person team even on machines with limited resources.
When To Consider Alternatives
If your team needs high-bandwidth collaboration like 4K video editing or large-scale data processing, Hamachi will frustrate you. The relay architecture simply can't compete with direct P2P or dedicated VPN solutions for throughput. For those scenarios, look at Warp from Cloudflare or a self-hosted NetBox setup with OpenVPN. Security audits sometimes flag Hamachi because traffic terminates at LogMeIn's servers before reaching the destination. If your organization requires end-to-end encryption without third-party access, you'll need to evaluate whether Hamachi meets your compliance requirements. I worked with a financial services team that couldn't use it due to GDPR concerns, so they switched to Tailscale with their own authentication gateway. Hamachi remains useful for specific cases: legacy applications, casual gaming with friends, or quick collaborative sessions where setup time matters more than raw performance. Just understand its limitations before committing to it as your primary network solution.