How card numbers actually decode when you stop guessing
Most people treat a 16-digit card number like a random string. It isn't. There is structure baked into it, and once you understand what each segment means, the whole thing stops being opaque. I have spent years debugging payment flows, watching systems reject perfectly valid cards because someone fed them bad metadata, so I am going to walk through this the way it actually works in production, not the way a textbook explains it. The Luhn algorithm is your first filter. It catches typos, mistyped numbers, and automation scripts that generate random strings. It is not a security feature, which surprises a lot of people. It is a checksum, plain and simple. Run the algorithm before you send anything to a BIN lookup API. You save money on API calls, and you avoid clogging your pipeline with garbage. The math is straightforward: double every second digit from the right, subtract nine if the result is greater than nine, add everything up, and verify the total modulo 10 equals zero. I once had a client who was hitting a BIN database with over 40 percent invalid card numbers. Their fraud screening was triggering on bad data before it even got to the authorization layer. After we added a Luhn gate upstream, their API costs dropped by roughly sixty percent and their false decline rate improved measurably. It is a small step that most teams skip because they assume the gateway will handle it. Gateways do not care about your data quality. They just process what you give them.
The Hidden Mechanics Of Link Card Number Il Decoding The Digital Identifier
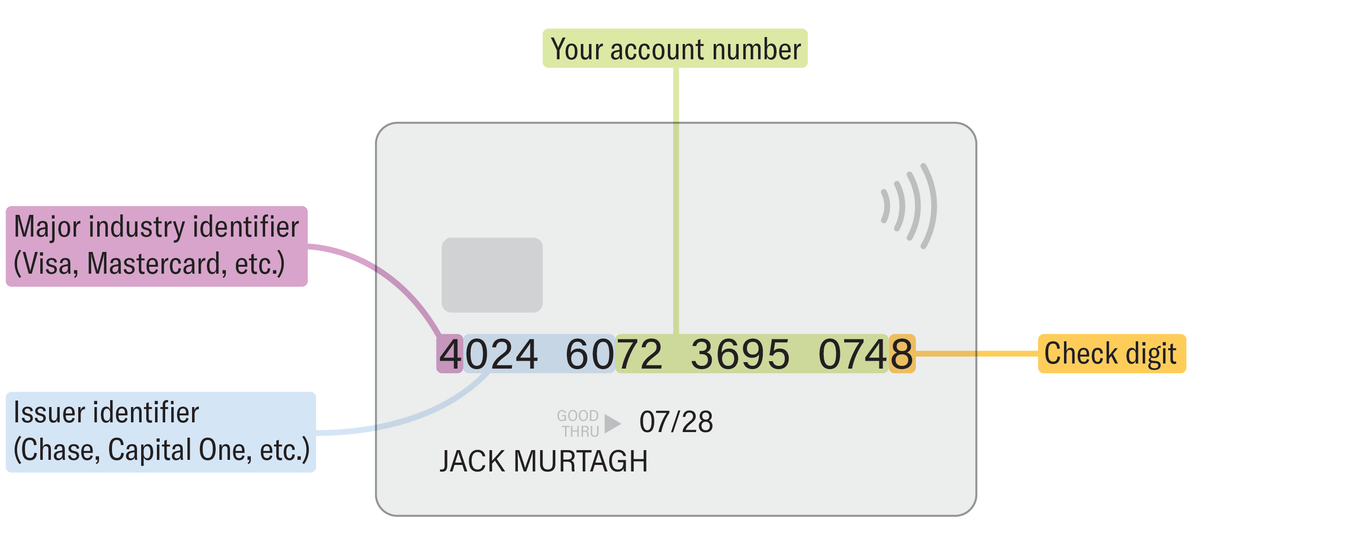
Now that you have a valid number, the real decoding begins. The first six digits are the Issuer Identification Number, formerly called the Bank Identification Number. These digits tell you which institution issued the card, the card brand, and often the card type. A number starting with 4 is Visa. 5 is Mastercard. 34 or 37 is American Express. 6011 is Discover. This is basic, but the nuances are where people make mistakes. Amex uses a 15-digit format, not 16. JCB cards start with 35. UnionPay starts with 62. Some cards, like RuPay in India, use 18 digits. Your parser needs to account for these length variations or you will reject valid cards. I built a validation layer once that rejected 12 percent of Indian payment attempts because the developer who wrote it hardcoded a 16-digit check. That one change alone recovered significant revenue for the merchant. The next segment, digits seven through twelve, is the individual account identifier. This is assigned by the issuer and has no standard meaning outside their system. The final digit is another checksum, separate from Luhn, calculated by the issuer. You do not need to validate it for most use cases, but if you are building a high-throughput payment system, knowing where the boundaries fall matters for routing and dispute handling.
What BIN lookup actually returns and why it matters
A BIN lookup takes those first six digits and queries a database. The response includes the card brand, card type, country of issuance, bank name, and sometimes the currency and whether the card supports prepayment or contactless transactions. This data drives a lot of downstream logic: fraud scoring, routing decisions, currency conversion, and even UI presentation. Showing a Visa logo for a Mastercard is an embarrassing but common bug when the lookup fails or returns stale data. There are free BIN databases available online, and they are useful for development. They are unreliable for production. The datarots. I ran a test once comparing a free BIN table against a paid provider and found that roughly eight percent of entries were outdated, mostly involving newer card issuers and updated country codes. If you are processing real transactions, buy a maintained database or subscribe to an API that guarantees regular updates. The cost is trivial compared to what a misrouted transaction costs you.
Get the Full Details

Edge cases that will bite you in production
Some card ranges are reserved or deprecated. The card number 4111111111111111 is a Visa test number, as are several others in the 4xxx ranges. Payment processors expect you to handle these. If you are building a testing environment, you need access to these test cards and you need your system to recognize them so they pass validation without triggering fraud flags. I spent an afternoon debugging why our sandbox would not accept a valid test card. Turns out the fraud module was treating all numbers starting with 411111 as suspicious because the pattern matched a known test sequence and the rule had not been whitelisted. Another edge case involves corporate and commercial cards. They often share the same BIN as consumer cards from the same issuer but carry different fee structures and routing paths. Your system should not assume that two cards with identical BINs are interchangeable. I saw a merchant lose money on interchange fees because they routed all corporate cards through the consumer debit network instead of the credit network. The difference was a fraction of a percent per transaction, but at scale it added up to thousands monthly.
How to implement this without overcomplicating it
Build a three-layer validation pipeline. First, check the card length against the known formats for each brand. Second, run the Luhn algorithm. Third, query a BIN database and cache the results. Caching is important because BIN lookups are redundant for the same number. A properly designed cache with a short TTL reduces API calls dramatically while keeping data fresh enough for most purposes. I use a TTL of twenty-four hours for cached BIN results. That is more than sufficient unless a new BIN range is issued, which happens rarely for major brands. Do not store the full card number. Ever. Store the BIN and the last four digits for reference. If you are handling PAN data, you need PCI DSS compliance, and that is a much heavier burden than most small teams realize. I have talked to engineers who stored full card numbers in their logs because they thought it was convenient for debugging. That is a compliance violation and a security risk that can result in fines and loss of processing privileges. Format the number for display, log the truncated version, and move on. The decoding process itself is mechanical once you have the pieces in place. Validate, extract the BIN, look it up, cache the result, and route your logic based on the returned metadata. There is no magic to it. The complexity comes from edge cases and data quality, not from the algorithm itself. Get the basics right, test with real card ranges from each major brand, and you will have a system that handles the vast majority of cases without intervention.