Getting Past the Basics of Workday User Management
Workday Um sounds straightforward on paper. You assign roles, map workers to processes, and hope the integration holds together. The reality is messier. Most organizations treat User Management as an afterthought, something you configure once and forget. That approach breaks down within six months as headcount changes, role rotations, and cross-border compliance requirements pile up. I spent three years cleaning up a particularly broken deployment where someone had hardcoded worker IDs into access control policies instead of using dynamic role assignments. When a acquisition merged in two European divisions, every single policy had to be manually rewritten. Took me about four weeks to fix what should have taken two days if they'd just used role variables properly.
The Hidden Engine Of HR How Workday Um Is Redefining The Employee Lifecycle
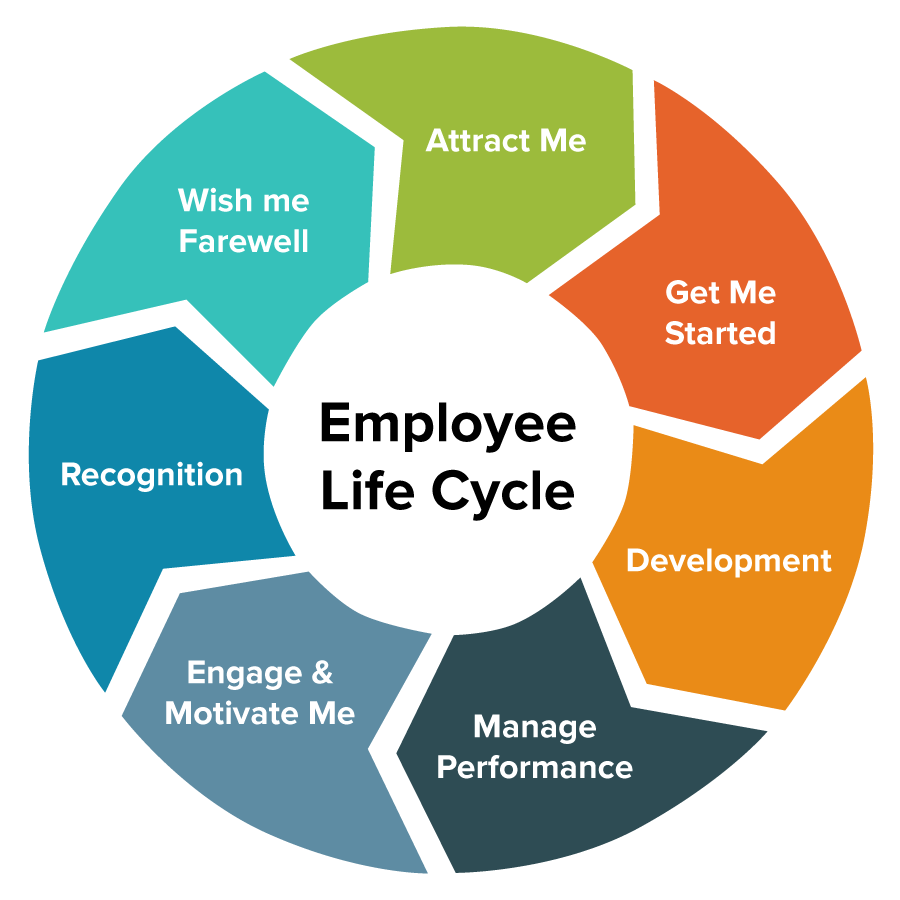
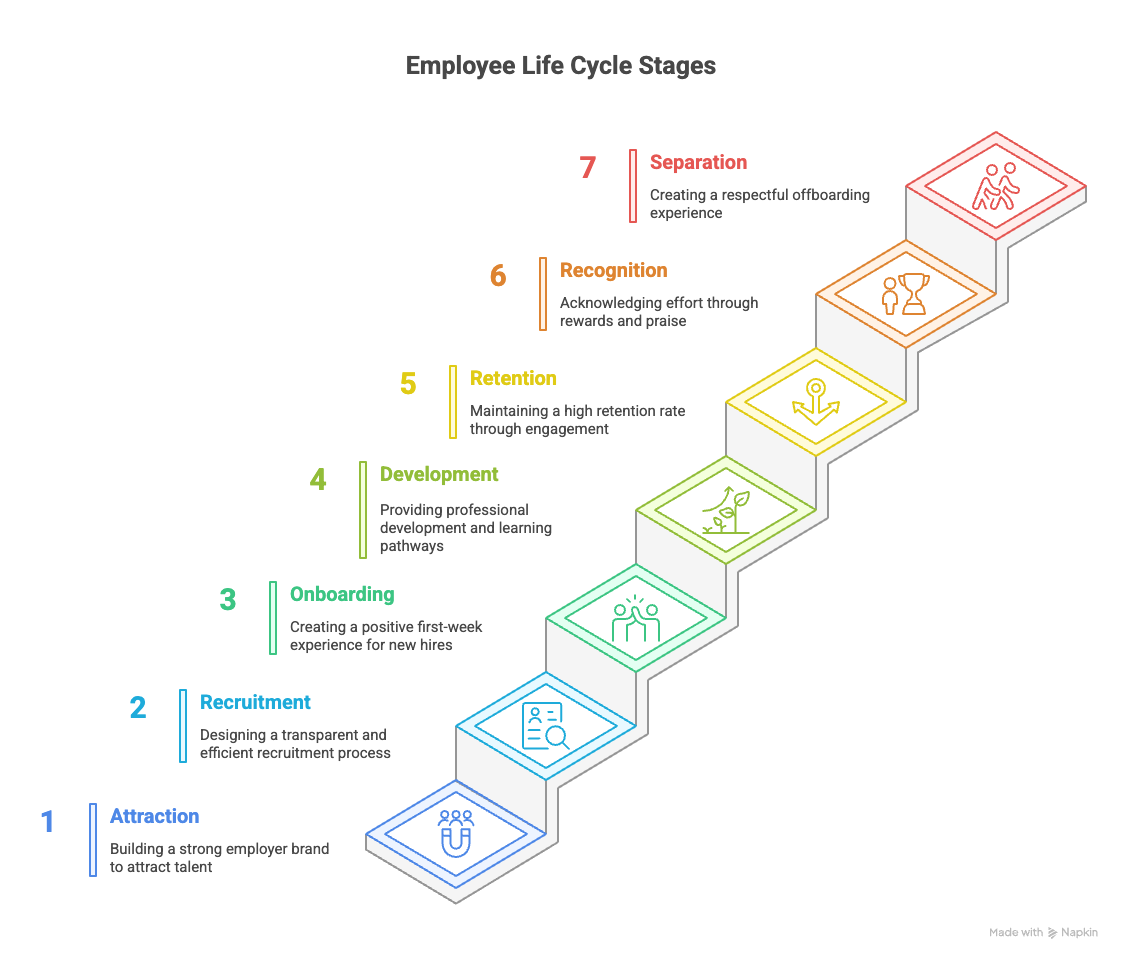
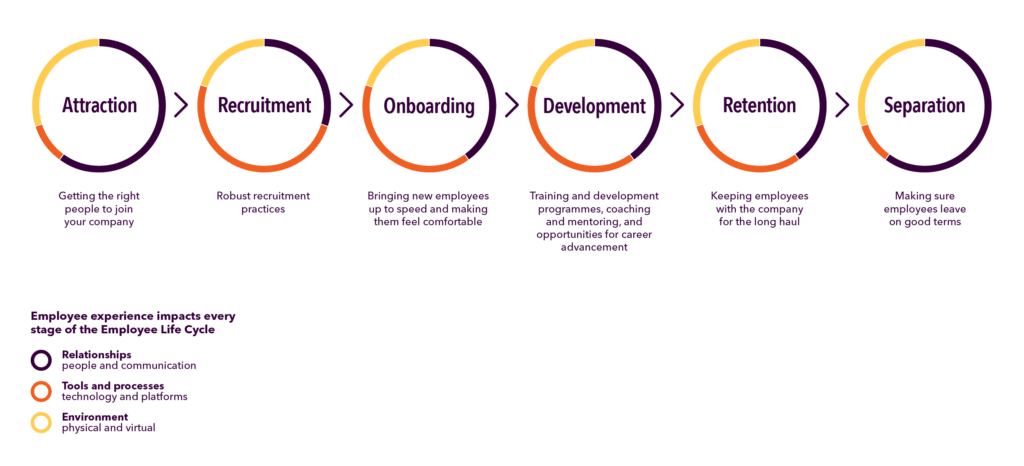
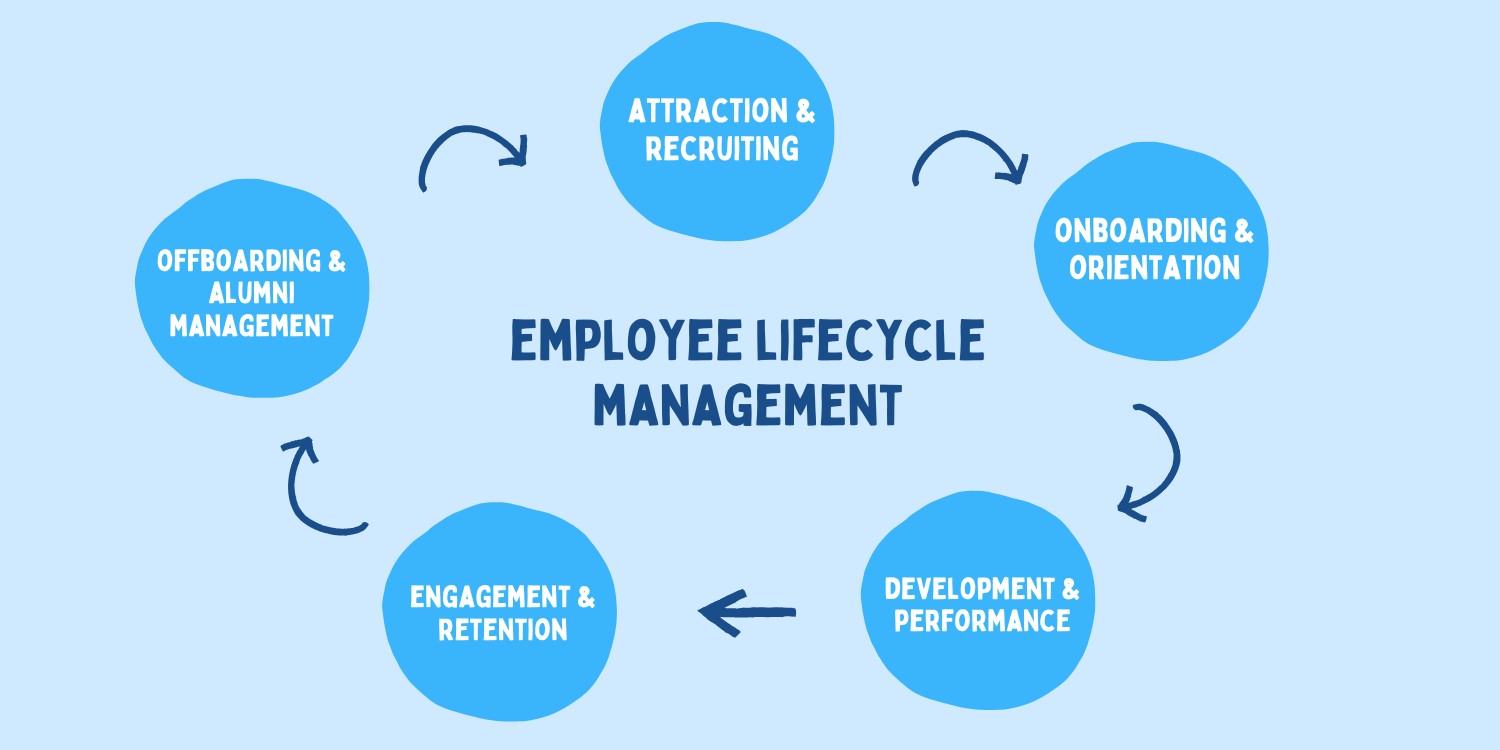
People understand Workday as a payroll system or an applicant tracker. They rarely see the User Management layer underneath everything. It controls who sees what, when they see it, and how data flows between modules. Get this layer wrong and you are not just dealing with permission errors. You are dealing with compliance gaps, audit failures, and frustrated HR business partners who cannot process a simple transfer. The employee lifecycle in Workday is not a linear path from hire to retire. It is a branching network of events, each triggering different downstream actions based on your configuration. A termination in one country might suppress benefits enrollment in another. A contractor conversion can silently break access if the worker type change does not cascade to the correct role mappings. Most teams miss the connection between Worker Type and Role Assignment rules. When a contingent worker converts to a regular employee, Workday does not automatically inherit the same access patterns unless you build that bridge explicitly. I learned this the hard way during a client rollout where converted contractors retained their old temporary access for fourteen months because the automated workflow never fired the role recalculation event.
What Actually Happens When You Configure Access Correctly
Start with the foundational structure: Business Group, Organization, and Location. These three objects form the hierarchy that access control policies reference. If your org structure does not match how HR actually operates, your policies will either be too broad or too restrictive. Role Assignment is where most people stop understanding things. There are two types. Standard roles apply to workers directly. Profile-based roles apply to a profile that can be assigned to multiple worker types. The difference matters when you are managing a blended workforce of employees, contractors, and interns. Put them all in standard roles and you lose the ability to filter by engagement type efficiently. The second thing people misunderstand is Supertype access. You can define access rules that apply across the entire organization or within a business group. Cross-business-group access requires explicit configuration. If you do not set this up, a recruiter in one business group cannot view candidates imported by another group, and nobody notices until they try to approve a requisition and get an access denied error.
Get the Full Details
A Real Problem I Hit Recently
Last quarter I worked with a healthcare client who needed to restrict patient data access to specific job families while allowing managers to view aggregate reports. The requirement seemed simple. Configure a security role with a custom field filter on Patient Access Permission, assign that role to the relevant job families, and you are done. It was not done. The problem was that Workday evaluates security at two levels: object level and field level. The object level controlled whether a user could access the Patient record at all. The field level controlled which fields they could see. I had configured the field filter correctly but the object filter was missing. Users who should have been locked out entirely could still see the patient table, just with most columns blank. This meant they could identify that a patient existed and when the record was last updated, even though they could not see the clinical data. The fix required adding a Supertype Security Role with a Domain Filter that restricted the Patient Access Permission domain to users whose Department matched specific values. I built this using a dynamic assignment rule based on the worker's department custom field rather than hardcoding department IDs, which would have required constant updates whenever the org chart changed.
What Beginners Miss About Integration Between Modules
Workday User Management does not operate in isolation. It connects to Learning, Recruiting, Compensation, Absence Management, and Time Tracking. Each of these modules has its own role catalog and its own permission model. The integration points are where most failures occur. Recruiting uses candidate profiles, not worker profiles. When a candidate becomes a worker, their recruiting data migrates, but the security context does not fully carry over. I have seen this cause situations where a new hire could access the recruiting dashboard for three months after starting because their candidate profile security was still active and overlapping with their new worker role. The cleanup required a manual recalculation of all role assignments for new hires in the affected business groups. Compensation visibility is another area that trips people up. Managers see compensation data for direct reports, but Workday also supports matrix reporting and project-based reporting structures. If your organization uses a hybrid model where someone reports to both a line manager and a project lead, you need to configure both reporting relationships explicitly in the role assignment. Otherwise, the project lead will not see compensation data for team members they manage operationally.
Downsides You Should Know About Before You Start
Workday Um is not a tool you can set and forget. It requires ongoing maintenance. Role assignments accumulate over time. Workers move between organizations. Business groups restructure. The system does not automatically clean up stale assignments. Without a quarterly audit process, you will develop role creep where users accumulate permissions from previous roles that no longer apply to their current position. The platform also has limitations with bulk operations. Updating role assignments for more than two thousand workers in a single batch often triggers timeout errors. I typically break these into chunks of five hundred with a ten-minute gap between runs. It is slower than you would expect, but it prevents the background task queue from backing up, which affects other scheduled processes running simultaneously. Another practical limitation is the reporting. Workday delivers some standard reports for user management, but none of them give you a clean view of role drift over time. You have to build custom reports combining the Security Role Assignment table with the Worker table and a date range filter. This is doable but it requires SQL knowledge or a consultant to set up initially.
When You Should Look Elsewhere
If your organization has fewer than five hundred workers and does not operate across multiple legal entities, Workday User Management may be overkill. The administrative overhead of maintaining role assignments and security policies often exceeds the value for smaller deployments. In those cases, a simpler system like BambooHR or Gusto handles the core lifecycle needs without the complexity. Similarly, if you need real-time access provisioning tied to an internal ITSM tool, Workday is not built for that level of automation without extensive customization. Some organizations pair Workday with a middleware solution like SailPoint or Okta to handle the provisioning workflow, but that adds cost and maintenance burden that may not be justified. There is also the question of data residency. If you operate in the EU and need strict data localization for certain employee records, Workday Um alone does not solve this. You need to combine it with regional data center configuration and field-level encryption settings that are available only in specific premium packages. Make sure you verify this before purchasing.
Practical Steps for a Clean Implementation
Map your current role structure against your org chart before touching the system. If your business groups do not align with how reporting lines actually work, everything downstream will be misconfigured. I recommend building a cross-reference spreadsheet showing each business group, the roles assigned within it, and the expected access patterns for each role type. Use dynamic assignment rules wherever possible. Do not hardcode worker IDs or job IDs into your security policies. These values change. Dynamic rules based on location, department, or engagement type survive reorganizations without requiring policy updates. Document every role assignment change. Workday provides an audit log, but it is not user-friendly for non-administrators. Maintain a separate change log that records who made the change, why it was made, and what the effective date is. This becomes critical during audits and when troubleshooting access issues months later.
Run a test cycle before going live. Create a small group of test workers with various role combinations and verify that each one can only access what they should. Check both positive and negative cases. Test that a worker moved to a different organization loses access to the old one and gains access to the new one. This step catches eighty percent of misconfigurations before they reach production. The employee lifecycle in Workday is only as strong as the User Management layer underneath it. Most organizations treat this as a technical detail. The ones that invest in getting it right spend less time fixing permission errors and more time using the data for strategic decisions. That difference shows up within the first year of deployment.