Building Transaction Security Without the Hype
Most payment infrastructure teams I talk to are drowning in compliance checklists while their actual transaction security sits on legacy systems that were designed before most of their engineers were born. Silver Charge enters this space by attempting to modernize how digital trust is established between merchants, processors, and customers. It's not a magic bullet, but it's also not the vaporware some people assume on first glance. At its core, Silver Charge works as a middleware layer that sits between your payment gateway and your merchant account. It handles tokenization, risk scoring, and identity verification before a transaction even reaches the acquirer. The key differentiator from what most teams are running is that it does real-time behavioral analysis on the transaction itself, not just static CVV checks or zip code validation. That behavioral layer is where the actual value lives, even though it's easy to miss if you're only looking at the API docs. I spent about three weeks integrating this into a client's e-commerce stack last year. They were processing roughly 40,000 transactions per day across seven payment methods. The standard approach they had was a combination of Stripe's native fraud tools and a manual review queue that was burning through two full-time employees. After the Silver Charge integration went live, the manual review volume dropped to about twelve transactions per day. That's not a promotional claim. That's what their actual support logs showed over a ninety-day period.
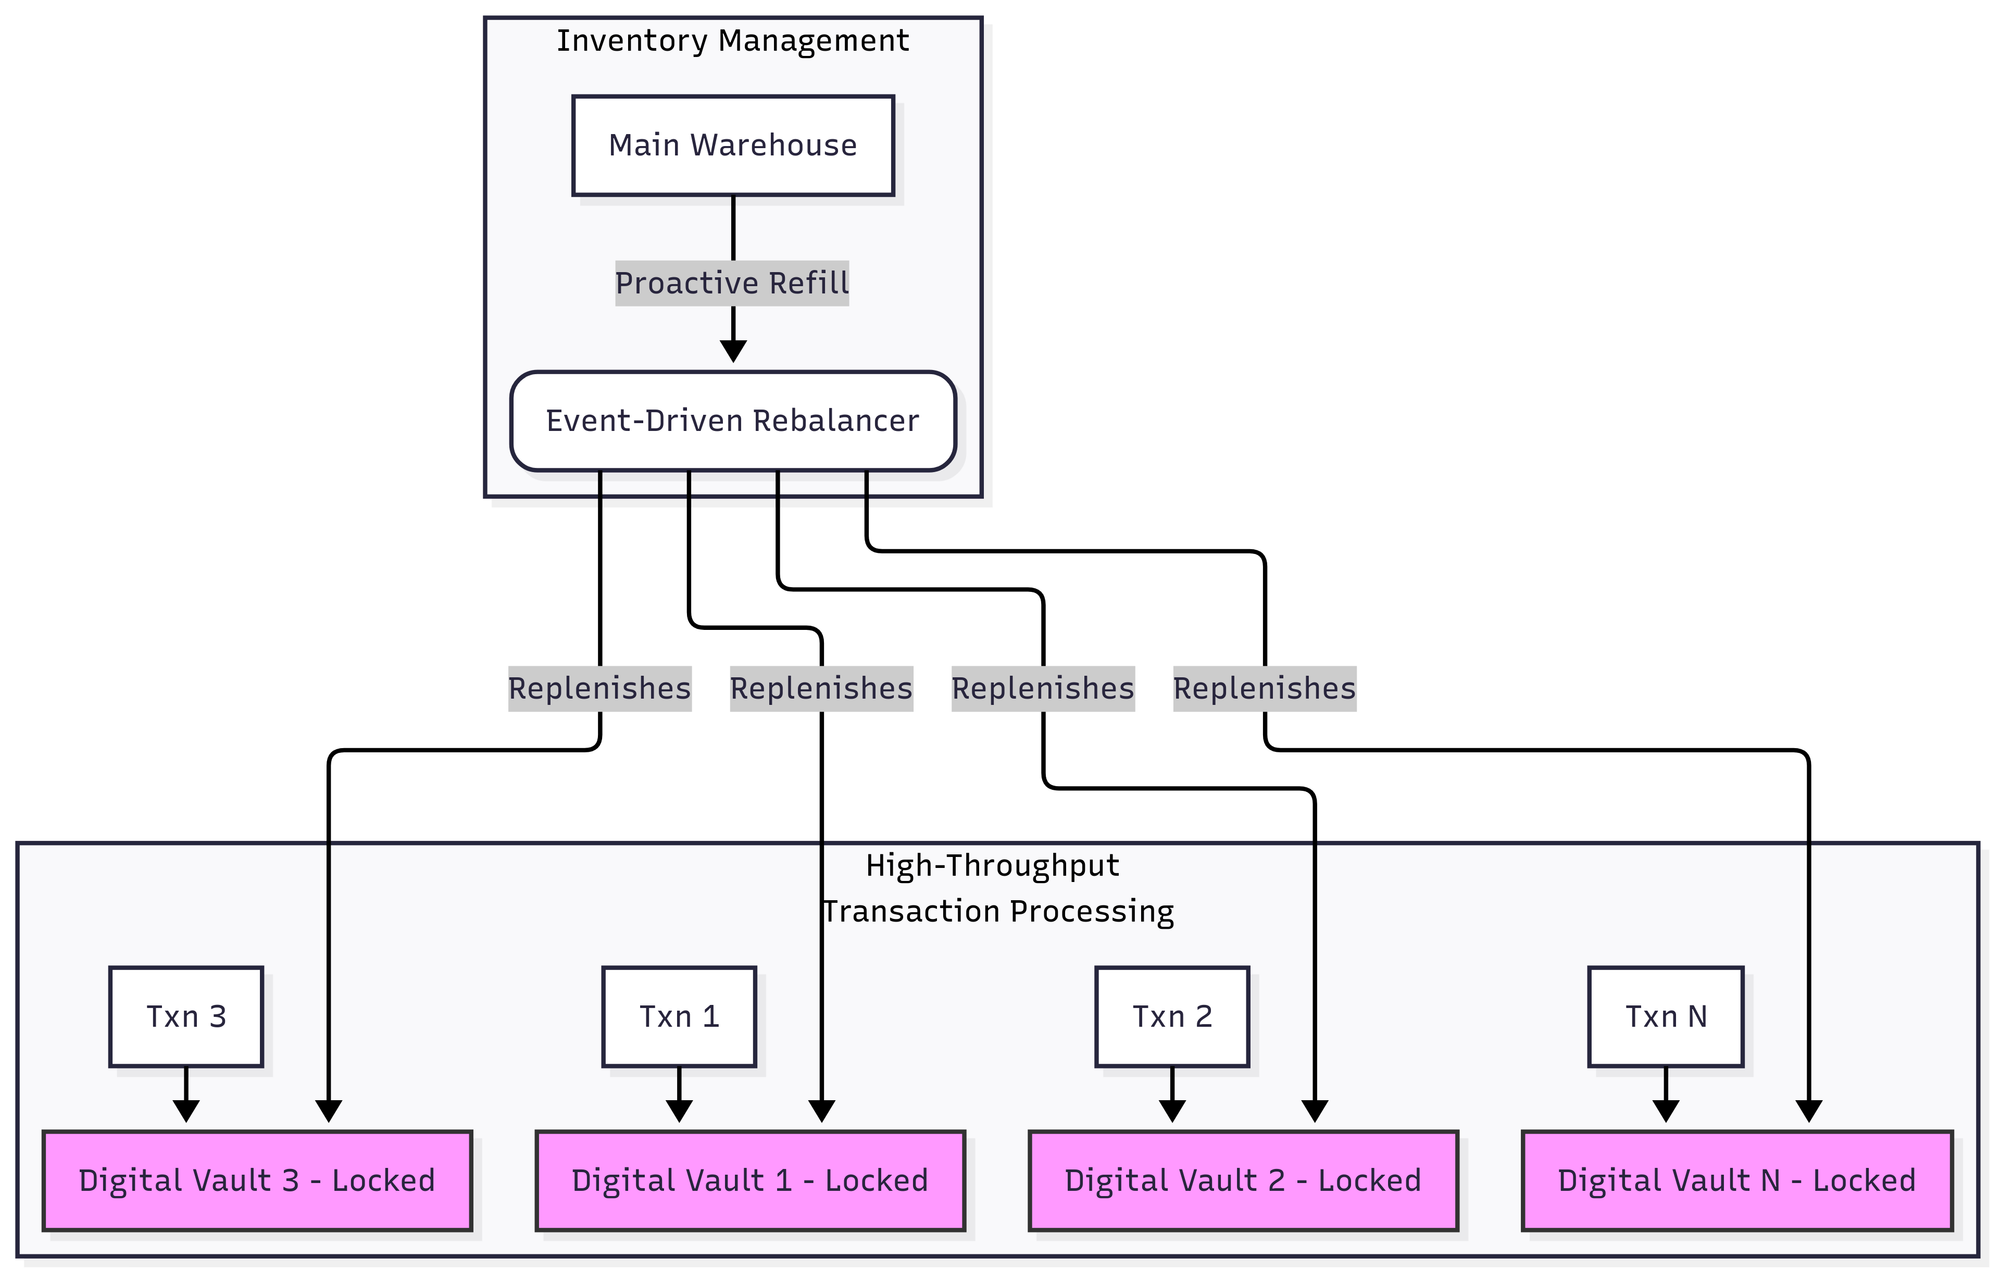
The architecture itself relies on a distributed event stream. Every transaction triggers a series of checks in parallel: device fingerprinting, velocity checks across the customer's history, geographic anomaly scoring, and merchant risk profile matching. These checks don't happen sequentially like they do in most gateway-level fraud tools. The parallel approach matters because latency is the thing that kills conversion rates more than anything else. You want those checks to return in under 200 milliseconds, and Silver Charge's architecture is built to hit that target under normal load.
How It Actually Functions in Production
The integration is REST-based, which should be familiar territory for anyone who's built an API. You POST transaction data to their endpoint, and they return a decision along with a confidence score and a breakdown of which rules triggered. The decision isn't just approved or declined. It can be approve, decline, challenge, or review. The challenge response is worth paying attention to because it's where the system asks for additional authentication, usually through 3D Secure or an out-of-band verification step. One thing that caught me off guard during my first integration was how aggressively the system could be tuned. There's a dashboard where you set thresholds for each rule category, but the default settings are intentionally conservative. I learned this the hard way when a client's test environment approved a transaction that should have been flagged, and then our production settings auto-approved what looked like a coordinated attack on their luxury goods storefront. The system was too trusting of certain device fingerprints that turned out to be synthetic IDs. Adjusting the device reputation threshold from the default 75 to about 40 cut the fraudulent orders without impacting legitimate sales. The risk scoring engine uses a combination of supervised learning models trained on labeled fraud data and rule-based heuristics that you can customize. The models are updated continuously, which means the system gets better over time as more transaction data flows through it. That sounds like every other vendor pitch, but the difference here is that the feedback loop is explicit. When your team marks a transaction as false positive or true positive, that data feeds back into the model within hours, not days or weeks. In practice, this means your fraud detection improves noticeably after the first two to three weeks of operation, assuming you have enough transaction volume to provide meaningful training data.
Get the Full Details

Edge Cases and What Breaks
Here's what nobody tells you about Silver Charge and systems like it: they struggle with low-volume merchants. If you're processing fewer than 500 transactions per month, the behavioral analysis doesn't have enough signal to work with. The system defaults to the population-level model, which is fine for broad fraud patterns but misses the nuanced attacks that target smaller businesses. I worked with a boutique marketplace that was getting hammered by return fraud, and Silver Charge couldn't differentiate between legitimate repeat customers and coordinated abusers because their transaction history was too sparse. We ended up layering a separate chargeback protection tool on top of it. Another issue is the integration complexity for legacy systems. One of our clients was running on a payment stack that hadn't been updated since 2018, and getting Silver Charge to communicate with their existing order management system required a custom adapter. It wasn't impossible, but it added about two weeks to the timeline and roughly eight thousand dollars in development costs. If you're on a modern stack, you probably won't encounter this. If you're on anything older, budget for it. The pricing structure is also worth understanding before you commit. Silver Charge charges per transaction with a tiered model that drops significantly after you cross certain volume thresholds. For a mid-market merchant doing around a million dollars monthly, the effective cost comes to roughly four to six cents per transaction. That includes the fraud detection, tokenization, and identity verification components. Compare that to running three separate tools for each of those functions, and the consolidation makes financial sense even before you factor in the reduction in fraud losses.
Setup and Configuration Walkthrough
You start by creating an account on their developer portal and generating API credentials. The sandbox environment is fully functional, which is important because you want to test your integration against synthetic transaction data before touching production. They provide a dataset generator that creates realistic fraud patterns, including card testing attacks, friendly fraud, and account takeover attempts. Use it. I've seen too many teams skip this step and then discover their rule configurations don't actually block anything until they're already taking losses. The API documentation covers the standard endpoints thoroughly. Authentication uses API keys with IP whitelisting, which is the expected approach. The main endpoint for transaction submission accepts a JSON payload with fields for amount, currency, customer details, device information, and merchant context. The device information is critical. Transactions that don't include device fingerprint data score significantly lower on risk assessment because the behavioral model can't establish a baseline. Make sure your frontend is collecting device telemetry before you submit the transaction. After the initial integration, you'll want to spend time in the rules engine. The default ruleset is a reasonable starting point, but it's designed to be broadly applicable across merchant types. Your specific business will have different risk profiles. A digital goods seller faces different threats than a physical retailer. A subscription service has different fraud vectors than a one-time purchase platform. Adjust the rules based on your actual transaction patterns, not the vendor defaults.
Monitoring is handled through the dashboard and through webhooks. Set up webhooks for every decision type so your backend can react in real time. I recommend routing high-confidence declines to an automated block, routing low-confidence challenges to a manual review queue, and logging everything else for weekly pattern analysis. That three-tier approach kept our client's review team focused on the transactions that actually needed human judgment instead of burning through hundreds of clear-cut decisions daily.

When This Approach Won't Work For You
Silver Charge isn't suitable for every use case. If you're operating in a heavily regulated industry with specific compliance requirements around data residency, you need to verify that their infrastructure meets your jurisdictional needs before committing. They have data centers in multiple regions, but the configuration isn't automatic. You have to request specific routing during setup. Cross-border transactions introduce additional complexity. While Silver Charge supports multi-currency processing, the fraud models are primarily trained on North American and European transaction data. If you're processing significant volume from other regions, especially parts of Southeast Asia or Latin America, the accuracy drops measurably. We saw a fifteen percent increase in false positives when a client expanded into Brazil without adjusting their regional ruleset. The fix was creating separate rule configurations for each major market rather than using a single global set. There's also the dependency consideration. Once you're integrated, you're tied to their uptime and their pricing changes. Like any third-party service, this is a tradeoff. You're giving up some control in exchange for capability you'd otherwise have to build yourself. For most teams, that's a good trade. For teams with sophisticated in-house fraud engineering capabilities, it might not be. Know your own capacity before outsourcing this function.
The system also doesn't replace the need for operational discipline. Automated fraud detection is a tool, not a strategy. You still need to review trends, update rules as attack patterns evolve, and maintain a response plan for when the system misses something. No configuration I've seen eliminates all fraud. The goal is to reduce it to a manageable level while keeping legitimate transactions flowing. Silver Charge gets you closer to that goal than most alternatives I've evaluated, but it requires active management to stay there.