The Architecture Nobody Talks About
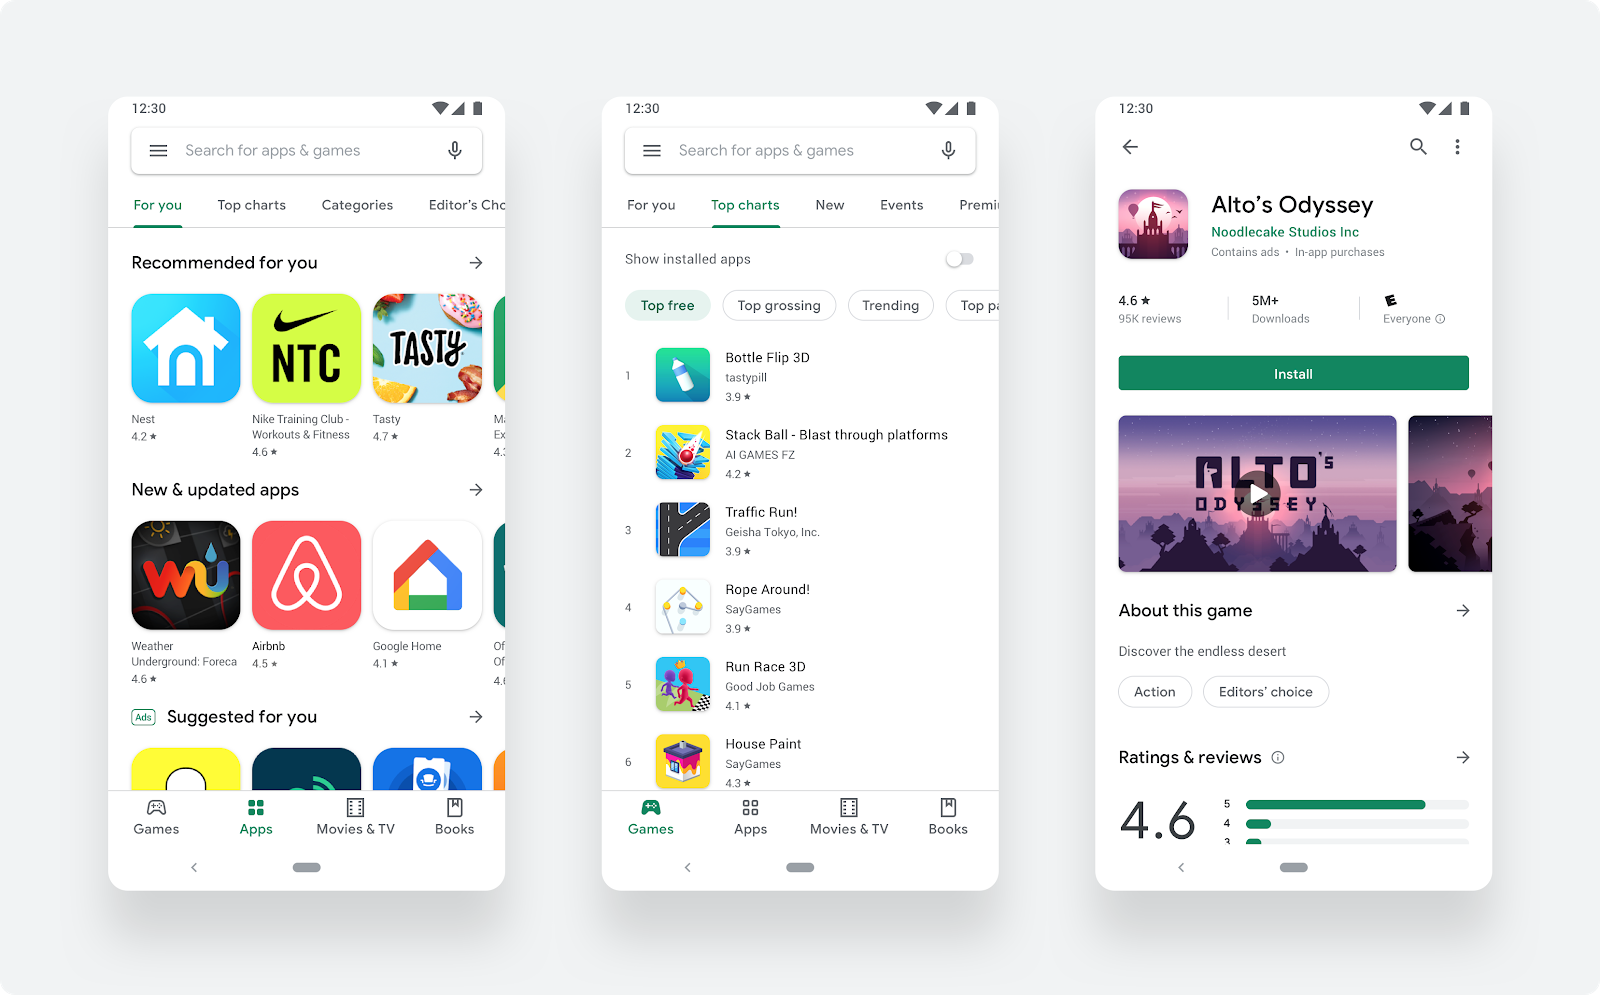
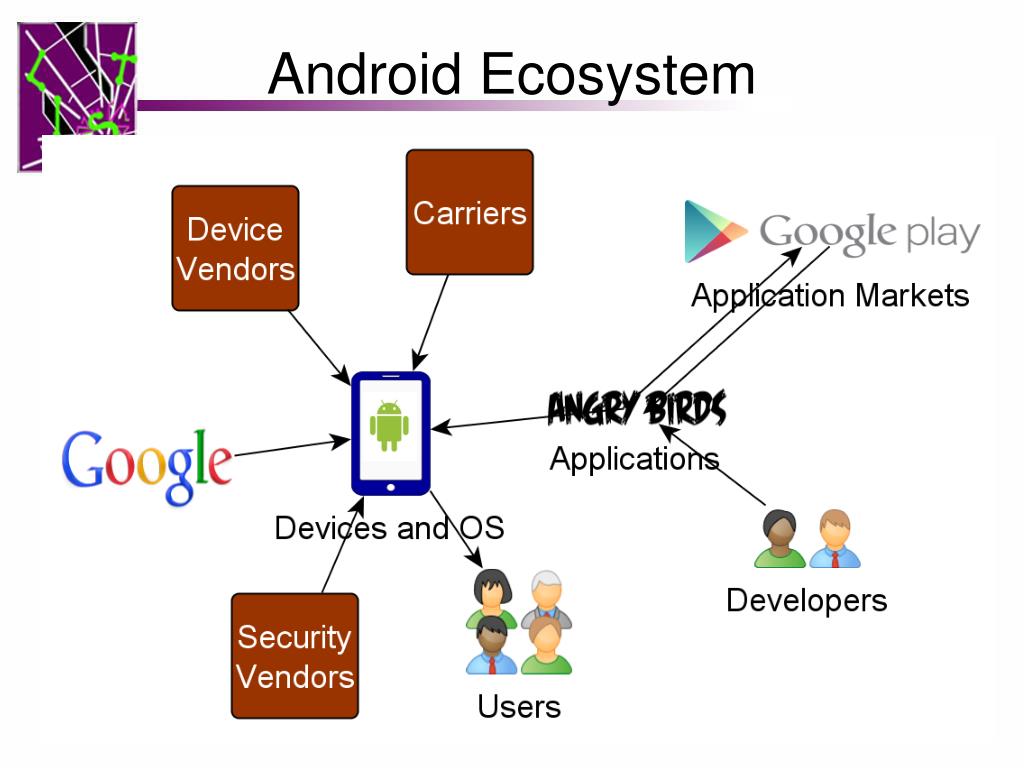
Most people think the Google Play Store is just a storefront. It is a storefront, but underneath that interface sits a sprawling distribution and enforcement infrastructure that controls how apps are packaged, verified, delivered, and updated across millions of devices. The same system also quietly shapes what you can install, how you pay, and which apps survive past your home screen.When I first started reverse-engineering Android app distribution back in 2016, I treated the .apk file as the source of truth. That was a mistake. The real object is the App Bundle. Google moved the industry toward that format roughly around 2021, and the shift was not trivial. An App Bundle contains all compiled code and resources up front, but the actual installation artifact gets split at publish time into base and configuration-specific module APKs. Dynamic Delivery selects which modules land on any given device based on its ABI, screen density, and locale. This is why your app size can vary by tens of megabytes depending on the phone. The Play ecosystem operates through several coordinated layers. There is the packaging layer (App Bundle format). There is the verification layer (Play Integrity API, Play App Signing, and signature scheme v2/v3). There is the delivery layer (CDN routing, split APK assembly, and instant app support). And there is the policy layer (content guidelines, payment rules, and Device Config enforcement). These layers talk to each other continuously during installation, updates, and runtime. Play App Signing is the single most consequential feature most developers do not fully understand. When you enroll, Google takes over the keystore. Your uploaded bundle gets signed with Google's key, not yours. This means you cannot change your signing certificate later without wiping user data. It also means sideloading and Play Store builds are cryptographically distinct, even though they come from the same bundle. I learned this the hard way in 2022 when a client tried to rotate their keystore mid-project. Their existing Play Store users could not receive the update until we re-enrolled and accepted the certificate change, which triggered a data migration prompt for roughly 40 percent of their active install base. The fix was patient, but it cost weeks of coordination with the platform team.
Play Integrity replaced SafetyNet Api in late 2022. It provides device integrity verification and app attribution through four endpoints: BASIC_INTEGRITY, MEETS_STRONG_INTEGRITY, DEVICE_COMPATIBILITY, and APP_ATTRIBUTION. The API itself is straightforward to call, but the real complexity lives in what you do with the results. Many developers treat APP_ATTRIBUTION as a download validation tool. It is not. It validates which Play Store package version served the app on which device. Using it for anti-piracy checks inside the app is fragile and increasingly unreliable as Google tightens the response format. Here is something most guides skip. The Play Store does not simply hand you an APK. It delivers a set of partial APKs through the PackageInstaller system. Your app's PackageManager sees this as a normal installation, but under the hood, the OS stitches together the base APK, the configuration APKs, and any dynamic feature modules your app requested. If your app uses Play Asset Delivery, those assets arrive asynchronously through a completely separate pipeline that writes directly to the app's internal storage area. The caching layer for downloaded assets can fill up silently, and there is no public API for forcing a cache clear beyond uninstalling the app or clearing storage through the system settings. I ran into this in 2024 when a gaming app I consulted on started reporting corrupted asset loads on Pixel devices running Android 14. The root cause was the new scoped storage enforcement interacting badly with the PAD cache invalidation logic. The workaround involved triggering an explicit flush after each asset pack load instead of relying on the automatic lazy cleanup, which added about 200 milliseconds per load cycle but eliminated the corruption issue entirely. Dynamic delivery is where the ecosystem truly exerts control. Google can route users to different module combinations without your app even knowing the difference. This is powerful, but it creates a maintenance nightmare for teams that built their distribution around monolithic APKs. You also have to account for instant apps, which require every feature module to be independently installable and cannot depend on background services or persistent storage at launch time. I have seen projects abandon instant app support after three months because the modularization requirements conflicted with their architecture, and the only clean exit was to remove the entry point from the Play Console configuration before the next store review cycle.
The payment infrastructure deserves a separate mention because it directly shapes revenue behavior. Google's in-app purchase system enforces a 15 to 30 percent commission on digital goods, and the enforcement is not theoretical. Apps that attempt to bypass the billing SDK through alternative payment flows face rejection during review or removal after publication. The policy exceptions exist for physical goods, subscriptions to external services, and certain regional workarounds, but the exception list is narrower than most developers assume. I advised a fitness app client in 2023 to restructure their subscription model around a web-based signup flow with local device activation keys. It worked, but it required building a complete identity reconciliation system to prevent account sharing, and the conversion rate dropped by roughly 35 percent compared to the in-app purchase funnel. The trade-off was acceptable for their margins, but it was not a trivial engineering undertaking. Device Config is another hidden mechanism. Google maintains a server-side configuration database that pushes device-specific parameters to installed apps through the Play Services framework. This includes things like allowed camera formats, background execution limits, and recommended UI padding values. Apps that query Device Config at runtime get accurate information about what the device and Google's policies permit. Apps that ignore it either make incorrect assumptions or fail compatibility tests during certification. The certification process itself has tightened considerably since 2023, with automated behavior checks that scan for prohibited patterns like hidden redirects, obfuscated credential collection, and unauthorized use of sensitive APIs. There are real limitations to this architecture. The Play Integrity API responses can vary between devices from the same manufacturer, especially on heavily modified ROMs or devices with custom bootloaders. APP_ATTRIBUTION tokens expire after approximately 30 days, so any validation logic that depends on them must be time-bounded and gracefully degraded. Dynamic feature modules increase build complexity and testing surface area significantly. And the Play Store review process remains inconsistently applied across regions, with some categories facing automatic flags that require manual appeals lasting weeks.
Get the Full Details

If you need to distribute outside the Play ecosystem entirely, sideloading remains technically possible through APK extraction or direct download, but you lose automatic updates, malware scanning, and the ability to use Google Pay integration. The trade-off is real, and it matters more for enterprise deployments where device management policies override store-based distribution anyway. The practical takeaway is that the Play ecosystem is not a neutral distribution channel. It is an active participant in how your app behaves on device. Understanding the packaging pipeline, the signing chain, the dynamic delivery routing, and the policy enforcement mechanisms is not optional if you are building for Android at scale. Most problems I see in production trace back to one of those four layers being misconfigured or misunderstood during the initial release planning phase.