Getting Cloudflare Zero Trust DNS Running On Your Network
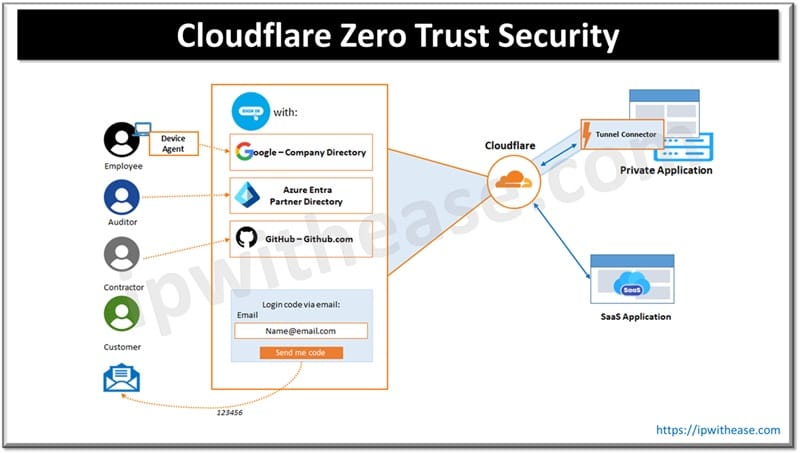
DNS filtering sounds like a simple concept until you actually try to wire it into an existing infrastructure without breaking the internal resolver chain. Cloudflare Zero Trust provides a managed DNS layer that sits in front of your users and blocks malicious domains before they resolve. It works. I deployed it across three remote offices last year and it did exactly what it promised on the external query side. The catch is that the setup has a few moving parts that most people gloss over. The basic mechanism is straightforward. You create an account in the Cloudflare Zero Trust dashboard, designate the organizational domain, and then switch your DNS resolvers to the Cloudflare endpoint addresses they provide. Every DNS query from any device under that org routes through their filters. Queries for known malware domains, phishing infrastructure, and cryptomining services get dropped. That is the entire thesis. But here is the part nobody puts in the marketing copy. Zero Trust DNS does not encrypt your DNS traffic by default. It filters it. If you want encrypted DoH queries, you have to explicitly enable that setting in the dashboard and push the DoH endpoint configuration out to your clients. I learned this the hard way when I spent two days troubleshooting why a threat intel report from our SIEM was flagging unencrypted DNS queries still leaking outbound from a fleet of Windows workstations. The DNS filtering was active. The encryption toggle was not. Turning on DoH support and redistributing the client config took about forty-five minutes and resolved the issue entirely.
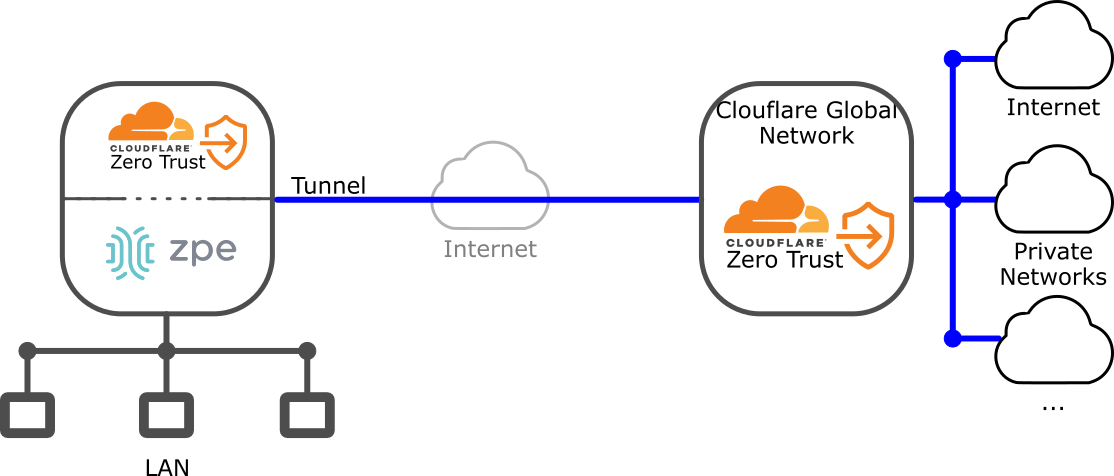
Another thing that trips people up is the fallback behavior. When Cloudflare Zero Trust DNS goes down or a client loses connectivity to their resolver, most operating systems will silently revert to the fallback DNS servers configured at the OS or DHCP level. Your network might appear secured during business hours and then quietly stop filtering after an overnight outage when the cloud tunnel drops. I dealt with this on a small manufacturing site where the VPN to the Zero Trust tunnel would drop for roughly ten minutes every night during a backup window. During those ten minutes, all DNS queries fell back to the ISP default resolver, which meant zero filtering. The workaround was to lock the internal DNS server on the firewall to forward all queries through the Cloudflare DoH endpoint rather than letting the endpoints themselves choose the resolver. That eliminated the fallback gap entirely. Configuration took about twenty minutes. Setting this up properly requires a few concrete steps. First, add and verify your organizational domain in the Zero Trust dashboard. This usually involves adding a DNS TXT record to your public zone, which takes effect within the propagation window of your TTL settings. Second, under Network > DNS, you will see the Cloudflare nameserver addresses you need to point your DHCP scopes or device policies toward. Third, configure your action settings. You can set malicious queries to block or sandbox them, and you can enable the safe browsing policy which leverages Cloudflare's threat intelligence feeds. Fourth, enable encrypted DNS if you want DoH or DoT support, then distribute those endpoint addresses to your endpoints via Group Policy, MDM, or whichever management tool you already use. There is a nuance with split-horizon DNS that deserves attention. If your organization runs internal hostnames that should never leave your network, routing all DNS through Cloudflare means those internal queries now traverse the internet to Cloudflare and back. You can configure DNS forwarding rules in the Zero Trust dashboard to send specific domain queries to an internal resolver while routing everything else through Cloudflare. Without this, either your internal names break or your internal DNS traffic leaks outbound. I had to redraw the forwarding rules for a client who ran an Active Directory-integrated DNS zone and noticed that queries for .internal domains were being sent to Cloudflare's public resolvers, which obviously could not resolve them. Setting the forwarder rule for that specific zone pointed queries back to the internal DNS server and fixed the resolution failure immediately.
The other realistic limitation is that this is a perimeter defense, not a comprehensive security strategy. Zero Trust DNS filters based on domain reputation and threat intelligence. It does not inspect application-layer traffic, it does not validate user identity beyond the org enrollment, and it does nothing to stop lateral movement once a device is on your network. A credential theft attack that compromises a workstation will still work even if DNS filtering blocks the initial C2 domain, because the attacker can simply rotate to a new domain that has not yet been categorized. I saw this play out with a ransomware incident at a mid-size firm that had exactly this setup. The DNS layer blocked the initial dropper domain, but the attacker had already established a persistent backdoor through an RDP session two weeks prior. The DNS filtering would have prevented reinfection, but it did not prevent the initial compromise. That is not a flaw in Cloudflare's product. It is a flaw in assuming a single control solves the problem. If you need something more comprehensive, pairing Zero Trust DNS with a full ZTNA policy that controls application access based on identity and device posture closes a meaningful gap. Cloudflare offers both in the same dashboard, and configuring them together is faster than running two separate vendor stacks. The DNS-only approach is useful when you have a tight budget or a simple environment and need immediate coverage against malware domains and phishing infrastructure. It delivers that coverage quickly. Most deployments I have seen go live within a single afternoon if the domain verification proceeds without issues. One additional operational detail worth noting. The logging interface in Zero Trust surfaces query data at the domain level, not always at the per-client granularity you might expect depending on your plan tier. If you need to investigate a specific device's query history during a forensic walkthrough, you may find yourself cross-referencing endpoint logs rather than relying solely on the Cloudflare dashboard. This is manageable but it affects the speed of incident response. Factor that into your design decision if rapid attribution matters to your team.
Get the Full Details