Why Your Password System Is Already Broken
I spent three years working on identity infrastructure for a fintech company, and the most expensive part wasn't the code. It was dealing with the fact that every identity system built since 2015 has been solving yesterday's problems with increasing desperation. Centralized databases get breached, KYC processes take five business days, and users have approximately seventeen passwords they're all too lazy to keep straight. The industry knows this. Nobody has figured out how to fix it without creating a worse version of the same problem. That's starting to change, and not in the way the marketing teams want you to think. The Future Of Identity Verification How Blockchain And AI Are Revolutionizing Digital Security isn't a single product or platform. It's a set of overlapping approaches that happen to work tolerably well together when you stop treating them like separate solutions and start treating them like parts of a pipeline.
The Future Of Identity Verification How Blockchain And AI Are Revolutionizing Digital Security
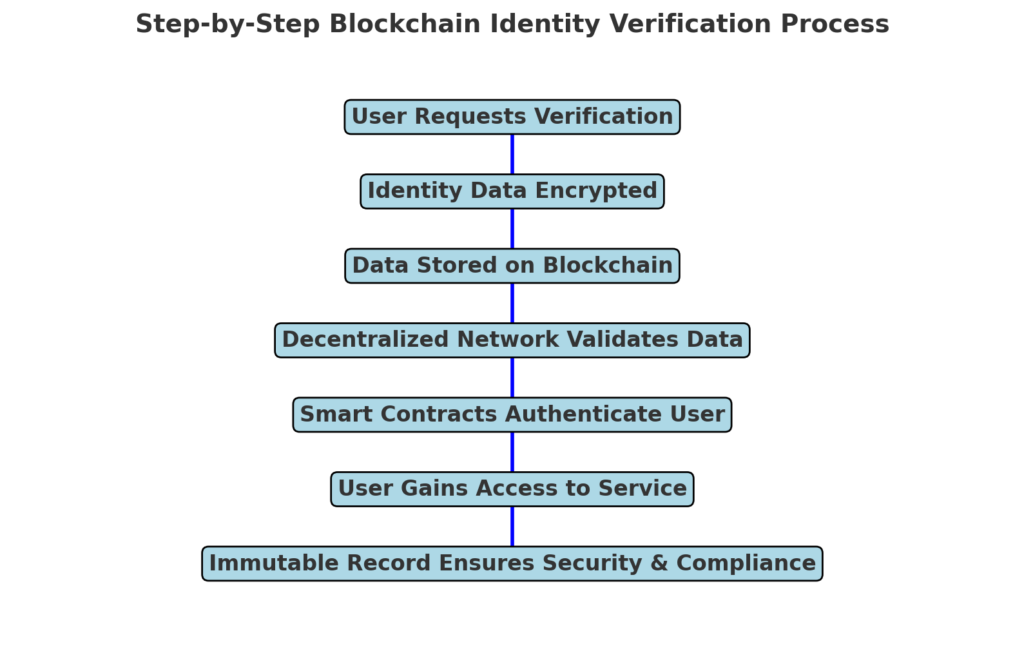
Let's talk about what this actually looks like in production, not in a slide deck. Blockchain identity in practice means decentralized identifiers, commonly called DIDs. These are cryptographic keys that belong to the user, not to some corporation that stores them in a database behind a firewall. The DID itself is just a reference, a pointer to a resolver that returns the corresponding public key. You can publish that resolver document on a blockchain or a distributed ledger, and anyone can verify that the key belongs to whoever claims it. No central authority. No middleman. The key is the credential. Then you layer on verifiable credentials, which are signed attestations issued by trusted entities. A university issues a verifiable credential that says someone graduated. The person holds it in their wallet. When they need to prove their degree to an employer, they share the credential without revealing anything else about themselves. No email sent, no portal login, no third party copying sensitive data into their HR system.
The AI component enters at two points. First, document analysis. When a government issues a new passport or ID card, AI models — typically OCR combined with layout analysis — verify that the document is authentic, that the image isn't edited, that the holograms and security features check out. This is largely solved now, though false positives around forged documents remain a real concern depending on your jurisdiction. Second, behavioral biometrics. Gait, typing rhythm, mouse movement patterns, even how someone holds their phone. AI systems can build a risk profile that adjusts in real time, flagging anomalies without needing a hardcoded rule set for every possible edge case. Here's the part nobody tells you: zero-knowledge proofs are where this gets genuinely interesting and genuinely difficult. A ZK-proof lets someone prove they satisfy a condition without revealing the underlying data. You can prove you're over twenty-one without revealing your birthdate, your name, or your address. The math works. The implementations work. Getting a ZK-proof verified inside a legacy compliance system that was built in 2009 is another story entirely. I ran into this directly during a rollout for a European payment processor. We'd built the credential verification layer, the ZK-proof generation for age verification, everything. The compliance team needed to produce audit trails that satisfied their regulator. ZK-proofs don't have audit trails in the traditional sense because by design they reveal nothing. We spent four months negotiating with the regulator about what constituted acceptable proof of compliance, and eventually had to implement a hybrid approach where the ZK-proof handled the user-facing verification and a separate opaque-attribution audit log handled the regulatory side. It worked. It's ugly. That's the reality of this space right now.
Get the Full Details
The most common pitfall I see teams make is assuming blockchain solves storage. It doesn't. Storing personal data on-chain is almost always the wrong decision — GDPR Article 20 right to erasure collisions with immutability is not a theoretical problem, it's a legal liability. The right pattern is storing only the hash or commitment on-chain and keeping the actual data encrypted off-chain, with key management handled through a threshold scheme so no single party can decrypt everything alone. Another counter-intuitive thing: AI verification accuracy actually degrades in diverse populations if you train on homogeneous data. I've seen Liveness detection systems fail at rates above 8% on darker skin tones in certain implementations because the training data was skewed. This isn't a hypothetical. It's a deployment risk that can get you sued or regulatory-reviewed depending on where you operate. Always validate your models across demographic segments before going to production, and get it in writing from your vendor that they've done the same. Practical implementation timeline: If you're starting from scratch with a well-defined use case, you're looking at roughly 4 to 6 months for a minimum viable system that handles basic DID verification and verifiable credential issuance. Adding ZK-proofs bumps that to 8 to 12 months. Full biometric integration with fraud detection? 12 to 18 months, assuming you have the data volume to train properly. The biggest variable isn't the technology — it's regulatory approval and the time it takes to convince stakeholders that a cryptographic signature is as good as a paper document.
Cost-wise, expect to spend between $150,000 and $400,000 for a production-grade system depending on scope. The ongoing costs are lower than maintaining a traditional KYC operation — typically 60 to 70% less per verification after the initial build — but the upfront engineering investment is significant. Most teams underestimate the compliance integration work by a factor of two. The honest assessment of limitations matters more than the hype. Blockchain identity systems still require some trusted setup for certain implementations. Self-sovereign identity frameworks assume users can manage their own keys, which means they will lose access to their identity at some point, usually when they change devices. AI-based liveness detection can be fooled by sufficiently sophisticated deepfakes, and the arms race between attackers and detectors hasn't reached equilibrium. None of these are showstoppers, but they're real constraints that determine whether your system holds up under actual attack conditions versus benchmark conditions. For smaller organizations without the budget to build from scratch, open-source implementations exist. Sovrin, Hyperledger Aries, and W3C-compliant libraries are production-tested in various configurations. The gap between deploying an open-source framework and deploying a custom solution is usually measured in weeks, not months, if your requirements align with standard credential flows. The real differentiator in practice isn't which framework you choose — it's how well you handle the integration with existing identity ecosystems and the specific regulatory requirements of your operating environment.