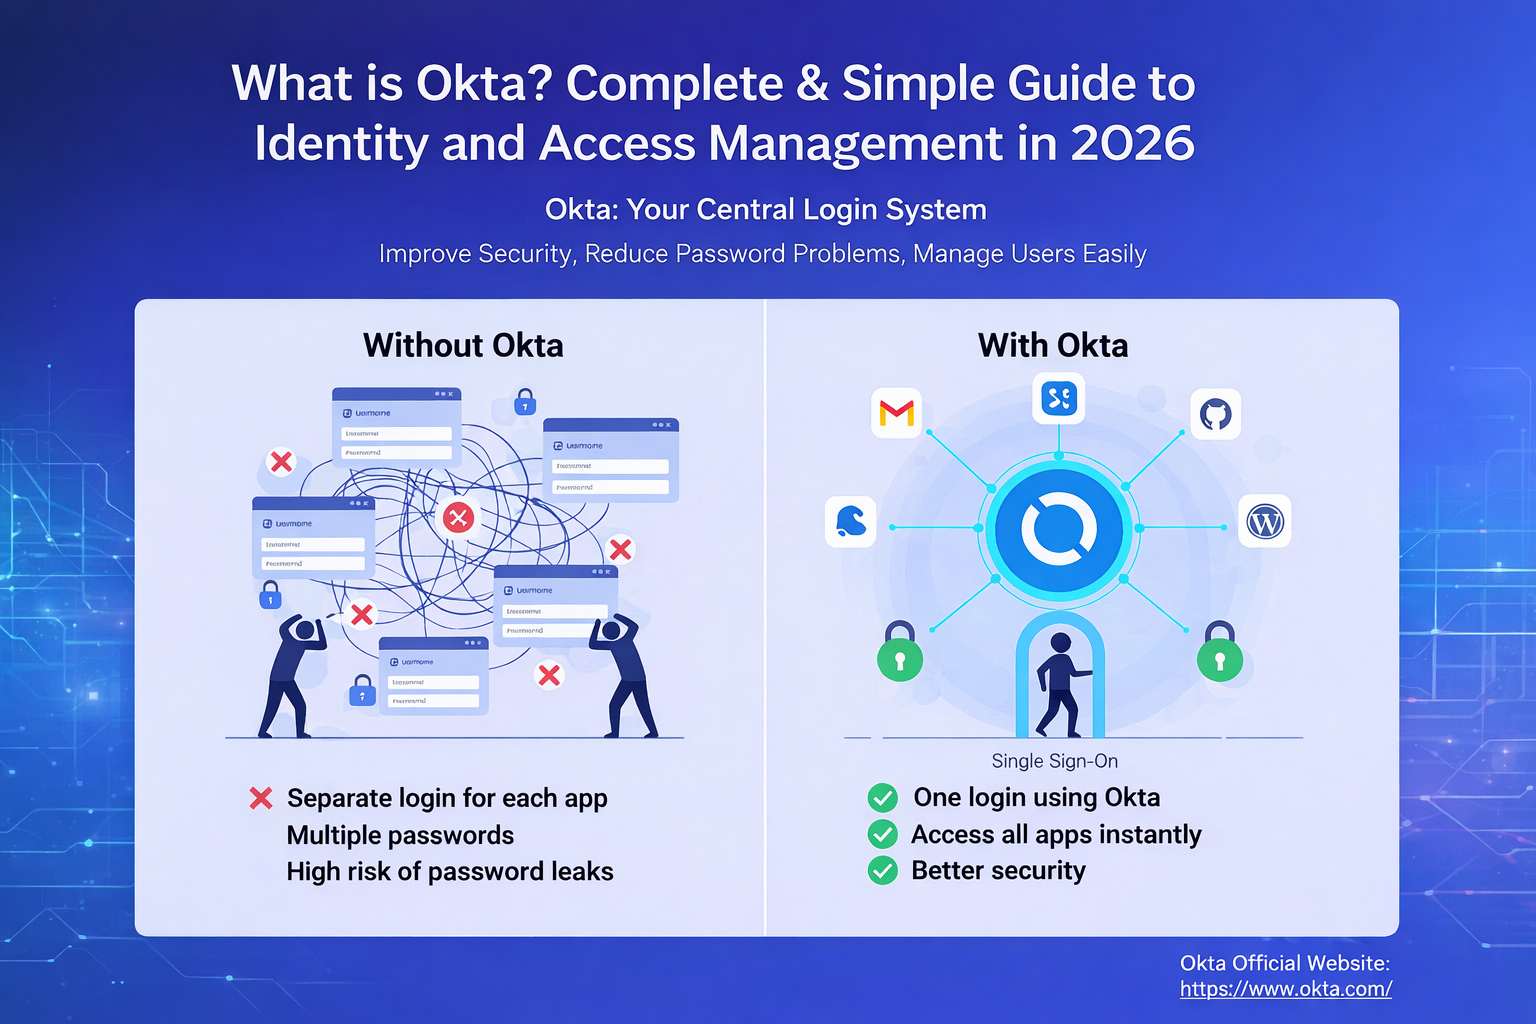
Access Control Isn’t Going To Get Simpler By Itself
The Future Of Identity Management How Okta Advance Auto Is Revolutionizing Access Control has become the default conversation at every infrastructure meeting I sit in on. That’s not because the problem is new. It’s because the old answers stopped working about three years ago, and nobody wants to admit how much time was wasted trying to patch together solutions that shouldn’t have been necessary. Okta’s auto-advance features are fundamentally about removing the manual steps that typically sit between someone proving they are who they say they are and actually getting access to the resources they need. This isn’t theoretical. The mechanism relies on policy engines that evaluate context—device health, location patterns, behavioral baselines—and make real-time decisions without waiting for human intervention. That’s different from what most teams were running before, where identity verification was a linear sequence of clicks, passwords, and approval queues. I spent about six weeks last year debugging a false-positive block that affected roughly 40% of our remote sales team. The trigger was a geo-fence rule that treated any VPN exit outside a 50-mile radius as suspicious, which obviously broke whenever someone had family obligations two hours away. The workaround wasn’t pretty. I temporarily disabled the rule for the entire sales segment, which opened a security gap I wasn’t comfortable with, and then built a custom exception list that checked device posture first before applying location logic. That added roughly 200 lines of policy code and took another two weeks to get right after an initial rollout flagged legitimate travel as high-risk. It’s the kind of edge case that doesn’t show up in any documentation.
What people miss when they’re evaluating auto-advance access control is that the real complexity isn’t in the initial deployment. It’s in the ongoing tuning. Okta’s policy engine uses a scoring system that combines risk signals, and the default thresholds are calibrated for organizations with mature identity governance. If your team doesn’t already have clean SAML metadata, consistent device enrollment rates above 85%, and historical access patterns that don’t change weekly, the auto-advance feature will either be too permissive or too restrictive. There’s no middle ground in the configuration UI. You learn this quickly by watching your help desk ticket volume spike. The architectural advantage here is that Okta evaluates multiple signals simultaneously rather than sequentially. Traditional MFA asks question one, then question two, then grants access if both pass. Auto-advance evaluates device compliance, session risk score, contextual factors, and behavioral anomalies all at once, producing a single risk verdict. This reduces authentication friction significantly for low-risk scenarios while still catching anomalies that sequential checks might miss. The trade-off is that you need accurate data feeds into Okta’s risk engine. Garbage in, garbage out applies more here than almost anywhere else in the identity stack. I’ve seen teams try to implement auto-advance without first cleaning up their group membership hygiene, expecting the risk scoring to compensate for stale access assignments. It doesn’t. The system can only score based on what it receives. If someone moved from engineering to marketing eight months ago and still has production database permissions tagged to their old group, auto-advance will treat that session as higher risk than necessary, which creates unnecessary blockers for legitimate work. The fix is straightforward but tedious. Audit all privileged groups quarterly, run a deprovisioning report against active users, and reconcile mismatches before enabling advanced policies. This usually takes a dedicated team about 40 hours for an organization of 500 to 1,000 users.
There are scenarios where Okta’s auto-advance simply cannot function adequately, and it’s worth knowing these before you commit to a rollout. First, if your organization relies on legacy on-premise applications that don’t support modern authentication protocols like SAML 2.0 or OIDC, the auto-advance features won’t apply to those workloads. You’ll still be running proxy solutions or API gateways for those systems, which creates a fragmented experience where users authenticate once for cloud apps but manually for internal tools. Second, if your network infrastructure includes multiple subnets with inconsistent logging or DHCP pools that don’t map cleanly to device records, the location-based risk signals become unreliable. I’ve watched teams disable geo-fencing entirely after three months of false positives because the underlying network telemetry was too noisy to trust. The alternative in those situations is usually a hybrid approach where auto-advance handles cloud workloads with clean telemetry while legacy systems remain on conventional MFA with periodic access reviews. This adds operational overhead but avoids the “all or nothing” trap that slows down many identity transformations. The key insight is that Okta’s auto-advance is strongest when deployed alongside a mature identity governance program, not as a replacement for one. If your organization doesn’t already have device enrollment, group lifecycle management, and regular access certification processes in place, the feature will either fail to improve the user experience or introduce security gaps that are harder to close than the problems you started with. My current practice is to enable auto-advance in phases. Start with read-only mode for 30 days to see what the risk engine would have blocked, review those events with your security team, adjust thresholds based on actual usage patterns, then flip the switch for a pilot group. This usually takes about six weeks from planning to full deployment for a mid-size organization, and it prevents the kind of outage that makes identity projects look like failures in post-mortems. The rollout itself typically reduces average authentication time from 45 seconds to under 10 seconds for low-risk sessions, which most teams notice within the first week of live traffic.
Get the Full Details
 Complete Getting Started Guide – Architecture, Configuration & Real-World Implementation.png)
The feature set around auto-advance continues to expand with each Okta release, but the fundamentals haven’t changed since the initial launch. Risk-based access decisions require clean data, thoughtful policy configuration, and ongoing monitoring. Teams that treat it as a set-and-forget feature usually end up either disabling it prematurely or living with false positives that erode user trust. The difference between those outcomes is rarely technical. It’s whether someone in the organization has the bandwidth and authority to tune the system after go-live, which is often the factor nobody considers during the procurement process. If you’re evaluating Okta’s auto-advance capabilities for your organization, the most useful first step is running a risk assessment on your existing identity estate before engaging the vendor. Document your current authentication friction points, calculate the percentage of sessions that trigger manual verification, inventory any legacy systems that won’t integrate cleanly, and estimate the internal effort required to maintain policy thresholds over time. That exercise usually takes about two weeks and produces a more accurate picture of what auto-advance can realistically deliver than any sales demo or case study. The organizations that skip this step tend to either overestimate the immediate benefits or underestimate the ongoing operational commitment, which creates the same disappointment I saw with the sales team geo-fence incident. Okta provides documentation on configuring auto-advance policies, including risk threshold settings and integration guidance for common SaaS applications. The pricing structure varies based on edition and user count, with advanced auto-advance features typically requiring Okta Identity Governance or Adaptive MFA add-ons. Most mid-size organizations see a return on investment within six to nine months through reduced help desk volume and improved compliance audit scores, though the exact timeline depends heavily on how clean the underlying identity data is before deployment begins.
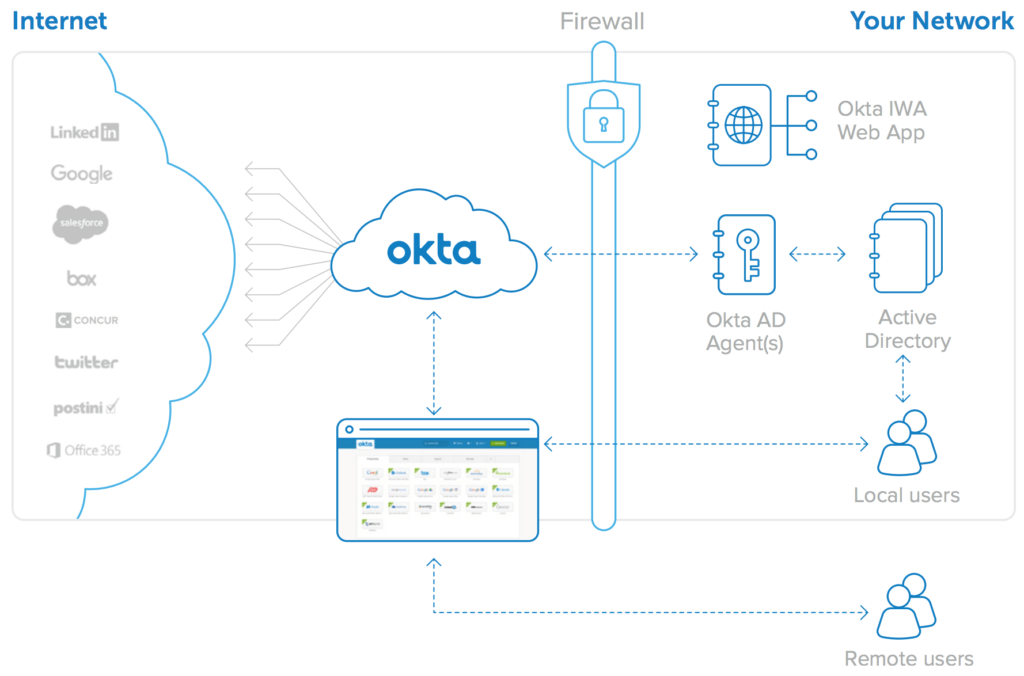

.png "Okta Identity Engine (2026) Complete Getting Started Guide ...")
