How Identity Became The New Perimeter (And Why Your Firewall Won't Save You)
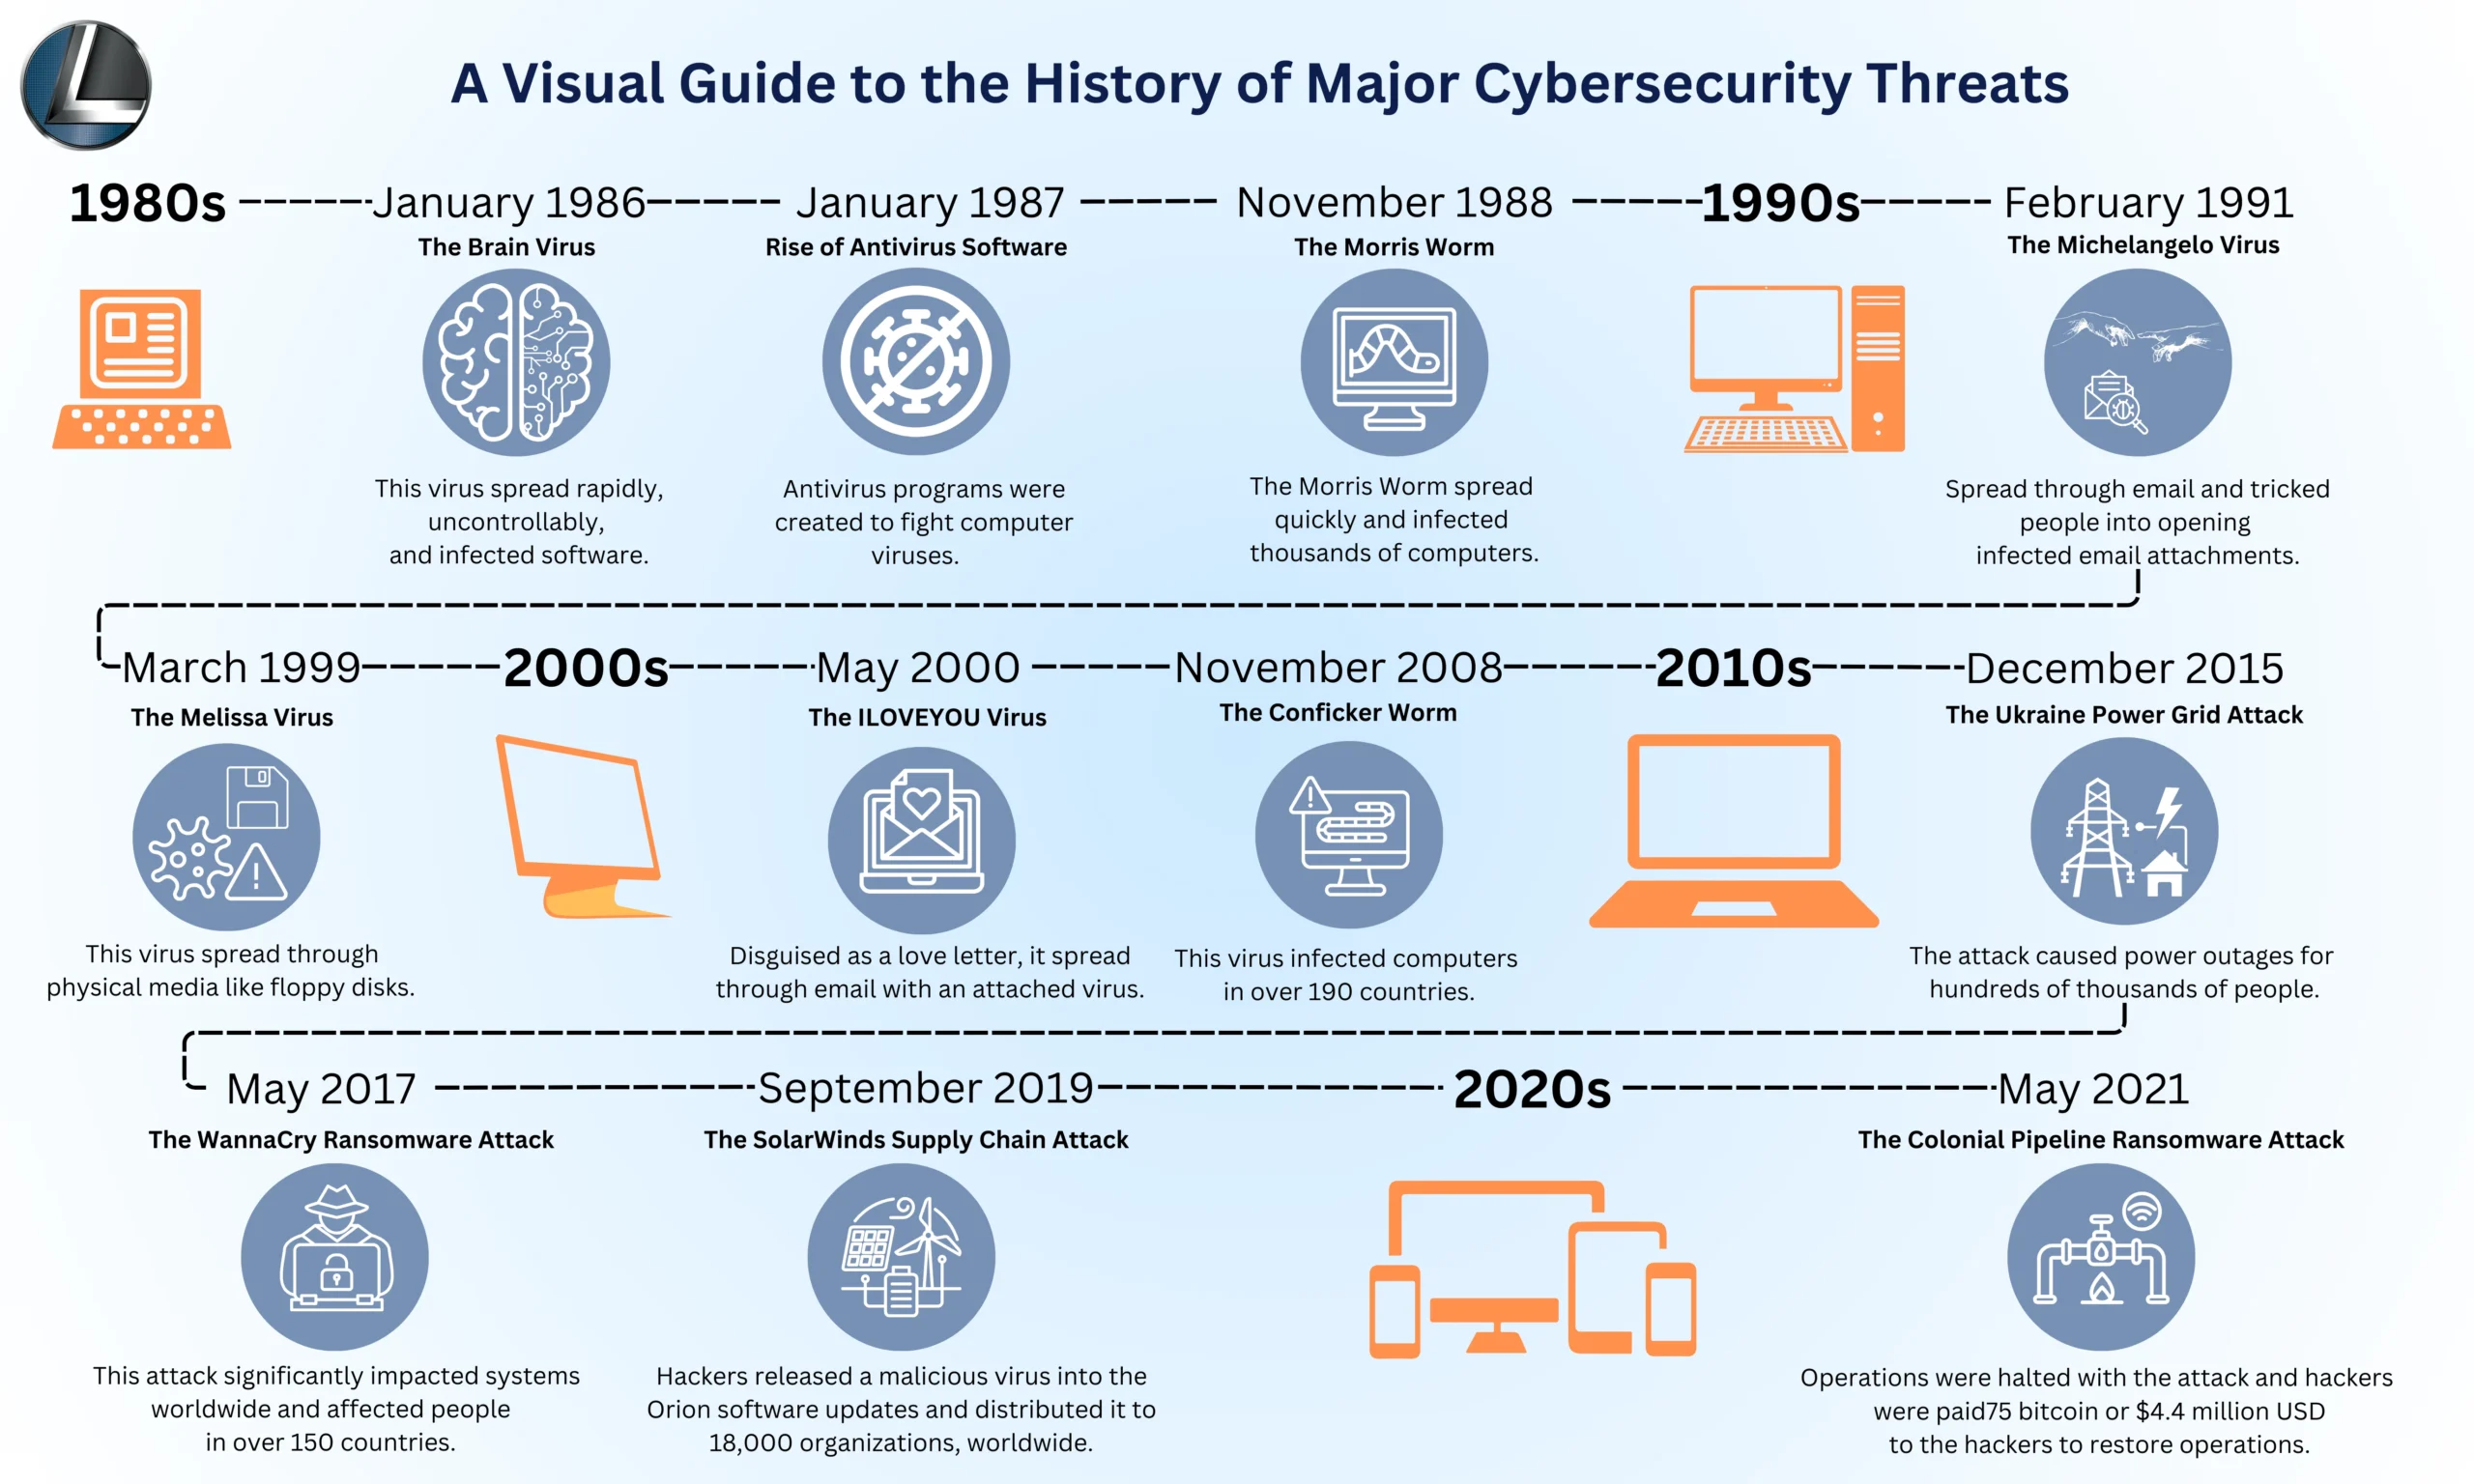
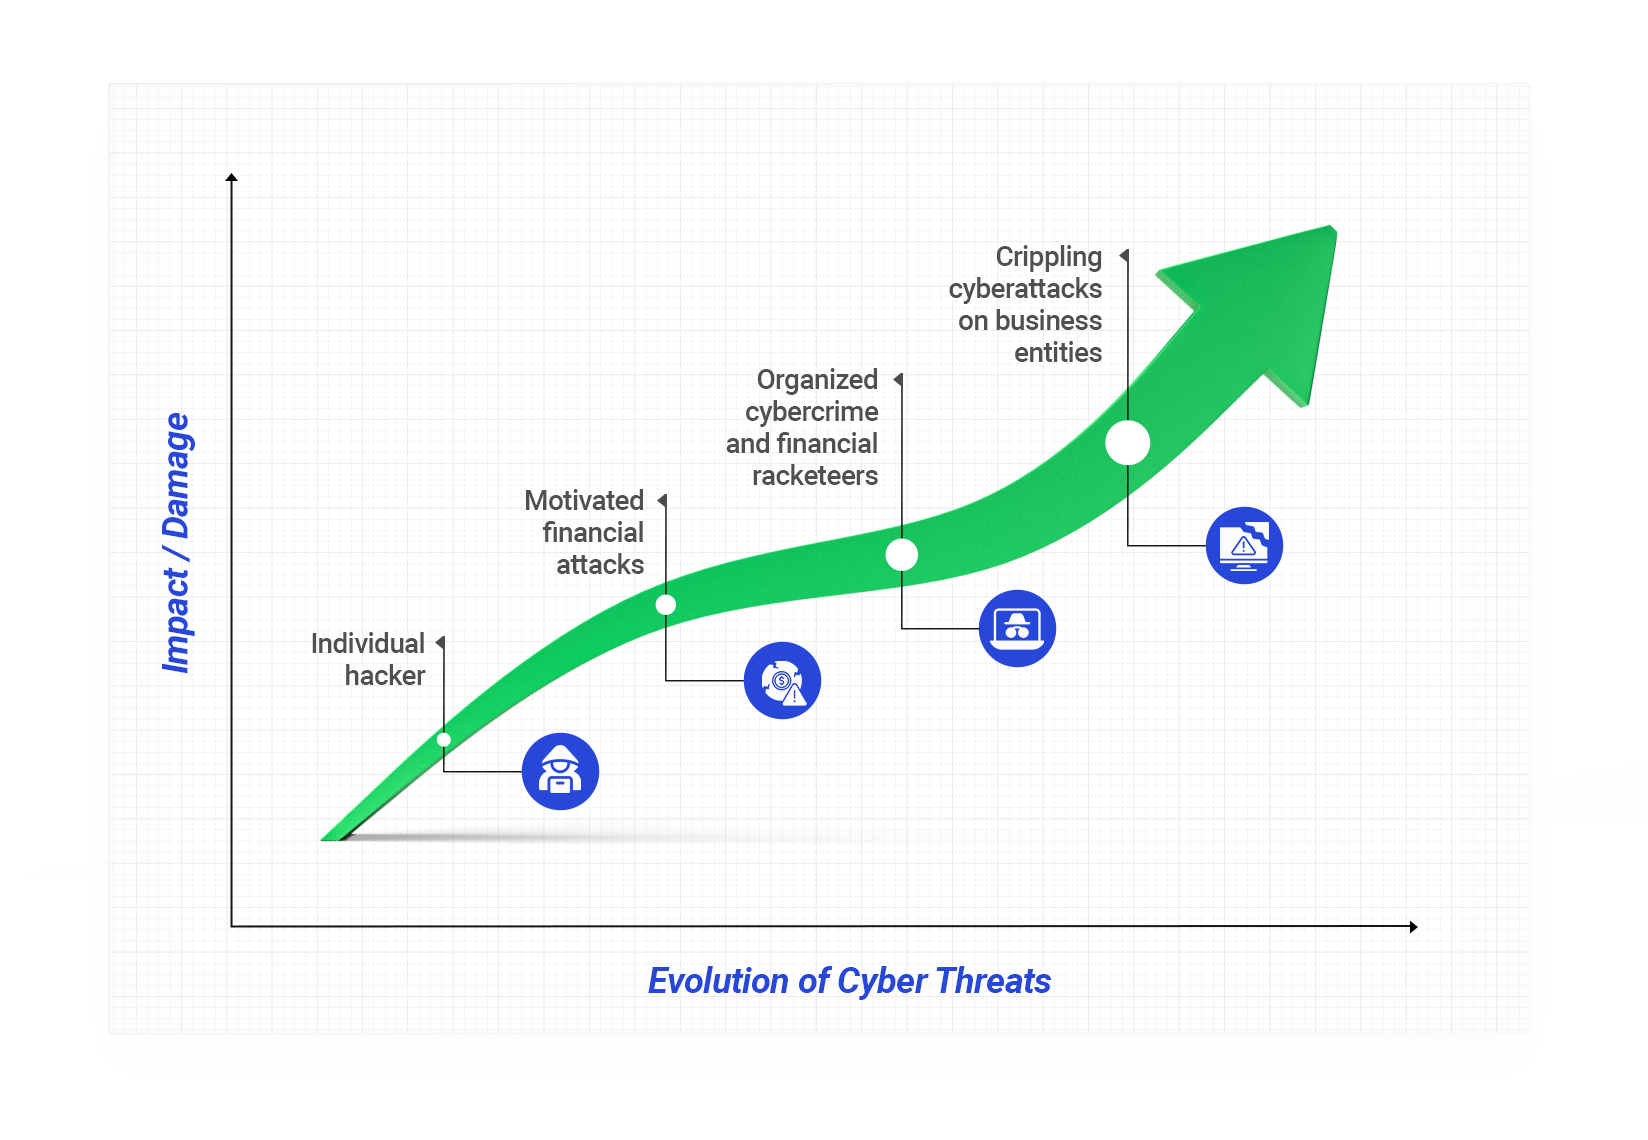
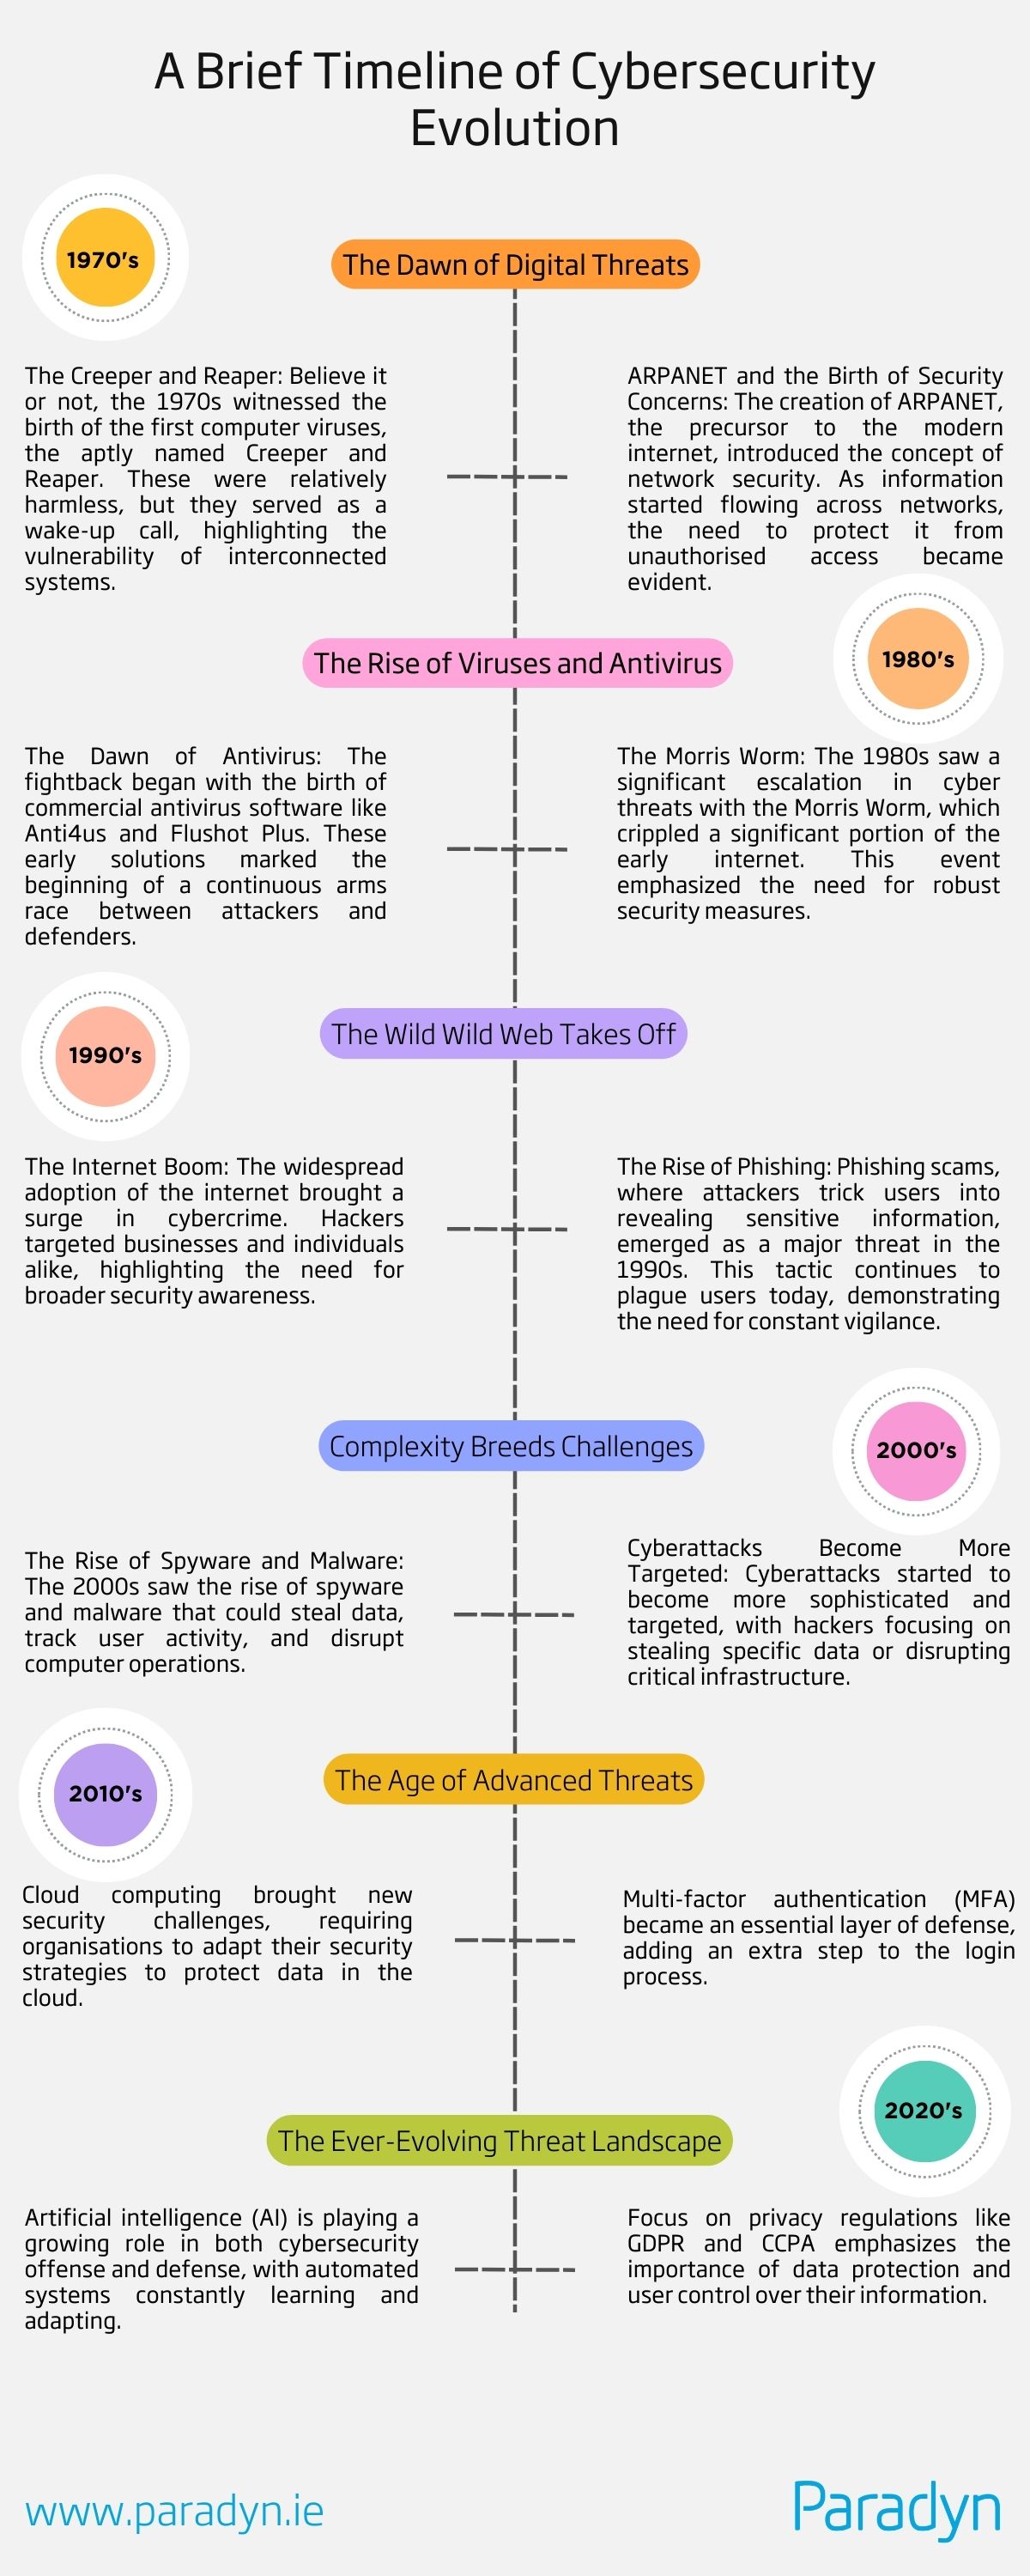
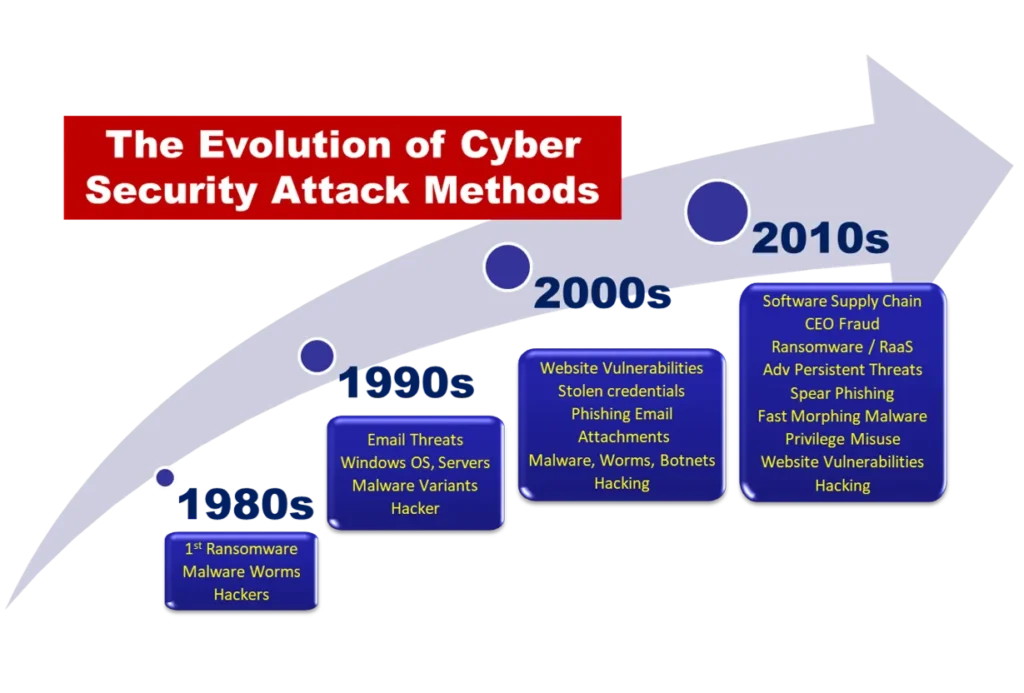
I spent years building out perimeter defenses before the whole paradigm shifted under my feet. That transition didn't happen overnight, and it definitely didn't happen because anyone in leadership suddenly cared about security. It happened because we ran out of reasons to keep expanding the network perimeter. The way threats have evolved over the last decade is one of the most important things I've had to adapt to professionally. When I started, a VPN and a decent firewall kept most attackers out. Now that approach is basically decorative. Attackers don't break in anymore, they log in. That's the core shift. Credential theft, session hijacking, and privilege escalation replaced port scanning and buffer overflows as the primary attack vectors. What that means for your organization is that the people managing your access controls are suddenly the most important line of defense you have.
The Evolution Of Cybersecurity Trends Threats And Best Practices In Management
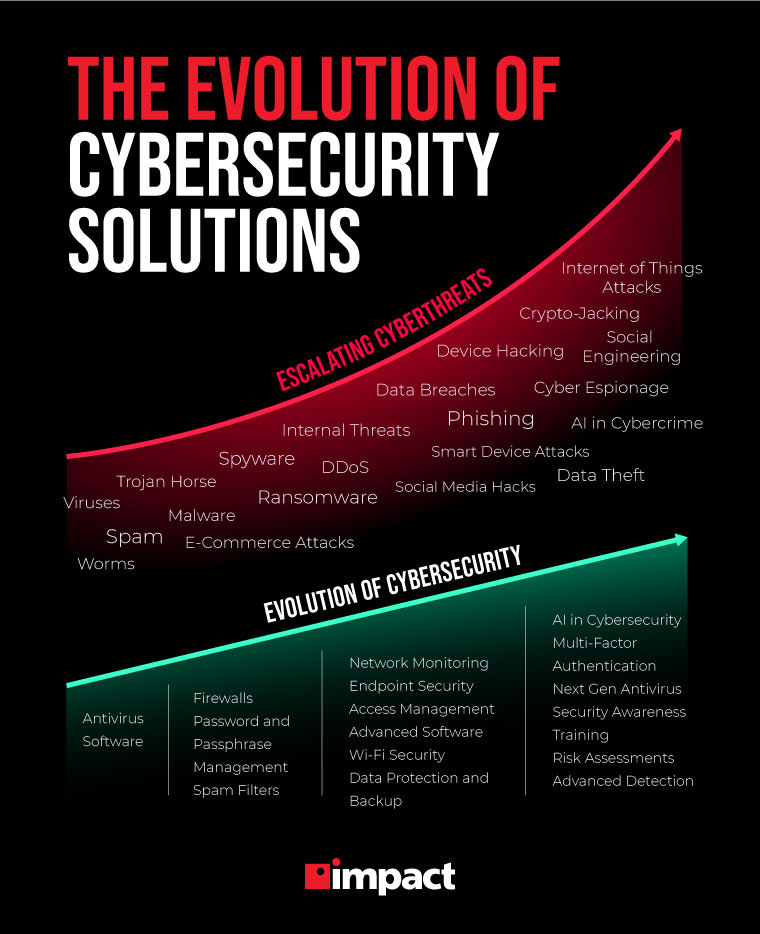
I remember working on an incident where an attacker had been operating inside a client's environment for eleven months before anyone noticed. They'd gotten in through a compromised VPN credential that wasn't rotated in over two years. The actual intrusion technique was sophisticated, but the access remained that simple. That's the thing nobody tells you about this field: the most advanced threat you face today is usually stopped by the same basic hygiene measures your grandparents' bank used. Multi-factor authentication isn't a buzzword. It's the single highest-ROI security investment you can make, and yet it's still the one most organizations treat as optional. The threat landscape right now is dominated by a few specific patterns. Ransomware operators have professionalized to the point where they run customer service portals and SLAs for their affiliates. Supply chain attacks surged after the SolarWinds incident because everyone realized that attacking your vendor is cheaper than attacking you directly. AI-assisted phishing has made social engineering attacks significantly more effective at scale. Lateral movement tools like Cobalt Strike have been widely available for years, which means even low-skill threat actors can operate with tradecraft that used to require dedicated resources. On the management side, the shift toward zero trust architecture has been the dominant trend. Not because every organization understands what zero trust actually means, but because regulatory pressure and insurance requirements have made it necessary. The practical implementation is often messy. I've seen companies deploy zero trust tools without first mapping their own network dependencies, which resulted in legitimate users being locked out of internal systems for days while IT tried to figure out why everything broke. The workaround I ended up using was running the zero trust policy in observation mode for at least thirty days before enforcing anything. That gives you visibility into what actually needs access and what's just legacy junk that hasn't been cleaned up.
Here's a counter-intuitive point that most people miss: the bigger your organization gets, the harder it is to maintain security visibility. This isn't because security gets worse as you scale. It's because the attack surface grows faster than your ability to monitor it. I've worked at companies where we had better tools at smaller scales and worse outcomes at larger ones. The lesson is that tool selection matters less than process discipline. A well-managed SIEM with five hundred events per day beats a poorly-managed SIEM with fifty thousand alerts. Tuning alert thresholds and reducing noise should be a continuous process, not a one-time setup task. When it comes to incident response planning, most organizations have a document that nobody has read since it was written. I'd recommend a different approach. Run tabletop exercises where you assign someone to play the attacker and walk through a realistic scenario step by step. The scenario doesn't need to be complex. A ransomware encryption event affecting your file servers is plenty stressful for a first exercise. What you're looking for is whether your backup restoration procedure actually works, whether your communication tree is current, and whether the person responsible for calling the legal team knows how to find that number in an emergency. Another area where I see consistent failure is patch management. The common assumption is that deploying a patch management solution like SCCM or Intune solves the problem. It doesn't. The problem is that critical patches create disruption, so operations teams delay or skip them. I've seen environments where Windows Security Updates were being held back for sixty to ninety days because nobody wanted to deal with printer drivers breaking after an update. Attackers know this too. They wait for the patch that breaks something and then exploit the gap between vulnerability disclosure and the next approved maintenance window. The practical fix is maintaining a separate, hardened environment for time-sensitive patches and testing them there first before rolling to production.
Get the Full Details
Vendor risk management is another domain where most organizations are severely underprepared. You can have the best internal security posture in the world and still get compromised through a third-party API integration that has broader access than your own systems do. I encountered this directly when a client's cloud provider experienced a breach that exposed their customer database through a misconfigured shared storage bucket. The attacker never touched the client's infrastructure. They went through the provider's account and exploited the principle of least privilege violation on the provider's side. After that, I started requiring all third-party security assessments to include a direct review of data access scopes, not just a checklist of security controls. The biggest bottleneck I see in security management today isn't technology. It's the lack of dedicated personnel who understand both the technical and business sides. A security team that only knows firewalls and encryption can't effectively communicate risk to leadership. A leadership team that only cares about uptime and budget will always deprioritize security unless someone can translate technical vulnerabilities into business impact. The people who succeed in this field are the ones who can explain to a CFO why a forty-thousand-dollar identity governance solution prevents a two-million-dollar breach. That translation skill is more valuable than any certification. There are also specific metrics that matter and metrics that are basically vanity. The number of security events your SIEM processes per day is not a useful metric. Mean time to detect and mean time to respond are more useful, but only if you're measuring them consistently across incidents of similar severity. A better approach is tracking the percentage of critical vulnerabilities patched within your target window, the ratio of false positives to true positives in your alert pipeline, and the number of privileged accounts with inactive credentials. These numbers tell you something actionable.
If you're starting from scratch or trying to rebuild a security program that's fallen behind, the order of operations matters. Patch management and vulnerability scanning come first because unpatched systems are trivially exploitable. Identity and access management comes second because compromised credentials are the primary initial access vector. Logging and monitoring comes third because you can't detect breaches without visibility. Everything else, including advanced threat detection and security orchestration, depends on those three foundations being solid. Trying to implement advanced capabilities before the basics are in place is like building a second floor on a house with no foundation.