Understanding Cyber Deception in the Context of National Security
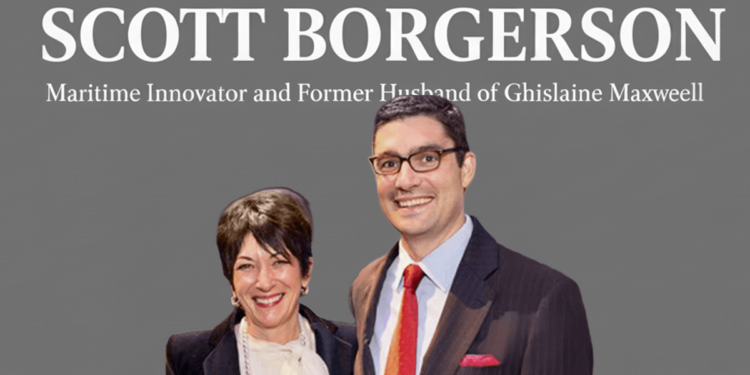
Scott Borgerson is not a household name, but anyone who has worked in defensive cyber operations knows why he matters. He spent decades in the Coast Guard and later at U.S. Cyber Command, where he was directly involved in shaping how the United States approaches the intersection of cyber deception and national security. The core of what he represents is a pragmatic view: you cannot defend critical infrastructure by only building walls. You have to make attackers waste time, expose their tradecraft, and reveal their hand before they ever reach anything important. Borgerson's career gives you a practical roadmap. He started in maritime operations, which teaches you something most cyber people miss: the environment itself can be used against the adversary. In a port, you don't just monitor shipping lanes. You set up false signals, control what an opposing force can see, and let them walk into a controlled space. Translating that to cyberspace means building systems that look like they're worth attacking when they're actually your trap. The deception playbook Borgerson's work points toward has several layers. First is the honey network. This is not about setting up a single fake server and calling it a day. It involves creating a believable internal architecture with decoy assets, fake credentials, and lateral movement paths that look real but are entirely monitored. When an APT group gets past the perimeter and starts probing, they should hit a honeypot within minutes, not days. I remember working through an engagement where our initial detection came from a compromised credential someone reused across a fake jump server. The attacker thought they had gotten into an actual domain controller. They did not. It was running on a thin client with no network access beyond the decoy environment. We watched them spend about four hours trying to escalate privileges before we pulled the feed. That window gave us their entire methodology, tooling list, and likely attribution indicators.
The second layer is data poisoning. Modern defenders sometimes forget that attackers are also consuming data. If you seed false information into threat intelligence feeds, log repositories, or even version control systems that your monitoring tools pull from, you can guide an adversary toward wrong targets. This requires careful control, because once you start lying to your own systems, you can lose track of what is real. I learned this the hard way during a red team exercise where we injected false endpoint telemetry into a SIEM feed to mislead the attackers. The exercise ran so long that some of our own SOC analysts started questioning whether certain alerts were from the exercise or a live intrusion. The fix was simple but easy to overlook: you have to tag every poisoned artifact with a marker that is invisible to the attacker but immediately obvious to your own team. A specific comment in the code, a known IP range reserved only for decoys, a marker string in registry keys. Something the adversary has no reason to know exists. The third layer is what Borgerson emphasizes more than most: operational culture. Deception does not work if the people inside the organization do not understand what is real and what is a trap. I have seen teams build elaborate honey networks and then have an analyst accidentally log into a decoy machine thinking it was production, take a screenshot, and forward it to an external contact. The deception failed not because the technology was bad but because the humans were not part of the design. The workaround is straightforward. Every decoy asset needs a clear, documented classification. It should not look different from real systems. But the personnel file for each machine, the asset inventory, and the onboarding documentation must flag it as a honeypot. And you have to train people on this regularly. Once a year is insufficient. Every quarter, at minimum.
How to Build a Practical Deception Framework
Most organizations start by buying a commercial deception platform and hoping it covers everything. That approach fails because it treats deception as a product, not as a system. The real question is what you are trying to achieve. Are you trying to detect initial access? Lateral movement? Data exfiltration? Credential theft? Each objective requires different decoy assets and different placement. Start by mapping your actual attack surface. I know this sounds obvious but the majority of teams skip it. You need to know where your sensitive assets live, which systems talk to each other, and what credentials have elevated access. Once you have that map, you identify gaps. These are the spaces where an attacker could move that you currently have no visibility into. That is where you place your first decoys. Not everywhere. Just in the blind spots. Decoy placement follows three rules. The first rule is proximity. A decoy that sits in an isolated VLAN and sends all its alerts to a monitoring dashboard is useless. It needs to be positioned where real attackers would actually go. If your database servers talk to application servers, put a decoy on the application tier. If your cloud environment has storage buckets that should not be public, create fake buckets with names that match your real naming conventions and watch for access attempts. The second rule is believability. Decoy systems need to respond like real systems. A server that does not respond to SSH prompts, does not have any running services, and returns empty error messages will be ignored or immediately identified as fake by anyone with experience. I once saw an attacker spend thirty seconds on a decoy VM, notice the clock skew in the system logs, and move on. The clock skew came from the VM never having been connected to NTP. Fixing that alone made the decoy ten times more effective.
Get the Full Details
The third rule is escalation. Your decoys should give the attacker something to work with, but only up to a point. A decoy domain controller that hands out real-looking Kerberos tickets and responds to LDAP queries is valuable. A decoy that also tries to connect back to a real command and control server is dangerous and unnecessary. Keep the decoy contained. The moment you simulate behavior that could leak outside the lab, you have crossed from deception into risk.
Common Pitfalls That Break Deception Programs
The biggest failure mode I see is alert fatigue from poorly tuned detection rules. When you deploy a honey network, you will generate noise. Some of it is from legitimate scanning, some from automated vulnerability tools, and some from actual attackers. If your SIEM is not filtering out the routine background traffic, you will drown in false positives within a week. The specific fix is to baseline your environment first. Run your deception infrastructure for two weeks with logging only and no alerts. Watch what comes in. Then set thresholds based on actual data, not on generic rules. A single connection to a decoy is noise. Five connections to five different decoys in thirty minutes is signal. Another pitfall is assuming attribution is possible from deception data alone. Borgerson's work makes it clear that deception can tell you a lot about an attacker's methods, but it cannot reliably tell you who they are. You can learn their tooling, their patience level, their escalation preferences, their targeting criteria. But mapping that to a specific nation state or group is speculative unless you have other sources feeding into it. The mistake teams make is overconfidence in what the deception data proves. It proves behavior. It does not prove identity. A less obvious problem is the cost of maintenance. Decoy systems decay. Operating systems get unpatched. Fake services break. Credentials expire. A honey token that stops returning realistic responses becomes worse than useless because it gives a false sense of coverage. I track this by running a weekly health check on every decoy asset. If a decoy has not seen legitimate-looking traffic in fourteen days, I investigate. Either the traffic pattern has changed and I need to reposition the decoy, or the decoy itself has broken and needs to be rebuilt. Both happen frequently.
Where Deception Fails Completely
There are scenarios where a deception strategy adds almost no value. The first is when the attacker has insider knowledge. If someone inside the organization already knows where your real assets are and how your network is structured, a decoy they planted or a fake service they helped configure will be indistinguishable from a real one to your monitoring tools. You end up tracking your own agent instead of the attacker. The workaround here is to segregate your deception infrastructure from your monitoring infrastructure. Do not use the same SOC analyst team to investigate both real alerts and decoy alerts. Rotate responsibilities so that the people reviewing decoy hits do not have context about real asset locations. The second failure mode is high-sophistication adversaries who deliberately avoid everything that looks interesting. These attackers are looking for silence, not activity. They scan slowly, probe minimally, and target systems that nobody else would bother defending. A honey network that lights up with automated scanning traffic might still be completely invisible to a patient, manual operative. In those cases, deception alone is insufficient. You need behavioral analytics on your real assets, network segmentation to limit what an attacker can reach even after initial compromise, and continuous monitoring of privileged access. Deception complements those controls but does not replace them. The bottom line is that cyber deception is a tool, not a strategy. Borgerson's career shows this clearly. He has always treated deception as part of a layered defense, not as a standalone solution. The organizations that get the best results are the ones that deploy it deliberately, maintain it rigorously, and do not pretend it solves problems it was never designed to solve.