What DNS Actually Is
DNS stands for Domain Name System. It translates human-readable domain names into IP addresses. When you type example.com into your browser, your computer doesn't understand that text. It needs a numerical address like 93.184.216.34. DNS bridges that gap. Every request you make goes through a process that takes roughly 20 to 200 milliseconds, depending on your resolver and whether anything is cached. It isn't a single database. The system is distributed across thousands of servers worldwide, organized hierarchically from root servers down to authoritative name servers for each domain. This design was created in 1983 by Paul Mockapetris, and the basic protocol has changed remarkably little since then.
How a Lookup Actually Works
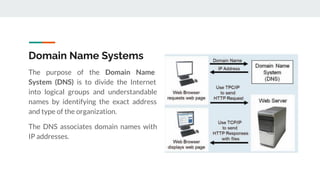
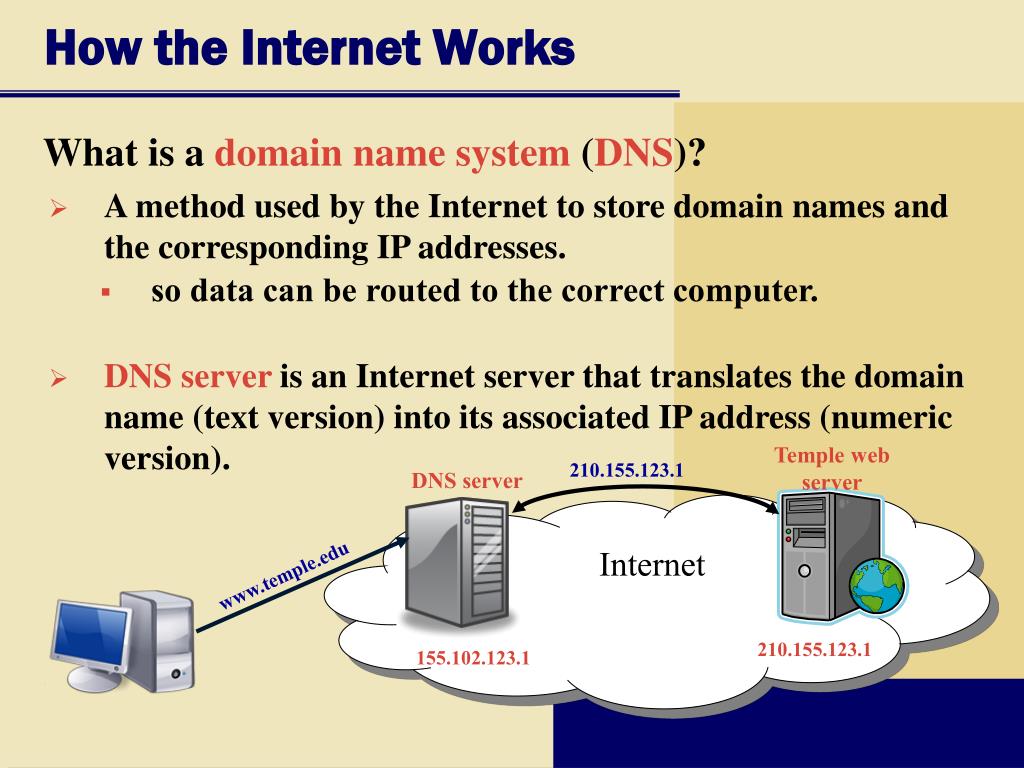
I want to explain the process because most people have the wrong mental model here. You don't just ask a domain name server for an IP and get it back. The lookup chain is more involved than that. Your machine first checks its local cache. If there's nothing there, it contacts your recursive resolver, usually provided by your ISP or a service like Google's 8.8.8.8 or Cloudflare's 1.1.1.1. That resolver then navigates the hierarchy. It starts at one of the 13 root server clusters, gets pointed to the top-level domain server for .com, which then points it to the authoritative nameserver for your specific domain. Only that final server knows the actual IP address. Each step adds latency if nothing is cached along the way. The whole thing should resolve in under a second on a healthy connection. If it's taking longer, something is misconfigured or there's a caching failure somewhere in the chain.
The Domain System How Internet Addresses Power Our Connected World
This mechanism is why the modern internet functions at all. Without DNS, we'd need to memorize numerical addresses for every service we use. You'd type 172.67.182.31 into your browser instead of github.com. Nobody does that. The system handles billions of lookups every minute globally, and the vast majority complete without users noticing. A records map a domain to an IPv4 address. AAAA records do the same for IPv6. CNAME records point one domain name to another domain name, not to an IP. MX records specify mail servers. TXT records hold arbitrary text and are used for everything from SPF and DKIM email authentication to domain verification for third-party services. NS records delegate authority to specific nameservers. SRV records exist for service discovery but nobody uses them outside of specific enterprise VoIP and messaging setups. LOC records exist for geographic coordinates and are essentially unused. The five I listed above cover 99% of real-world configurations.
Get the Full Details
One thing beginners consistently miss: CNAME records cannot coexist with any other record type for the same hostname. You cannot have a CNAME and an MX record on the same subdomain. This trips up a lot of people who try to set up a custom mail domain on a CNAME alias. The fix is straightforward, but you have to understand why the rule exists in the first place. DNS standards were written this way because resolving a CNAME requires a second lookup, and mixing record types creates ambiguous resolution paths.
Real Problems I've Encountered
I spent four hours once debugging a website that refused to resolve on certain mobile networks. Desktop browsers worked fine. Android phones on cellular data failed. The issue was that the hosting provider's nameservers had AAAA records pointing to IPv6 addresses, but the hosting environment didn't actually have IPv6 routing configured. Most desktop resolvers would fall back gracefully to the A record. Some mobile carrier DNS resolvers, particularly on certain European networks, would refuse to complete the query entirely rather than attempt the fallback. The workaround was adding a local DNS forwarder rule on our router to force those resolvers to ignore the broken AAAA records for that domain. Not an elegant solution, but it stopped the bleeding. Another common issue: TTL misconfiguration. I've seen people set TTLs to 3600 seconds when they needed to push out a DNS change quickly. With a one-hour TTL, updates propagate slowly because most resolvers honor the cached value for the full duration. Lowering the TTL to 60 seconds before making changes gives you near-realtime propagation, but it increases query volume against your authoritative servers. There's a tradeoff you have to manage deliberately rather than guessing.
Where DNS Fails
The system has structural weaknesses. It was designed in an era when trust between servers was assumed. There's no built-in authentication for DNS responses. That's why DNSSEC exists, but adoption is incomplete. Only a small fraction of domains publish signed records. Most resolvers will happily accept unsigned responses even when a domain claims to support DNSSEC, because the validation isn't enforced consistently across all resolvers. DNS poisoning attacks are theoretically possible on any unencrypted lookup. Response spoofing requires the attacker to guess query IDs and respond faster than the legitimate server. Modern resolvers have randomized query IDs and extended randomization techniques that make this difficult, but not impossible. DoH and DoT encryption address part of this by encrypting the query itself, but the final resolution still passes through the resolver, which becomes a single point of surveillance and potential manipulation. Censorship is another area where DNS breaks down. Many countries block access to specific domains at the DNS level. Raising the DNS server to a different provider in a less restricted jurisdiction is the standard workaround, but it only works if your network doesn't also block IP ranges or deep packet inspection catches the encrypted DoH traffic.

Practical Recommendations
If you're running a domain that matters for your business, use a reputable DNS provider with anycast infrastructure. Cloudflare, AWS Route 53, and Azure DNS all offer high availability. Cheap or free DNS hosting from domain registrars is fine for personal projects but usually lacks the redundancy and attack surface of dedicated providers. Enable DNSSEC. It adds cryptographic signing to your zone and protects against spoofing at the resolution level. The configuration varies by provider but typically involves generating a key pair and publishing a DS record at your registrar. Takes about ten minutes if your provider has automation for it. Set sensible TTLs. Default is often 3600, which is reasonable for stable records. If you're doing frequent infrastructure changes, drop to 300 beforehand. Don't set TTLs below 60 seconds unless you're running a CDN or edge compute system that genuinely benefits from rapid reassignment. Lower TTLs increase resolver load and can trigger rate limiting on your authoritative servers.
Monitor your records. Broken DNS doesn't always bring a site down completely. Partial failures, split views between geographies, and stale caches cause intermittent issues that are harder to diagnose than total outages. Set up monitoring that checks resolution from multiple locations and validates SSL certificates chain back to the expected domain.
Advanced: Split-Horizon and Geo-DNS
Most people never configure these, but they're worth understanding. Split-horizon DNS returns different records depending on the source IP of the query. This is commonly used by corporations so that employees inside the network resolve internal service names to private IPs while external queries get public addresses. Some consumer router firmware supports a simplified version of this, letting you override specific DNS responses for your local network. Geo-DNS routes traffic to different IP addresses based on the geographic location of the resolver. Large CDNs and cloud providers use this extensively. If you run a service with users concentrated in specific regions and you have servers in multiple locations, a provider like Cloudflare or Amazon Route 53 can automatically direct European users to Frankfurt, American users to Virginia, and Asian users to Tokyo based on resolver location. This reduces latency without requiring any client-side configuration. The catch is that geo-routing accuracy depends entirely on how well your DNS provider maps resolver IPs to geographic regions. IP geolocation databases are imperfect. Some mobile carriers register their DNS resolvers in unexpected locations. You'll get rough regional distribution, not precision targeting.