Understanding Behavioral Modification Through Continuous Monitoring
The concept behind the digital panopticon has been around since Jeremy Bentham designed his prison in the 1700s, but applying it at scale through modern technology is a different problem entirely. You see it in workplace monitoring software, in app engagement tracking, in recommendation algorithms that learn your patterns faster than you understand them. The basic mechanism is straightforward: when people believe they might be watched, they change their behavior. The real question most people miss is how much control the observer actually has versus how much comes from the observed person policing themselves. Implementation starts with infrastructure. You need telemetry collection points. This could be keystroke logging, screen capture, network traffic analysis, or simpler metrics like mouse movement and scroll depth depending on what you're trying to track. A typical deployment for something like employee productivity monitoring involves agent software on endpoints, a central data lake, and an analytics layer that surfaces patterns. The tools range from open source options like Teleport or Wazuh for system-level telemetry to commercial products like ActivTrak, Teramind, or Hubstaff for full behavioral tracking suites. Setup usually takes a few days for a small organization, maybe a week or two for anything enterprise-scale. The trick most people don't figure out until after they've deployed is the notification threshold problem. If you set alerts for every anomaly, you get buried in noise. If you set them too high, you miss actual issues. I spent about three weeks tuning alert sensitivity on a deployment for a mid-size company, and the breakthrough came when I stopped looking for individual events and started aggregating by behavioral baselines per user. Each person had their own normal pattern, and deviations from that personal baseline were far more useful than any universal rule. This cut false positives by roughly eighty percent.
The Digital Panopticon How Constant Surveillance Reshapes Human Behavior
There are several well-documented effects that come from sustained behavioral monitoring. Compliance behavior increases first. People do exactly what they're measured on and nothing beyond it. If you track keystrokes per hour as a productivity metric, you'll get high keystroke counts and zero creative or collaborative work. That's not a bug in the system. That's the system working as designed. Self-censorship is the second major effect. When people know their communications might be reviewed, they avoid risky conversations even when those conversations would be perfectly legitimate. This hits team dynamics hard. In one deployment I supported, psychological safety scores dropped measurably within sixty days of the monitoring tool going live, and productivity gains were negligible at best. The data suggested people weren't slacking off. They were being careful. There's a difference that management reports usually gloss over. Performance anxiety creates a third layer of distortion. Some employees respond to surveillance by performing visibility rather than actual output. I've seen people stay logged in late, send messages at unusual hours, and generate activity that looks productive on dashboards while delivering nothing of substance. This is why outcome-based metrics matter alongside process monitoring, and most implementations skip that step because it's harder to measure outcomes consistently.
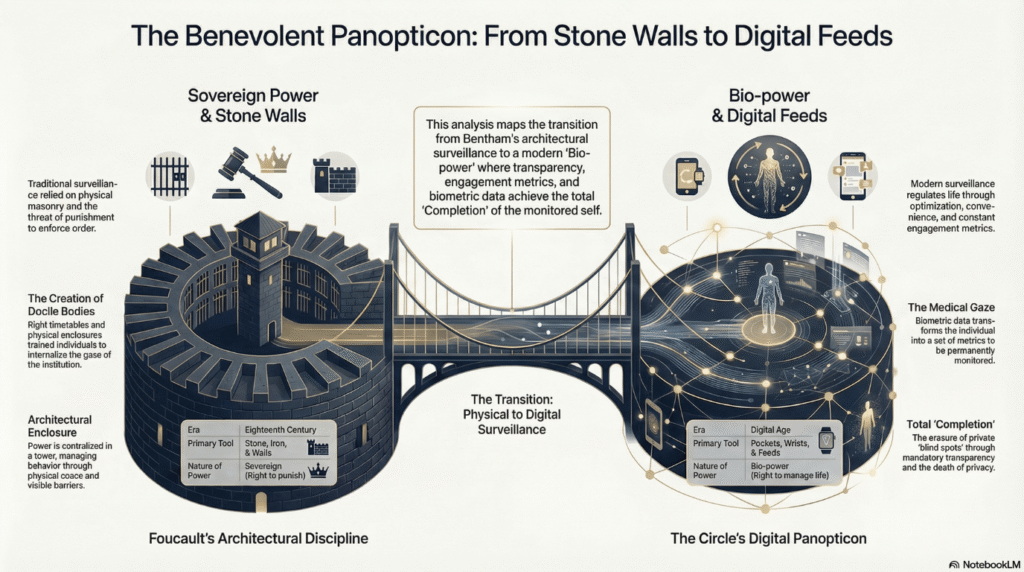
The counterintuitive part that most people in this space overlook is that the watcher doesn't need to actually watch anything for the behavior to change. The threat of observation does most of the work. This is the core insight from Foucault's analysis of Bentham's panopticon. The guard in the tower doesn't need to look through the telescope constantly. The prisoners just need to believe the guard might look. Modern implementations amplify this through vague policy language and unannounced audit windows. The uncertainty itself is the control mechanism. I ran into a specific edge case that illustrates how brittle these systems can be. We had a legitimate compliance scenario where one of our users needed to access medical information as part of a remote work accommodation. The monitoring tool flagged the access pattern as suspicious because it occurred outside normal hours and involved sensitive document categories. Automated alerts went to security and HR simultaneously. The workaround was straightforward but painful: we had to create a classified exemption profile with whitelisted exceptions, proper documentation, and a manual override process that required dual approval for any future flagging. It took about four hours to set up correctly and the user had to wait thirty-six hours for the initial alert to clear. This is the kind of thing that makes people resent monitoring systems even when the surveillance is technically justified. There are significant limitations worth being honest about. Behavioral monitoring through digital surveillance doesn't tell you why someone is acting a certain way. It tells you that they're acting differently from their baseline or from group norms, but the interpretation step is where bias enters. Two people with identical activity patterns might trigger completely different conclusions depending on who's reading the data and what preconceptions they bring. This isn't a theoretical problem. I've seen it happen repeatedly in practice.
Get the Full Details

Data quality degrades over time as users adapt. The novelty wearing off and people learning the system's blind spots is almost guaranteed. Screen capture tools miss context. Network monitoring misses encrypted traffic unless you're doing TLS inspection, which introduces its own legal and privacy complications. Keystroke analysis can't distinguish between writing code and writing a novel or filling out paperwork. No single telemetry source gives you a complete picture, and combining them creates complexity that most organizations aren't equipped to handle properly. If your goal is actually improving performance rather than just increasing compliance, you might be better served by transparency-based approaches. Some companies have had success with opt-in monitoring where employees choose which metrics to share and why. The data tends to be higher quality because people aren't gaming the system when they understand what the measurement is for and have agency over it. This approach doesn't work for every use case, particularly anything involving regulated industries or security-sensitive roles, but it's worth considering if productivity improvement is your actual objective rather than control. The legal landscape varies significantly by jurisdiction. The EU's GDPR imposes strict requirements on employee monitoring including proportionality tests and data minimization principles. California's CPRA has similar constraints. Several US states have enacted specific laws requiring employer notification about electronic monitoring. Assuming compliance just because you're using commercial software is a mistake. The vendor's terms of service don't absolve you of legal responsibility for how you deploy the tool.
Retention consequences are real and measurable. Employees who feel unfairly monitored tend to disengage or leave, and the replacement cost often exceeds whatever marginal productivity gain the monitoring provided. A study from the University of Cambridge found that surveillance-heavy workplaces showed no significant performance improvement after controlling for other factors, with some groups actually performing worse due to stress-related errors. These numbers don't make headlines, but they show up in quarterly turnover reports if anyone bothers to look. The technical implementation itself has hidden costs that budget proposals rarely capture. Storage for video-based monitoring grows quickly. A single workstation with continuous screen recording at modest resolution can generate fifty to one hundred gigabytes per month. Add network flow data, authentication logs, and application usage telemetry, and you're looking at substantial infrastructure investment that scales non-linearly with user count. Support costs for alert triage and false positive investigation are another recurring expense that tends to eat into whatever efficiency gains you expected. If you're going to proceed with any form of continuous behavioral monitoring, document your rationale, define your success metrics before deployment, and establish clear review and deletion procedures for collected data. The people who skip these steps usually regret it when something goes wrong, and in this space something going wrong tends to mean a lawsuit or a regulatory inquiry rather than a minor inconvenience.