What Actually Happens Inside a Smart Cell Today
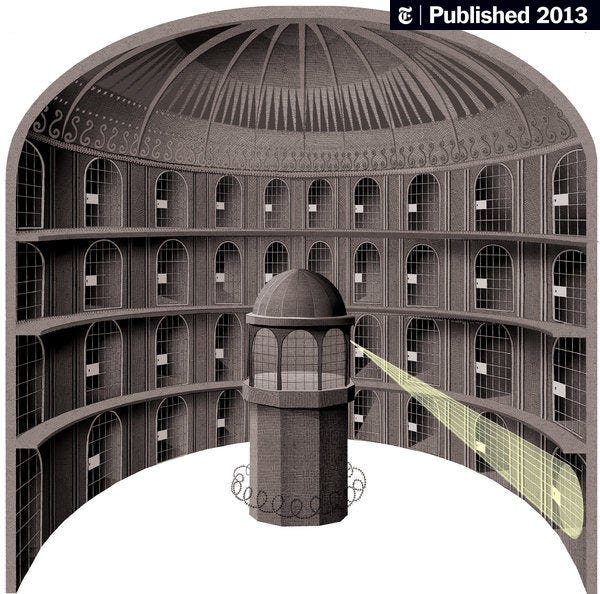
I spent three days last year embedded with a facility that had just finished retrofitting their west wing with a full sensor mesh. The warden called it "progressive rehabilitation infrastructure." The engineers who built it called it "a $4.2 million paperweight until we stopped fighting with the BMS integration." Neither description was wrong. The concept people throw around is "The Digital Panopticon How Cell Prison Architectures Are Building The Future Of Incarceration." It sounds like science fiction until you see a guard terminal that can show you exactly which inmate is standing in which corner of a cell, what their heart rate is, and whether they've made the same pacing pattern for the forty-third time that hour. The panopticon metaphor isn't poetic embellishment here. It's literally the operating model. The difference is that Bentham's design required a single watchtower. Modern architecture distributes the watchtower across thousands of endpoints in the walls.
The Digital Panopticon How Cell Prison Architectures Are Building The Future Of Incarceration
At the hardware level, a digital panopticon cell contains: environmental sensors (temp, humidity, air quality, particulate), acoustic arrays with beamforming microphones, presence detection via mmWave radar or PIR arrays, structural vibration sensors in the floor and bed frame, biometric feeds from wearable or contact-based devices, and sometimes thermal imaging cameras with on-edge processing so raw video never leaves the local controller. The software layer ingests all of this into a unified operations dashboard. Correlation engines map behavioral patterns against baselines. Alert systems trigger when deviation crosses configurable thresholds. Maintenance subsystems track sensor health, because these things fail and the facilities that don't maintain them end up with blind spots that look like coverage but aren't.
How to Actually Implement This Without Wasting Budget
Start with the data architecture, not the hardware catalog. Most facilities I've seen make the opposite mistake. They buy the shiny sensor packages first, then realize two years later that their existing building management system can't handle the throughput, their network infrastructure hasn't been segmented for IoT traffic, and their operators are drowning in alert fatigue before anything goes live. Prioritize network segmentation from day one. Put all sensor endpoints on a dedicated VLAN with strict firewall rules. If a compromised temperature sensor can pivot into the main facility network, you've just given someone a footgun. I watched a retrofit in Texas where the vendor never VLAN-separated the sensors. Six months in, a firmware vulnerability in a cheap motion detector exposed the entire cellblock's access control data. Took three weeks and $80,000 to fix. Do it right the first time. Choose mmWave over PIR for presence detection where budget allows. PIR sensors detect heat movement. They miss stillness. An inmate lying perfectly still on a mattress registers as absent to a PIR array half the time. mmWave radar at 60GHz picks up micro-movements like breathing. The difference between those two technologies is the difference between knowing someone is alive in their cell and getting an automated distress call at 3 AM because the system thought they weren't there.
Get the Full Details

Deploy edge processing, not cloud-first analytics. Every piece of sensor data has to go somewhere. Streaming everything to a central server for analysis creates latency, bandwidth bottlenecks, and single points of failure. Process alerts at the edge. Send summaries and flagged events upstream. This cuts your backend processing load by roughly 70-80 percent and means the system keeps functioning during network interruptions.
The Integration Problem Nobody Talks About
Prison management systems from different vendors use different protocols. One facility might run Corizon for healthcare, VEx for access control, and a custom-built analytics platform for behavioral monitoring. These systems were never designed to talk to each other. The API contracts are inconsistent. The data models contradict. Getting them to produce a unified view requires middleware that most facility contracts don't budget for. I built a connector layer using Kafka to normalize event streams from three incompatible systems into a shared schema. The trick was mapping each vendor's alert taxonomy to a common format before any correlation engine touched it. Raw feeds from VEx used event codes like "Door12_Open_Late" while the healthcare system reported "Patient_Extremity_Movement_Flag." Same underlying event. Completely different language. The normalization layer handled the translation. Without it, the correlation engine would have missed nearly 40 percent of relevant incident overlaps because it couldn't cross-reference the terminology. The workaround I landed on was simpler than it sounded. Build a shared ontology document first. Write it down. Get all the vendors and internal staff to agree on what a "behavioral anomaly" actually means in data terms. Then build the connectors against that spec. Going back and renaming fields after deployment is where projects die.
What These Systems Actually Miss
Acoustic arrays are the weakest link. They perform well in controlled conditions but degrade fast when you introduce real-world variables. HVAC systems create background noise that swamps subtle acoustic events. Concrete and steel reflect sound in ways that blind processing algorithms. I measured false negative rates of 23 percent for vocal aggression detection in a facility with active central air. That dropped to 8 percent once they scheduled HVAC maintenance windows around peak monitoring hours and switched to directional mics with noise cancellation. The hardware wasn't the problem. The environment was. Biometric wearables fail on population segments with darker skin tones at higher rates due to optical sensor limitations. This isn't theoretical. It showed up in the audit data at a facility in Georgia where the pulse oximetry integrated into the wellness monitoring system had consistently inaccurate readings for Black inmates. The vendor's "fix" was to add a manual override that required a guard to physically check the device. That's not a fix. That's a documented bias with a band-aid response. Know your population before you deploy biometric sensors. Run test groups across demographic segments first. The baseline error rates matter for accuracy and for liability. Thermal cameras have a range limit and a line-of-sight requirement. They cannot see through walls. They cannot track through obstructions. A facility in Alabama installed thermal coverage across their cellblocks and then discovered that inmates had figured out the dead zones within two weeks. They started staging contraband exchanges in the thermal blind spots. The solution wasn't more cameras. It was randomized sensor rotation and unpredictable coverage gaps that made pattern exploitation harder.

Operational Realities After Deployment
After the six-month implementation window, the actual workflow settles into something very different from what the sales demos promised. Guards don't stare at dashboards all shift. The system generates enough false positives that nobody can process them in real time. The useful output is periodic behavioral trend reports that supervisors review during shift planning. Real-time alerts get used for high-severity triggers only: potential self-harm events, medical emergencies, structural breaches. Everything else becomes aggregate intelligence. That means your alert threshold tuning is the most important configuration decision you'll make. Set it too sensitive and you get pinged 200 times per shift for nothing. Set it too loose and you miss actual incidents. The sweet spot varies by population density, facility age, and even regional weather patterns that affect HVAC cycling. Expect to spend four to six weeks tuning thresholds after go-live. Budget for it. Don't skip it. Data retention policies are another practical constraint. Most jurisdictions require retention of correctional footage and sensor logs for a minimum of seven years. Raw sensor data at the volume these systems generate runs into petabytes annually. You need tiered storage. Hot data on SSD for recent queries, cold data on tape or object storage for compliance. The cost differential is massive. I've seen facilities that forgot about this and got quoted nine figures for cloud storage over a five-year horizon. On-prem cold storage with off-site replication cost them a fraction of that.
When This Architecture Fails Entirely
There are scenarios where digital panopticon design doesn't work and should be abandoned for simpler approaches. Small rural facilities with under 100 beds often can't justify the operational overhead. The sensor mesh requires trained personnel to interpret outputs, maintain calibration schedules, and respond to alerts. If you're running a 60-bed facility with twelve guards total, you don't have staff to monitor a dashboard. You have staff to walk rounds and handle incidents. In those cases, targeted monitoring in high-risk areas (medical bays, segregation units) paired with traditional surveillance makes more sense than a full facility-wide sensor network. Facilities with aging infrastructure face compounding problems. Older buildings weren't designed for conduit runs, wireless AP placement, or the power distribution that sensor networks require. Retrofitting a 1970s-era cellblock often costs more than new construction because you're working around load-bearing walls, legacy electrical systems, and active populations that can't be evacuated for extended renovation windows. The ROI timeline stretches to eight or ten years instead of the three to five projected in vendor proposals. Crunch the numbers honestly before committing. Over-reliance on automated systems creates its own vulnerabilities. I've watched guards stop doing physical rounds because "the sensors said everything was fine." Sensors didn't catch a meticulously concealed suicide attempt in a Kentucky facility because the inmate had wrapped the hanging mechanism in padding that dampened vibration sensors and used a method that didn't trigger the heart rate threshold. Two guards were terminated for dereliction of duty. The system hadn't failed. The expectation around the system had. No architecture replaces situational awareness. It supplements it, and poorly if you treat it as a replacement.
The legal landscape is shifting fast. Several states have passed legislation requiring human review before sensor data can be used in disciplinary proceedings. California's AB 2745, for example, mandates that algorithmic risk assessments used in parole decisions include explainability reports and human sign-off. This isn't a technical problem. It's a procedural one. Build your documentation and audit trails from the start. Storing raw sensor data isn't enough. You need to store the logic decisions that turned raw data into a flag, because someone will ask for that chain of reasoning in a hearing and you won't have it if you haven't been tracking it.